Compare commits
260 Commits
| Author | SHA1 | Date | |
|---|---|---|---|
 veeso |
5cee1184dc | ||
|
Christian Visintin
|
4a9da89642 | ||
|
veeso
|
282f75c3f3 | ||
|
Christian Visintin
|
535ed23540 | ||
|
Christian Visintin
|
70bd7d7330 | ||
|
Christian Visintin
|
352eec4762 | ||
|
Christian Visintin
|
3a5327f5b1 | ||
|
Christian Visintin
|
b1601fb17e | ||
|
Christian Visintin
|
bca261b7b2 | ||
|
Christian Visintin
|
904befaea8 | ||
|
Christian Visintin
|
afe7b05830 | ||
|
Christian Visintin
|
837592e48a | ||
|
Christian Visintin
|
ab5de031e3 | ||
|
Christian Visintin
|
f3085161e6 | ||
|
Christian Visintin
|
1dafc76850 | ||
|
Christian Visintin
|
f066d6a387 | ||
|
Christian Visintin
|
987751d732 | ||
|
Christian Visintin
|
1ca8abbfe8 | ||
|
Christian Visintin
|
26e71a2f1d | ||
|
Christian Visintin
|
b1d77c78fe | ||
|
Christian Visintin
|
2a7d48a92b | ||
|
Christian Visintin
|
82141e7f2b | ||
|
Christian Visintin
|
14bc15cfca | ||
|
Christian Visintin
|
85fa99e4cc | ||
|
Christian Visintin
|
3ff3cdb587 | ||
|
Christian Visintin
|
726443ae21 | ||
|
Christian Visintin
|
0bd449e7bc | ||
|
Christian Visintin
|
c24f08691d | ||
|
Christian Visintin
|
14e6872432 | ||
|
Christian Visintin
|
88900a80b8 | ||
|
Christian Visintin
|
ce619bcff2 | ||
|
Christian Visintin
|
5a16467e71 | ||
|
Christian Visintin
|
b6ca8c57f0 | ||
|
Christian Visintin
|
660c17a0df | ||
|
Christian Visintin
|
aed4ecc522 | ||
|
Christian Visintin
|
ee69ba6ef8 | ||
|
Christian Visintin
|
0db3ea43d2 | ||
|
Christian Visintin
|
6a61eb16f7 | ||
|
Christian Visintin
|
e32ed613cc | ||
|
Christian Visintin
|
dbd61f0fab | ||
|
Christian Visintin
|
a18fa0ca5a | ||
|
Christian Visintin
|
c8846266d7 | ||
|
Christian Visintin
|
40440832be | ||
|
Christian Visintin
|
34c03841be | ||
|
Christian Visintin
|
ded71dce48 | ||
|
Christian Visintin
|
eefa1b3db0 | ||
|
Christian Visintin
|
a2d766d688 | ||
|
Christian Visintin
|
f92cb93755 | ||
|
Christian Visintin
|
d070825dd7 | ||
|
Christian Visintin
|
3774156873 | ||
|
Christian Visintin
|
bbeefc557e | ||
|
Christian Visintin
|
3ee21aba2f | ||
|
Christian Visintin
|
6cf5bf18cf | ||
|
Christian Visintin
|
d7b7ab7fa1 | ||
|
Christian Visintin
|
48b387de14 | ||
|
Christian Visintin
|
e381484022 | ||
|
Christian Visintin
|
203a6da387 | ||
|
Christian Visintin
|
3379940ec9 | ||
|
Christian Visintin
|
2153164484 | ||
|
Christian Visintin
|
0cc7362bd9 | ||
|
Christian Visintin
|
5c84a0e88d | ||
|
Christian Visintin
|
a25b17a4e5 | ||
|
Christian Visintin
|
d670aed079 | ||
|
Christian Visintin
|
6fa3c042b1 | ||
|
Christian Visintin
|
fc7e789390 | ||
|
Christian Visintin
|
3c4356af92 | ||
|
Christian Visintin
|
ba513850c1 | ||
|
Christian Visintin
|
f56dd60868 | ||
|
Christian Visintin
|
f544a63d19 | ||
|
Christian Visintin
|
02fec64d35 | ||
|
Christian Visintin
|
a54ff078cc | ||
|
Christian Visintin
|
c27748272d | ||
|
Christian Visintin
|
f6d65cf09d | ||
|
Christian Visintin
|
930e76814f | ||
|
Christian Visintin
|
cdd4c60805 | ||
|
Christian Visintin
|
c652ca18b8 | ||
|
Christian Visintin
|
0ad18ea5e7 | ||
|
Christian Visintin
|
2ed71c7ff8 | ||
|
Christian Visintin
|
49102985a4 | ||
|
Christian Visintin
|
bc59df494b | ||
|
Christian Visintin
|
080c013fab | ||
|
Christian Visintin
|
6252df2959 | ||
|
Christian Visintin
|
9160c52cb0 | ||
|
Christian Visintin
|
38f1fccfd0 | ||
|
Christian Visintin
|
6ceaf048b5 | ||
|
Christian Visintin
|
534c16427e | ||
|
Christian Visintin
|
9b19240925 | ||
|
Christian Visintin
|
0ddbf3b104 | ||
|
Christian Visintin
|
126e58503f | ||
|
Christian Visintin
|
0be8b60c7d | ||
|
Christian Visintin
|
4ed6b118ca | ||
|
Christian Visintin
|
a48b226d9b | ||
|
Christian Visintin
|
e11af03fdd | ||
|
Christian Visintin
|
f044e6ace2 | ||
|
Christian Visintin
|
e056afbd28 | ||
|
Christian Visintin
|
9442e3b150 | ||
|
Christian Visintin
|
9c00b9a86c | ||
|
Christian Visintin
|
622cfe260a | ||
|
Christian Visintin
|
0c3ced012e | ||
|
Christian Visintin
|
d60c5007f9 | ||
|
Christian Visintin
|
7e10b8e68b | ||
|
Christian Visintin
|
08509caf1b | ||
|
Christian Visintin
|
89de2d2dfa | ||
|
Christian Visintin
|
abc80b93ad | ||
|
Christian Visintin
|
1b79a6fc91 | ||
|
Christian Visintin
|
5a3aa64fba | ||
|
Christian Visintin
|
bc4b096077 | ||
|
Christian Visintin
|
0025b87b0f | ||
|
Christian Visintin
|
bd0843d3da | ||
|
Christian Visintin
|
0ba43d5714 | ||
|
Christian Visintin
|
97e1ca789a | ||
|
Christian Visintin
|
2df13fac10 | ||
|
Christian Visintin
|
186313f57c | ||
|
Christian Visintin
|
8b0be49609 | ||
|
Christian Visintin
|
e062ee0447 | ||
|
Christian Visintin
|
c81cf39fe9 | ||
|
Christian Visintin
|
9cfef867a9 | ||
|
Christian Visintin
|
18314e6a2e | ||
|
Christian Visintin
|
9f3df1a79a | ||
|
Christian Visintin
|
fe424107e9 | ||
|
Christian Visintin
|
d97535894c | ||
|
Christian Visintin
|
4d65e48b3c | ||
|
Christian Visintin
|
0d24662b3d | ||
|
Christian Visintin
|
bc14b049c0 | ||
|
Christian Visintin
|
d32c588f15 | ||
|
Christian Visintin
|
60e86aff2a | ||
|
Christian Visintin
|
5f83a1468c | ||
|
Christian Visintin
|
5758a12c3b | ||
|
Christian Visintin
|
49a74d02ea | ||
|
Christian Visintin
|
f6d35f1eea | ||
|
Christian Visintin
|
3fb61a76fe | ||
|
Christian Visintin
|
ff4452c971 | ||
|
Christian Visintin
|
fd1d8a0e26 | ||
|
Christian Visintin
|
b0d6da8e23 | ||
|
Christian Visintin
|
4ca0865fe3 | ||
|
Christian Visintin
|
b8115362f8 | ||
|
Christian Visintin
|
155f747563 | ||
|
Christian Visintin
|
b04976bde3 | ||
|
veeso
|
5f7a0d8a46 | ||
|
veeso
|
694232564a | ||
|
veeso
|
54b674ad43 | ||
|
veeso
|
c32822037e | ||
|
veeso
|
abb5c212c5 | ||
|
veeso
|
e9b54a227b | ||
|
veeso
|
befc32198a | ||
|
veeso
|
7e5103ff7e | ||
|
veeso
|
2cb600083e | ||
|
Christian Visintin
|
47d23673e6 | ||
|
Christian Visintin
|
a0b357cf8c | ||
|
Christian Visintin
|
75943f2b93 | ||
|
veeso
|
085ab721f9 | ||
|
Christian Visintin
|
f4156a5059 | ||
|
Christian Visintin
|
4bebec369f | ||
|
Christian Visintin
|
05c8613279 | ||
|
veeso
|
205d2813ad | ||
|
veeso
|
86660a0cc9 | ||
|
veeso
|
05830db206 | ||
|
veeso
|
3c79e812eb | ||
 moshyfawn |
0287e7706a | ||
|
veeso
|
67a14c2725 | ||
|
veeso
|
df03c5c1bf | ||
|
veeso
|
3ce3ffee3d | ||
|
Christian Visintin
|
c0b32a1847 | ||
|
Christian Visintin
|
81ae0035c3 | ||
|
veeso
|
783da22ca2 | ||
|
veeso
|
8715c2b6f9 | ||
|
veeso
|
98a748dccc | ||
|
Christian Visintin
|
bef031a414 | ||
|
veeso
|
ce0e953182 | ||
|
veeso
|
9a5caf75c3 | ||
|
veeso
|
446f4a3a32 | ||
|
veeso
|
da75912d26 | ||
|
veeso
|
4ed23c2a18 | ||
|
Christian Visintin
|
23ae334bef | ||
|
Christian Visintin
|
ec75ae1486 | ||
|
veeso
|
368570592f | ||
|
veeso
|
806793421e | ||
|
veeso
|
1f377b242d | ||
|
veeso
|
a4906b129a | ||
|
veeso
|
5c6e8925ad | ||
|
veeso
|
a18eff689d | ||
|
veeso
|
274742d6d9 | ||
|
veeso
|
cdebcbd4dc | ||
|
veeso
|
cdf303a847 | ||
|
veeso
|
dd35fe825c | ||
|
veeso
|
5c4a971aca | ||
|
veeso
|
7522b4d0ff | ||
|
veeso
|
b0f314837e | ||
|
Christian Visintin
|
8a9ba7745a | ||
 haruna |
b7d75a2749 | ||
|
Christian Visintin
|
fe0d9b0aa6 | ||
|
veeso
|
7dba691ccc | ||
|
veeso
|
099e2154ba | ||
|
veeso
|
f2efb25ad7 | ||
|
veeso
|
e45c3d5b4e | ||
|
veeso
|
69f821baef | ||
|
Christian Visintin
|
11559d0962 | ||
|
veeso
|
79c33095fc | ||
|
veeso
|
0ec6bcbcef | ||
|
Christian Visintin
|
3cde067339 | ||
|
Christian Visintin
|
c05ef32270 | ||
|
Christian Visintin
|
7eb913ec7b | ||
|
veeso
|
4e63093d25 | ||
|
Christian Visintin
|
e5d50698d2 | ||
|
Christian Visintin
|
79c31c2d84 | ||
|
Christian Visintin
|
aab266a661 | ||
|
veeso
|
a4c9acb49f | ||
|
veeso
|
6205c7f3c5 | ||
|
veeso
|
e4af014013 | ||
|
Christian Visintin
|
c9f649f40f | ||
|
veeso
|
1f27ca2607 | ||
|
veeso
|
a1288c7480 | ||
|
veeso
|
4bfec52ba5 | ||
|
Christian Visintin
|
3f01be3baa | ||
|
Christian Visintin
|
8e2ffeabce | ||
|
Christian Visintin
|
fc68e2621b | ||
|
Christian Visintin
|
b2a8a3041c | ||
|
veeso
|
c507d54700 | ||
|
veeso
|
31c5ad7534 | ||
|
veeso
|
14ac10547c | ||
|
Christian Visintin
|
ae1638ee17 | ||
|
veeso
|
c5f76ec51c | ||
|
veeso
|
d319a2fae4 | ||
|
veeso
|
72a5703a08 | ||
|
veeso
|
91b4d4e463 | ||
|
veeso
|
17719ea370 | ||
|
veeso
|
707a3faa54 | ||
|
veeso
|
dfe58e6147 | ||
|
veeso
|
c49dab3888 | ||
|
veeso
|
47ff07e496 | ||
|
veeso
|
61a8fb95e4 | ||
|
Christian Visintin
|
f757336d75 | ||
|
veeso
|
cf529c1678 | ||
|
Christian Visintin
|
631f09b9a8 | ||
 Eric Long |
65aed76605 | ||
|
veeso
|
9036d83635 | ||
|
Christian Visintin
|
179c4de4ed | ||
|
Christian Visintin
|
f3b84c97e1 | ||
|
Christian Visintin
|
b5b3aeb645 | ||
|
veeso
|
e5172d4207 | ||
|
Christian Visintin
|
50e7f5f5d0 | ||
|
veeso
|
88cdae79a8 | ||
 Michał Sieroń |
4f3b97b198 | ||
 Hartur Alcantara |
54a8317d0e | ||
 Orhun Parmaksız |
3a46aa74f9 | ||
|
Orhun Parmaksız
|
aca5b37898 | ||
 veeso |
0394a12c9f | ||
|
Christian Visintin
|
e61d04aa1b | ||
|
veeso
|
c0c9f7c0dd | ||
|
veeso
|
905fe5fc9f | ||
|
veeso
|
89ab53a71b | ||
|
veeso
|
7dccac6105 | ||
|
veeso
|
44051ec718 | ||
|
Christian Visintin
|
c7469b8594 | ||
|
veeso
|
5dfee2cbd9 | ||
|
Christian Visintin
|
679a829744 | ||
 PIRADATA |
2a51ab984c | ||
 Jarod |
2b2ebadd6a | ||
|
Christian Visintin
|
2b15a23fe8 | ||
|
veeso
|
d30c3dfadd |
@@ -0,0 +1,4 @@
|
||||
# These are supported funding model platforms
|
||||
|
||||
github: veeso
|
||||
liberapay: veeso
|
||||
@@ -1,42 +0,0 @@
|
||||
name: "Build artifacts"
|
||||
|
||||
on:
|
||||
workflow_dispatch:
|
||||
|
||||
jobs:
|
||||
build-binaries:
|
||||
name: Build - ${{ matrix.platform.release_for }}
|
||||
strategy:
|
||||
matrix:
|
||||
platform:
|
||||
- release_for: MacOS-x86_64
|
||||
os: macos-latest
|
||||
target: x86_64-apple-darwin
|
||||
script: macos.sh
|
||||
|
||||
- release_for: MacOS-M1
|
||||
os: macos-latest
|
||||
target: aarch64-apple-darwin
|
||||
script: macos.sh
|
||||
|
||||
runs-on: ${{ matrix.platform.os }}
|
||||
steps:
|
||||
- uses: actions/checkout@v2
|
||||
- uses: actions-rs/toolchain@v1
|
||||
with:
|
||||
toolchain: stable
|
||||
override: true
|
||||
target: ${{ matrix.platform.target }}
|
||||
- name: Build release
|
||||
run: cargo build --release --target ${{ matrix.platform.target }}
|
||||
- name: Prepare artifact files
|
||||
run: |
|
||||
mkdir -p .artifact
|
||||
mv target/${{ matrix.platform.target }}/release/termscp .artifact/termscp
|
||||
- name: "Upload artifact"
|
||||
uses: actions/upload-artifact@v3
|
||||
with:
|
||||
if-no-files-found: error
|
||||
retention-days: 1
|
||||
name: ${{ matrix.platform.release_for }}
|
||||
path: .artifact/*
|
||||
@@ -0,0 +1,68 @@
|
||||
name: CI
|
||||
|
||||
on:
|
||||
pull_request:
|
||||
branches: [main]
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
push:
|
||||
branches: [main]
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
|
||||
env:
|
||||
CARGO_TERM_COLOR: always
|
||||
|
||||
permissions:
|
||||
contents: read
|
||||
|
||||
jobs:
|
||||
build:
|
||||
name: build-(${{ matrix.os }})
|
||||
runs-on: ${{ matrix.os }}
|
||||
strategy:
|
||||
fail-fast: false
|
||||
matrix:
|
||||
os: [ubuntu-latest, macos-latest, windows-latest]
|
||||
steps:
|
||||
- uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
persist-credentials: false
|
||||
- name: Install Linux dependencies
|
||||
if: runner.os == 'Linux'
|
||||
run: sudo apt update && sudo apt install -y libdbus-1-dev libsmbclient-dev
|
||||
- name: Install macOS dependencies
|
||||
if: runner.os == 'macOS'
|
||||
run: |
|
||||
brew update
|
||||
brew install \
|
||||
pkg-config \
|
||||
samba
|
||||
brew link --force samba
|
||||
- name: Install nightly toolchain
|
||||
if: runner.os == 'Linux'
|
||||
uses: dtolnay/rust-toolchain@29eef336d9b2848a0b548edc03f92a220660cdb8 # stable
|
||||
with:
|
||||
toolchain: nightly
|
||||
components: rustfmt
|
||||
- name: Format
|
||||
if: runner.os == 'Linux'
|
||||
run: cargo +nightly fmt --all -- --check
|
||||
- name: Install stable toolchain
|
||||
uses: dtolnay/rust-toolchain@29eef336d9b2848a0b548edc03f92a220660cdb8 # stable
|
||||
with:
|
||||
toolchain: stable
|
||||
components: clippy
|
||||
- name: Build
|
||||
if: runner.os != 'Linux'
|
||||
run: cargo build
|
||||
- name: Run tests (Linux)
|
||||
if: runner.os == 'Linux'
|
||||
run: cargo test --no-default-features --features github-actions --no-fail-fast
|
||||
- name: Run tests
|
||||
if: runner.os != 'Linux'
|
||||
run: cargo test --verbose --features github-actions
|
||||
- name: Clippy
|
||||
run: cargo clippy -- -Dwarnings
|
||||
@@ -0,0 +1,21 @@
|
||||
name: codeberg-mirror
|
||||
on:
|
||||
push:
|
||||
|
||||
permissions:
|
||||
contents: read
|
||||
|
||||
jobs:
|
||||
mirror:
|
||||
runs-on: ubuntu-latest
|
||||
steps:
|
||||
- uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
fetch-depth: 0
|
||||
persist-credentials: false
|
||||
- name: "Mirror to Codeberg"
|
||||
uses: yesolutions/mirror-action@1708f16cdb28634fd3ba10c5c79abc91f5578a14 # v0.7.0
|
||||
with:
|
||||
REMOTE: 'ssh://git@codeberg.org/veeso/termscp.git'
|
||||
GIT_SSH_PRIVATE_KEY: ${{ secrets.GIT_SSH_PRIVATE_KEY }}
|
||||
GIT_SSH_NO_VERIFY_HOST: "true"
|
||||
@@ -1,45 +0,0 @@
|
||||
name: Coverage
|
||||
|
||||
on:
|
||||
pull_request:
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
push:
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
|
||||
env:
|
||||
CARGO_TERM_COLOR: always
|
||||
|
||||
jobs:
|
||||
build:
|
||||
runs-on: ubuntu-latest
|
||||
|
||||
steps:
|
||||
- uses: actions/checkout@v2
|
||||
- name: Install dependencies
|
||||
run: sudo apt update && sudo apt install -y libdbus-1-dev libsmbclient-dev libsmbclient
|
||||
- name: Setup nightly toolchain
|
||||
uses: actions-rs/toolchain@v1
|
||||
with:
|
||||
toolchain: nightly
|
||||
override: true
|
||||
- name: Run tests (nightly)
|
||||
uses: actions-rs/cargo@v1
|
||||
with:
|
||||
command: test
|
||||
args: --no-default-features --features github-actions --no-fail-fast
|
||||
env:
|
||||
CARGO_INCREMENTAL: "0"
|
||||
RUSTFLAGS: "-Zprofile -Ccodegen-units=1 -Cinline-threshold=0 -Clink-dead-code -Coverflow-checks=off -Cpanic=abort -Zpanic_abort_tests"
|
||||
RUSTDOCFLAGS: "-Zprofile -Ccodegen-units=1 -Cinline-threshold=0 -Clink-dead-code -Coverflow-checks=off -Cpanic=abort -Zpanic_abort_tests"
|
||||
- name: Coverage with grcov
|
||||
id: coverage
|
||||
uses: actions-rs/grcov@v0.1
|
||||
- name: Coveralls
|
||||
uses: coverallsapp/github-action@v1.1.1
|
||||
with:
|
||||
github-token: ${{ secrets.GITHUB_TOKEN }}
|
||||
path-to-lcov: ${{ steps.coverage.outputs.report }}
|
||||
@@ -9,15 +9,24 @@ on:
|
||||
env:
|
||||
CARGO_TERM_COLOR: always
|
||||
|
||||
permissions:
|
||||
contents: read
|
||||
|
||||
jobs:
|
||||
build:
|
||||
runs-on: ubuntu-latest
|
||||
strategy:
|
||||
matrix:
|
||||
os:
|
||||
- ubuntu-latest
|
||||
- macos-latest
|
||||
runs-on: ${{ matrix.os }}
|
||||
|
||||
steps:
|
||||
- uses: actions/checkout@v2
|
||||
- name: Install dependencies
|
||||
run: sudo apt update && sudo apt install -y curl wget libsmbclient
|
||||
- uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
persist-credentials: false
|
||||
- name: Install termscp from script
|
||||
run: |
|
||||
./install.sh -v=0.12.3 -f
|
||||
./install.sh -f
|
||||
which termscp || exit 1
|
||||
termscp --version
|
||||
|
||||
@@ -1,37 +0,0 @@
|
||||
name: Linux
|
||||
|
||||
on:
|
||||
pull_request:
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
push:
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
|
||||
env:
|
||||
CARGO_TERM_COLOR: always
|
||||
|
||||
jobs:
|
||||
build:
|
||||
runs-on: ubuntu-latest
|
||||
|
||||
steps:
|
||||
- uses: actions/checkout@v2
|
||||
- name: Install dependencies
|
||||
run: sudo apt update && sudo apt install -y libdbus-1-dev libsmbclient-dev
|
||||
- uses: actions-rs/toolchain@v1
|
||||
with:
|
||||
toolchain: stable
|
||||
override: true
|
||||
components: rustfmt, clippy
|
||||
- name: Run tests
|
||||
uses: actions-rs/cargo@v1
|
||||
with:
|
||||
command: test
|
||||
args: --no-default-features --features github-actions --no-fail-fast
|
||||
- name: Format
|
||||
run: cargo fmt --all -- --check
|
||||
- name: Clippy
|
||||
run: cargo clippy -- -Dwarnings
|
||||
@@ -1,31 +0,0 @@
|
||||
name: MacOS
|
||||
|
||||
on:
|
||||
pull_request:
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
push:
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
|
||||
env:
|
||||
CARGO_TERM_COLOR: always
|
||||
|
||||
jobs:
|
||||
build:
|
||||
runs-on: macos-latest
|
||||
steps:
|
||||
- uses: actions/checkout@v2
|
||||
- uses: actions-rs/toolchain@v1
|
||||
with:
|
||||
toolchain: stable
|
||||
override: true
|
||||
components: rustfmt, clippy
|
||||
- name: Build
|
||||
run: cargo build
|
||||
- name: Run tests
|
||||
run: cargo test --verbose --features github-actions
|
||||
- name: Clippy
|
||||
run: cargo clippy -- -Dwarnings
|
||||
@@ -0,0 +1,66 @@
|
||||
name: Deploy docs to GitHub Pages
|
||||
|
||||
on:
|
||||
push:
|
||||
branches:
|
||||
- main
|
||||
paths:
|
||||
- "docs/**"
|
||||
- ".github/workflows/pages.yml"
|
||||
workflow_dispatch:
|
||||
|
||||
permissions:
|
||||
contents: read
|
||||
|
||||
concurrency:
|
||||
group: pages
|
||||
cancel-in-progress: false
|
||||
|
||||
jobs:
|
||||
deploy:
|
||||
runs-on: ubuntu-latest
|
||||
permissions:
|
||||
pages: write
|
||||
id-token: write
|
||||
environment:
|
||||
name: github-pages
|
||||
url: ${{ steps.deployment.outputs.page_url }}
|
||||
steps:
|
||||
- uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
persist-credentials: false
|
||||
- name: Install mdBook
|
||||
uses: peaceiris/actions-mdbook@ee69d230fe19748b7abf22df32acaa93833fad08 # v2
|
||||
with:
|
||||
mdbook-version: latest
|
||||
- name: Install mdbook-mermaid
|
||||
run: cargo install mdbook-mermaid
|
||||
- name: Build en-US
|
||||
run: mdbook build docs/en-US
|
||||
- name: Build zh-CN
|
||||
run: mdbook build docs/zh-CN
|
||||
- name: Assemble site
|
||||
run: |
|
||||
rm -rf site_out
|
||||
mkdir -p site_out/en-US site_out/zh-CN
|
||||
cp -r docs/en-US/book/* site_out/en-US/
|
||||
cp -r docs/zh-CN/book/* site_out/zh-CN/
|
||||
cp -r docs/shared site_out/shared
|
||||
cp docs/shared/og_preview.jpg site_out/og_preview.jpg
|
||||
cp docs/shared/favicon.ico site_out/favicon.ico
|
||||
cp docs/CNAME site_out/CNAME
|
||||
cat > site_out/index.html <<'HTML'
|
||||
<!doctype html>
|
||||
<meta charset="utf-8">
|
||||
<title>termscp docs</title>
|
||||
<meta http-equiv="refresh" content="0; url=./en-US/">
|
||||
<link rel="canonical" href="./en-US/">
|
||||
<a href="./en-US/">termscp documentation</a>
|
||||
HTML
|
||||
- name: Upload artifact
|
||||
uses: actions/upload-pages-artifact@56afc609e74202658d3ffba0e8f6dda462b719fa # v3
|
||||
with:
|
||||
path: site_out
|
||||
- name: Deploy to GitHub Pages
|
||||
id: deployment
|
||||
uses: actions/deploy-pages@d6db90164ac5ed86f2b6aed7e0febac5b3c0c03e # v4
|
||||
@@ -0,0 +1,448 @@
|
||||
name: Release
|
||||
|
||||
on:
|
||||
workflow_dispatch:
|
||||
inputs:
|
||||
version:
|
||||
description: "Version to release, e.g. 1.1.0 (no leading v)"
|
||||
required: true
|
||||
type: string
|
||||
dry_run:
|
||||
description: "Dry run: build & compute everything, push/publish nothing"
|
||||
required: true
|
||||
type: boolean
|
||||
default: true
|
||||
|
||||
permissions:
|
||||
contents: read
|
||||
|
||||
jobs:
|
||||
prepare:
|
||||
runs-on: ubuntu-latest
|
||||
outputs:
|
||||
version: ${{ inputs.version }}
|
||||
steps:
|
||||
- uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
token: ${{ secrets.RELEASE_PAT }}
|
||||
persist-credentials: true
|
||||
fetch-depth: 0
|
||||
fetch-tags: true
|
||||
|
||||
- name: Configure git identity
|
||||
run: |
|
||||
git config user.name "veeso"
|
||||
git config user.email "christian.visintin@veeso.dev"
|
||||
|
||||
- name: Install git-cliff
|
||||
uses: taiki-e/install-action@56545b37b57562edd73171cb6c62cc509db4c34e # v2
|
||||
with:
|
||||
tool: git-cliff
|
||||
|
||||
- name: Bump version
|
||||
env:
|
||||
VERSION: ${{ inputs.version }}
|
||||
run: dist/release/bump_version.sh "$VERSION" "$(date +%F)"
|
||||
|
||||
- name: Generate CHANGELOG
|
||||
env:
|
||||
VERSION: ${{ inputs.version }}
|
||||
run: git-cliff --tag "v$VERSION" -o CHANGELOG.md
|
||||
|
||||
- name: Generate release notes
|
||||
env:
|
||||
VERSION: ${{ inputs.version }}
|
||||
run: git-cliff --unreleased --tag "v$VERSION" --strip header -o RELEASE_NOTES.md
|
||||
|
||||
- name: Upload release notes
|
||||
uses: actions/upload-artifact@ea165f8d65b6e75b540449e92b4886f43607fa02 # v4
|
||||
with:
|
||||
name: release-notes
|
||||
path: RELEASE_NOTES.md
|
||||
retention-days: 1
|
||||
if-no-files-found: error
|
||||
|
||||
- name: Show diff (dry run)
|
||||
if: ${{ inputs.dry_run }}
|
||||
run: git --no-pager diff
|
||||
|
||||
- name: Commit & push version bump
|
||||
if: ${{ !inputs.dry_run }}
|
||||
env:
|
||||
VERSION: ${{ inputs.version }}
|
||||
run: |
|
||||
rm -f RELEASE_NOTES.md
|
||||
git add -A
|
||||
git commit -m "chore: release v$VERSION"
|
||||
git push origin HEAD:main
|
||||
|
||||
build:
|
||||
needs: prepare
|
||||
name: build-${{ matrix.target }}
|
||||
strategy:
|
||||
fail-fast: false
|
||||
matrix:
|
||||
include:
|
||||
- target: x86_64-unknown-linux-gnu
|
||||
os: ubuntu-latest
|
||||
kind: linux
|
||||
deb_suffix: amd64
|
||||
- target: aarch64-unknown-linux-gnu
|
||||
os: ubuntu-24.04-arm
|
||||
kind: linux
|
||||
deb_suffix: arm64
|
||||
- target: aarch64-apple-darwin
|
||||
os: macos-latest
|
||||
kind: macos
|
||||
features: "--features smb-vendored"
|
||||
- target: x86_64-apple-darwin
|
||||
os: macos-latest
|
||||
kind: macos
|
||||
features: "--no-default-features --features keyring"
|
||||
- target: x86_64-pc-windows-msvc
|
||||
os: windows-latest
|
||||
kind: windows
|
||||
- target: aarch64-pc-windows-msvc
|
||||
os: windows-11-arm
|
||||
kind: windows
|
||||
runs-on: ${{ matrix.os }}
|
||||
env:
|
||||
VERSION: ${{ needs.prepare.outputs.version }}
|
||||
TARGET: ${{ matrix.target }}
|
||||
FEATURES: ${{ matrix.features }}
|
||||
steps:
|
||||
- uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
ref: ${{ inputs.dry_run && github.sha || 'main' }}
|
||||
persist-credentials: false
|
||||
fetch-depth: 0
|
||||
fetch-tags: true
|
||||
- uses: dtolnay/rust-toolchain@29eef336d9b2848a0b548edc03f92a220660cdb8 # stable
|
||||
with:
|
||||
targets: ${{ matrix.target }}
|
||||
|
||||
# ---- Linux: native per-arch build (x86_64 on ubuntu-latest, aarch64 on ubuntu-24.04-arm) ----
|
||||
- name: Install dependencies (Linux)
|
||||
if: matrix.kind == 'linux'
|
||||
run: |
|
||||
sudo apt-get update
|
||||
sudo apt-get install -y \
|
||||
make \
|
||||
libgit2-dev \
|
||||
build-essential \
|
||||
pkg-config \
|
||||
libbsd-dev \
|
||||
libcap-dev \
|
||||
libcups2-dev \
|
||||
libgnutls28-dev \
|
||||
libicu-dev \
|
||||
libjansson-dev \
|
||||
libkeyutils-dev \
|
||||
libldap2-dev \
|
||||
zlib1g-dev \
|
||||
libpam0g-dev \
|
||||
libacl1-dev \
|
||||
libarchive-dev \
|
||||
flex \
|
||||
bison \
|
||||
libntirpc-dev \
|
||||
libtracker-sparql-3.0-dev \
|
||||
libglib2.0-dev \
|
||||
libdbus-1-dev \
|
||||
libsasl2-dev \
|
||||
libunistring-dev \
|
||||
cpanminus
|
||||
sudo cpanm Parse::Yapp::Driver
|
||||
cargo install cargo-deb
|
||||
- name: Build (Linux)
|
||||
if: matrix.kind == 'linux'
|
||||
run: cargo build --release --features smb-vendored --target "$TARGET"
|
||||
- name: Build deb (Linux)
|
||||
if: matrix.kind == 'linux'
|
||||
run: cargo deb --no-build --target "$TARGET" --features smb-vendored
|
||||
|
||||
# ---- macOS ----
|
||||
- name: Install deps (macOS)
|
||||
if: matrix.kind == 'macos'
|
||||
run: |
|
||||
brew update
|
||||
brew install bison cpanminus cups flex gettext gmp gnutls icu4c jansson \
|
||||
libarchive libbsd libunistring libgit2 libtirpc openldap pkg-config zlib
|
||||
for p in bison cups flex gettext gmp gnutls icu4c jansson libarchive \
|
||||
libbsd libgit2 libtirpc libunistring openldap zlib; do brew link --force "$p"; done
|
||||
cpanm Parse::Yapp::Driver
|
||||
- name: Build (macOS)
|
||||
if: matrix.kind == 'macos'
|
||||
run: cargo build --release $FEATURES --target "$TARGET"
|
||||
|
||||
# ---- Windows ----
|
||||
- name: Build (Windows)
|
||||
if: matrix.kind == 'windows'
|
||||
run: cargo build --release --features smb-vendored --target "$env:TARGET"
|
||||
|
||||
# ---- Package posix (tar.gz) ----
|
||||
- name: Package (posix)
|
||||
if: matrix.kind != 'windows'
|
||||
run: |
|
||||
mkdir -p artifact
|
||||
cp "target/$TARGET/release/termscp" artifact/termscp
|
||||
tar -czf "artifact/termscp-v$VERSION-$TARGET.tar.gz" -C artifact termscp
|
||||
shasum -a 256 "artifact/termscp-v$VERSION-$TARGET.tar.gz" | awk '{print $1}' > "artifact/$TARGET.sha256"
|
||||
|
||||
# ---- Package windows (zip) ----
|
||||
- name: Package (windows)
|
||||
if: matrix.kind == 'windows'
|
||||
shell: pwsh
|
||||
run: |
|
||||
New-Item -ItemType Directory -Force artifact | Out-Null
|
||||
Copy-Item "target/$env:TARGET/release/termscp.exe" artifact/termscp.exe
|
||||
Compress-Archive -Path artifact/termscp.exe -DestinationPath "artifact/termscp-v$env:VERSION-$env:TARGET.zip"
|
||||
(Get-FileHash "artifact/termscp-v$env:VERSION-$env:TARGET.zip" -Algorithm SHA256).Hash.ToLower() | Out-File -NoNewline "artifact/$env:TARGET.sha256"
|
||||
|
||||
- name: Move deb into artifact dir (Linux)
|
||||
if: matrix.kind == 'linux'
|
||||
run: cp target/"$TARGET"/debian/*.deb artifact/
|
||||
|
||||
- name: Upload build artifacts
|
||||
uses: actions/upload-artifact@ea165f8d65b6e75b540449e92b4886f43607fa02 # v4
|
||||
with:
|
||||
name: build-${{ matrix.target }}
|
||||
path: artifact/*
|
||||
retention-days: 1
|
||||
if-no-files-found: error
|
||||
|
||||
publish-homebrew:
|
||||
needs: [prepare, build]
|
||||
runs-on: ubuntu-latest
|
||||
env:
|
||||
VERSION: ${{ needs.prepare.outputs.version }}
|
||||
steps:
|
||||
- name: Download build artifacts
|
||||
uses: actions/download-artifact@d3f86a106a0bac45b974a628896c90dbdf5c8093 # v4
|
||||
with:
|
||||
pattern: build-*
|
||||
path: dl
|
||||
merge-multiple: true
|
||||
|
||||
- name: Checkout homebrew tap
|
||||
uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
repository: veeso/homebrew-termscp
|
||||
token: ${{ secrets.RELEASE_PAT }}
|
||||
path: tap
|
||||
persist-credentials: true
|
||||
|
||||
- name: Rewrite formula
|
||||
run: |
|
||||
set -euo pipefail
|
||||
cd "$GITHUB_WORKSPACE"
|
||||
SHA_MAC_ARM=$(cat dl/aarch64-apple-darwin.sha256)
|
||||
SHA_MAC_X64=$(cat dl/x86_64-apple-darwin.sha256)
|
||||
SHA_LIN_ARM=$(cat dl/aarch64-unknown-linux-gnu.sha256)
|
||||
SHA_LIN_X64=$(cat dl/x86_64-unknown-linux-gnu.sha256)
|
||||
BASE="https://github.com/veeso/termscp/releases/latest/download"
|
||||
cat > tap/Formula/termscp.rb <<EOF
|
||||
class Termscp < Formula
|
||||
desc "A feature rich terminal file transfer and explorer with support for SCP/SFTP/FTP/S3/Kube/SMB/WebDAV"
|
||||
homepage "https://termscp.rs/"
|
||||
license "MIT"
|
||||
version "$VERSION"
|
||||
|
||||
on_macos do
|
||||
depends_on "bison"
|
||||
depends_on "cups"
|
||||
depends_on "flex"
|
||||
depends_on "gettext"
|
||||
depends_on "gmp"
|
||||
depends_on "gnutls"
|
||||
depends_on "icu4c"
|
||||
depends_on "jansson"
|
||||
depends_on "libarchive"
|
||||
depends_on "libbsd"
|
||||
depends_on "libgit2"
|
||||
depends_on "libtirpc"
|
||||
depends_on "libunistring"
|
||||
depends_on "openldap"
|
||||
depends_on "zlib"
|
||||
|
||||
on_arm do
|
||||
url "$BASE/termscp-v$VERSION-aarch64-apple-darwin.tar.gz"
|
||||
sha256 "$SHA_MAC_ARM"
|
||||
end
|
||||
on_intel do
|
||||
url "$BASE/termscp-v$VERSION-x86_64-apple-darwin.tar.gz"
|
||||
sha256 "$SHA_MAC_X64"
|
||||
end
|
||||
end
|
||||
|
||||
on_linux do
|
||||
depends_on "dbus"
|
||||
|
||||
on_arm do
|
||||
url "$BASE/termscp-v$VERSION-aarch64-unknown-linux-gnu.tar.gz"
|
||||
sha256 "$SHA_LIN_ARM"
|
||||
end
|
||||
on_intel do
|
||||
url "$BASE/termscp-v$VERSION-x86_64-unknown-linux-gnu.tar.gz"
|
||||
sha256 "$SHA_LIN_X64"
|
||||
end
|
||||
end
|
||||
|
||||
def install
|
||||
bin.install "termscp"
|
||||
end
|
||||
end
|
||||
EOF
|
||||
|
||||
- name: Show formula (dry run)
|
||||
if: ${{ inputs.dry_run }}
|
||||
run: cat tap/Formula/termscp.rb
|
||||
|
||||
- name: Commit & push formula
|
||||
if: ${{ !inputs.dry_run }}
|
||||
run: |
|
||||
cd tap
|
||||
git config user.name "veeso"
|
||||
git config user.email "christian.visintin@veeso.dev"
|
||||
git add Formula/termscp.rb
|
||||
git commit -m "termscp $VERSION"
|
||||
git push
|
||||
|
||||
release:
|
||||
needs: [prepare, build]
|
||||
runs-on: ubuntu-latest
|
||||
permissions:
|
||||
contents: write
|
||||
env:
|
||||
VERSION: ${{ needs.prepare.outputs.version }}
|
||||
steps:
|
||||
- uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
token: ${{ secrets.RELEASE_PAT }}
|
||||
ref: ${{ inputs.dry_run && github.sha || 'main' }}
|
||||
persist-credentials: true
|
||||
|
||||
- name: Download build artifacts
|
||||
uses: actions/download-artifact@d3f86a106a0bac45b974a628896c90dbdf5c8093 # v4
|
||||
with:
|
||||
pattern: build-*
|
||||
path: dl
|
||||
merge-multiple: true
|
||||
|
||||
- name: Download release notes
|
||||
uses: actions/download-artifact@d3f86a106a0bac45b974a628896c90dbdf5c8093 # v4
|
||||
with:
|
||||
name: release-notes
|
||||
path: notes
|
||||
|
||||
- name: Patch chocolatey checksums & pack
|
||||
run: |
|
||||
set -euo pipefail
|
||||
SHA_WIN_X64=$(cat dl/x86_64-pc-windows-msvc.sha256)
|
||||
SHA_WIN_ARM=$(cat dl/aarch64-pc-windows-msvc.sha256)
|
||||
PS=dist/chocolatey/tools/chocolateyinstall.ps1
|
||||
# arm checksum is the first $checksum line, x64 the second (matches file order)
|
||||
SHA_WIN_ARM="$SHA_WIN_ARM" SHA_WIN_X64="$SHA_WIN_X64" \
|
||||
perl -0pi -e 'BEGIN{our $n=0} s/(\$checksum\s*=\s*'"'"')[0-9a-f]*('"'"')/ $n++==0 ? "${1}$ENV{SHA_WIN_ARM}${2}" : "${1}$ENV{SHA_WIN_X64}${2}" /ge' "$PS"
|
||||
docker run --rm -v "$PWD/dist/chocolatey:/work" -w /work \
|
||||
chocolatey/choco:latest choco pack --output-directory /work
|
||||
|
||||
- name: Assemble release assets
|
||||
run: |
|
||||
mkdir -p out
|
||||
cp dl/*.tar.gz dl/*.deb dl/*.zip out/ 2>/dev/null || true
|
||||
cp dist/chocolatey/*.nupkg out/
|
||||
|
||||
- name: Upload assets artifact (dry run)
|
||||
if: ${{ inputs.dry_run }}
|
||||
uses: actions/upload-artifact@ea165f8d65b6e75b540449e92b4886f43607fa02 # v4
|
||||
with:
|
||||
name: release-assets-dryrun
|
||||
path: out/*
|
||||
retention-days: 3
|
||||
|
||||
- name: Create GitHub release
|
||||
if: ${{ !inputs.dry_run }}
|
||||
env:
|
||||
GH_TOKEN: ${{ secrets.RELEASE_PAT }}
|
||||
run: |
|
||||
gh release create "v$VERSION" out/* \
|
||||
--title "v$VERSION" \
|
||||
--notes-file notes/RELEASE_NOTES.md
|
||||
|
||||
publish-crate:
|
||||
needs: [prepare, release]
|
||||
if: ${{ !inputs.dry_run }}
|
||||
runs-on: ubuntu-latest
|
||||
permissions:
|
||||
contents: read
|
||||
id-token: write
|
||||
env:
|
||||
VERSION: ${{ needs.prepare.outputs.version }}
|
||||
steps:
|
||||
- uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
ref: main
|
||||
persist-credentials: false
|
||||
fetch-depth: 0
|
||||
fetch-tags: true
|
||||
- uses: dtolnay/rust-toolchain@29eef336d9b2848a0b548edc03f92a220660cdb8 # stable
|
||||
|
||||
- name: Install dependencies (Linux)
|
||||
run: |
|
||||
sudo apt-get update
|
||||
sudo apt-get install -y \
|
||||
make \
|
||||
libgit2-dev \
|
||||
build-essential \
|
||||
pkg-config \
|
||||
libbsd-dev \
|
||||
libcap-dev \
|
||||
libcups2-dev \
|
||||
libgnutls28-dev \
|
||||
libicu-dev \
|
||||
libjansson-dev \
|
||||
libkeyutils-dev \
|
||||
libldap2-dev \
|
||||
zlib1g-dev \
|
||||
libpam0g-dev \
|
||||
libacl1-dev \
|
||||
libarchive-dev \
|
||||
flex \
|
||||
bison \
|
||||
libntirpc-dev \
|
||||
libtracker-sparql-3.0-dev \
|
||||
libglib2.0-dev \
|
||||
libdbus-1-dev \
|
||||
libsasl2-dev \
|
||||
libunistring-dev \
|
||||
cpanminus
|
||||
sudo cpanm Parse::Yapp::Driver
|
||||
|
||||
- name: Authenticate to crates.io
|
||||
id: auth
|
||||
uses: rust-lang/crates-io-auth-action@bbd81622f20ce9e2dd9622e3218b975523e45bbe # v1.0.4
|
||||
|
||||
- name: Publish to crates.io
|
||||
env:
|
||||
CARGO_REGISTRY_TOKEN: ${{ steps.auth.outputs.token }}
|
||||
run: cargo publish --features smb-vendored
|
||||
|
||||
publish-choco:
|
||||
needs: [prepare, release]
|
||||
if: ${{ !inputs.dry_run }}
|
||||
runs-on: windows-latest
|
||||
env:
|
||||
VERSION: ${{ needs.prepare.outputs.version }}
|
||||
steps:
|
||||
- name: Download nupkg from release
|
||||
env:
|
||||
GH_TOKEN: ${{ secrets.RELEASE_PAT }}
|
||||
run: gh release download "v$env:VERSION" --repo veeso/termscp --pattern "*.nupkg"
|
||||
|
||||
- name: Push to Chocolatey
|
||||
env:
|
||||
CHOCO_API_KEY: ${{ secrets.CHOCO_API_KEY }}
|
||||
run: |
|
||||
choco apikey --key $env:CHOCO_API_KEY --source https://push.chocolatey.org/
|
||||
choco push (Get-ChildItem *.nupkg).Name --source https://push.chocolatey.org/
|
||||
@@ -0,0 +1,38 @@
|
||||
name: Site
|
||||
|
||||
on:
|
||||
pull_request:
|
||||
branches: [main]
|
||||
push:
|
||||
branches: [main]
|
||||
|
||||
permissions:
|
||||
contents: read
|
||||
|
||||
defaults:
|
||||
run:
|
||||
working-directory: site
|
||||
|
||||
jobs:
|
||||
build-site:
|
||||
runs-on: ubuntu-latest
|
||||
|
||||
steps:
|
||||
- uses: actions/checkout@df4cb1c069e1874edd31b4311f1884172cec0e10 # v6
|
||||
with:
|
||||
persist-credentials: false
|
||||
- uses: actions/setup-node@49933ea5288caeca8642d1e84afbd3f7d6820020 # v4.4.0
|
||||
with:
|
||||
node-version: 24
|
||||
cache: npm
|
||||
cache-dependency-path: site/package-lock.json
|
||||
- name: Install dependencies
|
||||
run: npm ci
|
||||
- name: Format
|
||||
run: npm run format:check
|
||||
- name: Lint
|
||||
run: npm run check
|
||||
- name: Test
|
||||
run: npm test --if-present
|
||||
- name: Build
|
||||
run: npm run build
|
||||
@@ -3,6 +3,9 @@ on:
|
||||
schedule:
|
||||
- cron: "30 1 * * *"
|
||||
|
||||
permissions:
|
||||
contents: read
|
||||
|
||||
jobs:
|
||||
close-issues:
|
||||
runs-on: ubuntu-latest
|
||||
@@ -10,7 +13,7 @@ jobs:
|
||||
issues: write
|
||||
pull-requests: write
|
||||
steps:
|
||||
- uses: actions/stale@v4.1.1
|
||||
- uses: actions/stale@a20b814fb01b71def3bd6f56e7494d667ddf28da # v4.1.1
|
||||
with:
|
||||
days-before-issue-stale: 30
|
||||
days-before-issue-close: 7
|
||||
@@ -21,3 +24,4 @@ jobs:
|
||||
days-before-pr-close: -1
|
||||
repo-token: ${{ secrets.GITHUB_TOKEN }}
|
||||
exempt-issue-labels: "backlog"
|
||||
exempt-all-milestones: true
|
||||
|
||||
@@ -1,43 +0,0 @@
|
||||
# Simple workflow for deploying static content to GitHub Pages
|
||||
name: Deploy static content to Pages
|
||||
|
||||
on:
|
||||
# Runs on pushes targeting the default branch
|
||||
push:
|
||||
branches: ["main"]
|
||||
paths:
|
||||
- "./site/**/*"
|
||||
|
||||
# Allows you to run this workflow manually from the Actions tab
|
||||
workflow_dispatch:
|
||||
|
||||
# Sets permissions of the GITHUB_TOKEN to allow deployment to GitHub Pages
|
||||
permissions:
|
||||
contents: read
|
||||
pages: write
|
||||
id-token: write
|
||||
|
||||
# Allow one concurrent deployment
|
||||
concurrency:
|
||||
group: "pages"
|
||||
cancel-in-progress: true
|
||||
|
||||
jobs:
|
||||
# Single deploy job since we're just deploying
|
||||
deploy:
|
||||
environment:
|
||||
name: github-pages
|
||||
url: ${{ steps.deployment.outputs.page_url }}
|
||||
runs-on: ubuntu-latest
|
||||
steps:
|
||||
- name: Checkout
|
||||
uses: actions/checkout@v3
|
||||
- name: Setup Pages
|
||||
uses: actions/configure-pages@v2
|
||||
- name: Upload artifact
|
||||
uses: actions/upload-pages-artifact@v1
|
||||
with:
|
||||
path: "./site/"
|
||||
- name: Deploy to GitHub Pages
|
||||
id: deployment
|
||||
uses: actions/deploy-pages@v1
|
||||
@@ -1,32 +0,0 @@
|
||||
name: Windows
|
||||
|
||||
on:
|
||||
pull_request:
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
push:
|
||||
paths-ignore:
|
||||
- "*.md"
|
||||
- "./site/**/*"
|
||||
|
||||
env:
|
||||
CARGO_TERM_COLOR: always
|
||||
|
||||
jobs:
|
||||
build:
|
||||
runs-on: windows-2019
|
||||
|
||||
steps:
|
||||
- uses: actions/checkout@v2
|
||||
- uses: actions-rs/toolchain@v1
|
||||
with:
|
||||
toolchain: stable
|
||||
override: true
|
||||
components: rustfmt, clippy
|
||||
- name: Build
|
||||
run: cargo build
|
||||
- name: Run tests
|
||||
run: cargo test --verbose --features github-actions
|
||||
- name: Clippy
|
||||
run: cargo clippy -- -Dwarnings
|
||||
@@ -24,3 +24,11 @@ dist/pkgs/arch/*.tar.gz
|
||||
|
||||
dist/pkgs/
|
||||
dist/build/macos/openssl/
|
||||
|
||||
.idea/
|
||||
.claude/
|
||||
|
||||
|
||||
# brainstorming visual companion
|
||||
.superpowers/
|
||||
docs/*/book/
|
||||
|
||||
@@ -0,0 +1,21 @@
|
||||
{
|
||||
// Markdown lint config for the termscp docs site (mdBook).
|
||||
"config": {
|
||||
// Line length is impractical for keyboard/style tables and long prose;
|
||||
// mdBook reflows in the browser, so we don't enforce a hard wrap.
|
||||
"MD013": false,
|
||||
// Table column alignment can't be satisfied for CJK (zh-CN) content:
|
||||
// markdownlint counts code points while CJK glyphs are double-width, so a
|
||||
// visually aligned table never matches. Rendering is unaffected.
|
||||
"MD060": false
|
||||
},
|
||||
"globs": ["docs/en-US/**/*.md", "docs/zh-CN/**/*.md"],
|
||||
"ignores": [
|
||||
// mdBook build output.
|
||||
"**/book/**",
|
||||
// SUMMARY.md uses multiple level-1 headings as mdBook part titles.
|
||||
"**/SUMMARY.md",
|
||||
// GitHub READMEs (not part of the book) keep centered HTML badges.
|
||||
"**/README.md"
|
||||
]
|
||||
}
|
||||
@@ -0,0 +1,111 @@
|
||||
# CLAUDE.md
|
||||
|
||||
This file provides guidance to Claude Code (claude.ai/code) when working with code in this repository.
|
||||
|
||||
## Project Overview
|
||||
|
||||
termscp is a terminal file transfer client with a TUI (Terminal User Interface), supporting SFTP, SCP, FTP/FTPS, Kube, S3, SMB, and WebDAV protocols. It features a dual-pane file explorer (local + remote), bookmarks, system keyring integration, file watching/sync, an embedded terminal, and customizable themes.
|
||||
|
||||
- **Language**: Rust (edition 2024, MSRV 1.89.0)
|
||||
- **UI Framework**: tuirealm v3 (built on crossterm)
|
||||
- **File Transfer**: remotefs ecosystem
|
||||
|
||||
## Build & Development Commands
|
||||
|
||||
```bash
|
||||
# Build
|
||||
cargo build
|
||||
cargo build --release
|
||||
cargo build --no-default-features # minimal build without SMB/keyring
|
||||
|
||||
# Test (CI-equivalent)
|
||||
cargo test --no-default-features --features github-actions --no-fail-fast
|
||||
|
||||
# Run a single test
|
||||
cargo test <test_name> -- --nocapture
|
||||
|
||||
# Run tests for a module
|
||||
cargo test --lib filetransfer::
|
||||
cargo test --lib config::params::tests
|
||||
|
||||
# Lint
|
||||
cargo clippy -- -Dwarnings
|
||||
|
||||
# Format
|
||||
cargo fmt --all -- --check # check only
|
||||
cargo fmt --all # fix
|
||||
```
|
||||
|
||||
### System Dependencies (for building)
|
||||
|
||||
- **Linux**: `libdbus-1-dev`, `libsmbclient-dev`
|
||||
- **macOS**: `pkg-config`, `samba` (brew, with force link)
|
||||
|
||||
## Feature Flags
|
||||
|
||||
- **`smb`** (default): SMB/Samba protocol support
|
||||
- **`keyring`** (default): System keyring integration for password storage
|
||||
- **`smb-vendored`**: Vendored SMB library (for static builds)
|
||||
- **`github-actions`**: CI flag — disables real keyring in tests, uses file-based storage
|
||||
- **`isolated-tests`**: For parallel test isolation
|
||||
|
||||
## Architecture
|
||||
|
||||
### Application Lifecycle
|
||||
|
||||
```
|
||||
main.rs → parse CLI args → ActivityManager::new() → ActivityManager::run()
|
||||
↓
|
||||
Activity loop (draw → poll → update)
|
||||
├── AuthActivity (login/bookmarks)
|
||||
├── FileTransferActivity (dual-pane explorer)
|
||||
└── SetupActivity (configuration)
|
||||
```
|
||||
|
||||
`ActivityManager` owns a `Context` that is passed between activities. Each activity takes ownership of the Context on `on_create()` and returns it on `on_destroy()`.
|
||||
|
||||
### Key Modules
|
||||
|
||||
| Module | Path | Purpose |
|
||||
|--------|------|---------|
|
||||
| **activity_manager** | `src/activity_manager.rs` | Orchestrates activity lifecycle and transitions |
|
||||
| **ui/activities** | `src/ui/activities/{auth,filetransfer,setup}/` | Three main screens, each implementing the `Activity` trait |
|
||||
| **ui/context** | `src/ui/context.rs` | Shared `Context` struct (terminal, config, bookmarks, theme) |
|
||||
| **filetransfer** | `src/filetransfer/` | Protocol enum, `RemoteFsBuilder`, connection parameters |
|
||||
| **host** | `src/host/` | `HostBridge` trait — abstracts local (`Localhost`) and remote (`RemoteBridged`) file operations |
|
||||
| **explorer** | `src/explorer/` | `FileExplorer` — directory navigation, sorting, filtering, transfer queue |
|
||||
| **system** | `src/system/` | `BookmarksClient`, `ConfigClient`, `ThemeProvider`, `SshKeyStorage`, `KeyStorage` trait |
|
||||
| **config** | `src/config/` | TOML-based serialization for themes, bookmarks, user params |
|
||||
|
||||
### Core Traits
|
||||
|
||||
- **`Activity`** (`src/ui/activities/mod.rs`): `on_create`, `on_draw`, `will_umount`, `on_destroy` — UI screen lifecycle
|
||||
- **`HostBridge`** (`src/host/bridge.rs`): Unified file operations interface (connect, list_dir, open_file, mkdir, remove, rename, copy, etc.)
|
||||
- **`KeyStorage`** (`src/system/keys/mod.rs`): `get_key`/`set_key` — password storage abstraction (keyring or encrypted file fallback)
|
||||
|
||||
### Conditional Compilation
|
||||
|
||||
The `build.rs` defines cfg aliases via `cfg_aliases`:
|
||||
- `posix`, `macos`, `linux`, `win` — platform shortcuts
|
||||
- `smb`, `smb_unix`, `smb_windows` — feature + platform combinations
|
||||
|
||||
Platform-specific dependencies: SSH and FTP crates use different TLS backends on Unix vs Windows. SMB support is completely gated behind the `smb` feature flag.
|
||||
|
||||
### File Transfer Protocols
|
||||
|
||||
`FileTransferProtocol` enum maps to protocol-specific parameter types (`ProtocolParams` enum) and `RemoteFsBuilder` constructs the appropriate `RemoteFs` client. Each protocol has its own params struct (e.g., `GenericProtocolParams` for SSH-based, `AwsS3Params`, `KubeProtocolParams`, `SmbParams`, `WebDAVProtocolParams`).
|
||||
|
||||
## Code Conventions
|
||||
|
||||
- **rustfmt**: `group_imports = "StdExternalCrate"`, `imports_granularity = "Module"`
|
||||
- **Error handling**: Custom error types with `thiserror`, module-level Result aliases (e.g., `HostResult<T>`)
|
||||
- **Builder pattern**: Used for `RemoteFsBuilder`, `HostBridgeBuilder`
|
||||
- **Client pattern**: System services wrapped as clients (`BookmarksClient`, `ConfigClient`)
|
||||
- **Tests**: Unit tests in `#[cfg(test)]` blocks within source files. Tests requiring serial execution use `#[serial]` from `serial_test`
|
||||
- **Encryption**: Bookmark passwords encrypted with `magic-crypt`; keys stored in system keyring or encrypted file
|
||||
|
||||
## Other conventions
|
||||
|
||||
- Always run `cargo +nightly fmt --all` and `cargo clippy --no-default-features -- -Dwarnings` after modifying Rust code
|
||||
- Always put plans to `./.claude/plans/`
|
||||
- When changing behavior that is documented under `docs/` (paths, config keys, commands, flags, etc.), update BOTH `docs/en-US/` and `docs/zh-CN/` to keep the translations in sync
|
||||
@@ -2,75 +2,131 @@
|
||||
|
||||
## Our Pledge
|
||||
|
||||
In the interest of fostering an open and welcoming environment, we as
|
||||
contributors and maintainers pledge to making participation in our project and
|
||||
our community a harassment-free experience for everyone, regardless of age, body
|
||||
size, disability, ethnicity, sex characteristics, gender identity and expression,
|
||||
level of experience, education, socio-economic status, nationality, personal
|
||||
appearance, race, religion, or sexual identity and orientation.
|
||||
We as members, contributors, and leaders pledge to make participation in our
|
||||
community a harassment-free experience for everyone, regardless of age, body
|
||||
size, visible or invisible disability, ethnicity, sex characteristics, gender
|
||||
identity and expression, level of experience, education, socio-economic status,
|
||||
nationality, personal appearance, race, caste, color, religion, or sexual
|
||||
identity and orientation.
|
||||
|
||||
We pledge to act and interact in ways that contribute to an open, welcoming,
|
||||
diverse, inclusive, and healthy community.
|
||||
|
||||
## Our Standards
|
||||
|
||||
Examples of behavior that contributes to creating a positive environment
|
||||
include:
|
||||
Examples of behavior that contributes to a positive environment for our
|
||||
community include:
|
||||
|
||||
* Using welcoming and inclusive language
|
||||
* Being respectful of differing viewpoints and experiences
|
||||
* Gracefully accepting constructive criticism
|
||||
* Focusing on what is best for the community
|
||||
* Showing empathy towards other community members
|
||||
* Demonstrating empathy and kindness toward other people
|
||||
* Being respectful of differing opinions, viewpoints, and experiences
|
||||
* Giving and gracefully accepting constructive feedback
|
||||
* Accepting responsibility and apologizing to those affected by our mistakes,
|
||||
and learning from the experience
|
||||
* Focusing on what is best not just for us as individuals, but for the overall
|
||||
community
|
||||
|
||||
Examples of unacceptable behavior by participants include:
|
||||
Examples of unacceptable behavior include:
|
||||
|
||||
* The use of sexualized language or imagery and unwelcome sexual attention or
|
||||
advances
|
||||
* Trolling, insulting/derogatory comments, and personal or political attacks
|
||||
* The use of sexualized language or imagery, and sexual attention or advances of
|
||||
any kind
|
||||
* Trolling, insulting or derogatory comments, and personal or political attacks
|
||||
* Public or private harassment
|
||||
* Publishing others' private information, such as a physical or electronic
|
||||
address, without explicit permission
|
||||
* Publishing others' private information, such as a physical or email address,
|
||||
without their explicit permission
|
||||
* Other conduct which could reasonably be considered inappropriate in a
|
||||
professional setting
|
||||
professional setting
|
||||
|
||||
## Our Responsibilities
|
||||
## Enforcement Responsibilities
|
||||
|
||||
Project maintainers are responsible for clarifying the standards of acceptable
|
||||
behavior and are expected to take appropriate and fair corrective action in
|
||||
response to any instances of unacceptable behavior.
|
||||
Community leaders are responsible for clarifying and enforcing our standards of
|
||||
acceptable behavior and will take appropriate and fair corrective action in
|
||||
response to any behavior that they deem inappropriate, threatening, offensive,
|
||||
or harmful.
|
||||
|
||||
Project maintainers have the right and responsibility to remove, edit, or
|
||||
reject comments, commits, code, wiki edits, issues, and other contributions
|
||||
that are not aligned to this Code of Conduct, or to ban temporarily or
|
||||
permanently any contributor for other behaviors that they deem inappropriate,
|
||||
threatening, offensive, or harmful.
|
||||
Community leaders have the right and responsibility to remove, edit, or reject
|
||||
comments, commits, code, wiki edits, issues, and other contributions that are
|
||||
not aligned to this Code of Conduct, and will communicate reasons for moderation
|
||||
decisions when appropriate.
|
||||
|
||||
## Scope
|
||||
|
||||
This Code of Conduct applies both within project spaces and in public spaces
|
||||
when an individual is representing the project or its community. Examples of
|
||||
representing a project or community include using an official project e-mail
|
||||
address, posting via an official social media account, or acting as an appointed
|
||||
representative at an online or offline event. Representation of a project may be
|
||||
further defined and clarified by project maintainers.
|
||||
This Code of Conduct applies within all community spaces, and also applies when
|
||||
an individual is officially representing the community in public spaces.
|
||||
Examples of representing our community include using an official email address,
|
||||
posting via an official social media account, or acting as an appointed
|
||||
representative at an online or offline event.
|
||||
|
||||
## Enforcement
|
||||
|
||||
Instances of abusive, harassing, or otherwise unacceptable behavior may be
|
||||
reported by contacting the project team at christian.visintin1997@gmail.com. All
|
||||
complaints will be reviewed and investigated and will result in a response that
|
||||
is deemed necessary and appropriate to the circumstances. The project team is
|
||||
obligated to maintain confidentiality with regard to the reporter of an incident.
|
||||
Further details of specific enforcement policies may be posted separately.
|
||||
reported to the community leaders responsible for enforcement at
|
||||
[INSERT CONTACT METHOD].
|
||||
All complaints will be reviewed and investigated promptly and fairly.
|
||||
|
||||
Project maintainers who do not follow or enforce the Code of Conduct in good
|
||||
faith may face temporary or permanent repercussions as determined by other
|
||||
members of the project's leadership.
|
||||
All community leaders are obligated to respect the privacy and security of the
|
||||
reporter of any incident.
|
||||
|
||||
## Enforcement Guidelines
|
||||
|
||||
Community leaders will follow these Community Impact Guidelines in determining
|
||||
the consequences for any action they deem in violation of this Code of Conduct:
|
||||
|
||||
### 1. Correction
|
||||
|
||||
**Community Impact**: Use of inappropriate language or other behavior deemed
|
||||
unprofessional or unwelcome in the community.
|
||||
|
||||
**Consequence**: A private, written warning from community leaders, providing
|
||||
clarity around the nature of the violation and an explanation of why the
|
||||
behavior was inappropriate. A public apology may be requested.
|
||||
|
||||
### 2. Warning
|
||||
|
||||
**Community Impact**: A violation through a single incident or series of
|
||||
actions.
|
||||
|
||||
**Consequence**: A warning with consequences for continued behavior. No
|
||||
interaction with the people involved, including unsolicited interaction with
|
||||
those enforcing the Code of Conduct, for a specified period of time. This
|
||||
includes avoiding interactions in community spaces as well as external channels
|
||||
like social media. Violating these terms may lead to a temporary or permanent
|
||||
ban.
|
||||
|
||||
### 3. Temporary Ban
|
||||
|
||||
**Community Impact**: A serious violation of community standards, including
|
||||
sustained inappropriate behavior.
|
||||
|
||||
**Consequence**: A temporary ban from any sort of interaction or public
|
||||
communication with the community for a specified period of time. No public or
|
||||
private interaction with the people involved, including unsolicited interaction
|
||||
with those enforcing the Code of Conduct, is allowed during this period.
|
||||
Violating these terms may lead to a permanent ban.
|
||||
|
||||
### 4. Permanent Ban
|
||||
|
||||
**Community Impact**: Demonstrating a pattern of violation of community
|
||||
standards, including sustained inappropriate behavior, harassment of an
|
||||
individual, or aggression toward or disparagement of classes of individuals.
|
||||
|
||||
**Consequence**: A permanent ban from any sort of public interaction within the
|
||||
community.
|
||||
|
||||
## Attribution
|
||||
|
||||
This Code of Conduct is adapted from the [Contributor Covenant][homepage], version 1.4,
|
||||
available at <https://www.contributor-covenant.org/version/1/4/code-of-conduct.html>
|
||||
This Code of Conduct is adapted from the [Contributor Covenant][homepage],
|
||||
version 2.1, available at
|
||||
[https://www.contributor-covenant.org/version/2/1/code_of_conduct.html][v2.1].
|
||||
|
||||
Community Impact Guidelines were inspired by
|
||||
[Mozilla's code of conduct enforcement ladder][Mozilla CoC].
|
||||
|
||||
For answers to common questions about this code of conduct, see the FAQ at
|
||||
[https://www.contributor-covenant.org/faq][FAQ]. Translations are available at
|
||||
[https://www.contributor-covenant.org/translations][translations].
|
||||
|
||||
[homepage]: https://www.contributor-covenant.org
|
||||
|
||||
For answers to common questions about this code of conduct, see
|
||||
<https://www.contributor-covenant.org/faq>
|
||||
[v2.1]: https://www.contributor-covenant.org/version/2/1/code_of_conduct.html
|
||||
[Mozilla CoC]: https://github.com/mozilla/diversity
|
||||
[FAQ]: https://www.contributor-covenant.org/faq
|
||||
[translations]: https://www.contributor-covenant.org/translations
|
||||
|
||||
@@ -1,7 +1,7 @@
|
||||
# Contributing
|
||||
|
||||
Before contributing to this repository, please first discuss the change you wish to make via issue of this repository before making a change.
|
||||
Please note we have a [code of conduct](CODE_OF_CONDUCT.md), please follow it in all your interactions with the project.
|
||||
Please note we have a [code of conduct](CODE_OF_CONDUCT.md). Please follow it in all your interactions with the project.
|
||||
|
||||
- [Contributing](#contributing)
|
||||
- [Project mission](#project-mission)
|
||||
@@ -20,9 +20,13 @@ Please note we have a [code of conduct](CODE_OF_CONDUCT.md), please follow it in
|
||||
|
||||
## Project mission
|
||||
|
||||
termscp was born because, as a terminal lover and Linux user, I wanted something like WinSCP on Linux and on terminal. I my previous job I used SFTP/SCP pratically everyday and that made me to desire an application like termscp so much, that eventually I started to work on it in the spare time. I saw there was a very cool library to create terminal user interface (`tui-rs`), so I started to code it. I wrote termscp as an experiment, I designed kinda nothing at the time. I just said
|
||||
termscp was born because, as a terminal lover and Linux user, I wanted something like WinSCP on Linux and on terminal. At my previous job, I used SFTP/SCP practically everyday and that made me desire an application like termscp so much that eventually I started to work on it in my spare time.
|
||||
|
||||
> Ok, there must be a `FileTransfer` trait somehow, I'll have more views, so I'll use something like Android activities, and there must be a module to interact with the local host".
|
||||
I saw there was a very cool library to create terminal user interfaces (`tui-rs`, now `ratatui`), so I started to code it.
|
||||
|
||||
I wrote termscp as an experiment. I didn't design anything at the time. I just said,
|
||||
|
||||
> "Ok, there must be a FileTransfer trait somehow. I'll have more views, so I'll use something like Android activities, and there must be a module to interact with the local host."
|
||||
|
||||
And so in december 2020 I had the first version of termscp running and it worked, but was very simple, raw and minimal.
|
||||
A lot of things have changed since them, both the features the project provides and my personal view of this project.
|
||||
@@ -63,7 +67,7 @@ Don't set other labels to your issue, not even priority.
|
||||
|
||||
When you open a bug try to be the most precise as possible in describing your issue. I'm not saying you should always be that precise, since sometimes it's very easy for maintainers to understand what you're talking about. Just try to be reasonable to understand sometimes we might not know what you're talking about or we just don't have the technical knowledge you might think.
|
||||
Please always provide the environment you're working on and consider that we don't provide any support for older version of termscp, at least for those not classified as LTS (if we'll ever have them).
|
||||
If you can, provide the log file or the snippet involving your issue. You can find in the [user manual](docs/man.md) the location of the log file. Please, if you can, enable the **debug mode**, before submitting the log, in order to provide us with a better overview of the problem.
|
||||
If you can, provide the log file or the snippet involving your issue. You can find in the [user manual](https://docs.termscp.rs/en-US/configuration/logging.html) the location of the log file. Please, if you can, enable the **debug mode**, before submitting the log, in order to provide us with a better overview of the problem.
|
||||
Last but not least: the template I've written must be used. Full stop.
|
||||
|
||||
Maintainers will may add additional labels to your issue:
|
||||
@@ -134,7 +138,7 @@ Let's make it simple and clear:
|
||||
In addition to the process described for the PRs, I've also decided to introduce a list of guidelines to follow when writing the code, that should be followed:
|
||||
|
||||
1. **Let's stop the NPM apocalypse**: personally I'm against the abuse of dependencies we make in software projects and I think that NodeJS has opened the way to this drama (and has already gone too far). Nowadays nobody cares about adding hundreds of dependencies to their projects. Don't misunderstand me: I think that package managers are cool, but I'm totally against the abuse we're making of them. I think when we work on a project, we should try to use the minor quantity of dependencies as possible, especially because it's not hard to see how many libraries are getting abandoned right now, causing compatibility issues after a while. So please, when working on termscp, try not to add useless dependencies.
|
||||
2. **No C-bindings**: personally I think that Rust still relies too much on C. And that's bad, really bad. Many libraries in Rust are just wrappers to C libraries, which is a huge problem, especially considering this is a multiplatform project. Everytime you add a C-binding to your project, you're forcing your users to install additional libraries to their systems. Sometimes these libraries are already installed on their systems (as happens for libssh2 or openssl in this case), but sometimes not. So if you really have to add a dependency to this project, please AVOID completely adding C-bounded libraries.
|
||||
2. **No C-bindings**: personally I think that Rust still relies too much on C. And that's bad, really bad. Many libraries in Rust are just wrappers to C libraries, which is a huge problem, especially considering this is a multiplatform project. Everytime you add a C-binding to your project, you're forcing your users to install additional libraries to their systems. Sometimes these libraries are already installed on their systems (as happens for openssl in this case), but sometimes not. So if you really have to add a dependency to this project, please AVOID completely adding C-bounded libraries.
|
||||
3. **Test units matter**: Whenever you implement something new to this project, always implement test units which cover the most cases as possible.
|
||||
4. **Comments are useful**: Many people say that the code should be that simple to talk by itself about what it does, and comments should then be useless. I personally don't agree. I'm not saying they're wrong, but I'm just saying that this approach has, in my personal opinion, many aspects which are underrated:
|
||||
1. What's obvious for me, might not be for the others.
|
||||
@@ -142,7 +146,7 @@ In addition to the process described for the PRs, I've also decided to introduce
|
||||
|
||||
## Developer contributions guide
|
||||
|
||||
You can view the developer guide [here](docs/developer.md).
|
||||
You can view the developer guide [here](https://docs.termscp.rs/en-US/developer/developer.html).
|
||||
|
||||
---
|
||||
|
||||
|
||||
@@ -1,22 +1,17 @@
|
||||
[package]
|
||||
authors = ["Christian Visintin <christian.visintin@veeso.dev>"]
|
||||
categories = ["command-line-utilities"]
|
||||
description = "termscp is a feature rich terminal file transfer and explorer with support for SCP/SFTP/FTP/S3"
|
||||
edition = "2021"
|
||||
homepage = "https://termscp.veeso.dev"
|
||||
include = ["src/**/*", "LICENSE", "README.md", "CHANGELOG.md"]
|
||||
keywords = [
|
||||
"scp-client",
|
||||
"sftp-client",
|
||||
"ftp-client",
|
||||
"winscp",
|
||||
"command-line-utility",
|
||||
]
|
||||
license = "MIT"
|
||||
name = "termscp"
|
||||
readme = "README.md"
|
||||
version = "1.1.1"
|
||||
edition = "2024"
|
||||
authors = ["Christian Visintin <christian.visintin@veeso.dev>"]
|
||||
description = "termscp is a feature rich terminal file transfer and explorer with support for SCP/SFTP/FTP/Kube/S3/WebDAV"
|
||||
license = "MIT"
|
||||
repository = "https://github.com/veeso/termscp"
|
||||
version = "0.12.3"
|
||||
categories = ["command-line-utilities"]
|
||||
homepage = "https://termscp.rs"
|
||||
include = ["src/**/*", "build.rs", "LICENSE", "README.md", "CHANGELOG.md"]
|
||||
keywords = ["terminal", "ftp", "scp", "sftp", "tui"]
|
||||
readme = "README.md"
|
||||
rust-version = "1.89.0"
|
||||
|
||||
[package.metadata.rpm]
|
||||
package = "termscp"
|
||||
@@ -29,84 +24,121 @@ termscp = { path = "/usr/bin/termscp" }
|
||||
|
||||
[package.metadata.deb]
|
||||
maintainer = "Christian Visintin <christian.visintin@veeso.dev>"
|
||||
copyright = "2022, Christian Visintin <christian.visintin@veeso.dev>"
|
||||
copyright = "2025, Christian Visintin <christian.visintin@veeso.dev>"
|
||||
extended-description-file = "docs/misc/README.deb.txt"
|
||||
|
||||
[features]
|
||||
default = ["keyring", "smb"]
|
||||
github-actions = []
|
||||
isolated-tests = []
|
||||
keyring = []
|
||||
smb = ["dep:remotefs-smb"]
|
||||
smb-vendored = ["remotefs-smb/vendored"]
|
||||
|
||||
[dependencies]
|
||||
aes = "0.9"
|
||||
aes-gcm = "0.10"
|
||||
argh = "0.1"
|
||||
base64 = "0.22"
|
||||
bitflags = "2"
|
||||
bytesize = "2"
|
||||
cbc = { version = "0.2", features = ["alloc"] }
|
||||
chrono = "0.4"
|
||||
content_inspector = "0.2"
|
||||
dirs = "6"
|
||||
edit = "0.1"
|
||||
filetime = "0.2"
|
||||
keyring-core = "1"
|
||||
lazy-regex = "3"
|
||||
log = "0.4"
|
||||
md-5 = "0.11"
|
||||
notify = "8"
|
||||
notify-rust = { version = "4", default-features = false, features = ["d"] }
|
||||
nucleo = "0.5"
|
||||
open = "5"
|
||||
rand = "0.10"
|
||||
regex = "1"
|
||||
remotefs = "0.3"
|
||||
remotefs-aws-s3 = "0.4"
|
||||
remotefs-kube = "0.4"
|
||||
remotefs-smb = { version = "0.3", optional = true }
|
||||
remotefs-ssh = { version = "0.8", default-features = false, features = [
|
||||
"russh",
|
||||
] }
|
||||
remotefs-webdav = "0.2"
|
||||
rpassword = "7"
|
||||
self_update = { version = "0.42", default-features = false, features = [
|
||||
"archive-tar",
|
||||
"archive-zip",
|
||||
"compression-flate2",
|
||||
"compression-zip-deflate",
|
||||
"rustls",
|
||||
] }
|
||||
semver = "1"
|
||||
serde = { version = "1", features = ["derive"] }
|
||||
shellexpand = "3"
|
||||
simplelog = "0.12"
|
||||
ssh2-config = "0.7"
|
||||
tempfile = "3"
|
||||
thiserror = "2"
|
||||
tokio = { version = "1", features = ["rt"] }
|
||||
toml = "1"
|
||||
tui-realm-stdlib = "4"
|
||||
tui-term = "0.3"
|
||||
tuirealm = "4"
|
||||
unicode-width = "0.2"
|
||||
whoami = "2"
|
||||
wildmatch = "2"
|
||||
|
||||
[target."cfg(any(target_os = \"linux\", target_os = \"freebsd\"))".dependencies]
|
||||
dbus-secret-service-keyring-store = { version = "1", features = [
|
||||
"crypto-rust",
|
||||
"vendored",
|
||||
] }
|
||||
|
||||
[target."cfg(target_family = \"unix\")".dependencies]
|
||||
remotefs-ftp = { version = "0.4", features = [
|
||||
"native-tls",
|
||||
"native-tls-vendored",
|
||||
] }
|
||||
uzers = "0.12"
|
||||
|
||||
[target."cfg(target_family = \"windows\")".dependencies]
|
||||
remotefs-ftp = { version = "0.4", features = ["native-tls"] }
|
||||
|
||||
[target."cfg(target_os = \"macos\")".dependencies]
|
||||
apple-native-keyring-store = { version = "1", features = ["keychain"] }
|
||||
|
||||
[target."cfg(target_os = \"windows\")".dependencies]
|
||||
windows-native-keyring-store = "1"
|
||||
|
||||
[dev-dependencies]
|
||||
pretty_assertions = "1"
|
||||
serial_test = "3"
|
||||
|
||||
[build-dependencies]
|
||||
cfg_aliases = "0.2"
|
||||
|
||||
[[bin]]
|
||||
name = "termscp"
|
||||
path = "src/main.rs"
|
||||
|
||||
[dependencies]
|
||||
argh = "^0.1"
|
||||
bitflags = "^2.1"
|
||||
bytesize = "^1.1"
|
||||
chrono = "^0.4"
|
||||
content_inspector = "^0.2"
|
||||
dirs = "^5.0"
|
||||
edit = "^0.1"
|
||||
filetime = "^0.2"
|
||||
hostname = "^0.3"
|
||||
keyring = { version = "^2.0", optional = true }
|
||||
lazy-regex = "^2.5"
|
||||
lazy_static = "^1.4"
|
||||
log = "^0.4"
|
||||
magic-crypt = "^3.1"
|
||||
notify = "=4.0.17"
|
||||
notify-rust = { version = "^4.5", default-features = false, features = ["d"] }
|
||||
open = "^5.0"
|
||||
rand = "^0.8.5"
|
||||
remotefs = "^0.2.0"
|
||||
remotefs-aws-s3 = { version = "^0.2.1", default-features = false, features = [
|
||||
"find",
|
||||
"rustls",
|
||||
] }
|
||||
rpassword = "^7.0"
|
||||
self_update = { version = "^0.37", default-features = false, features = [
|
||||
"rustls",
|
||||
"archive-tar",
|
||||
"archive-zip",
|
||||
"compression-flate2",
|
||||
"compression-zip-deflate",
|
||||
] }
|
||||
serde = { version = "^1", features = ["derive"] }
|
||||
simplelog = "^0.12"
|
||||
ssh2-config = "^0.2"
|
||||
tempfile = "^3.4"
|
||||
thiserror = "^1"
|
||||
toml = "^0.7"
|
||||
tui-realm-stdlib = "^1.2"
|
||||
tuirealm = "^1.8.0"
|
||||
unicode-width = "^0.1"
|
||||
version-compare = "^0.1"
|
||||
whoami = "^1.4"
|
||||
wildmatch = "^2.1"
|
||||
[lints.rust]
|
||||
trivial_numeric_casts = "warn"
|
||||
unsafe_op_in_unsafe_fn = "warn"
|
||||
unused_lifetimes = "warn"
|
||||
|
||||
[dev-dependencies]
|
||||
pretty_assertions = "^1.3"
|
||||
serial_test = "^2.0"
|
||||
|
||||
[build-dependencies]
|
||||
cfg_aliases = "0.1"
|
||||
|
||||
[features]
|
||||
default = ["smb", "with-keyring"]
|
||||
github-actions = []
|
||||
with-keyring = ["keyring"]
|
||||
smb = ["remotefs-smb"]
|
||||
|
||||
[target."cfg(not(target_os = \"macos\"))".dependencies]
|
||||
remotefs-smb = { version = "^0.2", optional = true }
|
||||
|
||||
[target."cfg(target_family = \"windows\")"]
|
||||
[target."cfg(target_family = \"windows\")".dependencies]
|
||||
remotefs-ftp = { version = "^0.1.2", features = ["native-tls"] }
|
||||
remotefs-ssh = "^0.2"
|
||||
|
||||
[target."cfg(target_family = \"unix\")"]
|
||||
[target."cfg(target_family = \"unix\")".dependencies]
|
||||
remotefs-ftp = { version = "^0.1.2", features = ["vendored", "native-tls"] }
|
||||
remotefs-ssh = { version = "^0.2", features = ["ssh2-vendored"] }
|
||||
users = "0.11.0"
|
||||
[lints.clippy]
|
||||
complexity = { level = "warn", priority = -1 }
|
||||
correctness = { level = "warn", priority = -1 }
|
||||
cloned_instead_of_copied = "warn"
|
||||
implicit_clone = "warn"
|
||||
manual_string_new = "warn"
|
||||
perf = { level = "warn", priority = -1 }
|
||||
redundant_closure_for_method_calls = "warn"
|
||||
style = { level = "warn", priority = -1 }
|
||||
suspicious = { level = "warn", priority = -1 }
|
||||
unnested_or_patterns = "warn"
|
||||
|
||||
[profile.dev]
|
||||
incremental = true
|
||||
|
||||
@@ -1,58 +1,19 @@
|
||||
# termscp
|
||||
|
||||
<p align="center">
|
||||
<img src="/assets/images/termscp.svg" width="256" height="256" />
|
||||
<img src="/assets/images/termscp.svg" alt="termscp logo" width="256" height="256" />
|
||||
</p>
|
||||
|
||||
<p align="center">~ A feature rich terminal file transfer ~</p>
|
||||
<p align="center">
|
||||
<a href="https://termscp.veeso.dev" target="_blank">Website</a>
|
||||
<a href="https://termscp.rs" target="_blank">Website</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#get-started" target="_blank">Installation</a>
|
||||
<a href="https://termscp.rs/install" target="_blank">Installation</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#user-manual" target="_blank">User manual</a>
|
||||
<a href="https://docs.termscp.rs" target="_blank">User manual</a>
|
||||
</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/gb.png"
|
||||
alt="English"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/de/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/de.png"
|
||||
alt="Deutsch"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/es/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/es.png"
|
||||
alt="Español"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/fr/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/fr.png"
|
||||
alt="Français"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/it/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/it.png"
|
||||
alt="Italiano"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/zh-CN/README.md"
|
||||
><img
|
||||
@@ -62,64 +23,19 @@
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
<p align="center">Developed by <a href="https://veeso.dev/" target="_blank">@veeso</a></p>
|
||||
<p align="center">Current version: 0.12.3 (06/10/2023)</p>
|
||||
<p align="center">Developed by <a href="https://veeso.me/" target="_blank">@veeso</a></p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://opensource.org/licenses/MIT"
|
||||
><img
|
||||
src="https://img.shields.io/badge/License-MIT-teal.svg"
|
||||
alt="License-MIT"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/stargazers"
|
||||
><img
|
||||
src="https://img.shields.io/github/stars/veeso/termscp.svg"
|
||||
alt="Repo stars"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/d/termscp.svg"
|
||||
alt="Downloads counter"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/v/termscp.svg"
|
||||
alt="Latest version"
|
||||
/></a>
|
||||
<a href="https://ko-fi.com/veeso">
|
||||
<img
|
||||
src="https://img.shields.io/badge/donate-ko--fi-red"
|
||||
alt="Ko-fi"
|
||||
/></a>
|
||||
</p>
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Linux/badge.svg"
|
||||
alt="Linux CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/MacOS/badge.svg"
|
||||
alt="MacOS CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Windows/badge.svg"
|
||||
alt="Windows CI"
|
||||
/></a>
|
||||
<a href="https://coveralls.io/github/veeso/termscp"
|
||||
><img
|
||||
src="https://coveralls.io/repos/github/veeso/termscp/badge.svg"
|
||||
alt="Coveralls"
|
||||
/></a>
|
||||
</p>
|
||||
[](https://opensource.org/licenses/MIT)
|
||||
[](https://github.com/veeso/termscp/stargazers)
|
||||
[](https://crates.io/crates/termscp)
|
||||
[](https://crates.io/crates/termscp)
|
||||
[](https://github.com/veeso/termscp/actions/workflows/ci.yml)
|
||||
|
||||
---
|
||||
|
||||
## About termscp 🖥
|
||||
|
||||
Termscp is a feature rich terminal file transfer and explorer, with support for SCP/SFTP/FTP/S3. So basically is a terminal utility with an TUI to connect to a remote server to retrieve and upload files and to interact with the local file system. It is **Linux**, **MacOS**, **FreeBSD**, **NetBSD** and **Windows** compatible.
|
||||
Termscp is a feature rich terminal file transfer and explorer, with support for SCP/SFTP/FTP/Kube/S3/WebDAV. So basically is a terminal utility with an TUI to connect to a remote server to retrieve and upload files and to interact with the local file system. It is **Linux**, **MacOS**, **FreeBSD**, **NetBSD** and **Windows** compatible.
|
||||
|
||||

|
||||
|
||||
@@ -131,14 +47,17 @@ Termscp is a feature rich terminal file transfer and explorer, with support for
|
||||
- **SFTP**
|
||||
- **SCP**
|
||||
- **FTP** and **FTPS**
|
||||
- **Kube**
|
||||
- **S3**
|
||||
- **SMB**
|
||||
- **WebDAV**
|
||||
- 🖥 Explore and operate on the remote and on the local machine file system with a handy UI
|
||||
- Create, remove, rename, search, view and edit files
|
||||
- ⭐ Connect to your favourite hosts through built-in bookmarks and recent connections
|
||||
- 📝 View and edit files with your favourite applications
|
||||
- 💁 SFTP/SCP authentication with SSH keys and username/password
|
||||
- 🐧 Compatible with Windows, Linux, FreeBSD, NetBSD and MacOS
|
||||
- 🐚 Embedded terminal for executing commands on the system.
|
||||
- 🎨 Make it yours!
|
||||
- Themes
|
||||
- Custom file explorer format
|
||||
@@ -162,12 +81,18 @@ If you want to contribute to this project, don't forget to check out our [contri
|
||||
If you are a Linux, a FreeBSD or a MacOS user this simple shell script will install termscp on your system with a single command:
|
||||
|
||||
```sh
|
||||
curl -sSLf http://get-termscp.veeso.dev | sh
|
||||
curl --proto '=https' --tlsv1.2 -sSLf https://termscp.rs/install.sh | sh
|
||||
```
|
||||
|
||||
> ❗ MacOs installation requires [Homebrew](https://brew.sh/), otherwise the Rust compiler will be installed
|
||||
|
||||
while if you're a Windows user, you can install termscp with [Chocolatey](https://chocolatey.org/):
|
||||
if you're a Windows user, you can install termscp from PowerShell with a single command:
|
||||
|
||||
```ps
|
||||
irm https://termscp.rs/install.ps1 | iex
|
||||
```
|
||||
|
||||
or, alternatively, with [Chocolatey](https://chocolatey.org/):
|
||||
|
||||
```ps
|
||||
choco install termscp
|
||||
@@ -179,9 +104,15 @@ NetBSD users can install termscp from the official repositories.
|
||||
pkgin install termscp
|
||||
```
|
||||
|
||||
For more information or other platforms, please visit [termscp.veeso.dev](https://termscp.veeso.dev/#get-started) to view all installation methods.
|
||||
Arch Linux users can install termscp from the official repositories.
|
||||
|
||||
⚠️ If you're looking on how to update termscp just run termscp from CLI with: `(sudo) termscp --update` ⚠️
|
||||
```sh
|
||||
pacman -S termscp
|
||||
```
|
||||
|
||||
For more information or other platforms, please visit [termscp.rs](https://termscp.rs/install) to view all installation methods.
|
||||
|
||||
⚠️ If you're looking on how to update termscp just run termscp from CLI with: `(sudo) termscp update` ⚠️
|
||||
|
||||
### Requirements ❗
|
||||
|
||||
@@ -205,36 +136,22 @@ These requirements are not forced required to run termscp, but to enjoy all of i
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- **Linux** users:
|
||||
- A keyring manager: read more in the [User manual](docs/man.md#linux-keyring)
|
||||
- A keyring manager: read more in the [User manual](https://docs.termscp.rs/en-US/configuration/password-security.html#linux-keyring)
|
||||
- **WSL** users
|
||||
- To **open** files via `V` (at least one of these)
|
||||
- [wslu](https://github.com/wslutilities/wslu)
|
||||
|
||||
---
|
||||
|
||||
## Support the developer ☕
|
||||
|
||||
If you like termscp and you're grateful for the work I've done, please consider a little donation 🥳
|
||||
|
||||
You can make a donation with one of these platforms:
|
||||
|
||||
[](https://ko-fi.com/veeso)
|
||||
[](https://www.paypal.me/chrisintin)
|
||||
[](https://btc.com/bc1qvlmykjn7htz0vuprmjrlkwtv9m9pan6kylsr8w)
|
||||
|
||||
---
|
||||
|
||||
## User manual 📚
|
||||
|
||||
The user manual can be found on the [termscp's website](https://termscp.veeso.dev/#user-manual) or on [Github](docs/man.md).
|
||||
The user manual can be found on [termscp's documentation website](https://docs.termscp.rs).
|
||||
|
||||
---
|
||||
|
||||
## Upcoming Features 🧪
|
||||
|
||||
For **2023** there will be two major updates during the year.
|
||||
|
||||
Along to new features, termscp developments is now focused on UX and performance improvements, so if you have any suggestion, feel free to open an issue.
|
||||
See [Milestones](https://github.com/veeso/termscp/milestones)
|
||||
|
||||
---
|
||||
|
||||
@@ -263,12 +180,13 @@ termscp is powered by these awesome projects:
|
||||
- [crossterm](https://github.com/crossterm-rs/crossterm)
|
||||
- [edit](https://github.com/milkey-mouse/edit)
|
||||
- [keyring-rs](https://github.com/hwchen/keyring-rs)
|
||||
- [kube](https://github.com/kube-rs/kube)
|
||||
- [open-rs](https://github.com/Byron/open-rs)
|
||||
- [pavao](https://github.com/veeso/pavao)
|
||||
- [remotefs](https://github.com/veeso/remotefs-rs)
|
||||
- [rpassword](https://github.com/conradkleinespel/rpassword)
|
||||
- [self_update](https://github.com/jaemk/self_update)
|
||||
- [tui-rs](https://github.com/fdehau/tui-rs)
|
||||
- [ratatui](https://github.com/ratatui-org/ratatui)
|
||||
- [tui-realm](https://github.com/veeso/tui-realm)
|
||||
- [whoami](https://github.com/libcala/whoami)
|
||||
- [wildmatch](https://github.com/becheran/wildmatch)
|
||||
|
||||
@@ -6,11 +6,11 @@ fn main() {
|
||||
// Platforms
|
||||
macos: { target_os = "macos" },
|
||||
linux: { target_os = "linux" },
|
||||
unix: { target_family = "unix" },
|
||||
windows: { target_family = "windows" },
|
||||
posix: { target_family = "unix" },
|
||||
win: { target_family = "windows" },
|
||||
// exclusive features
|
||||
smb: { all(feature = "smb", not( macos )) },
|
||||
smb_unix: { all(unix, feature = "smb", not(macos)) },
|
||||
smb: { feature = "smb" },
|
||||
smb_unix: { all(unix, feature = "smb") },
|
||||
smb_windows: { all(windows, feature = "smb") }
|
||||
}
|
||||
}
|
||||
|
||||
@@ -0,0 +1,46 @@
|
||||
[changelog]
|
||||
body = """
|
||||
## {{ version | trim_start_matches(pat="v") }}
|
||||
|
||||
Released on {{ timestamp | date(format="%Y-%m-%d") }}
|
||||
{%- if commits | filter(attribute="breaking", value=true) | length > 0 %}
|
||||
|
||||
### ⚠ Breaking Changes
|
||||
|
||||
{%- for commit in commits | filter(attribute="breaking", value=true) %}
|
||||
- {% if commit.scope %}**{{ commit.scope }}:** {% endif %}{{ commit.message | split(pat="\n") | first | trim }}
|
||||
{%- if commit.breaking_description %}
|
||||
> {{ commit.breaking_description }}
|
||||
{%- endif %}
|
||||
{%- endfor %}
|
||||
{%- endif %}
|
||||
{%- for group, commits in commits | group_by(attribute="group") %}
|
||||
|
||||
### {{ group | upper_first }}
|
||||
{% for commit in commits %}
|
||||
- {% if commit.breaking %}💥 {% endif %}{% if commit.scope %}**{{ commit.scope }}:** {% endif %}{{ commit.message | split(pat="\n") | first | trim }}
|
||||
{%- if commit.body %}
|
||||
> {{ commit.body | split(pat="\n") | join(sep="\n > ") }}
|
||||
{%- endif %}
|
||||
{%- endfor %}
|
||||
{%- endfor %}
|
||||
"""
|
||||
trim = false
|
||||
|
||||
[git]
|
||||
conventional_commits = true
|
||||
filter_unconventional = true
|
||||
split_commits = false
|
||||
commit_parsers = [
|
||||
{ message = "^feat", group = "Added" },
|
||||
{ message = "^fix", group = "Fixed" },
|
||||
{ message = "^refactor", group = "Changed" },
|
||||
{ message = "^perf", group = "Performance" },
|
||||
{ message = "^doc", group = "Documentation" },
|
||||
{ message = "^test", group = "Testing" },
|
||||
{ message = "^ci", group = "CI" },
|
||||
{ message = "^chore", skip = true },
|
||||
]
|
||||
filter_commits = false
|
||||
tag_pattern = "v[0-9].*"
|
||||
sort_commits = "oldest"
|
||||
@@ -1,25 +0,0 @@
|
||||
# Build with Docker
|
||||
|
||||
- [Build with Docker](#build-with-docker)
|
||||
- [Prerequisites](#prerequisites)
|
||||
- [Build](#build)
|
||||
|
||||
---
|
||||
|
||||
## Prerequisites
|
||||
|
||||
- Docker
|
||||
|
||||
## Build
|
||||
|
||||
1. Build x86_64
|
||||
|
||||
this will build termscp for:
|
||||
|
||||
- Linux x86_64 Deb packages
|
||||
- Linux x86_64 RPM packages
|
||||
- Windows x86_64 MSVC packages
|
||||
|
||||
```sh
|
||||
|
||||
```
|
||||
@@ -1,26 +0,0 @@
|
||||
FROM centos:centos7 as builder
|
||||
|
||||
WORKDIR /usr/src/
|
||||
# Install dependencies
|
||||
RUN yum -y install \
|
||||
git \
|
||||
gcc \
|
||||
pkgconfig \
|
||||
gcc \
|
||||
make \
|
||||
dbus-devel \
|
||||
libsmbclient-devel \
|
||||
bash \
|
||||
rpm-build
|
||||
# Install rust
|
||||
RUN curl --proto '=https' --tlsv1.2 -sSf https://sh.rustup.rs > /tmp/rust.sh && \
|
||||
chmod +x /tmp/rust.sh && \
|
||||
/tmp/rust.sh -y
|
||||
# Clone repository
|
||||
RUN git clone https://github.com/veeso/termscp.git
|
||||
# Set workdir to termscp
|
||||
WORKDIR /usr/src/termscp/
|
||||
# Install cargo rpm
|
||||
RUN source $HOME/.cargo/env && cargo install cargo-rpm
|
||||
|
||||
ENTRYPOINT ["tail", "-f", "/dev/null"]
|
||||
@@ -1,27 +0,0 @@
|
||||
FROM debian:buster
|
||||
|
||||
WORKDIR /usr/src/
|
||||
# Install dependencies
|
||||
RUN apt update && apt install -y \
|
||||
git \
|
||||
gcc \
|
||||
pkg-config \
|
||||
libdbus-1-dev \
|
||||
build-essential \
|
||||
libsmbclient-dev \
|
||||
libsmbclient \
|
||||
bash \
|
||||
curl
|
||||
|
||||
# Install rust
|
||||
RUN curl --proto '=https' --tlsv1.2 -sSf https://sh.rustup.rs > /tmp/rust.sh && \
|
||||
chmod +x /tmp/rust.sh && \
|
||||
/tmp/rust.sh -y
|
||||
# Clone repository
|
||||
RUN git clone https://github.com/veeso/termscp.git
|
||||
# Set workdir to termscp
|
||||
WORKDIR /usr/src/termscp/
|
||||
# Install cargo deb
|
||||
RUN . $HOME/.cargo/env && cargo install cargo-deb
|
||||
|
||||
ENTRYPOINT ["tail", "-f", "/dev/null"]
|
||||
@@ -1,53 +0,0 @@
|
||||
#!/bin/sh
|
||||
|
||||
if [ -z "$1" ]; then
|
||||
echo "Usage: freebsd.sh <version>"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
VERSION=$1
|
||||
|
||||
set -e # Don't fail
|
||||
|
||||
# Go to root dir
|
||||
cd ../../
|
||||
# Check if in correct directory
|
||||
if [ ! -f Cargo.toml ]; then
|
||||
echo "Please start freebsd.sh from dist/build/ directory"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# Build release
|
||||
cargo build --release && cargo strip
|
||||
# Make pkg
|
||||
cd target/release/
|
||||
PKG="termscp-v${VERSION}-x86_64-unknown-freebsd.tar.gz"
|
||||
tar czf $PKG termscp
|
||||
sha256sum $PKG
|
||||
# Calc sha256 of exec and copy to path
|
||||
HASH=`sha256sum termscp | cut -d ' ' -f1`
|
||||
sudo cp termscp /usr/local/bin/termscp
|
||||
mkdir -p ../../dist/pkgs/freebsd/
|
||||
mv $PKG ../../dist/pkgs/freebsd/$PKG
|
||||
cd ../../dist/pkgs/freebsd/
|
||||
rm manifest
|
||||
echo -e "name: \"termscp\"" > manifest
|
||||
echo -e "version: $VERSION" >> manifest
|
||||
echo -e "origin: veeso/termscp" >> manifest
|
||||
echo -e "comment: \"A feature rich terminal UI file transfer and explorer with support for SCP/SFTP/FTP/S3\"" >> manifest
|
||||
echo -e "desc: <<EOD\n\
|
||||
A feature rich terminal UI file transfer and explorer with support for SCP/SFTP/FTP/S3\n\
|
||||
EOD\n\
|
||||
arch: \"amd64\"\n\
|
||||
www: \"https://termscp.veeso.dev/termscp/\"\n\
|
||||
maintainer: \"christian.visintin1997@gmail.com\"\n\
|
||||
prefix: \"/usr/local/bin\"\n\
|
||||
deps: {\n\
|
||||
libssh: {origin: security/libssh, version: 0.9.5}\n\
|
||||
}\n\
|
||||
files: {\n\
|
||||
/usr/local/bin/termscp: \"$HASH\"\n\
|
||||
}\n\
|
||||
" >> manifest
|
||||
|
||||
exit $?
|
||||
@@ -1,62 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
if [ -z "$1" ]; then
|
||||
echo "Usage: $0 <version> [branch] [--no-cache]"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
VERSION=$1
|
||||
|
||||
if [ -z "$2" ]; then
|
||||
BRANCH=$VERSION
|
||||
else
|
||||
BRANCH=$2
|
||||
fi
|
||||
|
||||
CACHE=""
|
||||
|
||||
if [ "$3" == "--no-cache" ]; then
|
||||
CACHE="--no-cache"
|
||||
fi
|
||||
|
||||
# names
|
||||
ARM64_DEB_NAME="termscp-arm64_deb"
|
||||
ARM64_RPM_NAME="termscp-arm64_rpm"
|
||||
|
||||
docker run --rm --privileged multiarch/qemu-user-static --reset -p yes
|
||||
|
||||
set -e # Don't fail
|
||||
|
||||
# Create pkgs directory
|
||||
cd ..
|
||||
PKGS_DIR=$(pwd)/pkgs
|
||||
cd -
|
||||
mkdir -p ${PKGS_DIR}/
|
||||
# Build aarch64_deb
|
||||
cd aarch64_debian10/
|
||||
docker buildx build --platform linux/arm64 $CACHE --build-arg branch=${BRANCH} --tag $ARM64_DEB_NAME .
|
||||
cd -
|
||||
mkdir -p ${PKGS_DIR}/deb/
|
||||
mkdir -p ${PKGS_DIR}/aarch64-unknown-linux-gnu/
|
||||
docker run --name "$ARM64_DEB_NAME" -d "$ARM64_DEB_NAME" || docker start "$ARM64_DEB_NAME"
|
||||
docker exec -it "$ARM64_DEB_NAME" bash -c ". \$HOME/.cargo/env && git fetch origin && git checkout origin/$BRANCH && cargo build --release && cargo deb"
|
||||
docker cp ${ARM64_DEB_NAME}:/usr/src/termscp/target/debian/termscp_${VERSION}_arm64.deb ${PKGS_DIR}/deb/
|
||||
docker cp ${ARM64_DEB_NAME}:/usr/src/termscp/target/release/termscp ${PKGS_DIR}/aarch64-unknown-linux-gnu/
|
||||
docker stop "$ARM64_DEB_NAME"
|
||||
# Make tar.gz
|
||||
cd ${PKGS_DIR}/aarch64-unknown-linux-gnu/
|
||||
tar cvzf termscp-v${VERSION}-aarch64-unknown-linux-gnu.tar.gz termscp
|
||||
echo "Sha256 (homebrew aarch64): $(sha256sum termscp-v${VERSION}-aarch64-unknown-linux-gnu.tar.gz)"
|
||||
rm termscp
|
||||
cd -
|
||||
# Build aarch64_centos7
|
||||
cd aarch64_centos7/
|
||||
docker buildx build --platform linux/arm64 $CACHE --build-arg branch=${BRANCH} --tag $ARM64_RPM_NAME .
|
||||
cd -
|
||||
mkdir -p ${PKGS_DIR}/rpm/
|
||||
docker run --name "$ARM64_RPM_NAME" -d "$ARM64_RPM_NAME" || docker start "$ARM64_RPM_NAME"
|
||||
docker exec -it "$ARM64_RPM_NAME" bash -c ". \$HOME/.cargo/env && git fetch origin && git checkout origin/$BRANCH; cargo rpm init; cargo rpm build"
|
||||
docker cp ${ARM64_RPM_NAME}:/usr/src/termscp/target/release/rpmbuild/RPMS/aarch64/termscp-${VERSION}-1.el7.aarch64.rpm ${PKGS_DIR}/rpm/termscp-${VERSION}-1.aarch64.rpm
|
||||
docker stop "$ARM64_RPM_NAME"
|
||||
|
||||
exit $?
|
||||
@@ -1,60 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
if [ -z "$1" ]; then
|
||||
echo "Usage: $0 <version> [branch] [--no-cache]"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
VERSION=$1
|
||||
|
||||
if [ -z "$2" ]; then
|
||||
BRANCH=$VERSION
|
||||
else
|
||||
BRANCH=$2
|
||||
fi
|
||||
|
||||
CACHE=""
|
||||
|
||||
if [ "$3" == "--no-cache" ]; then
|
||||
CACHE="--no-cache"
|
||||
fi
|
||||
|
||||
# names
|
||||
X86_64_DEB_NAME="termscp-x86_64_deb"
|
||||
X86_64_RPM_NAME="termscp-x86_64_rpm"
|
||||
|
||||
set -e # Don't fail
|
||||
|
||||
# Create pkgs directory
|
||||
cd ..
|
||||
PKGS_DIR=$(pwd)/pkgs
|
||||
cd -
|
||||
mkdir -p ${PKGS_DIR}/
|
||||
# Build x86_64_deb
|
||||
cd x86_64_debian10/
|
||||
docker build $CACHE --build-arg branch=${BRANCH} --tag "$X86_64_DEB_NAME" .
|
||||
cd -
|
||||
mkdir -p ${PKGS_DIR}/deb/
|
||||
mkdir -p ${PKGS_DIR}/x86_64-unknown-linux-gnu/
|
||||
docker run --name "$X86_64_DEB_NAME" -d "$X86_64_DEB_NAME" || docker start "$X86_64_DEB_NAME"
|
||||
docker exec -it "$X86_64_DEB_NAME" bash -c ". \$HOME/.cargo/env && git fetch origin && git checkout origin/$BRANCH && cargo build --release && cargo deb"
|
||||
docker cp ${X86_64_DEB_NAME}:/usr/src/termscp/target/debian/termscp_${VERSION}_amd64.deb ${PKGS_DIR}/deb/
|
||||
docker cp ${X86_64_DEB_NAME}:/usr/src/termscp/target/release/termscp ${PKGS_DIR}/x86_64-unknown-linux-gnu/
|
||||
docker stop "$X86_64_DEB_NAME"
|
||||
# Make tar.gz
|
||||
cd ${PKGS_DIR}/x86_64-unknown-linux-gnu/
|
||||
tar cvzf termscp-v${VERSION}-x86_64-unknown-linux-gnu.tar.gz termscp
|
||||
echo "Sha256 x86_64 (homebrew): $(sha256sum termscp-v${VERSION}-x86_64-unknown-linux-gnu.tar.gz)"
|
||||
rm termscp
|
||||
cd -
|
||||
# Build x86_64_centos7
|
||||
cd x86_64_centos7/
|
||||
docker build $CACHE --build-arg branch=${BRANCH} --tag "$X86_64_RPM_NAME" .
|
||||
cd -
|
||||
mkdir -p ${PKGS_DIR}/rpm/
|
||||
docker run --name "$X86_64_RPM_NAME" -d "$X86_64_RPM_NAME" || docker start "$X86_64_RPM_NAME"
|
||||
docker exec -it "$X86_64_RPM_NAME" bash -c ". \$HOME/.cargo/env && git fetch origin && git checkout origin/$BRANCH; cargo rpm init; cargo rpm build"
|
||||
docker cp ${X86_64_RPM_NAME}:/usr/src/termscp/target/release/rpmbuild/RPMS/x86_64/termscp-${VERSION}-1.el7.x86_64.rpm ${PKGS_DIR}/rpm/termscp-${VERSION}-1.x86_64.rpm
|
||||
docker stop "$X86_64_RPM_NAME"
|
||||
|
||||
exit $?
|
||||
@@ -1,110 +0,0 @@
|
||||
#!/bin/sh
|
||||
|
||||
make_pkg() {
|
||||
ARCH=$1
|
||||
VERSION=$2
|
||||
TARGET_DIR="$3"
|
||||
if [ -z "$TARGET_DIR" ]; then
|
||||
TARGET_DIR=target/release/
|
||||
fi
|
||||
ROOT_DIR=$(pwd)
|
||||
cd "$TARGET_DIR"
|
||||
PKG="termscp-v${VERSION}-${ARCH}-apple-darwin.tar.gz"
|
||||
tar czf "$PKG" termscp
|
||||
HASH=$(sha256sum "$PKG")
|
||||
mkdir -p "${ROOT_DIR}/dist/pkgs/macos/"
|
||||
mv "$PKG" "${ROOT_DIR}/dist/pkgs/macos/$PKG"
|
||||
cd -
|
||||
echo "$HASH"
|
||||
}
|
||||
|
||||
detect_platform() {
|
||||
local platform
|
||||
platform="$(uname -s | tr '[:upper:]' '[:lower:]')"
|
||||
|
||||
case "${platform}" in
|
||||
linux) platform="linux" ;;
|
||||
darwin) platform="macos" ;;
|
||||
freebsd) platform="freebsd" ;;
|
||||
esac
|
||||
|
||||
printf '%s' "${platform}"
|
||||
}
|
||||
|
||||
detect_arch() {
|
||||
local arch
|
||||
arch="$(uname -m | tr '[:upper:]' '[:lower:]')"
|
||||
|
||||
case "${arch}" in
|
||||
amd64) arch="x86_64" ;;
|
||||
armv*) arch="arm" ;;
|
||||
arm64) arch="aarch64" ;;
|
||||
esac
|
||||
|
||||
# `uname -m` in some cases mis-reports 32-bit OS as 64-bit, so double check
|
||||
if [ "${arch}" = "x86_64" ] && [ "$(getconf LONG_BIT)" -eq 32 ]; then
|
||||
arch="i686"
|
||||
elif [ "${arch}" = "aarch64" ] && [ "$(getconf LONG_BIT)" -eq 32 ]; then
|
||||
arch="arm"
|
||||
fi
|
||||
|
||||
printf '%s' "${arch}"
|
||||
}
|
||||
|
||||
if [ -z "$1" ]; then
|
||||
echo "Usage: macos.sh <version>"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
PLATFORM="$(detect_platform)"
|
||||
ARCH="$(detect_arch)"
|
||||
|
||||
if [ "$PLATFORM" != "macos" ]; then
|
||||
echo "macos build is only available on MacOs systems"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
VERSION=$1
|
||||
export BUILD_ROOT
|
||||
BUILD_ROOT="$(pwd)/../../"
|
||||
|
||||
set -e # Don't fail
|
||||
|
||||
# Go to root dir
|
||||
cd ../../
|
||||
# Check if in correct directory
|
||||
if [ ! -f Cargo.toml ]; then
|
||||
echo "Please start macos.sh from dist/build/ directory"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# Build release (x86_64)
|
||||
X86_TARGET=""
|
||||
X86_TARGET_DIR=""
|
||||
if [ "$ARCH" = "aarch64" ]; then
|
||||
X86_TARGET="--target x86_64-apple-darwin"
|
||||
X86_TARGET_DIR="target/x86_64-apple-darwin/release/"
|
||||
fi
|
||||
cargo build --release $X86_TARGET
|
||||
# Make pkg
|
||||
X86_64_HASH=$(make_pkg "x86_64" "$VERSION" $X86_TARGET_DIR)
|
||||
RET_X86_64=$?
|
||||
|
||||
ARM64_TARGET=""
|
||||
ARM64_TARGET_DIR=""
|
||||
if [ "$ARCH" = "aarch64" ]; then
|
||||
ARM64_TARGET="--target aarch64-apple-darwin"
|
||||
ARM64_TARGET_DIR="target/aarch64-apple-darwin/release/"
|
||||
fi
|
||||
cd "$BUILD_ROOT"
|
||||
# Build ARM64 pkg
|
||||
cargo build --release $ARM64_TARGET
|
||||
# Make pkg
|
||||
ARM64_HASH=$(make_pkg "arm64" "$VERSION" $ARM64_TARGET_DIR)
|
||||
RET_ARM64=$?
|
||||
|
||||
echo "x86_64 hash: $X86_64_HASH"
|
||||
echo "arm64 hash: $ARM64_HASH"
|
||||
|
||||
[ "$RET_ARM64" -eq 0 ] && [ "$RET_X86_64" -eq 0 ]
|
||||
exit $?
|
||||
@@ -1,20 +0,0 @@
|
||||
$ErrorActionPreference = 'Stop';
|
||||
|
||||
if ($args.Count -eq 0) {
|
||||
Write-Output "Usage: windows.ps1 <version>"
|
||||
exit 1
|
||||
}
|
||||
|
||||
$version = $args[0]
|
||||
|
||||
# Go to root directory
|
||||
Set-Location ..\..\
|
||||
# Build
|
||||
cargo build --release
|
||||
# Make zip
|
||||
$zipName = "termscp-v$version-x86_64-pc-windows-msvc.zip"
|
||||
Set-Location .\target\release\
|
||||
Compress-Archive -Force termscp.exe $zipName
|
||||
# Get checksum
|
||||
Get-FileHash $zipName
|
||||
Move-Item $zipName .\..\..\dist\pkgs\windows\$zipName
|
||||
@@ -1,26 +0,0 @@
|
||||
FROM centos:centos7 as builder
|
||||
|
||||
WORKDIR /usr/src/
|
||||
# Install dependencies
|
||||
RUN yum -y install \
|
||||
git \
|
||||
gcc \
|
||||
pkgconfig \
|
||||
gcc \
|
||||
make \
|
||||
dbus-devel \
|
||||
libsmbclient-devel \
|
||||
bash \
|
||||
rpm-build
|
||||
# Install rust
|
||||
RUN curl --proto '=https' --tlsv1.2 -sSf https://sh.rustup.rs > /tmp/rust.sh && \
|
||||
chmod +x /tmp/rust.sh && \
|
||||
/tmp/rust.sh -y
|
||||
# Clone repository
|
||||
RUN git clone https://github.com/veeso/termscp.git
|
||||
# Set workdir to termscp
|
||||
WORKDIR /usr/src/termscp/
|
||||
# Install cargo rpm
|
||||
RUN source $HOME/.cargo/env && cargo install cargo-rpm
|
||||
|
||||
ENTRYPOINT ["tail", "-f", "/dev/null"]
|
||||
@@ -1,27 +0,0 @@
|
||||
FROM debian:buster
|
||||
|
||||
WORKDIR /usr/src/
|
||||
# Install dependencies
|
||||
RUN apt update && apt install -y \
|
||||
git \
|
||||
gcc \
|
||||
pkg-config \
|
||||
libdbus-1-dev \
|
||||
build-essential \
|
||||
libsmbclient-dev \
|
||||
libsmbclient \
|
||||
bash \
|
||||
curl
|
||||
|
||||
# Install rust
|
||||
RUN curl --proto '=https' --tlsv1.2 -sSf https://sh.rustup.rs > /tmp/rust.sh && \
|
||||
chmod +x /tmp/rust.sh && \
|
||||
/tmp/rust.sh -y
|
||||
# Clone repository
|
||||
RUN git clone https://github.com/veeso/termscp.git
|
||||
# Set workdir to termscp
|
||||
WORKDIR /usr/src/termscp/
|
||||
# Install cargo deb
|
||||
RUN . $HOME/.cargo/env && cargo install cargo-deb
|
||||
|
||||
ENTRYPOINT ["tail", "-f", "/dev/null"]
|
||||
@@ -0,0 +1,8 @@
|
||||
# Chocolatey How To
|
||||
|
||||
Just:
|
||||
|
||||
1. Calculate the SHA256 checksum for the latest release of ZIP files both for aarch64 and x86_64 versions.
|
||||
2. Update checksums in `tools/chocolateyinstall.ps1`
|
||||
3. run `choco pack`
|
||||
4. run `choco push termscp.$VERSION.nupkg --source https://push.chocolatey.org/`
|
||||
@@ -0,0 +1,58 @@
|
||||
<?xml version="1.0" encoding="utf-8"?>
|
||||
|
||||
<package xmlns="http://schemas.microsoft.com/packaging/2015/06/nuspec.xsd">
|
||||
<metadata>
|
||||
<id>termscp</id>
|
||||
<version>1.1.1</version>
|
||||
<title>termSCP</title>
|
||||
<authors>Christian Visintin</authors>
|
||||
<owners>Christian Visintin</owners>
|
||||
<projectUrl>https://veeso.github.io/termscp/</projectUrl>
|
||||
<copyright>Christian Visintin (C) 2024</copyright>
|
||||
<licenseUrl>https://github.com/veeso/TermSCP/blob/main/LICENSE</licenseUrl>
|
||||
<iconUrl>https://rawcdn.githack.com/veeso/termscp/c3e5663cf45c4d6a7b50c8b15f89683a2e01b829/assets/images/termscp-512.png</iconUrl>
|
||||
<requireLicenseAcceptance>true</requireLicenseAcceptance>
|
||||
<projectSourceUrl>https://github.com/veeso/termscp/tree/main/src</projectSourceUrl>
|
||||
<packageSourceUrl>https://github.com/veeso/termscp</packageSourceUrl>
|
||||
<releaseNotes>https://github.com/veeso/termscp/blob/main/CHANGELOG.md</releaseNotes>
|
||||
<docsUrl>https://docs.rs/termscp</docsUrl>
|
||||
<bugTrackerUrl>https://github.com/veeso/termscp/issues</bugTrackerUrl>
|
||||
<tags>termscp winscp rust rust-lang rust-crate scp ssh-client ssh sftp-client ftp-client ftps utility terminal-app terminal command-line-utility command-line-tool tui-rs winscp sftp</tags>
|
||||
<summary>A feature rich terminal UI file transfer and explorer with support for SCP/SFTP/FTP/Kube/WebDAV/S3</summary>
|
||||
<description>
|
||||
## About TermSCP
|
||||
|
||||
Termscp is a feature rich terminal file transfer and explorer, with support for SCP/SFTP/FTP/S3. So basically is a terminal utility with an TUI to connect to a remote server to retrieve and upload files and to interact with the local file system. It is **Linux**, **MacOS**, **BSD** and **Windows** compatible and supports SFTP, SCP, FTP and FTPS.
|
||||
|
||||
Features:
|
||||
|
||||
- 📁 Different communication protocols
|
||||
- SFTP
|
||||
- Kube
|
||||
- WebDAV
|
||||
- SCP
|
||||
- FTP and FTPS
|
||||
- S3
|
||||
- SMB
|
||||
- 🖥 Explore and operate on the remote and on the local machine file system with a handy UI
|
||||
- Create, remove, rename, search, view and edit files
|
||||
- ⭐ Connect to your favourite hosts through built-in bookmarks and recent connections
|
||||
- 📝 View and edit text files with your favourite text editor
|
||||
- 💁 SFTP/SCP authentication through SSH keys and username/password
|
||||
- 🐧 Compatible with Windows, Linux, BSD and MacOS
|
||||
- ✏ Customizable
|
||||
- Themes
|
||||
- Custom file explorer format
|
||||
- Customizable text editor
|
||||
- Customizable file sorting
|
||||
- 🔐 Save your password in your operating system key vault
|
||||
- 🦀 Rust-powered
|
||||
- 🤝 Easy to extend with new file transfers protocols
|
||||
- 👀 Developed keeping an eye on performance
|
||||
- 🦄 Frequent awesome updates
|
||||
</description>
|
||||
</metadata>
|
||||
<files>
|
||||
<file src="tools/**" target="tools" />
|
||||
</files>
|
||||
</package>
|
||||
@@ -0,0 +1,25 @@
|
||||
$ErrorActionPreference = 'Stop';
|
||||
$toolsDir = "$(Split-Path -parent $MyInvocation.MyCommand.Definition)"
|
||||
|
||||
# Detect arch: PROCESSOR_ARCHITECTURE is "ARM64" on ARM, "AMD64" on x64
|
||||
$is_arm64 = $env:PROCESSOR_ARCHITECTURE -eq 'ARM64' -or $env:PROCESSOR_ARCHITEW6432 -eq 'ARM64'
|
||||
|
||||
if ($is_arm64) {
|
||||
$url = 'https://github.com/veeso/termscp/releases/download/v1.1.1/termscp-v1.1.1-msvc.zip'
|
||||
$checksum = 'f6ad6c62f1578562f9af4bcee93bd4cc429cb52219c3636359b008db8789587e'
|
||||
} else {
|
||||
$url = 'https://github.com/veeso/termscp/releases/download/v1.1.1/termscp-v1.1.1-x86_64-pc-windows-msvc.zip'
|
||||
$checksum = 'd7796081b6f67b82acfa94557aa6852d12a33daab3cca6490660b20e42752005'
|
||||
}
|
||||
|
||||
$packageArgs = @{
|
||||
packageName = $env:ChocolateyPackageName
|
||||
fileType = 'EXE'
|
||||
url = $url
|
||||
unzipLocation = $toolsDir
|
||||
softwareName = 'termscp*'
|
||||
checksum = $checksum
|
||||
checksumType = 'sha256'
|
||||
validExitCodes = @(0, 3010, 1641)
|
||||
}
|
||||
Install-ChocolateyZipPackage @packageArgs
|
||||
@@ -1,11 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
echo "Installing cargo-deb..."
|
||||
cargo install cargo-deb
|
||||
if [ ! -f "Cargo.toml" ]; then
|
||||
echo "Yout must be in the project root directory"
|
||||
exit 1
|
||||
fi
|
||||
echo "Running cargo-deb"
|
||||
cargo deb
|
||||
exit $?
|
||||
@@ -0,0 +1,34 @@
|
||||
#!/usr/bin/env bash
|
||||
# Bump termscp version across all tracked locations.
|
||||
# Usage: bump_version.sh <version> [date] [root]
|
||||
set -euo pipefail
|
||||
|
||||
VERSION="${1:?usage: bump_version.sh <version> [date] [root]}"
|
||||
DATE="${2:-$(date +%F)}"
|
||||
ROOT="${3:-$(git rev-parse --show-toplevel)}"
|
||||
|
||||
# in-place sed that works on both GNU and BSD/macOS
|
||||
sedi() { perl -0777 -pi -e "$1" "$2"; }
|
||||
|
||||
# Cargo.toml — only the top-level package version (line-anchored), not deps
|
||||
sedi "s/^version = \"[0-9][0-9A-Za-z.\\-]*\"/version = \"$VERSION\"/m" "$ROOT/Cargo.toml"
|
||||
|
||||
# install.sh — the literal default assignment only
|
||||
sedi "s/^TERMSCP_VERSION=\"[0-9][0-9A-Za-z.\\-]*\"/TERMSCP_VERSION=\"$VERSION\"/m" "$ROOT/install.sh"
|
||||
|
||||
# install.ps1 — the default -Version parameter value only
|
||||
sedi "s/\\\$Version = \"[0-9][0-9A-Za-z.\\-]*\"/\\\$Version = \"$VERSION\"/" "$ROOT/install.ps1"
|
||||
|
||||
# README.md — version + release date
|
||||
sedi "s/Current version: [0-9][0-9A-Za-z.\\-]* [0-9]{4}-[0-9]{2}-[0-9]{2}/Current version: $VERSION $DATE/" "$ROOT/README.md"
|
||||
|
||||
# site: version constant displayed on the website
|
||||
sedi "s/^export const VERSION = \"[0-9][0-9A-Za-z.\\-]*\";/export const VERSION = \"$VERSION\";/m" "$ROOT/site/src/consts.ts"
|
||||
|
||||
# chocolatey nuspec
|
||||
sedi "s#<version>[0-9][0-9A-Za-z.\\-]*</version>#<version>$VERSION</version>#" "$ROOT/dist/chocolatey/termscp.nuspec"
|
||||
|
||||
# chocolatey install script — release tag + asset name in the URLs (checksums set later by CI)
|
||||
sedi "s#releases/download/v[0-9][0-9A-Za-z.\\-]*/termscp-v[0-9][0-9A-Za-z.\\-]*-#releases/download/v$VERSION/termscp-v$VERSION-#g" "$ROOT/dist/chocolatey/tools/chocolateyinstall.ps1"
|
||||
|
||||
echo "Bumped to $VERSION ($DATE)"
|
||||
@@ -0,0 +1,85 @@
|
||||
#!/usr/bin/env bash
|
||||
set -euo pipefail
|
||||
|
||||
SCRIPT_DIR="$(cd "$(dirname "$0")" && pwd)"
|
||||
BUMP="$SCRIPT_DIR/bump_version.sh"
|
||||
|
||||
ROOT="$(mktemp -d)"
|
||||
trap 'rm -rf "$ROOT"' EXIT
|
||||
|
||||
# --- build a fixture tree mirroring the real layout, all at 1.0.0 ---
|
||||
mkdir -p "$ROOT/site/html" "$ROOT/site/lang" "$ROOT/dist/chocolatey/tools"
|
||||
|
||||
cat > "$ROOT/Cargo.toml" <<'EOF'
|
||||
[package]
|
||||
name = "termscp"
|
||||
version = "1.0.0"
|
||||
|
||||
[dependencies]
|
||||
foo = { version = "1.0.0" }
|
||||
EOF
|
||||
|
||||
cat > "$ROOT/install.sh" <<'EOF'
|
||||
TERMSCP_VERSION="1.0.0"
|
||||
set_termscp_version() {
|
||||
TERMSCP_VERSION="$1"
|
||||
}
|
||||
EOF
|
||||
|
||||
cat > "$ROOT/README.md" <<'EOF'
|
||||
<p align="center">Current version: 1.0.0 2026-04-18</p>
|
||||
EOF
|
||||
|
||||
cat > "$ROOT/site/html/home.html" <<'EOF'
|
||||
<span>termscp 1.0.0 is NOW out! Download it from</span>
|
||||
EOF
|
||||
|
||||
cat > "$ROOT/site/html/get-started.html" <<'EOF'
|
||||
<a href="https://github.com/veeso/termscp/releases/latest/download/termscp.1.0.0.nupkg">Github</a>
|
||||
<pre>wget -O termscp.deb https://github.com/veeso/termscp/releases/latest/download/termscp_1.0.0_amd64.deb</pre>
|
||||
EOF
|
||||
|
||||
for lang in en it fr es zh-CN; do
|
||||
cat > "$ROOT/site/lang/$lang.json" <<'EOF'
|
||||
{ "versionAlert": "termscp 1.0.0 is NOW out! Download it from" }
|
||||
EOF
|
||||
done
|
||||
|
||||
cat > "$ROOT/dist/chocolatey/termscp.nuspec" <<'EOF'
|
||||
<version>1.0.0</version>
|
||||
EOF
|
||||
|
||||
cat > "$ROOT/dist/chocolatey/tools/chocolateyinstall.ps1" <<'EOF'
|
||||
$url = 'https://github.com/veeso/termscp/releases/download/v1.0.0/termscp-v1.0.0-aarch64-pc-windows-msvc.zip'
|
||||
$url = 'https://github.com/veeso/termscp/releases/download/v1.0.0/termscp-v1.0.0-x86_64-pc-windows-msvc.zip'
|
||||
EOF
|
||||
|
||||
# --- run the bump ---
|
||||
"$BUMP" 1.1.0 2026-06-07 "$ROOT"
|
||||
|
||||
fail() { echo "FAIL: $1"; exit 1; }
|
||||
have() { grep -q -- "$2" "$ROOT/$1" || fail "$1 missing: $2"; }
|
||||
missing() { ! grep -q -- "$2" "$ROOT/$1" || fail "$1 still has: $2"; }
|
||||
|
||||
# package version bumped, dependency version NOT touched
|
||||
have "Cargo.toml" 'version = "1.1.0"'
|
||||
have "Cargo.toml" 'foo = { version = "1.0.0" }'
|
||||
|
||||
have "install.sh" 'TERMSCP_VERSION="1.1.0"'
|
||||
have "README.md" 'Current version: 1.1.0 2026-06-07'
|
||||
missing "README.md" '2026-04-18'
|
||||
|
||||
have "site/html/home.html" 'termscp 1.1.0 is NOW out'
|
||||
have "site/lang/en.json" 'termscp 1.1.0 is NOW out'
|
||||
have "site/lang/zh-CN.json" 'termscp 1.1.0 is NOW out'
|
||||
have "site/html/get-started.html" 'termscp.1.1.0.nupkg'
|
||||
have "site/html/get-started.html" 'termscp_1.1.0_amd64.deb'
|
||||
have "dist/chocolatey/termscp.nuspec" '<version>1.1.0</version>'
|
||||
have "dist/chocolatey/tools/chocolateyinstall.ps1" 'releases/download/v1.1.0/termscp-v1.1.0-'
|
||||
missing "dist/chocolatey/tools/chocolateyinstall.ps1" 'v1.0.0'
|
||||
|
||||
# --- idempotency: running again at same version is a no-op (no error) ---
|
||||
"$BUMP" 1.1.0 2026-06-07 "$ROOT"
|
||||
have "Cargo.toml" 'version = "1.1.0"'
|
||||
|
||||
echo "PASS"
|
||||
@@ -1,16 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
which rpmbuild > /dev/null
|
||||
if [ $? -ne 0 ]; then
|
||||
echo "You must install rpmbuild on your machine"
|
||||
fi
|
||||
echo "Installing cargo-rpm..."
|
||||
cargo install cargo-rpm
|
||||
if [ ! -f "Cargo.toml" ]; then
|
||||
echo "Yout must be in the project root directory"
|
||||
exit 1
|
||||
fi
|
||||
echo "Running cargo-rpm"
|
||||
cargo rpm init
|
||||
cargo rpm build
|
||||
exit $?
|
||||
@@ -0,0 +1 @@
|
||||
docs.termscp.rs
|
||||
@@ -1,291 +0,0 @@
|
||||
# termscp
|
||||
|
||||
<p align="center">
|
||||
<img src="/assets/images/termscp.svg" width="256" height="256" />
|
||||
</p>
|
||||
|
||||
<p align="center">~ Eine funktionsreiche Terminal-Dateiübertragung ~</p>
|
||||
<p align="center">
|
||||
<a href="https://termscp.veeso.dev" target="_blank">Webseite</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#get-started" target="_blank">Installation</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#user-manual" target="_blank">Benutzerhandbuch</a>
|
||||
</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/gb.png"
|
||||
alt="English"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/de/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/de.png"
|
||||
alt="Deutsch"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/es/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/es.png"
|
||||
alt="Español"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/fr/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/fr.png"
|
||||
alt="Français"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/it/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/it.png"
|
||||
alt="Italiano"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/zh-CN/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/cn.png"
|
||||
alt="简体中文"
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
<p align="center">Entwickelt von <a href="https://veeso.dev/" target="_blank">@veeso</a></p>
|
||||
<p align="center">Aktuelle Version: 0.12.3 (06/10/2023)</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://opensource.org/licenses/MIT"
|
||||
><img
|
||||
src="https://img.shields.io/badge/License-MIT-teal.svg"
|
||||
alt="License-MIT"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/stargazers"
|
||||
><img
|
||||
src="https://img.shields.io/github/stars/veeso/termscp.svg"
|
||||
alt="Repo stars"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/d/termscp.svg"
|
||||
alt="Downloads counter"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/v/termscp.svg"
|
||||
alt="Latest version"
|
||||
/></a>
|
||||
<a href="https://ko-fi.com/veeso">
|
||||
<img
|
||||
src="https://img.shields.io/badge/donate-ko--fi-red"
|
||||
alt="Ko-fi"
|
||||
/></a>
|
||||
</p>
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Linux/badge.svg"
|
||||
alt="Linux CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/MacOS/badge.svg"
|
||||
alt="MacOS CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Windows/badge.svg"
|
||||
alt="Windows CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/FreeBSD/badge.svg"
|
||||
alt="FreeBSD CI"
|
||||
/></a>
|
||||
<a href="https://coveralls.io/github/veeso/termscp"
|
||||
><img
|
||||
src="https://coveralls.io/repos/github/veeso/termscp/badge.svg"
|
||||
alt="Coveralls"
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
---
|
||||
|
||||
## Über termscp 🖥
|
||||
|
||||
Termscp ist ein funktionsreicher Terminal-Dateitransfer und Explorer mit Unterstützung für SCP/SFTP/FTP/S3. Im Grunde handelt es sich also um ein Terminal-Dienstprogramm mit einer TUI, um eine Verbindung zu einem Remote-Server herzustellen, um Dateien abzurufen und hochzuladen und mit dem lokalen Dateisystem zu interagieren. Es ist **Linux**, **MacOS**, **FreeBSD** und **Windows** kompatibel.
|
||||
|
||||

|
||||
|
||||
---
|
||||
|
||||
## Features 🎁
|
||||
|
||||
- 📁 Verschiedene Kommunikationsprotokolle
|
||||
- **SFTP**
|
||||
- **SCP**
|
||||
- **FTP** und **FTPS**
|
||||
- **S3**
|
||||
- **SMB**
|
||||
- 🖥 Erkunden und bedienen Sie das Dateisystem der Fernbedienung und des lokalen Computers mit einer praktischen Benutzeroberfläche
|
||||
- Erstellen, Entfernen, Umbenennen, Suchen, Anzeigen und Bearbeiten von Dateien
|
||||
- ⭐ Verbinden Sie sich über integrierte Lesezeichen und aktuelle Verbindungen mit Ihren Lieblingshosts
|
||||
- 📝 Anzeigen und Bearbeiten von Dateien mit Ihren bevorzugten Anwendungen
|
||||
- 💁 SFTP/SCP-Authentifizierung mit SSH-Schlüsseln und Benutzername/Passwort
|
||||
- 🐧 Kompatibel mit Windows, Linux, FreeBSD und MacOS
|
||||
- 🎨 Mach es zu deinem!
|
||||
- Themen
|
||||
- Benutzerdefiniertes Datei-Explorer-Format
|
||||
- Anpassbarer Texteditor
|
||||
- Anpassbare Dateisortierung
|
||||
- und viele andere Parameter...
|
||||
- 📫 Lassen Sie sich benachrichtigen, wenn eine große Datei übertragen wurde
|
||||
- 🔭 Halten Sie Dateiänderungen mit dem Remote-Host synchron
|
||||
- 🔐 Speichern Sie Ihr Passwort in Ihrem Betriebssystem-Schlüsseltresor
|
||||
- 🦀 Rust-powered
|
||||
- 👀 Entwickelt, um die Leistung im Auge zu behalten
|
||||
- 🦄 Häufige tolle Updates
|
||||
|
||||
---
|
||||
|
||||
## Loslegen 🚀
|
||||
|
||||
Wenn Sie überlegen, termscp zu installieren, möchte ich Ihnen danken 💜 ! Ich hoffe, Sie werden Termscp genießen!
|
||||
Wenn Sie zu diesem Projekt beitragen möchten, vergessen Sie nicht, unseren [Beitragsleitfaden](../../CONTRIBUTING.md) zu lesen.
|
||||
|
||||
Wenn Sie ein Linux-, FreeBSD- oder MacOS-Benutzer sind, installiert dieses einfache Shell-Skript termscp mit einem einzigen Befehl auf Ihrem System:
|
||||
|
||||
```sh
|
||||
curl -sSLf http://get-termscp.veeso.dev | sh
|
||||
```
|
||||
|
||||
Wenn Sie ein Windows-Benutzer sind, können Sie termscp mit [Chocolatey](https://chocolatey.org/) installieren:
|
||||
|
||||
```sh
|
||||
choco install termscp
|
||||
```
|
||||
|
||||
Für weitere Informationen oder andere Plattformen besuchen Sie bitte [termscp.veeso.dev](https://termscp.veeso.dev/termscp/#get-started), um alle Installationsmethoden anzuzeigen.
|
||||
|
||||
⚠️ Wenn Sie wissen möchten, wie Sie termscp aktualisieren können, führen Sie einfach termscp über die CLI aus mit: `(sudo) termscp --update` ⚠️
|
||||
|
||||
### Softwareanforderungen ❗
|
||||
|
||||
- **Linux** Benutzer:
|
||||
- libssh
|
||||
- libdbus-1
|
||||
- pkg-config
|
||||
- libsmbclient
|
||||
- **FreeBSD** Benutzer:
|
||||
- libssh
|
||||
- dbus
|
||||
- pkgconf
|
||||
- libsmbclient
|
||||
|
||||
### Optionale Softwareanforderungen ✔️
|
||||
|
||||
Diese Anforderungen sind nicht zwingend erforderlich, um termscp auszuführen, sondern um alle Funktionen nutzen zu können
|
||||
|
||||
- **Linux/FreeBSD** Benutzer:
|
||||
- Um Dateien mit `V` zu **öffnen** (mindestens eines davon)
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- **Linux** Benutzer:
|
||||
- Ein Keyring-manager: Lesen Sie mehr in der [Bedienungsanleitung](man.md#linux-keyring)
|
||||
- **WSL** Benutzer
|
||||
- Um Dateien mit `V` zu **öffnen** (mindestens eines davon)
|
||||
- [wslu](https://github.com/wslutilities/wslu)
|
||||
|
||||
---
|
||||
|
||||
## Unterstütze mich ☕
|
||||
|
||||
Wenn Ihnen termscp gefällt und Sie für die Arbeit, die ich geleistet habe, dankbar sind, denken Sie bitte über eine kleine Spende nach 🥳
|
||||
|
||||
Sie können mit einer dieser Plattformen spenden:
|
||||
|
||||
[](https://ko-fi.com/veeso)
|
||||
[](https://www.paypal.me/chrisintin)
|
||||
|
||||
---
|
||||
|
||||
## User manual 📚
|
||||
|
||||
Das Benutzerhandbuch finden Sie auf der [termscp-Website](https://termscp.veeso.dev/termscp/#user-manual) oder auf [Github](man.md).
|
||||
|
||||
---
|
||||
|
||||
## Contributing and issues 🤝🏻
|
||||
|
||||
Beiträge, Fehlerberichte, neue Funktionen und Fragen sind willkommen! 😉
|
||||
Wenn Sie Fragen oder Bedenken haben, eine neue Funktion vorschlagen oder einfach nur die Bedingungen verbessern möchten, können Sie ein Problem oder eine PR erstellen.
|
||||
|
||||
Bitte befolgen Sie [unsere Beitragsrichtlinien](../../CONTRIBUTING.md)
|
||||
|
||||
---
|
||||
|
||||
## Changelog ⏳
|
||||
|
||||
Änderungsprotokoll von termscp ansehen [HIER](../../CHANGELOG.md)
|
||||
|
||||
---
|
||||
|
||||
## Powered by 💪
|
||||
|
||||
termscp wird von diesen großartigen Projekten unterstützt:
|
||||
|
||||
- [bytesize](https://github.com/hyunsik/bytesize)
|
||||
- [crossterm](https://github.com/crossterm-rs/crossterm)
|
||||
- [edit](https://github.com/milkey-mouse/edit)
|
||||
- [keyring-rs](https://github.com/hwchen/keyring-rs)
|
||||
- [open-rs](https://github.com/Byron/open-rs)
|
||||
- [rpassword](https://github.com/conradkleinespel/rpassword)
|
||||
- [rust-s3](https://github.com/durch/rust-s3)
|
||||
- [self_update](https://github.com/jaemk/self_update)
|
||||
- [ssh2-rs](https://github.com/alexcrichton/ssh2-rs)
|
||||
- [suppaftp](https://github.com/veeso/suppaftp)
|
||||
- [tui-rs](https://github.com/fdehau/tui-rs)
|
||||
- [tui-realm](https://github.com/veeso/tui-realm)
|
||||
- [whoami](https://github.com/libcala/whoami)
|
||||
- [wildmatch](https://github.com/becheran/wildmatch)
|
||||
|
||||
---
|
||||
|
||||
## Galerie 🎬
|
||||
|
||||
> Termscp Home
|
||||
|
||||

|
||||
|
||||
> Bookmarks
|
||||
|
||||

|
||||
|
||||
> Setup
|
||||
|
||||

|
||||
|
||||
> Text editor
|
||||
|
||||

|
||||
|
||||
---
|
||||
|
||||
## License 📃
|
||||
|
||||
termscp ist unter der MIT-Lizenz lizenziert.
|
||||
|
||||
Du kannst die gesamte Lizenz [HIER](../../LICENSE) lesen
|
||||
@@ -1,559 +0,0 @@
|
||||
# User manual 🎓
|
||||
|
||||
- [User manual 🎓](#user-manual-)
|
||||
- [Usage ❓](#usage-)
|
||||
- [Address argument 🌎](#address-argument-)
|
||||
- [AWS S3 address argument](#aws-s3-address-argument)
|
||||
- [SMB address argument](#smb-address-argument)
|
||||
- [How Password can be provided 🔐](#how-password-can-be-provided-)
|
||||
- [S3 connection parameters](#s3-connection-parameters)
|
||||
- [S3 credentials 🦊](#s3-credentials-)
|
||||
- [File explorer 📂](#file-explorer-)
|
||||
- [Keybindings ⌨](#keybindings-)
|
||||
- [Work on multiple files 🥷](#work-on-multiple-files-)
|
||||
- [Synchronized browsing ⏲️](#synchronized-browsing-️)
|
||||
- [Open and Open With 🚪](#open-and-open-with-)
|
||||
- [Bookmarks ⭐](#bookmarks-)
|
||||
- [Are my passwords Safe 😈](#are-my-passwords-safe-)
|
||||
- [Linux Keyring](#linux-keyring)
|
||||
- [KeepassXC setup for termscp](#keepassxc-setup-for-termscp)
|
||||
- [Configuration ⚙️](#configuration-️)
|
||||
- [SSH Key Storage 🔐](#ssh-key-storage-)
|
||||
- [File Explorer Format](#file-explorer-format)
|
||||
- [Themes 🎨](#themes-)
|
||||
- [My theme won't load 😱](#my-theme-wont-load-)
|
||||
- [Styles 💈](#styles-)
|
||||
- [Authentication page](#authentication-page)
|
||||
- [Transfer page](#transfer-page)
|
||||
- [Misc](#misc)
|
||||
- [Text Editor ✏](#text-editor-)
|
||||
- [Logging 🩺](#logging-)
|
||||
- [Notifications 📫](#notifications-)
|
||||
- [File watcher 🔭](#file-watcher-)
|
||||
|
||||
> ❗ I need a help to translate this manual into German. If you want to contribute to the translations, please open a PR 🙏
|
||||
|
||||
## Usage ❓
|
||||
|
||||
termscp can be started with the following options:
|
||||
|
||||
`termscp [options]... [protocol://user@address:port:wrkdir] [local-wrkdir]`
|
||||
|
||||
OR
|
||||
|
||||
`termscp [options]... -b [bookmark-name] [local-wrkdir]`
|
||||
|
||||
- `-P, --password <password>` if address is provided, password will be this argument
|
||||
- `-b, --address-as-bookmark` resolve address argument as a bookmark name
|
||||
- `-c, --config` Open termscp starting from the configuration page
|
||||
- `-q, --quiet` Disable logging
|
||||
- `-t, --theme <path>` Import specified theme
|
||||
- `-u, --update` Update termscp to latest version
|
||||
- `-v, --version` Print version info
|
||||
- `-h, --help` Print help page
|
||||
|
||||
termscp can be started in three different modes, if no extra arguments is provided, termscp will show the authentication form, where the user will be able to provide the parameters required to connect to the remote peer.
|
||||
|
||||
Alternatively, the user can provide an address as argument to skip the authentication form and starting directly the connection to the remote server.
|
||||
|
||||
If address argument or bookmark name is provided you can also provide the start working directory for local host
|
||||
|
||||
### Address argument 🌎
|
||||
|
||||
The address argument has the following syntax:
|
||||
|
||||
```txt
|
||||
[protocol://][username@]<address>[:port][:wrkdir]
|
||||
```
|
||||
|
||||
Let's see some example of this particular syntax, since it's very comfortable and you'll probably going to use this instead of the other one...
|
||||
|
||||
- Connect using default protocol (*defined in configuration*) to 192.168.1.31, port if not provided is default for the selected protocol (in this case depends on your configuration); username is current user's name
|
||||
|
||||
```sh
|
||||
termscp 192.168.1.31
|
||||
```
|
||||
|
||||
- Connect using default protocol (*defined in configuration*) to 192.168.1.31; username is `root`
|
||||
|
||||
```sh
|
||||
termscp root@192.168.1.31
|
||||
```
|
||||
|
||||
- Connect using scp to 192.168.1.31, port is 4022; username is `omar`
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022
|
||||
```
|
||||
|
||||
- Connect using scp to 192.168.1.31, port is 4022; username is `omar`. You will start in directory `/tmp`
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022:/tmp
|
||||
```
|
||||
|
||||
#### AWS S3 address argument
|
||||
|
||||
Aws S3 has a different syntax for CLI address argument, for obvious reasons, but I managed to keep it the more similar as possible to the generic address argument:
|
||||
|
||||
```txt
|
||||
s3://<bucket-name>@<region>[:profile][:/wrkdir]
|
||||
```
|
||||
|
||||
e.g.
|
||||
|
||||
```txt
|
||||
s3://buckethead@eu-central-1:default:/assets
|
||||
```
|
||||
|
||||
#### SMB address argument
|
||||
|
||||
SMB has a different syntax for CLI address argument, which is different whether you're on Windows or other systems:
|
||||
|
||||
**Windows** syntax:
|
||||
|
||||
```txt
|
||||
\\[username@]<server-name>\<share>[\path\...]
|
||||
```
|
||||
|
||||
**Other systems** syntax:
|
||||
|
||||
```txt
|
||||
smb://[username@]<server-name>[:port]/<share>[/path/.../]
|
||||
```
|
||||
|
||||
#### How Password can be provided 🔐
|
||||
|
||||
You have probably noticed, that, when providing the address as argument, there's no way to provide the password.
|
||||
Password can be basically provided through 3 ways when address argument is provided:
|
||||
|
||||
- `-P, --password` option: just use this CLI option providing the password. I strongly unrecommend this method, since it's very unsecure (since you might keep the password in the shell history)
|
||||
- Via `sshpass`: you can provide password via `sshpass`, e.g. `sshpass -f ~/.ssh/topsecret.key termscp cvisintin@192.168.1.31`
|
||||
- You will be prompted for it: if you don't use any of the previous methods, you will be prompted for the password, as happens with the more classics tools such as `scp`, `ssh`, etc.
|
||||
|
||||
---
|
||||
|
||||
## S3 connection parameters
|
||||
|
||||
These parameters are required to connect to aws s3 and other s3 compatible servers:
|
||||
|
||||
- AWS S3:
|
||||
- **bucket name**
|
||||
- **region**
|
||||
- *profile* (if not provided: "default")
|
||||
- *access key* (unless if public)
|
||||
- *secret access key* (unless if public)
|
||||
- *security token* (if required)
|
||||
- *session token* (if required)
|
||||
- new path style: **NO**
|
||||
- Other S3 endpoints:
|
||||
- **bucket name**
|
||||
- **endpoint**
|
||||
- *access key* (unless if public)
|
||||
- *secret access key* (unless if public)
|
||||
- new path style: **YES**
|
||||
|
||||
### S3 credentials 🦊
|
||||
|
||||
In order to connect to an Aws S3 bucket you must obviously provide some credentials.
|
||||
There are basically three ways to achieve this.
|
||||
So these are the ways you can provide the credentials for s3:
|
||||
|
||||
1. Authentication form:
|
||||
1. You can provide the `access_key` (should be mandatory), the `secret_access_key` (should be mandatory), `security_token` and the `session_token`
|
||||
2. If you save the s3 connection as a bookmark, these credentials will be saved as an encrypted AES-256/BASE64 string in your bookmarks file (except for the security token and session token which are meant to be temporary credentials).
|
||||
2. Use your credentials file: just configure the AWS cli via `aws configure` and your credentials should already be located at `~/.aws/credentials`. In case you're using a profile different from `default`, just provide it in the profile field in the authentication form.
|
||||
3. **Environment variables**: you can always provide your credentials as environment variables. Keep in mind that these credentials **will always override** the credentials located in the `credentials` file. See how to configure the environment below:
|
||||
|
||||
These should always be mandatory:
|
||||
|
||||
- `AWS_ACCESS_KEY_ID`: aws access key ID (usually starts with `AKIA...`)
|
||||
- `AWS_SECRET_ACCESS_KEY`: the secret access key
|
||||
|
||||
In case you've configured a stronger security, you *may* require these too:
|
||||
|
||||
- `AWS_SECURITY_TOKEN`: security token
|
||||
- `AWS_SESSION_TOKEN`: session token
|
||||
|
||||
⚠️ Your credentials are safe: termscp won't manipulate these values directly! Your credentials are directly consumed by the **s3** crate.
|
||||
In case you've got some concern regarding security, please contact the library author on [Github](https://github.com/durch/rust-s3) ⚠️
|
||||
|
||||
---
|
||||
|
||||
## File explorer 📂
|
||||
|
||||
When we refer to file explorers in termscp, we refer to the panels you can see after establishing a connection with the remote.
|
||||
These panels are basically 3 (yes, three actually):
|
||||
|
||||
- Local explorer panel: it is displayed on the left of your screen and shows the current directory entries for localhost
|
||||
- Remote explorer panel: it is displayed on the right of your screen and shows the current directory entries for the remote host.
|
||||
- Find results panel: depending on where you're searching for files (local/remote) it will replace the local or the explorer panel. This panel shows the entries matching the search query you performed.
|
||||
|
||||
In order to change panel you need to type `<LEFT>` to move the remote explorer panel and `<RIGHT>` to move back to the local explorer panel. Whenever you are in the find results panel, you need to press `<ESC>` to exit panel and go back to the previous panel.
|
||||
|
||||
### Keybindings ⌨
|
||||
|
||||
| Key | Command | Reminder |
|
||||
|---------------|-------------------------------------------------------|-------------|
|
||||
| `<ESC>` | Disconnect from remote; return to authentication page | |
|
||||
| `<BACKSPACE>` | Go to previous directory in stack | |
|
||||
| `<TAB>` | Switch explorer tab | |
|
||||
| `<RIGHT>` | Move to remote explorer tab | |
|
||||
| `<LEFT>` | Move to local explorer tab | |
|
||||
| `<UP>` | Move up in selected list | |
|
||||
| `<DOWN>` | Move down in selected list | |
|
||||
| `<PGUP>` | Move up in selected list by 8 rows | |
|
||||
| `<PGDOWN>` | Move down in selected list by 8 rows | |
|
||||
| `<ENTER>` | Enter directory | |
|
||||
| `<SPACE>` | Upload / download selected file | |
|
||||
| `<BACKTAB>` | Switch between log tab and explorer | |
|
||||
| `<A>` | Toggle hidden files | All |
|
||||
| `<B>` | Sort files by | Bubblesort? |
|
||||
| `<C|F5>` | Copy file/directory | Copy |
|
||||
| `<D|F7>` | Make directory | Directory |
|
||||
| `<E|F8|DEL>` | Delete file | Erase |
|
||||
| `<F>` | Search for files (wild match is supported) | Find |
|
||||
| `<G>` | Go to supplied path | Go to |
|
||||
| `<H|F1>` | Show help | Help |
|
||||
| `<K>` | Create symlink pointing to the currently selected entry | symlinK |
|
||||
| `<I>` | Show info about selected file or directory | Info |
|
||||
| `<L>` | Reload current directory's content / Clear selection | List |
|
||||
| `<M>` | Select a file | Mark |
|
||||
| `<N>` | Create new file with provided name | New |
|
||||
| `<O|F4>` | Edit file; see Text editor | Open |
|
||||
| `<P>` | Open log panel | Panel |
|
||||
| `<Q|F10>` | Quit termscp | Quit |
|
||||
| `<R|F6>` | Rename file | Rename |
|
||||
| `<S|F2>` | Save file as... | Save |
|
||||
| `<T>` | Synchronize changes to selected path to remote | Track |
|
||||
| `<U>` | Go to parent directory | Upper |
|
||||
| `<V|F3>` | Open file with default program for filetype | View |
|
||||
| `<W>` | Open file with provided program | With |
|
||||
| `<X>` | Execute a command | eXecute |
|
||||
| `<Y>` | Toggle synchronized browsing | sYnc |
|
||||
| `<Z>` | Change file mode | |
|
||||
| `<CTRL+A>` | Select all files | |
|
||||
| `<CTRL+C>` | Abort file transfer process | |
|
||||
| `<CTRL+T>` | Show all synchronized paths | Track |
|
||||
|
||||
### Work on multiple files 🥷
|
||||
|
||||
You can opt to work on multiple files, selecting them pressing `<M>`, in order to select the current file, or pressing `<CTRL+A>`, which will select all the files in the working directory.
|
||||
Once a file is marked for selection, it will be displayed with a `*` on the left.
|
||||
When working on selection, only selected file will be processed for actions, while the current highlighted item will be ignored.
|
||||
It is possible to work on multiple files also when in the find result panel.
|
||||
All the actions are available when working with multiple files, but be aware that some actions work in a slightly different way. Let's dive in:
|
||||
|
||||
- *Copy*: whenever you copy a file, you'll be prompted to insert the destination name. When working with multiple file, this name refers to the destination directory where all these files will be copied.
|
||||
- *Rename*: same as copy, but will move files there.
|
||||
- *Save as*: same as copy, but will write them there.
|
||||
|
||||
### Synchronized browsing ⏲️
|
||||
|
||||
When enabled, synchronized browsing, will allow you to synchronize the navigation between the two panels.
|
||||
This means that whenever you'll change the working directory on one panel, the same action will be reproduced on the other panel. If you want to enable synchronized browsing just press `<Y>`; press twice to disable. While enabled, the synchronized browsing state will be reported on the status bar on `ON`.
|
||||
|
||||
### Open and Open With 🚪
|
||||
|
||||
Open and open with commands are powered by [open-rs](https://docs.rs/crate/open/1.7.0).
|
||||
When opening files with View command (`<V>`), the system default application for the file type will be used. To do so, the default operting system service will be used, so be sure to have at least one of these installed on your system:
|
||||
|
||||
- **Windows** users: you don't have to worry about it, since the crate will use the `start` command.
|
||||
- **MacOS** users: you don't have to worry either, since the crate will use `open`, which is already installed on your system.
|
||||
- **Linux** users: one of these should be installed
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- **WSL** users: *wslview* is required, you must install [wslu](https://github.com/wslutilities/wslu).
|
||||
|
||||
> Q: Can I edit remote files using the view command?
|
||||
> A: No, at least not directly from the "remote panel". You have to download it to a local directory first, that's due to the fact that when you open a remote file, the file is downloaded into a temporary directory, but there's no way to create a watcher for the file to check when the program you used to open it was closed, so termscp is not able to know when you're done editing the file.
|
||||
|
||||
---
|
||||
|
||||
## Bookmarks ⭐
|
||||
|
||||
In termscp it is possible to save favourites hosts, which can be then loaded quickly from the main layout of termscp.
|
||||
termscp will also save the last 16 hosts you connected to.
|
||||
This feature allows you to load all the parameters required to connect to a certain remote, simply selecting the bookmark in the tab under the authentication form.
|
||||
|
||||
Bookmarks will be saved, if possible at:
|
||||
|
||||
- `$HOME/.config/termscp/` on Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` on MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` on Windows
|
||||
|
||||
For bookmarks only (this won't apply to recent hosts) it is also possible to save the password used to authenticate. The password is not saved by default and must be specified through the prompt when saving a new Bookmark.
|
||||
If you're concerned about the security of the password saved for your bookmarks, please read the [chapter below 👀](#are-my-passwords-safe-).
|
||||
|
||||
In order to create a new bookmark, just follow these steps:
|
||||
|
||||
1. Type in the authentication form the parameters to connect to your remote server
|
||||
2. Press `<CTRL+S>`
|
||||
3. Type in the name you want to give to the bookmark
|
||||
4. Choose whether to remind the password or not
|
||||
5. Press `<ENTER>` to submit
|
||||
|
||||
whenever you want to use the previously saved connection, just press `<TAB>` to navigate to the bookmarks list and load the bookmark parameters into the form pressing `<ENTER>`.
|
||||
|
||||
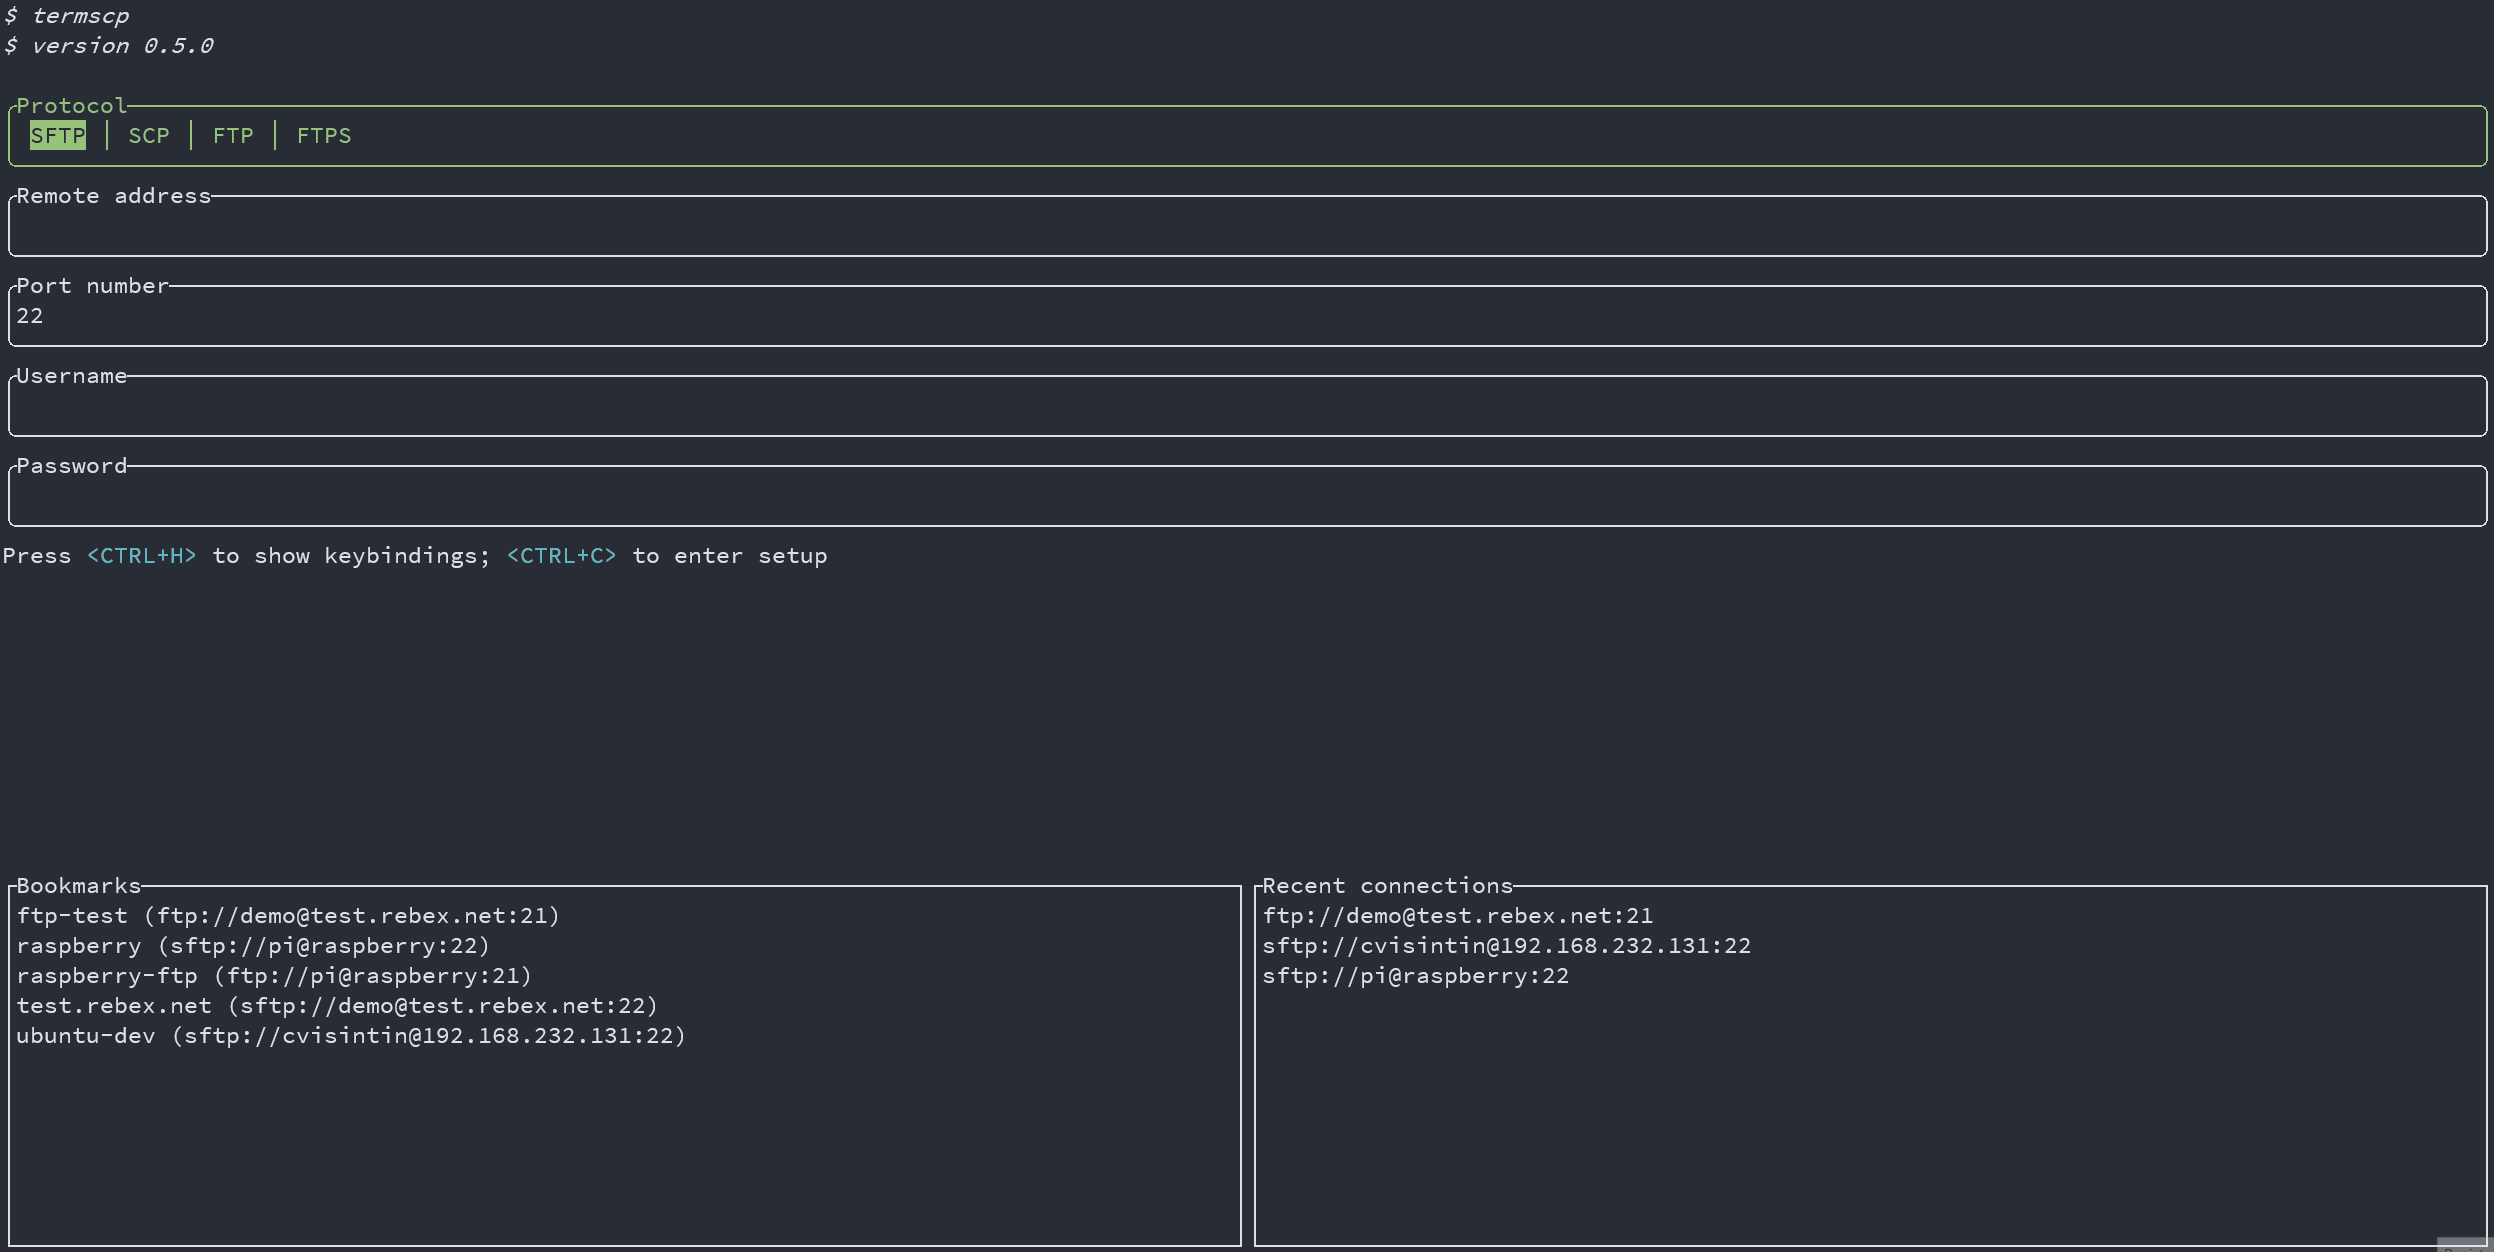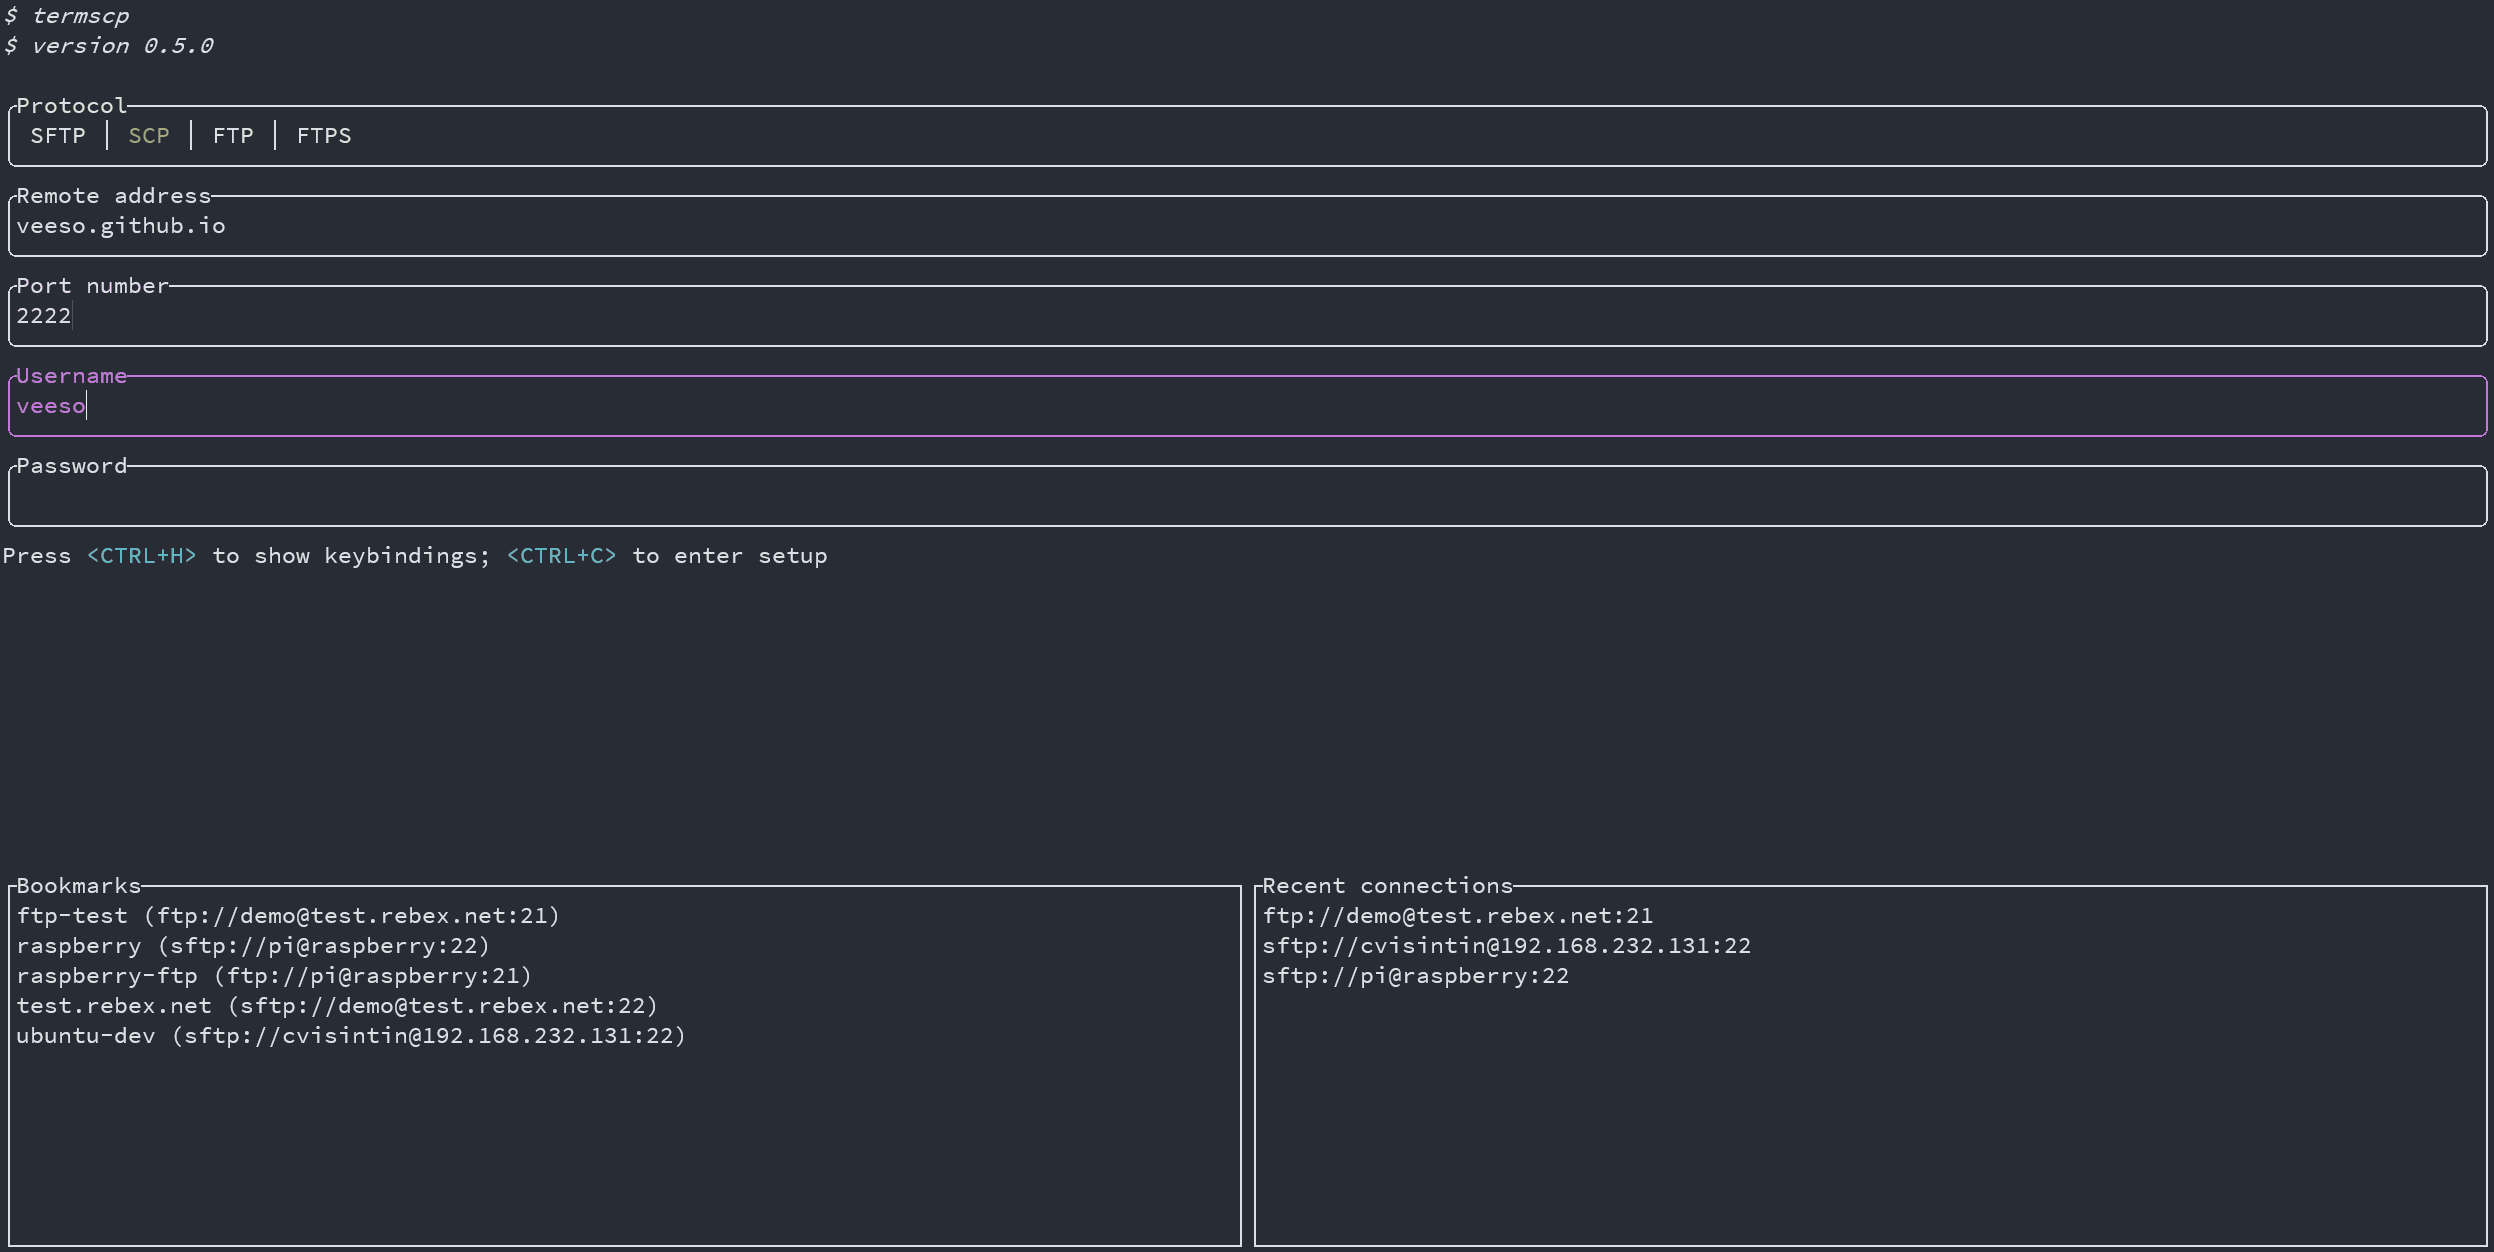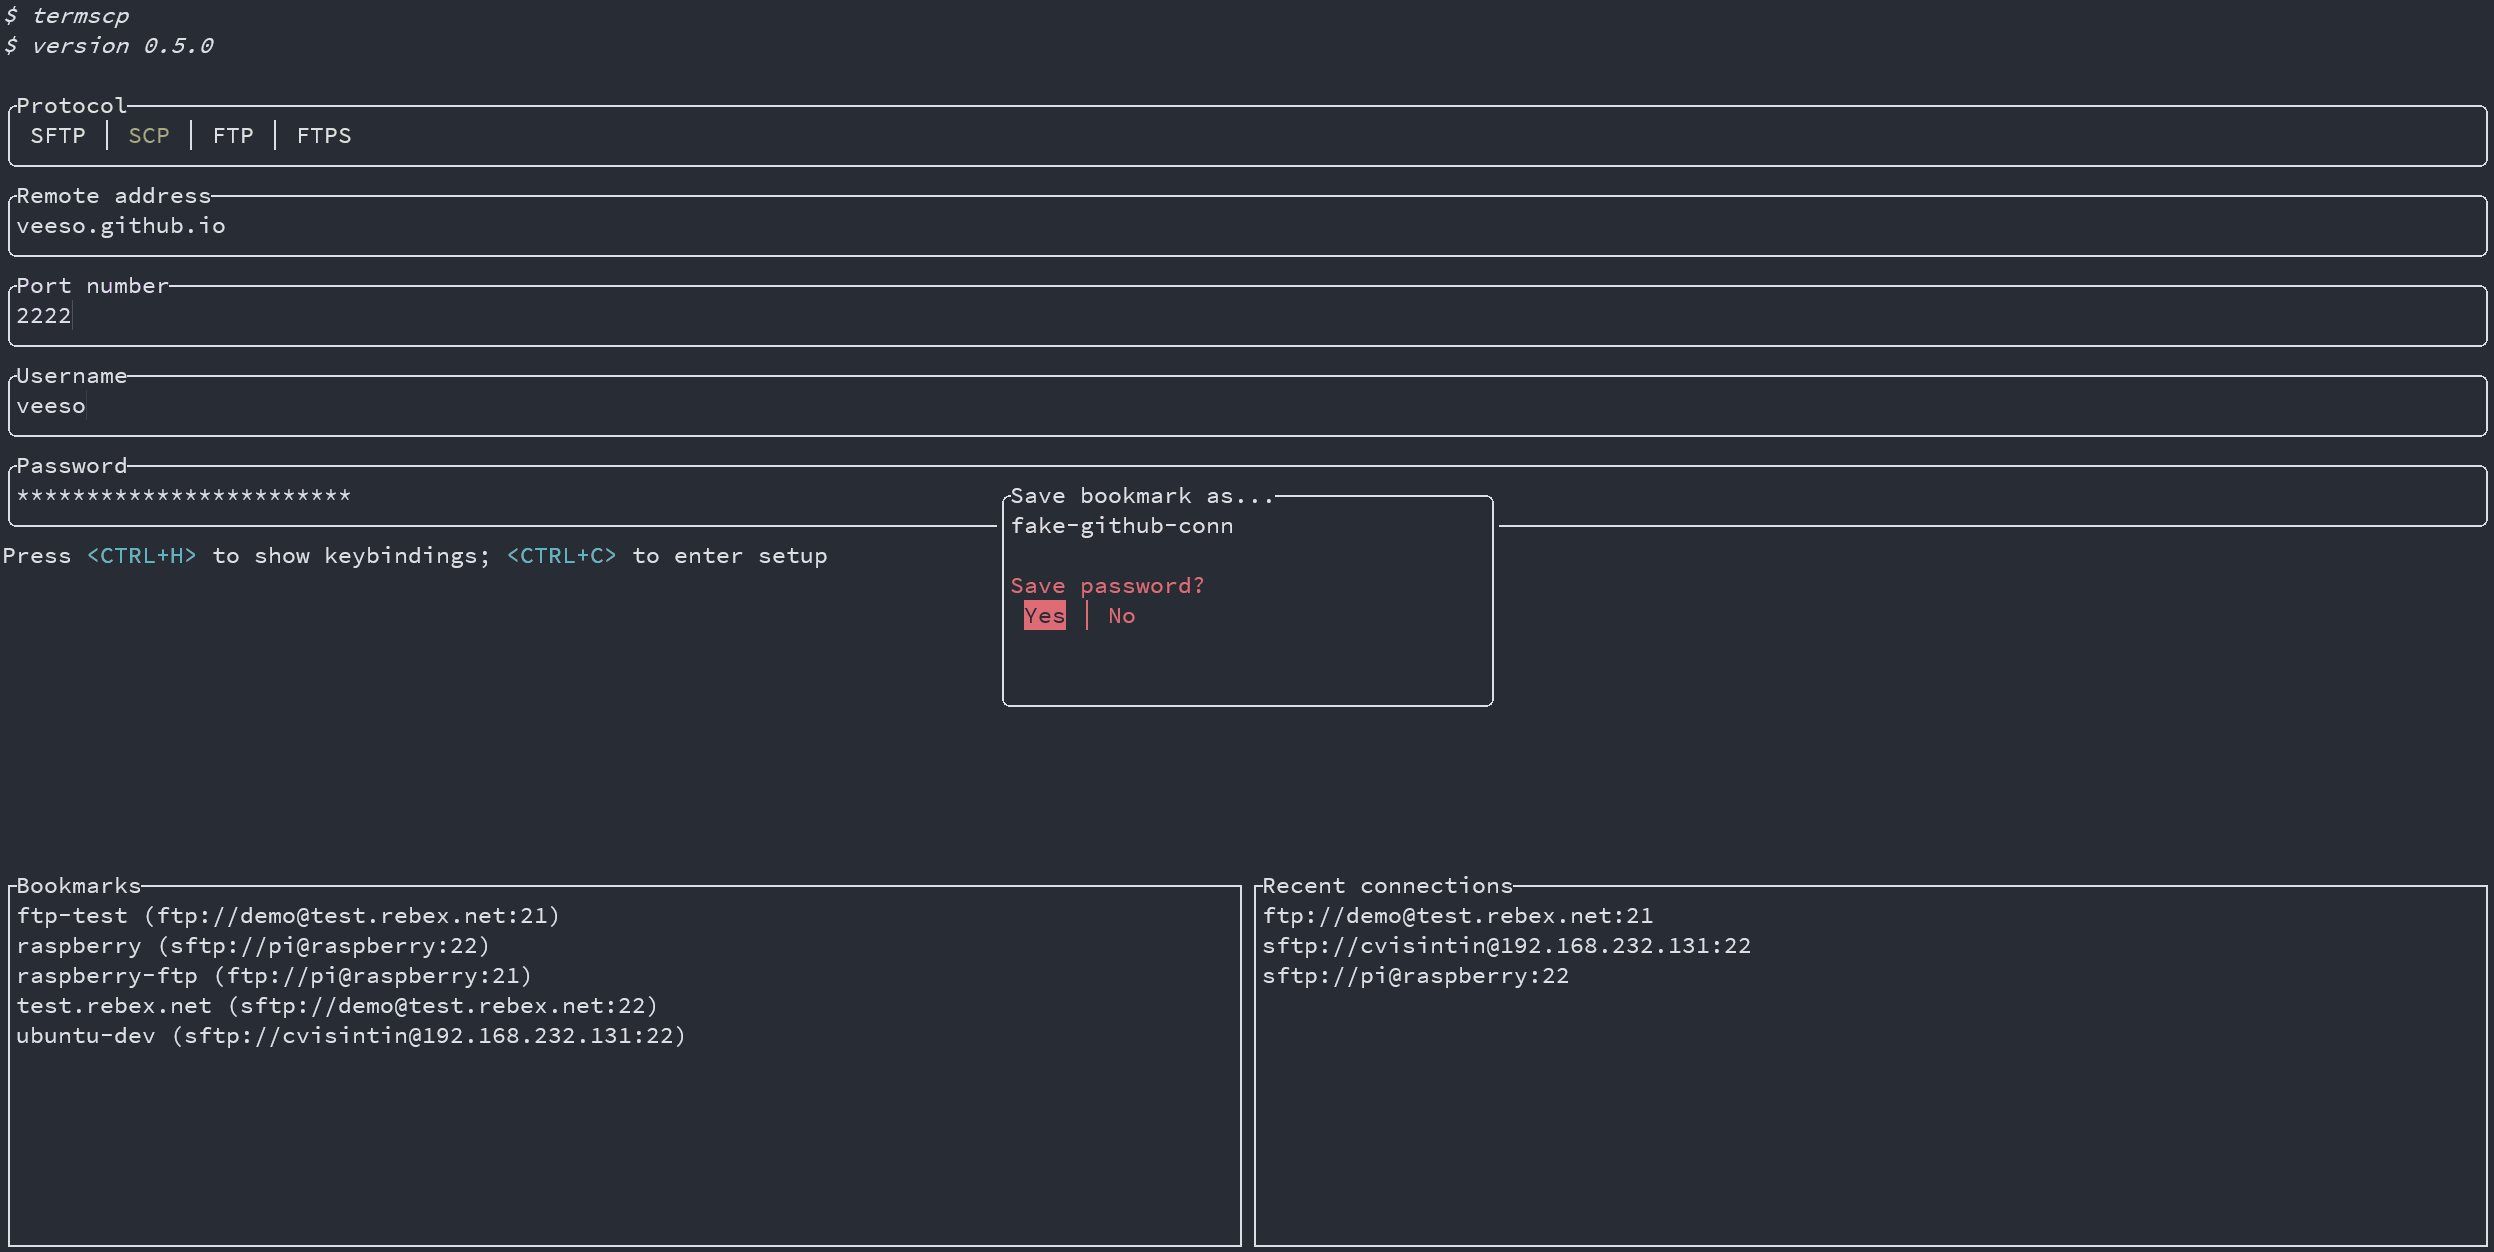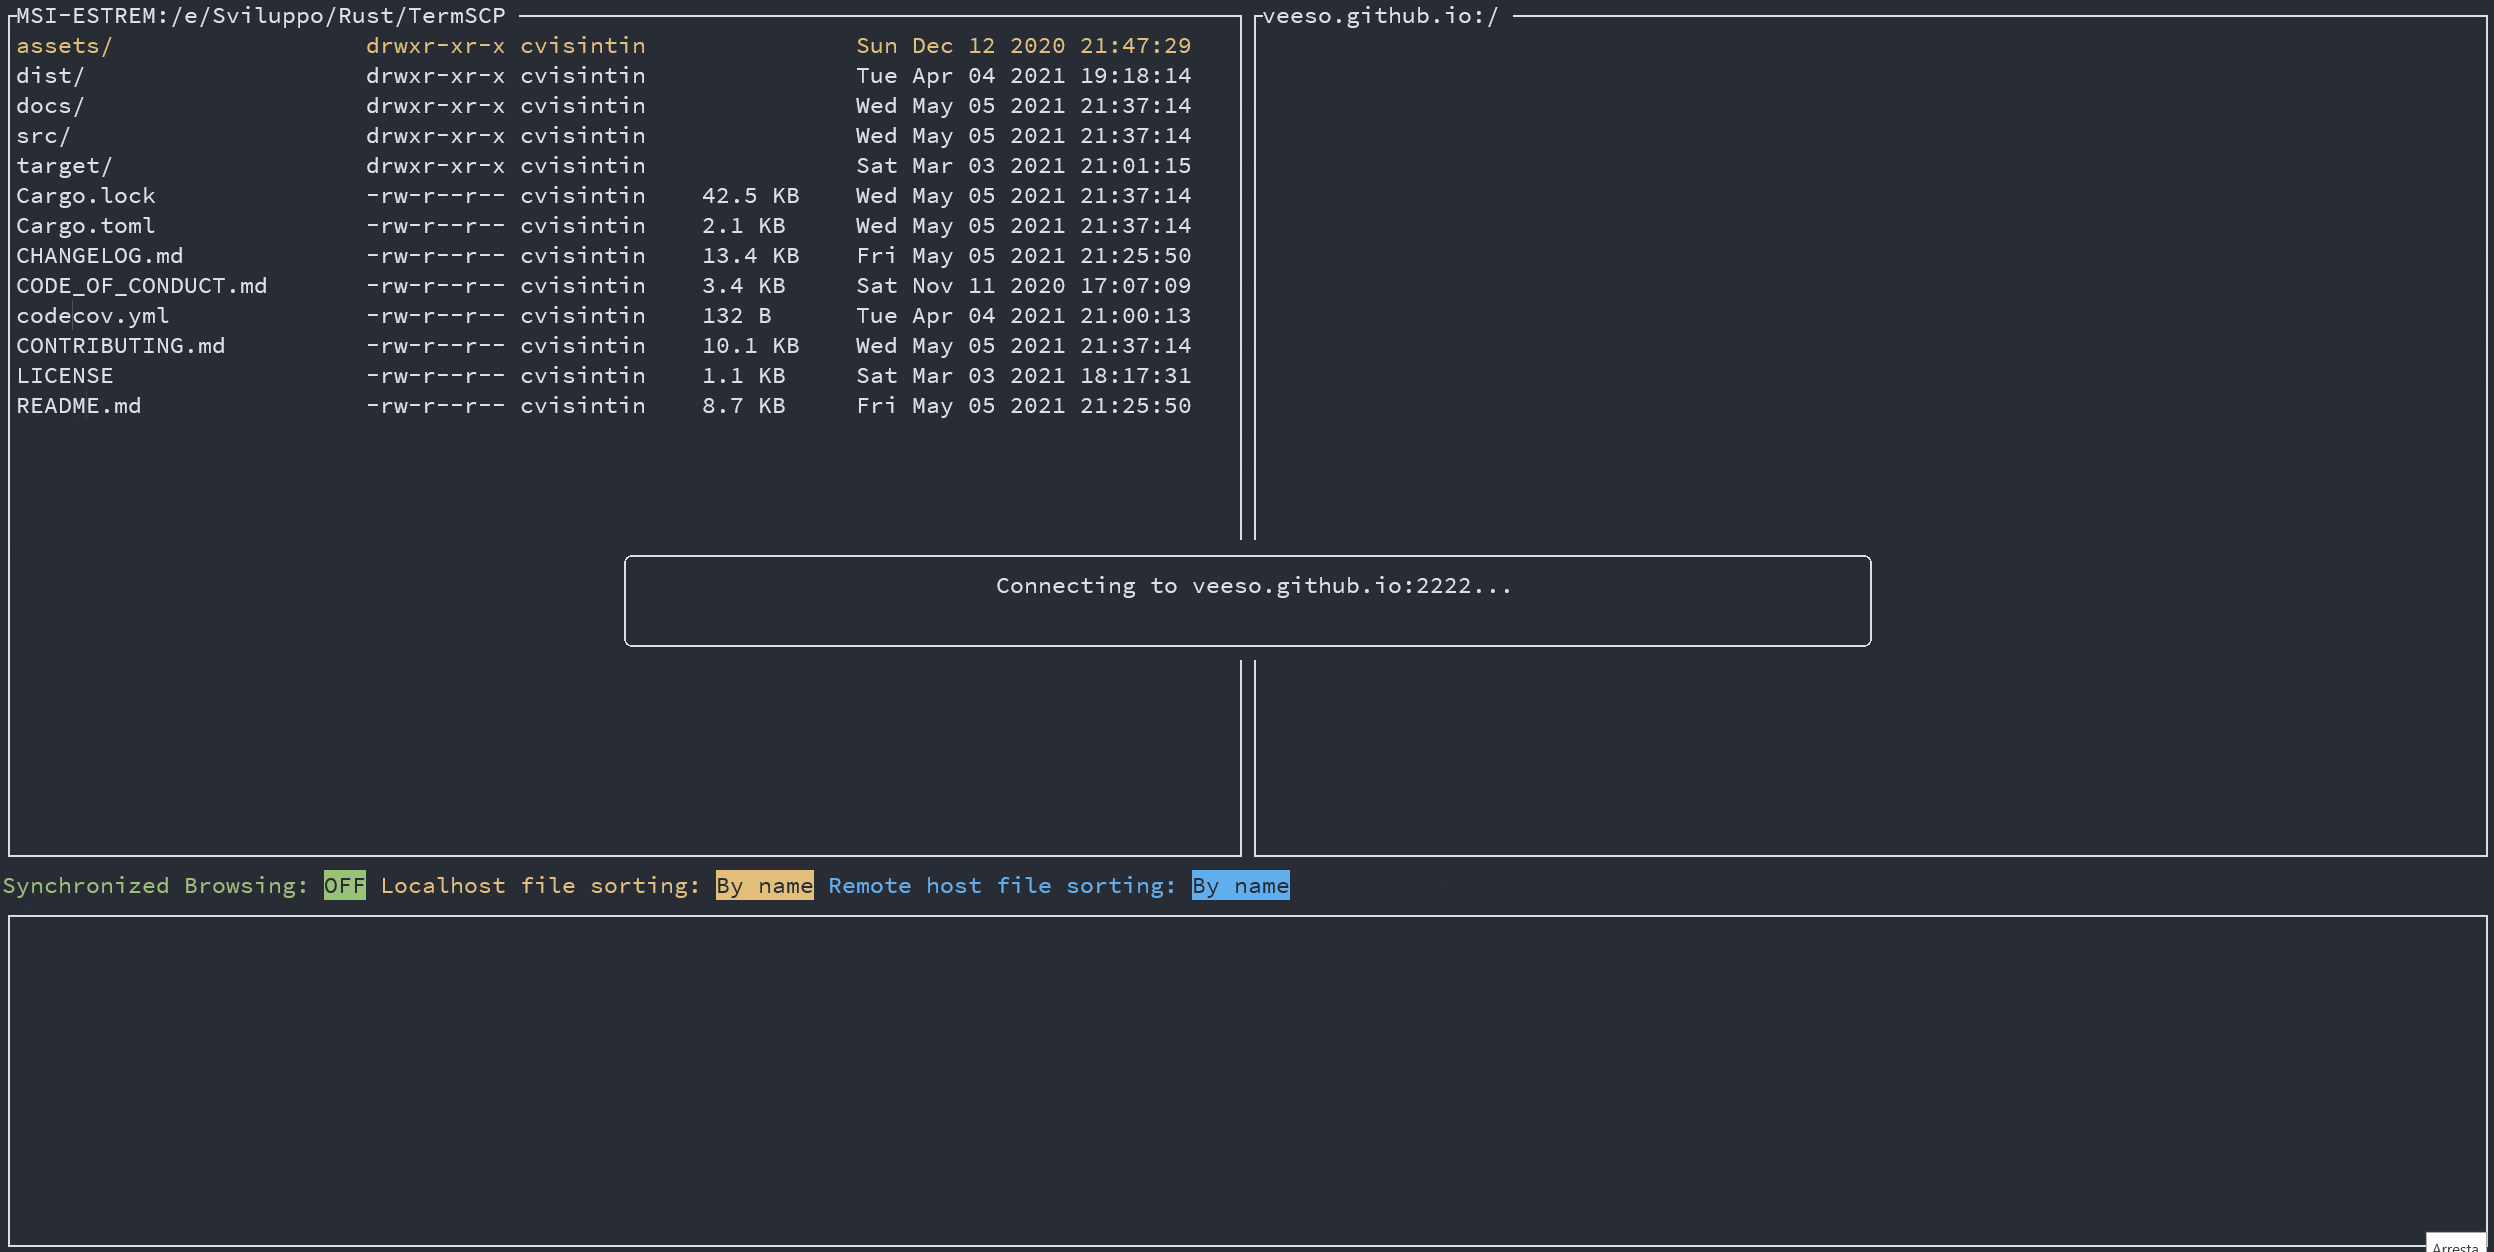
|
||||
|
||||
### Are my passwords Safe 😈
|
||||
|
||||
Sure 😉.
|
||||
As said before, bookmarks are saved in your configuration directory along with passwords. Passwords are obviously not plain text, they are encrypted with **AES-128**. Does this make them safe? Absolutely! (except for BSD and WSL users 😢)
|
||||
|
||||
On **Windows**, **Linux** and **MacOS** the key used to encrypt passwords is stored, if possible (but should be), respectively in the *Windows Vault*, in the *system keyring* and into the *Keychain*. This is actually super-safe and is directly managed by your operating system.
|
||||
|
||||
❗ Please, notice that if you're a Linux user, you'd better to read the [chapter below 👀](#linux-keyring), because the keyring might not be enabled or supported on your system!
|
||||
|
||||
On *BSD* and *WSL*, on the other hand, the key used to encrypt your passwords is stored on your drive (at $HOME/.config/termscp). It is then, still possible to retrieve the key to decrypt passwords. Luckily, the location of the key guarantees your key can't be read by users different from yours, but yeah, I still wouldn't save the password for a server exposed on the internet 😉.
|
||||
|
||||
#### Linux Keyring
|
||||
|
||||
We all love Linux thanks to the freedom it gives to the users. You can basically do anything you want as a Linux user, but this has also some cons, such as the fact that often there is no standard applications across different distributions. And this involves keyring too.
|
||||
This means that on Linux there might be no keyring installed on your system. Unfortunately the library we use to work with the key storage requires a service which exposes `org.freedesktop.secrets` on D-BUS and the worst fact is that there only two services exposing it.
|
||||
|
||||
- ❗ If you use GNOME as desktop environment (e.g. ubuntu users), you should already be fine, since keyring is already provided by `gnome-keyring` and everything should already be working.
|
||||
- ❗ For other desktop environment users there is a nice program you can use to get a keyring which is [KeepassXC](https://keepassxc.org/), which I use on my Manjaro installation (with KDE) and works fine. The only problem is that you have to setup it to be used along with termscp (but it's quite simple). To get started with KeepassXC read more [here](#keepassxc-setup-for-termscp).
|
||||
- ❗ What about you don't want to install any of these services? Well, there's no problem! **termscp will keep working as usual**, but it will save the key in a file, as it usually does for BSD and WSL.
|
||||
|
||||
##### KeepassXC setup for termscp
|
||||
|
||||
Follow these steps in order to setup keepassXC for termscp:
|
||||
|
||||
1. Install KeepassXC
|
||||
2. Go to "tools" > "settings" in toolbar
|
||||
3. Select "Secret service integration" and toggle "Enable KeepassXC freedesktop.org secret service integration"
|
||||
4. Create a database, if you don't have one yet: from toolbar "Database" > "New database"
|
||||
5. From toolbar: "Database" > "Database settings"
|
||||
6. Select "Secret service integration" and toggle "Expose entries under this group"
|
||||
7. Select the group in the list where you want the termscp secret to be kept. Remember that this group might be used by any other application to store secrets via DBUS.
|
||||
|
||||
---
|
||||
|
||||
## Configuration ⚙️
|
||||
|
||||
termscp supports some user defined parameters, which can be defined in the configuration.
|
||||
Underhood termscp has a TOML file and some other directories where all the parameters will be saved, but don't worry, you won't touch any of these files manually, since I made possible to configure termscp from its user interface entirely.
|
||||
|
||||
termscp, like for bookmarks, just requires to have these paths accessible:
|
||||
|
||||
- `$HOME/.config/termscp/` on Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` on MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` on Windows
|
||||
|
||||
To access configuration, you just have to press `<CTRL+C>` from the home of termscp.
|
||||
|
||||
These parameters can be changed:
|
||||
|
||||
- **Text Editor**: the text editor to use. By default termscp will find the default editor for you; with this option you can force an editor to be used (e.g. `vim`). **Also GUI editors are supported**, unless they `nohup` from the parent process so if you ask: yes, you can use `notepad.exe`, and no: **Visual Studio Code doesn't work**.
|
||||
- **Default Protocol**: the default protocol is the default value for the file transfer protocol to be used in termscp. This applies for the login page and for the address CLI argument.
|
||||
- **Show Hidden Files**: select whether hidden files shall be displayed by default. You will be able to decide whether to show or not hidden files at runtime pressing `A` anyway.
|
||||
- **Check for updates**: if set to `yes`, termscp will fetch the Github API to check if there is a new version of termscp available.
|
||||
- **Prompt when replacing existing files?**: If set to `yes`, termscp will prompt for confirmation you whenever a file transfer would cause an existing file on target host to be replaced.
|
||||
- **Group Dirs**: select whether directories should be groupped or not in file explorers. If `Display first` is selected, directories will be sorted using the configured method but displayed before files, viceversa if `Display last` is selected.
|
||||
- **Remote File formatter syntax**: syntax to display file info for each file in the remote explorer. See [File explorer format](#file-explorer-format)
|
||||
- **Local File formatter syntax**: syntax to display file info for each file in the local explorer. See [File explorer format](#file-explorer-format)
|
||||
- **Enable notifications?**: If set to `Yes`, notifications will be displayed.
|
||||
- **Notifications: minimum transfer size**: if transfer size is greater or equal than the specified value, notifications for transfer will be displayed. The accepted values are in format `{UNSIGNED} B/KB/MB/GB/TB/PB`
|
||||
- **SSH configuration path**: Set SSH configuration file to use when connecting to a SCP/SFTP server. If unset (empty) no file will be used. You can specify a path starting with `~` to indicate the home path (e.g. `~/.ssh/config`). The parameters supported by termscp are specified [HERE](https://github.com/veeso/ssh2-config#exposed-attributes).
|
||||
|
||||
### SSH Key Storage 🔐
|
||||
|
||||
Along with configuration, termscp provides also an **essential** feature for **SFTP/SCP clients**: the SSH key storage.
|
||||
|
||||
You can access the SSH key storage, from configuration moving to the `SSH Keys` tab, once there you can:
|
||||
|
||||
- **Add a new key**: just press `<CTRL+N>` and you will be prompted to create a new key. Provide the hostname/ip address and the username associated to the key and finally a text editor will open up: paste the **PRIVATE** ssh key into the text editor, save and quit.
|
||||
- **Remove an existing key**: just press `<DEL>` or `<CTRL+E>` on the key you want to remove, to delete persistently the key from termscp.
|
||||
- **Edit an existing key**: just press `<ENTER>` on the key you want to edit, to change the private key.
|
||||
|
||||
> Q: Wait, my private key is protected with password, can I use it?
|
||||
> A: Of course you can. The password provided for authentication in termscp, is valid both for username/password authentication and for RSA key authentication.
|
||||
|
||||
### File Explorer Format
|
||||
|
||||
It is possible through configuration to define a custom format for the file explorer. This is possible both for local and remote host, so you can have two different syntax in use. These fields, with name `File formatter syntax (local)` and `File formatter syntax (remote)` will define how the file entries will be displayed in the file explorer.
|
||||
The syntax for the formatter is the following `{KEY1}... {KEY2:LENGTH}... {KEY3:LENGTH:EXTRA} {KEYn}...`.
|
||||
Each key in bracket will be replaced with the related attribute, while everything outside brackets will be left unchanged.
|
||||
|
||||
- The key name is mandatory and must be one of the keys below
|
||||
- The length describes the length reserved to display the field. Static attributes doesn't support this (GROUP, PEX, SIZE, USER)
|
||||
- Extra is supported only by some parameters and is an additional options. See keys to check if extra is supported.
|
||||
|
||||
These are the keys supported by the formatter:
|
||||
|
||||
- `ATIME`: Last access time (with default syntax `%b %d %Y %H:%M`); Extra might be provided as the time syntax (e.g. `{ATIME:8:%H:%M}`)
|
||||
- `CTIME`: Creation time (with syntax `%b %d %Y %H:%M`); Extra might be provided as the time syntax (e.g. `{CTIME:8:%H:%M}`)
|
||||
- `GROUP`: Owner group
|
||||
- `MTIME`: Last change time (with syntax `%b %d %Y %H:%M`); Extra might be provided as the time syntax (e.g. `{MTIME:8:%H:%M}`)
|
||||
- `NAME`: File name (Elided if longer than LENGTH)
|
||||
- `PATH`: File absolute path (Elided if longer than LENGHT)
|
||||
- `PEX`: File permissions (UNIX format)
|
||||
- `SIZE`: File size (omitted for directories)
|
||||
- `SYMLINK`: Symlink (if any `-> {FILE_PATH}`)
|
||||
- `USER`: Owner user
|
||||
|
||||
If left empty, the default formatter syntax will be used: `{NAME:24} {PEX} {USER} {SIZE} {MTIME:17:%b %d %Y %H:%M}`
|
||||
|
||||
---
|
||||
|
||||
## Themes 🎨
|
||||
|
||||
Termscp provides you with an awesome feature: the possibility to set the colors for several components in the application.
|
||||
If you want to customize termscp there are two available ways to do so:
|
||||
|
||||
- From the **configuration menu**
|
||||
- Importing a **theme file**
|
||||
|
||||
In order to create your own customization from termscp, all you have to do so is to enter the configuration from the auth activity, pressing `<CTRL+C>` and then `<TAB>` twice. You should have now moved to the `themes` panel.
|
||||
|
||||
Here you can move with `<UP>` and `<DOWN>` to change the style you want to change, as shown in the gif below:
|
||||
|
||||
|
||||
|
||||
termscp supports both the traditional explicit hex (`#rrggbb`) and rgb `rgb(r, g, b)` syntax to provide colors, but also **[css colors](https://www.w3schools.com/cssref/css_colors.asp)** (such as `crimson`) are accepted 😉. There is also a special keywork which is `Default`. Default means that the color used will be the default foreground or background color based on the situation (foreground for texts and lines, background for well, guess what).
|
||||
|
||||
As said before, you can also import theme files. You can take inspiration from or directly use one of the themes provided along with termscp, located in the `themes/` directory of this repository and import them running termscp as `termscp -t <theme_file>`. If everything was fine, it should tell you the theme has successfully been imported.
|
||||
|
||||
### My theme won't load 😱
|
||||
|
||||
This is probably due to a recent update which has broken the theme. Whenever I add a new key to themes, the saved theme won't load. To fix this issues there are two really quick-fix solutions:
|
||||
|
||||
1. Reload theme: whenever I release an update I will also patch the "official" themes, so you just have to download it from the repository again and re-import the theme via `-t` option
|
||||
|
||||
```sh
|
||||
termscp -t <theme.toml>
|
||||
```
|
||||
|
||||
2. Fix your theme: If you're using a custom theme, then you can edit via `vim` and add the missing key. The theme is located at `$CONFIG_DIR/termscp/theme.toml` where `$CONFIG_DIR` is:
|
||||
|
||||
- FreeBSD/GNU-Linux: `$HOME/.config/`
|
||||
- MacOs: `$HOME/Library/Application Support`
|
||||
- Windows: `%appdata%`
|
||||
|
||||
❗ Missing keys are reported in the CHANGELOG under `BREAKING CHANGES` for the version you've just installed.
|
||||
|
||||
### Styles 💈
|
||||
|
||||
You can find in the table below, the description for each style field.
|
||||
Please, notice that **styles won't apply to configuration page**, in order to make it always accessible in case you mess everything up
|
||||
|
||||
#### Authentication page
|
||||
|
||||
| Key | Description |
|
||||
|----------------|------------------------------------------|
|
||||
| auth_address | Color of the input field for IP address |
|
||||
| auth_bookmarks | Color of the bookmarks panel |
|
||||
| auth_password | Color of the input field for password |
|
||||
| auth_port | Color of the input field for port number |
|
||||
| auth_protocol | Color of the radio group for protocol |
|
||||
| auth_recents | Color of the recents panel |
|
||||
| auth_username | Color of the input field for username |
|
||||
|
||||
#### Transfer page
|
||||
|
||||
| Key | Description |
|
||||
|--------------------------------------|---------------------------------------------------------------------------|
|
||||
| transfer_local_explorer_background | Background color of localhost explorer |
|
||||
| transfer_local_explorer_foreground | Foreground coloor of localhost explorer |
|
||||
| transfer_local_explorer_highlighted | Border and highlighted color for localhost explorer |
|
||||
| transfer_remote_explorer_background | Background color of remote explorer |
|
||||
| transfer_remote_explorer_foreground | Foreground coloor of remote explorer |
|
||||
| transfer_remote_explorer_highlighted | Border and highlighted color for remote explorer |
|
||||
| transfer_log_background | Background color for log panel |
|
||||
| transfer_log_window | Window color for log panel |
|
||||
| transfer_progress_bar_partial | Partial progress bar color |
|
||||
| transfer_progress_bar_total | Total progress bar color |
|
||||
| transfer_status_hidden | Color for status bar "hidden" label |
|
||||
| transfer_status_sorting | Color for status bar "sorting" label; applies also to file sorting dialog |
|
||||
| transfer_status_sync_browsing | Color for status bar "sync browsing" label |
|
||||
|
||||
#### Misc
|
||||
|
||||
These styles applie to different part of the application.
|
||||
|
||||
| Key | Description |
|
||||
|-------------------|---------------------------------------------|
|
||||
| misc_error_dialog | Color for error messages |
|
||||
| misc_info_dialog | Color for info dialogs |
|
||||
| misc_input_dialog | Color for input dialogs (such as copy file) |
|
||||
| misc_keys | Color of text for key strokes |
|
||||
| misc_quit_dialog | Color for quit dialogs |
|
||||
| misc_save_dialog | Color for save dialogs |
|
||||
| misc_warn_dialog | Color for warn dialogs |
|
||||
|
||||
---
|
||||
|
||||
## Text Editor ✏
|
||||
|
||||
termscp has, as you might have noticed, many features, one of these is the possibility to view and edit text file. It doesn't matter if the file is located on the local host or on the remote host, termscp provides the possibility to open a file in your favourite text editor.
|
||||
In case the file is located on remote host, the file will be first downloaded into your temporary file directory and then, **only** if changes were made to the file, re-uploaded to the remote host. termscp checks if you made changes to the file verifying the last modification time of the file.
|
||||
|
||||
Just a reminder: **you can edit only textual file**; binary files are not supported.
|
||||
|
||||
---
|
||||
|
||||
## Logging 🩺
|
||||
|
||||
termscp writes a log file for each session, which is written at
|
||||
|
||||
- `$HOME/.cache/termscp/termscp.log` on Linux/BSD
|
||||
- `$HOME/Library/Caches/termscp/termscp.log` on MacOs
|
||||
- `FOLDERID_LocalAppData\termscp\termscp.log` on Windows
|
||||
|
||||
the log won't be rotated, but will just be truncated after each launch of termscp, so if you want to report an issue and you want to attach your log file, keep in mind to save the log file in a safe place before using termscp again.
|
||||
The logging by default reports in *INFO* level, so it is not very verbose.
|
||||
|
||||
If you want to submit an issue, please, if you can, reproduce the issue with the level set to `TRACE`, to do so, launch termscp with
|
||||
the `-D` CLI option.
|
||||
|
||||
I know you might have some questions regarding log files, so I made a kind of a Q/A:
|
||||
|
||||
> I don't want logging, can I turn it off?
|
||||
|
||||
Yes, you can. Just start termscp with `-q or --quiet` option. You can alias termscp to make it persistent. Remember that logging is used to diagnose issues, so since behind every open source project, there should always be this kind of mutual help, keeping log files might be your way to support the project 😉. I don't want you to feel guilty, but just to say.
|
||||
|
||||
> Is logging safe?
|
||||
|
||||
If you're concerned about security, the log file doesn't contain any plain password, so don't worry and exposes the same information the sibling file `bookmarks` reports.
|
||||
|
||||
## Notifications 📫
|
||||
|
||||
Termscp will send Desktop notifications for these kind of events:
|
||||
|
||||
- on **Transfer completed**: The notification will be sent once a transfer has been successfully completed.
|
||||
- ❗ The notification will be displayed only if the transfer total size is at least the specified `Notifications: minimum transfer size` in the configuration.
|
||||
- on **Transfer failed**: The notification will be sent once a transfer has failed due to an error.
|
||||
- ❗ The notification will be displayed only if the transfer total size is at least the specified `Notifications: minimum transfer size` in the configuration.
|
||||
- on **Update available**: Whenever a new version of termscp is available, a notification will be displayed.
|
||||
- on **Update installed**: Whenever a new version of termscp has been installed, a notification will be displayed.
|
||||
- on **Update failed**: Whenever the installation of the update fails, a notification will be displayed.
|
||||
|
||||
❗ If you prefer to keep notifications turned off, you can just enter setup and set `Enable notifications?` to `No` 😉.
|
||||
❗ If you want to change the minimum transfer size to display notifications, you can change the value in the configuration with key `Notifications: minimum transfer size` and set it to whatever suits better for you 🙂.
|
||||
|
||||
## File watcher 🔭
|
||||
|
||||
The file watcher allows you to setup a list of paths to synchronize with the remote hosts.
|
||||
This means that whenever a change on the local file system will be detected on the synchronized path, the change will be automatically reported to the configured remote host path, within 5 seconds.
|
||||
|
||||
You can set as many paths to synchronize as you prefer:
|
||||
|
||||
1. Put the cursor on the local explorer on the directory/file you want to keep synchronized
|
||||
2. Go to the directory you want the changes to be reported to on the remote host
|
||||
3. Press `<T>`
|
||||
4. Answer `<YES>` to the radio popup
|
||||
|
||||
To unwatch, just press `<T>` on the local synchronized path (or to any of its subfolders)
|
||||
OR you can just press `<CTRL+T>` and press `<ENTER>` to the synchronized path you want to unwatch.
|
||||
|
||||
These changes will be reported to the remote host:
|
||||
|
||||
- New files, file changes
|
||||
- File moved/renamed
|
||||
- File removed/unlinked
|
||||
|
||||
> ❗ The watcher works only in one direction (local > remote). It is NOT possible to synchronize automatically the changes from remote to local.
|
||||
@@ -1,73 +0,0 @@
|
||||
# Developer Manual
|
||||
|
||||
Document audience: developers
|
||||
Revision: 2022-01-05
|
||||
|
||||
- [Developer Manual](#developer-manual)
|
||||
- [How termscp works](#how-termscp-works)
|
||||
- [Activities](#activities)
|
||||
- [The Context](#the-context)
|
||||
- [Achieving an abstract file transfer client](#achieving-an-abstract-file-transfer-client)
|
||||
|
||||
Welcome to the developer manual for termscp. This chapter DOESN'T contain the documentation for termscp modules, which can instead be found on Rust Docs at <https://docs.rs/termscp>
|
||||
This chapter describes how termscp works and the guide lines to implement stuff such as file transfers and add features to the user interface.
|
||||
|
||||
---
|
||||
|
||||
## How termscp works
|
||||
|
||||
termscp is basically made up of 3 core modules:
|
||||
|
||||
- the **host**: the host module provides functions to interact with the local host file system.
|
||||
- the **ui**: this module contains the implementation of the user interface, as we'll see in the next chapter, this is achieved through **activities**.
|
||||
- the **activity_manager**: the activity manager takes care of managing activities, basically it runs the activities of the user interface, and chooses, based on their state, when is the moment to terminate the current activity and which activity to run after the current one.
|
||||
|
||||
In addition to the 3 core modules, other have been added through the time:
|
||||
|
||||
- **config**: this module provides the configuration schema and serialization methods for it.
|
||||
- **explorer**: this modules exposes the explorer structures, which are used to handle the file explorer in the ui. So, basically they store the current directory model and the view states (e.g. sorting, whether to display hidden files, ...).
|
||||
- **system**: the system module provides a way to interact with the configuration, with the ssh key storage and with the bookmarks.
|
||||
- **utils**: contains the utilities used by pretty much all of the project.
|
||||
|
||||
## Activities
|
||||
|
||||
Just a little paragraph about activities. Really, read the code and the documentation to have a clear idea of how the ui works.
|
||||
I think there are many ways to implement a user interface and I've worked with different languages and frameworks in my career, so for this project I've decided to get what I like the most from different frameworks to implement it.
|
||||
|
||||
My approach was this:
|
||||
|
||||
- **Activities on top**: each "view" is an Activity and an `Activity Manager` handles them. I got inspired by Android for this case. I think that's a good way to implement the ui in case like this, where you have different views, each one with their view, their components and their logic. Activities work with the `Context`, which is a data holder to share data between the activities.
|
||||
- **Activities display Applications**: Each activity can show different **Applications**. An application, contains a **View** is basically a list of **components**, each one with its properties. The view is a facade to the components and also handles the focus, which is the current active component. You cannot have more than one component active, so you need to handle this; but at the same time you also have to give focus to the previously active component if the current one is destroyed. So basically **Application** takes care of all this stuff. If you're interested on how this works, you can read more on <https://github.com/veeso/tui-realm>.
|
||||
- **Components**: I've decided to write around `tui` in order to re-use widgets. To do so I've implemented the `Component` trait. To implement traits I got inspired by [React](https://reactjs.org/). Each component has its *Properties* and can have its *States*. Then each component must be able to handle input events and to be updated with new properties. Last but not least, each component must provide a method to **render** itself. At the beginning this was implemented inside of termscp, but now this has been moved to [tui-realm](https://github.com/veeso/tui-realm).
|
||||
- **Messages: an Elm based approach**: I was really satisfied with my implementation choices; the problem at this point was solving one of the biggest teardrops I've ever had with this project: **events**. Input events were really a pain to handle, since I had to handle states in the activity to handle which component was enabled etc. To solve this I got inspired by a wonderful language I had recently studied, which is [Elm](https://elm-lang.org/). Basically in Elm you implement your ui using three basic functions: **update**, **view** and **init**. View and init were pretty much already implemented here, but at this point I decided to implement also something like the **elm update function**. I came out with a huge match case to handle messages inside a recursive function, which you can basically find in the `update.rs` file inside each activity. This match case handles the messages produced by the components in front of an incoming input event. It matches the messages causing the activity to change its states *et voilà*.
|
||||
|
||||
I've implemented a Trait called `Activity`, which, is a very very reduced version of the Android activity of course.
|
||||
This trait provides only 3 methods:
|
||||
|
||||
- `on_create`: this method must initialize the activity; the context is passed to the activity, which will be the only owner of the Context, until the activity terminates.
|
||||
- `on_draw`: this method must be called each time you want to perform an update of the user interface. This is basically the run method of the activity. This method also cares about handling input events. The developer shouldn't draw the interface on each call of this method (consider that this method might be called hundreds of times per second), but only when actually something has changed (for example after an input event has been raised).
|
||||
- `will_umount`: this method was added in 0.4.0 and returns whethere the activity should be destroyed. If so returns an ExitReason, which indicates why the activity should be terminated. Based on the reason, the activity manager chooses whether to stop the execution of termscp or to start a new activity and which one.
|
||||
- `on_destroy`: this method finalizes the activity and drops it; this method returns the Context to the caller (the activity manager).
|
||||
|
||||
### The Context
|
||||
|
||||
The context is a structure which holds data which must be shared between activities. Everytime an Activity starts, the Context is taken by the activity, until it is destroyed, where finally the context is returned to the activity manager.
|
||||
The context basically holds the following data:
|
||||
|
||||
- The **Localhost**: the local host structure
|
||||
- The **File Transfer Params**: the current parameters set to connect to the remote
|
||||
- The **Config Client**: the configuration client is a structure which provides functions to access the user configuration
|
||||
- The **Store**: the store is a key-value storage which can hold any kind of data. This can be used to store states to share between activities or to keep persistence for heavy/slow tasks (such as checking for updates).
|
||||
- The **Terminal**: the terminal is used to view the tui on the terminal
|
||||
|
||||
---
|
||||
|
||||
## Achieving an abstract file transfer client
|
||||
|
||||
When I started to implement termscp, in december 2020, the file transfer was at the core of my implementation focus, since, for obvious reasons, it is at the heart of termscp.
|
||||
The first implementation consisted of a `filetransfer` module, which exposed a trait called `FileTransfer`, which exposed different methods to generically interact with the remote file system.
|
||||
This thing has changed over the last year, since different users has asked me to implement a dedicated library to implement this.
|
||||
So in the last quarter of 2021, I dedicated part of my time in implementing an abstract library to work with remote device file systems, and this is how [remotefs](https://github.com/veeso/remotefs-rs) was born.
|
||||
Remotefs provides a `RemoteFs` trait which exposes all of the core file-system functionalities and this has since 0.8.0 version, replaced the `FileTransfer` trait.
|
||||
|
||||
The file transfer module, still exists though, but its only task is to create a builder from the "file transfer parameters" into the `RemoteFs` client implementation.
|
||||
@@ -0,0 +1,37 @@
|
||||
# Summary
|
||||
|
||||
[Introduction](index.md)
|
||||
|
||||
# Getting started
|
||||
|
||||
- [Installation](getting-started/installation.md)
|
||||
- [Connecting to a server](getting-started/connecting.md)
|
||||
- [Connection parameters](getting-started/connection-parameters.md)
|
||||
|
||||
# Using termscp
|
||||
|
||||
- [The file explorer](usage/file-explorer.md)
|
||||
- [Keyboard shortcuts](usage/keyboard-shortcuts.md)
|
||||
- [Working with multiple files](usage/multiple-files.md)
|
||||
- [Synchronized browsing](usage/synced-browsing.md)
|
||||
- [Opening and editing files](usage/open-edit-files.md)
|
||||
- [Bookmarks and recent hosts](usage/bookmarks.md)
|
||||
- [Keeping files in sync](usage/file-watcher.md)
|
||||
|
||||
# Configuration
|
||||
|
||||
- [Configuration](configuration/configuration.md)
|
||||
- [File explorer format](configuration/explorer-format.md)
|
||||
- [SSH key storage](configuration/ssh-keys.md)
|
||||
- [Themes](configuration/themes.md)
|
||||
- [Notifications](configuration/notifications.md)
|
||||
- [Logging](configuration/logging.md)
|
||||
- [Password security](configuration/password-security.md)
|
||||
|
||||
# CLI reference
|
||||
|
||||
- [Command-line usage](cli/cli.md)
|
||||
|
||||
# Developer
|
||||
|
||||
- [Developer manual](developer/developer.md)
|
||||
@@ -0,0 +1,22 @@
|
||||
[book]
|
||||
title = "termscp"
|
||||
description = "A feature rich terminal UI file transfer and explorer with support for SCP/SFTP/FTP/Kube/S3/SMB/WebDAV"
|
||||
authors = ["Christian Visintin"]
|
||||
language = "en"
|
||||
src = "."
|
||||
|
||||
[output.html]
|
||||
default-theme = "light"
|
||||
preferred-dark-theme = "navy"
|
||||
git-repository-url = "https://github.com/veeso/termscp"
|
||||
edit-url-template = "https://github.com/veeso/termscp/edit/main/docs/en-US/{path}"
|
||||
additional-js = ["lang-switcher.js", "mermaid.min.js", "mermaid-init.js"]
|
||||
|
||||
[output.html.fold]
|
||||
enable = true
|
||||
level = 1
|
||||
|
||||
[preprocessor]
|
||||
|
||||
[preprocessor.mermaid]
|
||||
command = "mdbook-mermaid"
|
||||
@@ -0,0 +1,76 @@
|
||||
# Command-line usage
|
||||
|
||||
termscp can be started with the following invocation forms:
|
||||
|
||||
```sh
|
||||
termscp [options]... [protocol://user@address:port:wrkdir] [protocol://user@address:port:wrkdir] [local-wrkdir]
|
||||
```
|
||||
|
||||
OR
|
||||
|
||||
```sh
|
||||
termscp [options]... -b [bookmark-name] -b [bookmark-name] [local-wrkdir]
|
||||
```
|
||||
|
||||
AND any combination of the two.
|
||||
|
||||
If no extra arguments are provided, termscp shows the authentication form. If an
|
||||
address argument or a bookmark name is provided, termscp skips the form and
|
||||
connects directly to the remote server. When an address or bookmark is given,
|
||||
you may also provide the starting working directory for the local host as the
|
||||
last positional argument.
|
||||
|
||||
## Options
|
||||
|
||||
| Key | Description |
|
||||
| -------------------- | --------------------------------------------------------------------------------------------------------------------------------- |
|
||||
| `-b <bookmark-name>` | Resolve the positional address argument as a bookmark name. Repeat the flag to open multiple bookmarks. |
|
||||
| `-D` | Enable the `TRACE` log level (debug/verbose logging). |
|
||||
| `-P <password>` | Provide the password from the CLI. Repeat the flag for multiple remotes; the order must match the address arguments. Discouraged. |
|
||||
| `-q` | Disable logging. |
|
||||
| `-T <ticks>` | Set the UI tick interval in milliseconds. Default is `10`. |
|
||||
| `--wno-keyring` | Disable system keyring support. |
|
||||
| `-v` | Print version info. |
|
||||
| `--help` | Print the help page. |
|
||||
|
||||
The `-P` option is discouraged because the password may be kept in the shell
|
||||
history. See the bookmarks and password-security chapters for safer ways to
|
||||
provide credentials.
|
||||
|
||||
## Subcommands
|
||||
|
||||
termscp exposes the following subcommands.
|
||||
|
||||
### Import a theme
|
||||
|
||||
```sh
|
||||
termscp theme <theme-file>
|
||||
```
|
||||
|
||||
Import the theme defined in `<theme-file>`.
|
||||
|
||||
### Install the latest version
|
||||
|
||||
```sh
|
||||
termscp update
|
||||
```
|
||||
|
||||
Download and install the latest available version of termscp.
|
||||
|
||||
### Import ssh hosts
|
||||
|
||||
```sh
|
||||
termscp import-ssh-hosts [ssh-config-file]
|
||||
```
|
||||
|
||||
Import all the hosts from the specified ssh config file as bookmarks in
|
||||
termscp. If `[ssh-config-file]` is not provided, the default location
|
||||
`~/.ssh/config` is used. Identity files are imported as ssh keys in termscp too.
|
||||
|
||||
### Open configuration
|
||||
|
||||
```sh
|
||||
termscp config
|
||||
```
|
||||
|
||||
Start termscp directly in the configuration (setup) screen.
|
||||
@@ -0,0 +1,50 @@
|
||||
# Configuration
|
||||
|
||||
termscp supports a number of user-defined parameters. termscp stores them in a
|
||||
TOML file and a few directories, but you never edit these files by hand:
|
||||
configuration is done entirely from the user interface.
|
||||
|
||||
To enter the configuration, press `<CTRL+C>` from the termscp home.
|
||||
|
||||
termscp requires these paths to be accessible:
|
||||
|
||||
- `$HOME/.config/termscp/` on Linux/BSD
|
||||
- `$HOME/.config/termscp/` on macOS
|
||||
- `%USERPROFILE%\.termscp\` on Windows
|
||||
|
||||
## Parameters
|
||||
|
||||
The following parameters can be configured:
|
||||
|
||||
- **Text Editor**: the text editor to use. By default termscp finds the default
|
||||
editor for you; with this option you can force an editor to be used (e.g.
|
||||
`vim`). GUI editors are also supported, unless they detach (`nohup`) from the
|
||||
parent process.
|
||||
- **Default Protocol**: the default value for the file transfer protocol to be
|
||||
used in termscp. It applies to the login page and to the address CLI argument.
|
||||
- **Show Hidden Files**: whether hidden files are displayed by default. You can
|
||||
also toggle hidden files at runtime by pressing `A`.
|
||||
- **Check for updates**: if set to `yes`, termscp queries the GitHub API to
|
||||
check whether a new version of termscp is available.
|
||||
- **Prompt when replacing existing files**: if set to `yes`, termscp prompts for
|
||||
confirmation whenever a file transfer would replace an existing file on the
|
||||
target host.
|
||||
- **Group Dirs**: whether directories are grouped in the file explorers. If
|
||||
`Display first` is selected, directories are sorted with the configured method
|
||||
but displayed before files; with `Display last` they are displayed after
|
||||
files.
|
||||
- **Remote file formatter syntax**: syntax used to display file info for each
|
||||
file in the remote explorer. See [File explorer format](explorer-format.md).
|
||||
- **Local file formatter syntax**: syntax used to display file info for each file
|
||||
in the local explorer. See [File explorer format](explorer-format.md).
|
||||
- **Enable notifications**: if set to `Yes`, desktop notifications are displayed.
|
||||
See [Notifications](notifications.md).
|
||||
- **Notifications: minimum transfer size**: if the transfer size is greater than
|
||||
or equal to the specified value, transfer notifications are displayed. The
|
||||
accepted format is `{UNSIGNED} B/KB/MB/GB/TB/PB`.
|
||||
- **SSH configuration path**: SSH configuration file to use when connecting to a
|
||||
SCP/SFTP server. If left empty, no file is used. You can specify a path
|
||||
starting with `~` to indicate the home directory (e.g. `~/.ssh/config`). The
|
||||
attributes supported by termscp are listed at
|
||||
[the ssh2-config exposed attributes](https://github.com/veeso/ssh2-config#exposed-attributes).
|
||||
See also [SSH key storage](ssh-keys.md).
|
||||
@@ -0,0 +1,49 @@
|
||||
# File explorer format
|
||||
|
||||
You can define a custom format for the file explorer through the configuration.
|
||||
This is possible for both the local and the remote host, so you can use two
|
||||
different syntaxes. The fields are named **File formatter syntax (local)** and
|
||||
**File formatter syntax (remote)**, and they define how the file entries are
|
||||
displayed in the file explorer.
|
||||
|
||||
## Syntax
|
||||
|
||||
The syntax for the formatter is the following:
|
||||
|
||||
```text
|
||||
{KEY1}... {KEY2:LENGTH}... {KEY3:LENGTH:EXTRA} {KEYn}...
|
||||
```
|
||||
|
||||
Each key in braces is replaced with the related attribute, while everything
|
||||
outside braces is left unchanged.
|
||||
|
||||
- The key name is mandatory and must be one of the keys below.
|
||||
- `LENGTH` describes the width reserved to display the field. Static attributes
|
||||
do not support it (`GROUP`, `PEX`, `SIZE`, `USER`).
|
||||
- `EXTRA` is supported only by some keys and provides an additional option. See
|
||||
the keys below to check whether `EXTRA` is supported.
|
||||
|
||||
## Keys
|
||||
|
||||
These are the keys supported by the formatter:
|
||||
|
||||
| Key | Description |
|
||||
| --------- | ------------------------------------------------------------------------------------------------ |
|
||||
| `ATIME` | Last access time (default `%b %d %Y %H:%M`); `EXTRA` is the time format (e.g. `{ATIME:8:%H:%M}`) |
|
||||
| `CTIME` | Creation time (default `%b %d %Y %H:%M`); `EXTRA` is the time format (e.g. `{CTIME:8:%H:%M}`) |
|
||||
| `GROUP` | Owner group |
|
||||
| `MTIME` | Last change time (default `%b %d %Y %H:%M`); `EXTRA` is the time format (e.g. `{MTIME:8:%H:%M}`) |
|
||||
| `NAME` | File name (folders between root and first ancestors are elided if longer than `LENGTH`) |
|
||||
| `PATH` | File absolute path (folders between root and first ancestors are elided if longer than `LENGTH`) |
|
||||
| `PEX` | File permissions (UNIX format) |
|
||||
| `SIZE` | File size (omitted for directories) |
|
||||
| `SYMLINK` | Symlink target (if any, `-> {FILE_PATH}`) |
|
||||
| `USER` | Owner user |
|
||||
|
||||
## Default format
|
||||
|
||||
If left empty, the default formatter syntax is used:
|
||||
|
||||
```text
|
||||
{NAME:24} {PEX} {USER} {SIZE} {MTIME:17:%b %d %Y %H:%M}
|
||||
```
|
||||
@@ -0,0 +1,28 @@
|
||||
# Logging
|
||||
|
||||
termscp writes a log file for each session, located at:
|
||||
|
||||
- `$HOME/.cache/termscp/termscp.log` on Linux/BSD
|
||||
- `$HOME/Library/Caches/termscp/termscp.log` on macOS
|
||||
- `FOLDERID_LocalAppData\termscp\termscp.log` on Windows
|
||||
|
||||
The log is not rotated: it is truncated on each launch of termscp. If you want
|
||||
to report an issue and attach the log file, save the log somewhere safe before
|
||||
launching termscp again.
|
||||
|
||||
By default the log reports at the `INFO` level, so it is not very verbose.
|
||||
|
||||
## Reproducing an issue at TRACE level
|
||||
|
||||
To submit an issue, reproduce the problem with the log level set to `TRACE` by
|
||||
launching termscp with the `-D` CLI option.
|
||||
|
||||
## Disabling logging
|
||||
|
||||
To turn logging off, start termscp with the `-q` or `--quiet` option. You can
|
||||
alias termscp to make it persistent.
|
||||
|
||||
## Security
|
||||
|
||||
The log file does not contain any plaintext password. It exposes the same
|
||||
information as the sibling `bookmarks` file.
|
||||
@@ -0,0 +1,23 @@
|
||||
# Notifications
|
||||
|
||||
termscp sends desktop notifications for the following events:
|
||||
|
||||
- **Transfer completed**: sent once a transfer has been successfully completed.
|
||||
Displayed only if the total transfer size is at least the configured
|
||||
`Notifications: minimum transfer size`.
|
||||
- **Transfer failed**: sent once a transfer has failed due to an error.
|
||||
Displayed only if the total transfer size is at least the configured
|
||||
`Notifications: minimum transfer size`.
|
||||
- **Update available**: sent whenever a new version of termscp is available.
|
||||
- **Update installed**: sent whenever a new version of termscp has been
|
||||
installed.
|
||||
- **Update failed**: sent whenever the installation of an update fails.
|
||||
|
||||
## Disable notifications
|
||||
|
||||
To turn notifications off, enter setup and set `Enable notifications?` to `No`.
|
||||
|
||||
## Change the minimum transfer size
|
||||
|
||||
To change the threshold that gates transfer notifications, enter setup and set
|
||||
`Notifications: minimum transfer size` to the value that suits you.
|
||||
@@ -0,0 +1,49 @@
|
||||
# Password security
|
||||
|
||||
Bookmarks are saved in your configuration directory along with their passwords.
|
||||
Passwords are not stored in plaintext: they are encrypted with AES.
|
||||
|
||||
The key used to encrypt passwords is stored, where possible, in the operating
|
||||
system secret store:
|
||||
|
||||
- The Windows Vault on Windows
|
||||
- The system keyring on Linux
|
||||
- The Keychain on macOS
|
||||
|
||||
This is managed directly by your operating system.
|
||||
|
||||
On BSD and WSL there is no such secret store, so the encryption key is saved on
|
||||
disk at `$HOME/.config/termscp`. The location protects the key with file
|
||||
permissions so that it cannot be read by other users, but you should still avoid
|
||||
saving passwords for servers exposed on the internet on these systems.
|
||||
|
||||
## Linux keyring
|
||||
|
||||
On Linux there might be no keyring installed on your system. The key storage
|
||||
requires a service that exposes `org.freedesktop.secrets` on D-Bus, and only a
|
||||
few services provide it:
|
||||
|
||||
- If you use GNOME as your desktop environment (e.g. Ubuntu users), the keyring
|
||||
is already provided by `gnome-keyring` and everything should work out of the
|
||||
box.
|
||||
- For other desktop environments, you can use [KeepassXC](https://keepassxc.org/)
|
||||
to obtain a keyring. It must be set up to work with termscp; see
|
||||
[KeepassXC setup](#keepassxc-setup) below.
|
||||
- If you do not want to install any of these services, termscp keeps working as
|
||||
usual and falls back to saving the key in a file, as it does for BSD and WSL.
|
||||
|
||||
### KeepassXC setup
|
||||
|
||||
Follow these steps to set up KeepassXC for termscp:
|
||||
|
||||
1. Install KeepassXC.
|
||||
2. Go to "Tools" > "Settings" in the toolbar.
|
||||
3. Select "Secret service integration" and enable "Enable KeepassXC
|
||||
freedesktop.org secret service integration".
|
||||
4. Create a database, if you do not have one yet: from the toolbar, "Database" >
|
||||
"New database".
|
||||
5. From the toolbar, go to "Database" > "Database settings".
|
||||
6. Select "Secret service integration" and enable "Expose entries under this
|
||||
group".
|
||||
7. Select the group where the termscp secret will be kept. Note that any other
|
||||
application can read secrets exposed via D-Bus for that group.
|
||||
@@ -0,0 +1,25 @@
|
||||
# SSH key storage
|
||||
|
||||
Along with configuration, termscp provides an essential feature for SFTP/SCP
|
||||
clients: the SSH key storage.
|
||||
|
||||
To access the SSH key storage, enter the configuration and move to the
|
||||
`SSH Keys` tab.
|
||||
|
||||
## Manage keys
|
||||
|
||||
From the `SSH Keys` tab you can:
|
||||
|
||||
- **Add a new key**: press `<CTRL+N>`. You are prompted to provide the
|
||||
hostname/IP address and the username associated with the key, then a text
|
||||
editor opens: paste the **private** SSH key into the editor, save and quit.
|
||||
- **Remove an existing key**: press `<DEL>` or `<CTRL+E>` on the key you want to
|
||||
remove to delete it persistently from termscp.
|
||||
- **Edit an existing key**: press `<ENTER>` on the key you want to edit to change
|
||||
the private key.
|
||||
|
||||
## Password-protected keys
|
||||
|
||||
Password-protected private keys are supported. The password you provide for
|
||||
authentication in termscp is valid both for username/password authentication and
|
||||
for key authentication.
|
||||
@@ -0,0 +1,113 @@
|
||||
# Themes
|
||||
|
||||
termscp lets you set the colors for several components in the application. There
|
||||
are two ways to customize termscp:
|
||||
|
||||
- From the **configuration menu**
|
||||
- Importing a **theme file**
|
||||
|
||||
## Customize from the configuration menu
|
||||
|
||||
To customize termscp from the configuration menu, enter the configuration from
|
||||
the auth screen by pressing `<CTRL+C>`, then press `<TAB>` twice to reach the
|
||||
`themes` panel. Move with `<UP>` and `<DOWN>` to select the style you want to
|
||||
change, as shown in the gif below:
|
||||
|
||||

|
||||
|
||||
## Import a theme file
|
||||
|
||||
You can also import theme files. You can take inspiration from, or directly use,
|
||||
one of the themes bundled with termscp in the `themes/` directory of the
|
||||
repository. Import a theme by running:
|
||||
|
||||
```sh
|
||||
termscp theme <theme_file>
|
||||
```
|
||||
|
||||
If everything is fine, termscp confirms the theme has been imported.
|
||||
|
||||
## Color syntax
|
||||
|
||||
termscp accepts the following color formats:
|
||||
|
||||
- Explicit hexadecimal: `#rrggbb`
|
||||
- RGB: `rgb(r, g, b)`
|
||||
- [CSS color names](https://www.w3schools.com/cssref/css_colors.asp) (such as
|
||||
`crimson`)
|
||||
- The special keyword `Default`, which uses the situational default foreground
|
||||
or background color (foreground for texts and lines, background otherwise)
|
||||
|
||||
## Recovering from a theme that won't load
|
||||
|
||||
After an update, a saved theme can fail to load. This happens when a new key is
|
||||
added to themes: the previously saved theme no longer contains that key. There
|
||||
are two quick fixes:
|
||||
|
||||
1. Re-import the official theme. After each release the official themes are
|
||||
patched, so download the updated theme from the repository and re-import it:
|
||||
|
||||
```sh
|
||||
termscp theme <theme.toml>
|
||||
```
|
||||
|
||||
2. Edit your theme by hand. If you use a custom theme, edit the file and add the
|
||||
missing key. The theme is located at `$CONFIG_DIR/theme.toml`, where
|
||||
`$CONFIG_DIR` is:
|
||||
|
||||
- FreeBSD/Linux: `$HOME/.config/termscp`
|
||||
- macOS: `$HOME/.config/termscp`
|
||||
- Windows: `%USERPROFILE%\.termscp`
|
||||
|
||||
Missing keys are reported in the CHANGELOG under `BREAKING CHANGES` for the
|
||||
version you have just installed.
|
||||
|
||||
## Styles
|
||||
|
||||
The tables below describe each style field. Note that styles do **not** apply to
|
||||
the configuration page, so it always remains usable in case you change something
|
||||
by mistake.
|
||||
|
||||
### Authentication page
|
||||
|
||||
| Key | Description |
|
||||
| ---------------- | ---------------------------------------- |
|
||||
| `auth_address` | Color of the input field for IP address |
|
||||
| `auth_bookmarks` | Color of the bookmarks panel |
|
||||
| `auth_password` | Color of the input field for password |
|
||||
| `auth_port` | Color of the input field for port number |
|
||||
| `auth_protocol` | Color of the radio group for protocol |
|
||||
| `auth_recents` | Color of the recents panel |
|
||||
| `auth_username` | Color of the input field for username |
|
||||
|
||||
### Transfer page
|
||||
|
||||
| Key | Description |
|
||||
| -------------------------------------- | ------------------------------------------------------------------------- |
|
||||
| `transfer_local_explorer_background` | Background color of localhost explorer |
|
||||
| `transfer_local_explorer_foreground` | Foreground color of localhost explorer |
|
||||
| `transfer_local_explorer_highlighted` | Border and highlighted color for localhost explorer |
|
||||
| `transfer_remote_explorer_background` | Background color of remote explorer |
|
||||
| `transfer_remote_explorer_foreground` | Foreground color of remote explorer |
|
||||
| `transfer_remote_explorer_highlighted` | Border and highlighted color for remote explorer |
|
||||
| `transfer_log_background` | Background color for log panel |
|
||||
| `transfer_log_window` | Window color for log panel |
|
||||
| `transfer_progress_bar_partial` | Partial progress bar color |
|
||||
| `transfer_progress_bar_total` | Total progress bar color |
|
||||
| `transfer_status_hidden` | Color for status bar "hidden" label |
|
||||
| `transfer_status_sorting` | Color for status bar "sorting" label; applies also to file sorting dialog |
|
||||
| `transfer_status_sync_browsing` | Color for status bar "sync browsing" label |
|
||||
|
||||
### Misc
|
||||
|
||||
These styles apply to different parts of the application.
|
||||
|
||||
| Key | Description |
|
||||
| ------------------- | ------------------------------------------- |
|
||||
| `misc_error_dialog` | Color for error messages |
|
||||
| `misc_info_dialog` | Color for info dialogs |
|
||||
| `misc_input_dialog` | Color for input dialogs (such as copy file) |
|
||||
| `misc_keys` | Color of text for key strokes |
|
||||
| `misc_quit_dialog` | Color for quit dialogs |
|
||||
| `misc_save_dialog` | Color for save dialogs |
|
||||
| `misc_warn_dialog` | Color for warn dialogs |
|
||||
@@ -0,0 +1,128 @@
|
||||
# Developer manual
|
||||
|
||||
Welcome to the developer manual for termscp. This chapter does NOT contain the
|
||||
documentation for termscp modules, which can instead be found on Rust Docs at
|
||||
<https://docs.rs/termscp>. This chapter describes how termscp works and the
|
||||
guidelines to implement features such as file transfers and additions to the
|
||||
user interface.
|
||||
|
||||
termscp is written in Rust (edition 2024, MSRV 1.89.0). The user interface is
|
||||
built with [tuirealm](https://github.com/veeso/tui-realm) v3, which runs on top
|
||||
of [crossterm](https://github.com/crossterm-rs/crossterm).
|
||||
|
||||
## How termscp works
|
||||
|
||||
termscp is basically made up of 3 core modules:
|
||||
|
||||
- The **host**: the host module provides functions to interact with file
|
||||
systems. It exposes the `HostBridge` trait, which abstracts file operations
|
||||
over both the local host (`Localhost`) and the remote host (`RemoteBridged`).
|
||||
- The **ui**: this module contains the implementation of the user interface. As
|
||||
shown in the next chapter, this is achieved through **activities**.
|
||||
- The **activity_manager**: the activity manager takes care of managing
|
||||
activities. It runs the activities of the user interface and chooses, based on
|
||||
their state, when to terminate the current activity and which activity to run
|
||||
next.
|
||||
|
||||
In addition to the 3 core modules, others have been added over time:
|
||||
|
||||
- **config**: provides the configuration schema and its serialization methods.
|
||||
- **explorer**: exposes the explorer structures, which are used to handle the
|
||||
file explorer in the ui. They store the current directory model and the view
|
||||
states (e.g. sorting, whether to display hidden files, the transfer queue).
|
||||
- **filetransfer**: defines the `FileTransferProtocol` enum and the
|
||||
`RemoteFsBuilder`, which constructs the appropriate `RemoteFs` client from the
|
||||
connection parameters.
|
||||
- **system**: provides a way to interact with the configuration, the ssh key
|
||||
storage and the bookmarks.
|
||||
- **utils**: contains the utilities used by pretty much all of the project.
|
||||
|
||||
termscp supports the following protocols: SFTP, SCP, FTP/FTPS, Kube, S3, SMB and
|
||||
WebDAV.
|
||||
|
||||
## Activities
|
||||
|
||||
This paragraph gives a short overview of activities. Read the code and the
|
||||
documentation for a clear idea of how the ui works.
|
||||
|
||||
There are many ways to implement a user interface. This project borrows what
|
||||
works best from different frameworks:
|
||||
|
||||
- **Activities on top**: each "view" is an Activity, and an `Activity Manager`
|
||||
handles them. This approach is inspired by Android. It fits a ui that has
|
||||
different views, each one with its own components and logic. Activities work
|
||||
with the `Context`, which is a data holder used to share data between
|
||||
activities.
|
||||
- **Activities display Applications**: each activity can show different
|
||||
**Applications**. An application contains a **View**, which is basically a list
|
||||
of **components**, each one with its properties. The view is a facade to the
|
||||
components and also handles the focus, which is the current active component.
|
||||
You cannot have more than one active component, so this must be handled; at the
|
||||
same time, focus must be given back to the previously active component if the
|
||||
current one is destroyed. The **Application** takes care of all this. To learn
|
||||
more, read <https://github.com/veeso/tui-realm>.
|
||||
- **Components**: components are built around tui in order to reuse widgets. This
|
||||
is achieved through the `Component` trait, inspired by
|
||||
[React](https://reactjs.org/). Each component has its *Properties* and can have
|
||||
its *States*. Each component must handle input events, accept new properties,
|
||||
and provide a method to **render** itself. This logic now lives in
|
||||
[tui-realm](https://github.com/veeso/tui-realm).
|
||||
- **Messages: an Elm-based approach**: input events are handled with an approach
|
||||
inspired by [Elm](https://elm-lang.org/). In Elm you implement your ui using
|
||||
three basic functions: **update**, **view** and **init**. termscp implements
|
||||
the equivalent of the Elm update function as a large match case inside a
|
||||
recursive function, which you can find in the `update.rs` file inside each
|
||||
activity. This match case handles the messages produced by the components in
|
||||
response to incoming input events and causes the activity to change its state.
|
||||
|
||||
termscp implements a trait called `Activity`, a much reduced version of the
|
||||
Android activity. This trait provides these methods:
|
||||
|
||||
- `on_create`: initializes the activity. The context is passed to the activity,
|
||||
which becomes the only owner of the Context until the activity terminates.
|
||||
- `on_draw`: called each time the user interface should be updated. This is
|
||||
basically the run method of the activity, and it also handles input events. The
|
||||
interface should not be drawn on every call (this method may be called hundreds
|
||||
of times per second), but only when something has actually changed (for example
|
||||
after an input event).
|
||||
- `will_umount`: returns whether the activity should be destroyed. If so, it
|
||||
returns an `ExitReason`, which indicates why the activity should terminate.
|
||||
Based on the reason, the activity manager chooses whether to stop the execution
|
||||
of termscp or to start a new activity, and which one.
|
||||
- `on_destroy`: finalizes the activity and drops it. This method returns the
|
||||
Context to the caller (the activity manager).
|
||||
|
||||
### The Context
|
||||
|
||||
The context is a structure that holds data shared between activities. Every time
|
||||
an Activity starts, the Context is taken by the activity, until it is destroyed,
|
||||
where the context is finally returned to the activity manager. The context holds
|
||||
the following data:
|
||||
|
||||
- The **Localhost**: the local host structure.
|
||||
- The **File Transfer Params**: the current parameters used to connect to the
|
||||
remote.
|
||||
- The **Config Client**: a structure that provides functions to access the user
|
||||
configuration.
|
||||
- The **Store**: a key-value storage that can hold any kind of data. It can be
|
||||
used to share state between activities or to keep persistence for heavy or slow
|
||||
tasks (such as checking for updates).
|
||||
- The **Terminal**: used to render the tui on the terminal.
|
||||
|
||||
## Achieving an abstract file transfer client
|
||||
|
||||
When the implementation of termscp started, in December 2020, file transfer was
|
||||
at the core of the design, since it is at the heart of termscp. The first
|
||||
implementation consisted of a `filetransfer` module that exposed a trait called
|
||||
`FileTransfer`, which provided methods to generically interact with the remote
|
||||
file system.
|
||||
|
||||
This changed over time, as different users asked for a dedicated library. In the
|
||||
last quarter of 2021, [remotefs](https://github.com/veeso/remotefs-rs) was born:
|
||||
an abstract library to work with remote device file systems. remotefs provides a
|
||||
`RemoteFs` trait that exposes all of the core file-system functionalities, and
|
||||
since version 0.8.0 it has replaced the `FileTransfer` trait.
|
||||
|
||||
The file transfer module still exists, but its only task is to build a
|
||||
`RemoteFs` client implementation from the file transfer parameters through the
|
||||
`RemoteFsBuilder`.
|
||||
@@ -0,0 +1,77 @@
|
||||
# Connecting to a server
|
||||
|
||||
termscp can start in three different ways depending on the arguments you pass.
|
||||
|
||||
- No arguments: termscp opens the authentication form, where you provide the
|
||||
parameters required to connect to the remote host.
|
||||
- An address argument: termscp skips the authentication form and connects
|
||||
directly to the remote host.
|
||||
- A bookmark name with `-b <bookmark-name>`: termscp resolves the argument as a
|
||||
saved bookmark and connects. Repeat `-b` to open several bookmarks.
|
||||
|
||||
When you provide an address argument or a bookmark name, you can also provide a
|
||||
start working directory for the local host.
|
||||
|
||||
## The authentication form
|
||||
|
||||
When termscp starts without an address, it shows the authentication form. Fill
|
||||
in the protocol, address, port, username, and password, then connect. termscp
|
||||
will open the dual-pane explorer once the connection succeeds.
|
||||
|
||||
## Address argument syntax
|
||||
|
||||
The generic address argument has the following syntax:
|
||||
|
||||
```txt
|
||||
[protocol://][username@]<address>[:port][:wrkdir]
|
||||
```
|
||||
|
||||
This syntax is convenient, and you will probably use it instead of the
|
||||
interactive form. Here are some examples.
|
||||
|
||||
Connect using the default protocol (defined in your configuration) to
|
||||
`192.168.1.31`. If the port is not provided, the default port for the selected
|
||||
protocol is used. The username is the current user's name.
|
||||
|
||||
```sh
|
||||
termscp 192.168.1.31
|
||||
```
|
||||
|
||||
Connect using the default protocol to `192.168.1.31` as user `root`:
|
||||
|
||||
```sh
|
||||
termscp root@192.168.1.31
|
||||
```
|
||||
|
||||
Connect using SCP to `192.168.1.31` on port `4022` as user `omar`:
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022
|
||||
```
|
||||
|
||||
Connect using SCP to `192.168.1.31` on port `4022` as user `omar`, starting in
|
||||
directory `/tmp`:
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022:/tmp
|
||||
```
|
||||
|
||||
For protocol-specific address syntax (S3, Kube, WebDAV, and SMB), see
|
||||
[Connection parameters](connection-parameters.md).
|
||||
|
||||
## How the password is provided
|
||||
|
||||
When you provide the address as an argument, there is no field for the password
|
||||
in the address itself. You can provide the password in three ways:
|
||||
|
||||
- You will be prompted for it. This is the default: if you don't use any of the
|
||||
methods below, termscp prompts for the password, like classic tools such as
|
||||
`scp` and `ssh`.
|
||||
- `-P, --password` option: pass the password directly on the command line. This
|
||||
method is discouraged because it is insecure: the password may be kept in
|
||||
your shell history.
|
||||
- Via `sshpass`: provide the password through `sshpass`, for example:
|
||||
|
||||
```sh
|
||||
sshpass -f ~/.ssh/topsecret.key termscp cvisintin@192.168.1.31
|
||||
```
|
||||
@@ -0,0 +1,168 @@
|
||||
# Connection parameters
|
||||
|
||||
Each protocol has its own set of authentication-form fields and its own
|
||||
command-line address syntax. This page describes them protocol by protocol.
|
||||
|
||||
## SFTP / SCP
|
||||
|
||||
Authentication-form fields:
|
||||
|
||||
- Host (address)
|
||||
- Port (default `22`)
|
||||
- Username
|
||||
- Password or SSH key
|
||||
|
||||
You can authenticate either with a username and password or with an SSH key.
|
||||
See [SSH key storage](../configuration/ssh-keys.md) for how to manage keys.
|
||||
|
||||
Address syntax:
|
||||
|
||||
```txt
|
||||
[protocol://][username@]<address>[:port][:wrkdir]
|
||||
```
|
||||
|
||||
## FTP / FTPS
|
||||
|
||||
Authentication-form fields:
|
||||
|
||||
- Host (address)
|
||||
- Port (default `21`)
|
||||
- Username
|
||||
- Password
|
||||
- Secure (FTPS): enable TLS to use FTPS instead of plain FTP
|
||||
|
||||
Address syntax:
|
||||
|
||||
```txt
|
||||
[protocol://][username@]<address>[:port][:wrkdir]
|
||||
```
|
||||
|
||||
## Kube
|
||||
|
||||
Authentication-form fields:
|
||||
|
||||
- Namespace
|
||||
- Cluster URL (Kubernetes API URL)
|
||||
- Username
|
||||
- Client certificate path
|
||||
- Client key path
|
||||
|
||||
Address syntax:
|
||||
|
||||
```txt
|
||||
kube://[namespace][@<cluster_url>][$</path>]
|
||||
```
|
||||
|
||||
## S3
|
||||
|
||||
termscp supports both AWS S3 and other S3-compatible endpoints.
|
||||
|
||||
Authentication-form fields:
|
||||
|
||||
- Bucket name
|
||||
- Region (for AWS S3) or endpoint (for other S3-compatible servers)
|
||||
- Profile
|
||||
- Access key
|
||||
- Secret access key
|
||||
- Security token
|
||||
- Session token
|
||||
- New path style
|
||||
|
||||
The required and optional fields differ depending on the endpoint:
|
||||
|
||||
- AWS S3:
|
||||
- bucket name (required)
|
||||
- region (required)
|
||||
- profile (optional; defaults to `default`)
|
||||
- access key (required unless the bucket is public)
|
||||
- secret access key (required unless the bucket is public)
|
||||
- security token (if required)
|
||||
- session token (if required)
|
||||
- new path style: NO
|
||||
- Other S3 endpoints:
|
||||
- bucket name (required)
|
||||
- endpoint (required)
|
||||
- access key (required unless the bucket is public)
|
||||
- secret access key (required unless the bucket is public)
|
||||
- new path style: YES
|
||||
|
||||
Address syntax:
|
||||
|
||||
```txt
|
||||
s3://<bucket>@<region>[:profile][:/wrkdir]
|
||||
```
|
||||
|
||||
For example:
|
||||
|
||||
```txt
|
||||
s3://buckethead@eu-central-1:default:/assets
|
||||
```
|
||||
|
||||
### S3 credentials
|
||||
|
||||
To connect to an AWS S3 bucket you must provide credentials. There are three
|
||||
ways to do this.
|
||||
|
||||
1. Authentication form: provide the access key (usually mandatory), the secret
|
||||
access key (usually mandatory), the security token, and the session token.
|
||||
If you save the S3 connection as a bookmark, the access key and secret access
|
||||
key are saved as an encrypted AES-256/BASE64 string in your bookmarks file.
|
||||
The security token and session token are not saved, since they are meant to
|
||||
be temporary credentials.
|
||||
2. Credentials file: configure the AWS CLI with `aws configure`. Your
|
||||
credentials are then stored at `~/.aws/credentials`. If you use a profile
|
||||
other than `default`, provide it in the profile field of the authentication
|
||||
form.
|
||||
3. Environment variables: provide your credentials as environment variables.
|
||||
These always override the credentials in the credentials file. The following
|
||||
are usually mandatory:
|
||||
|
||||
- `AWS_ACCESS_KEY_ID`: AWS access key ID (usually starts with `AKIA...`)
|
||||
- `AWS_SECRET_ACCESS_KEY`: the secret access key
|
||||
|
||||
If you have configured stronger security, you may also need:
|
||||
|
||||
- `AWS_SECURITY_TOKEN`: security token
|
||||
- `AWS_SESSION_TOKEN`: session token
|
||||
|
||||
Your credentials are safe: termscp does not manipulate these values directly.
|
||||
They are consumed directly by the `s3` crate.
|
||||
|
||||
## SMB
|
||||
|
||||
Authentication-form fields:
|
||||
|
||||
- Server (address)
|
||||
- Share
|
||||
- Username
|
||||
- Password
|
||||
- Port (other systems only; default `445`)
|
||||
- Workgroup (other systems only)
|
||||
|
||||
On Windows the port and workgroup fields are not used.
|
||||
|
||||
Windows address syntax:
|
||||
|
||||
```txt
|
||||
\\[username@]<server-name>\<share>[\path\...]
|
||||
```
|
||||
|
||||
Other systems address syntax:
|
||||
|
||||
```txt
|
||||
smb://[username@]<server-name>[:port]/<share>[/path/.../]
|
||||
```
|
||||
|
||||
## WebDAV
|
||||
|
||||
Authentication-form fields:
|
||||
|
||||
- URI (the base WebDAV endpoint)
|
||||
- Username
|
||||
- Password
|
||||
|
||||
Address syntax:
|
||||
|
||||
```txt
|
||||
http(s)://<username>:<password>@<url></path>
|
||||
```
|
||||
@@ -0,0 +1,83 @@
|
||||
# Installation
|
||||
|
||||
termscp is available for many platforms. Pick the method that matches your
|
||||
system below.
|
||||
|
||||
## Linux, FreeBSD, and macOS
|
||||
|
||||
This shell script installs termscp on your system with a single command:
|
||||
|
||||
```sh
|
||||
curl --proto '=https' --tlsv1.2 -sSLf https://termscp.rs/install.sh | sh
|
||||
```
|
||||
|
||||
On macOS the installation requires [Homebrew](https://brew.sh/); otherwise the
|
||||
Rust compiler is installed to build termscp from source.
|
||||
|
||||
## Windows
|
||||
|
||||
Install termscp from PowerShell with a single command:
|
||||
|
||||
```ps
|
||||
irm https://termscp.rs/install.ps1 | iex
|
||||
```
|
||||
|
||||
Alternatively, install it with [Chocolatey](https://chocolatey.org/):
|
||||
|
||||
```ps
|
||||
choco install termscp
|
||||
```
|
||||
|
||||
## NetBSD
|
||||
|
||||
Install termscp from the official repositories:
|
||||
|
||||
```sh
|
||||
pkgin install termscp
|
||||
```
|
||||
|
||||
## Arch Linux
|
||||
|
||||
Install termscp from the official repositories:
|
||||
|
||||
```sh
|
||||
pacman -S termscp
|
||||
```
|
||||
|
||||
## Requirements
|
||||
|
||||
The following system dependencies are required to run termscp.
|
||||
|
||||
- Linux users:
|
||||
- libdbus-1
|
||||
- pkg-config
|
||||
- libsmbclient
|
||||
- FreeBSD and NetBSD users:
|
||||
- dbus
|
||||
- pkgconf
|
||||
- libsmbclient
|
||||
|
||||
### Optional requirements
|
||||
|
||||
These dependencies are not required to run termscp, but they are needed to
|
||||
enjoy all of its features.
|
||||
|
||||
- Linux and FreeBSD users, to open files via `V` (at least one of these):
|
||||
- xdg-open
|
||||
- gio
|
||||
- gnome-open
|
||||
- kde-open
|
||||
- Linux users: a keyring manager. Read more in the
|
||||
[Password security](../configuration/password-security.md) page.
|
||||
- WSL users, to open files via `V`:
|
||||
- [wslu](https://github.com/wslutilities/wslu)
|
||||
|
||||
## Updating termscp
|
||||
|
||||
To update termscp to the latest version, run it from the command line with:
|
||||
|
||||
```sh
|
||||
(sudo) termscp update
|
||||
```
|
||||
|
||||
For all platforms and methods, see <https://termscp.rs/install>.
|
||||
@@ -0,0 +1,28 @@
|
||||
# termscp
|
||||
|
||||

|
||||
|
||||
termscp is a feature-rich terminal file transfer client and explorer with a
|
||||
TUI (Terminal User Interface). It lets you connect to a remote server to
|
||||
upload and download files while interacting with your local file system at the
|
||||
same time. termscp runs on Linux, macOS, FreeBSD, NetBSD, and Windows.
|
||||
|
||||
## Features
|
||||
|
||||
- Multiple transfer protocols: SFTP, SCP, FTP and FTPS, Kube, S3, SMB,
|
||||
and WebDAV.
|
||||
- Dual-pane explorer to browse and operate on both the remote and the local
|
||||
file system: create, remove, rename, search, view, and edit files.
|
||||
- Bookmarks and recent connections to quickly reconnect to your favorite
|
||||
hosts.
|
||||
- View and edit files with your favorite editor.
|
||||
- SFTP/SCP authentication with SSH keys or username and password.
|
||||
- Embedded terminal for running commands on your system.
|
||||
- Make it yours: themes, custom file explorer format, customizable text
|
||||
editor, and customizable file sorting.
|
||||
- Desktop notifications when a large file has been transferred.
|
||||
- File watcher that keeps your changes synchronized with the remote host.
|
||||
- Save your passwords in your operating system's key vault.
|
||||
- Rust-powered and built with an eye on performance.
|
||||
|
||||
Ready to try it? See [Installation](getting-started/installation.md).
|
||||
@@ -0,0 +1,47 @@
|
||||
// Injects a language toggle (EN / 中文) into the mdBook menu bar.
|
||||
// Swaps the leading /en-US/ <-> /zh-CN/ path segment, preserving the
|
||||
// rest of the path; falls back to the language root on 404 navigation.
|
||||
(function () {
|
||||
const LANGS = [
|
||||
{ code: "en-US", label: "EN" },
|
||||
{ code: "zh-CN", label: "中文" },
|
||||
];
|
||||
|
||||
function currentLang() {
|
||||
const m = window.location.pathname.match(/\/(en-US|zh-CN)\//);
|
||||
return m ? m[1] : "en-US";
|
||||
}
|
||||
|
||||
function swapTo(code) {
|
||||
const path = window.location.pathname;
|
||||
const cur = currentLang();
|
||||
if (path.includes(`/${cur}/`)) {
|
||||
return path.replace(`/${cur}/`, `/${code}/`);
|
||||
}
|
||||
return `/${code}/`;
|
||||
}
|
||||
|
||||
function build() {
|
||||
const right = document.querySelector(".right-buttons");
|
||||
if (!right) return;
|
||||
const cur = currentLang();
|
||||
const wrap = document.createElement("div");
|
||||
wrap.className = "lang-switcher";
|
||||
wrap.style.display = "inline-flex";
|
||||
wrap.style.gap = "0.5rem";
|
||||
wrap.style.marginInlineStart = "0.5rem";
|
||||
LANGS.forEach((l) => {
|
||||
const a = document.createElement("a");
|
||||
a.textContent = l.label;
|
||||
a.href = swapTo(l.code);
|
||||
a.title = l.code;
|
||||
a.setAttribute("aria-current", l.code === cur ? "true" : "false");
|
||||
if (l.code === cur) a.style.fontWeight = "bold";
|
||||
wrap.appendChild(a);
|
||||
});
|
||||
right.appendChild(wrap);
|
||||
}
|
||||
|
||||
if (document.readyState !== "loading") build();
|
||||
else document.addEventListener("DOMContentLoaded", build);
|
||||
})();
|
||||
@@ -0,0 +1,39 @@
|
||||
// This Source Code Form is subject to the terms of the Mozilla Public
|
||||
// License, v. 2.0. If a copy of the MPL was not distributed with this
|
||||
// file, You can obtain one at https://mozilla.org/MPL/2.0/.
|
||||
|
||||
(() => {
|
||||
const darkThemes = ['ayu', 'navy', 'coal'];
|
||||
const lightThemes = ['light', 'rust'];
|
||||
|
||||
const classList = document.getElementsByTagName('html')[0].classList;
|
||||
|
||||
let lastThemeWasLight = true;
|
||||
for (const cssClass of classList) {
|
||||
if (darkThemes.includes(cssClass)) {
|
||||
lastThemeWasLight = false;
|
||||
break;
|
||||
}
|
||||
}
|
||||
|
||||
const theme = lastThemeWasLight ? 'default' : 'dark';
|
||||
mermaid.initialize({ startOnLoad: true, theme });
|
||||
|
||||
// Simplest way to make mermaid re-render the diagrams in the new theme is via refreshing the page
|
||||
|
||||
for (const darkTheme of darkThemes) {
|
||||
document.getElementById(darkTheme).addEventListener('click', () => {
|
||||
if (lastThemeWasLight) {
|
||||
window.location.reload();
|
||||
}
|
||||
});
|
||||
}
|
||||
|
||||
for (const lightTheme of lightThemes) {
|
||||
document.getElementById(lightTheme).addEventListener('click', () => {
|
||||
if (!lastThemeWasLight) {
|
||||
window.location.reload();
|
||||
}
|
||||
});
|
||||
}
|
||||
})();
|
||||
@@ -0,0 +1,13 @@
|
||||
<link rel="icon" type="image/x-icon" href="/shared/favicon.ico">
|
||||
<link rel="icon" type="image/svg+xml" href="/shared/termscp.svg">
|
||||
|
||||
<meta property="og:title" content="{{#if chapter_title}}{{ chapter_title }} · {{/if}}{{ book_title }}">
|
||||
<meta property="og:description" content="A feature rich terminal UI file transfer and explorer with support for SCP/SFTP/FTP/Kube/S3/SMB/WebDAV">
|
||||
<meta property="og:image" content="https://docs.termscp.rs/og_preview.jpg">
|
||||
<meta property="og:url" content="https://docs.termscp.rs/">
|
||||
<meta property="og:type" content="website">
|
||||
|
||||
<meta name="twitter:card" content="summary_large_image">
|
||||
<meta name="twitter:title" content="{{#if chapter_title}}{{ chapter_title }} · {{/if}}{{ book_title }}">
|
||||
<meta name="twitter:description" content="A feature rich terminal UI file transfer and explorer with support for SCP/SFTP/FTP/Kube/S3/SMB/WebDAV">
|
||||
<meta name="twitter:image" content="https://docs.termscp.rs/og_preview.jpg">
|
||||
@@ -0,0 +1,31 @@
|
||||
# Bookmarks and recent hosts
|
||||
|
||||
termscp lets you save your favourite hosts as bookmarks, which can then be loaded quickly from the main layout. termscp also keeps the last 16 hosts you connected to. Both features let you reload all the parameters required to connect to a remote simply by selecting an entry in the tab under the authentication form.
|
||||
|
||||
## Where bookmarks are stored
|
||||
|
||||
Bookmarks are saved, when possible, in the configuration directory:
|
||||
|
||||
- `$HOME/.config/termscp/` on Linux/BSD
|
||||
- `$HOME/.config/termscp/` on macOS
|
||||
- `%USERPROFILE%\.termscp\` on Windows
|
||||
|
||||
## Saving passwords
|
||||
|
||||
For bookmarks only, you can optionally save the password used to authenticate. This does not apply to recent hosts, which never save passwords. The password is not saved by default; you are prompted to choose whether to save it when you create a new bookmark.
|
||||
|
||||
If you are concerned about the security of the passwords saved for your bookmarks, see [Are my passwords safe?](../configuration/password-security.md)
|
||||
|
||||
## Creating a bookmark
|
||||
|
||||
1. Fill in the authentication form with the parameters to connect to your remote server.
|
||||
2. Press `<CTRL+S>`.
|
||||
3. Type the name you want to give to the bookmark.
|
||||
4. Choose whether to remember the password.
|
||||
5. Press `<ENTER>` to submit.
|
||||
|
||||
## Loading a bookmark
|
||||
|
||||
To use a previously saved connection, press `<TAB>` to navigate to the bookmarks list, then press `<ENTER>` to load the bookmark parameters into the form.
|
||||
|
||||

|
||||
@@ -0,0 +1,18 @@
|
||||
# The file explorer
|
||||
|
||||
After you establish a connection with a remote host, termscp shows the file explorer. The explorer is made up of three panels.
|
||||
|
||||
- **Local explorer panel**: displayed on the left of the screen. It shows the entries of the current directory on localhost.
|
||||
- **Remote explorer panel**: displayed on the right of the screen. It shows the entries of the current directory on the remote host.
|
||||
- **Find results panel**: shown after you search for files. Depending on where you searched (local or remote), it replaces the local explorer panel or the remote explorer panel and lists the entries matching your search query.
|
||||
|
||||
## Switching between panels
|
||||
|
||||
Use the following keys to move between panels.
|
||||
|
||||
- `<LEFT>`: move to the local explorer panel.
|
||||
- `<RIGHT>`: move to the remote explorer panel.
|
||||
- `<TAB>`: switch the active explorer tab.
|
||||
- `<ESC>`: while in the find results panel, exit it and return to the previous panel.
|
||||
|
||||
For the complete list of keys available in the explorer, see [Keyboard shortcuts](keyboard-shortcuts.md).
|
||||
@@ -0,0 +1,29 @@
|
||||
# Keeping files in sync
|
||||
|
||||
The file watcher synchronizes local paths to a remote path. When a change is detected on a watched local path, it is propagated to the configured remote path within about 5 seconds.
|
||||
|
||||
You can watch as many paths as you like.
|
||||
|
||||
## Watching a path
|
||||
|
||||
1. Put the cursor on the local explorer, on the file or directory you want to keep synchronized.
|
||||
2. In the remote panel, navigate to the directory where the changes should be reported.
|
||||
3. Press `<T>`.
|
||||
4. Answer `<YES>` to the popup.
|
||||
|
||||
## Unwatching a path
|
||||
|
||||
You can stop watching a path in two ways:
|
||||
|
||||
- Press `<T>` on the watched local path (or any of its subfolders).
|
||||
- Press `<CTRL+T>`, then press `<ENTER>` on the path you want to unwatch.
|
||||
|
||||
## Propagated changes
|
||||
|
||||
The following changes are reported to the remote host:
|
||||
|
||||
- New files and file changes
|
||||
- Files moved or renamed
|
||||
- Files removed or unlinked
|
||||
|
||||
The watcher works in one direction only (local to remote). Changes made on the remote host are **not** synchronized back to the local host.
|
||||
@@ -0,0 +1,49 @@
|
||||
# Keyboard shortcuts
|
||||
|
||||
The following keys are available in the file explorer. Press `<H|F1>` at any time to open the in-app help.
|
||||
|
||||
| Key | Action |
|
||||
| -------------- | ---------------------------------------------------------------------- |
|
||||
| `<ESC>` | Disconnect from the remote and return to the authentication page |
|
||||
| `<BACKSPACE>` | Go to the previous directory in the navigation stack |
|
||||
| `<TAB>` | Switch the active explorer tab |
|
||||
| `<RIGHT>` | Move to the remote explorer tab |
|
||||
| `<LEFT>` | Move to the local explorer tab |
|
||||
| `<UP>` | Move up in the selected list |
|
||||
| `<DOWN>` | Move down in the selected list |
|
||||
| `<PGUP>` | Move up in the selected list by 8 rows |
|
||||
| `<PGDOWN>` | Move down in the selected list by 8 rows |
|
||||
| `<ENTER>` | Enter the selected directory |
|
||||
| `<SPACE>` | Upload or download the selected file |
|
||||
| `<BACKTAB>` | Switch between the log tab and the explorer |
|
||||
| `<A>` | Toggle the display of hidden files |
|
||||
| `<B>` | Choose how files are sorted |
|
||||
| `<C\|F5>` | Copy the selected file or directory |
|
||||
| `<D\|F7>` | Make a new directory |
|
||||
| `<E\|F8\|DEL>` | Delete the selected file |
|
||||
| `<F>` | Search for files (wildcard matching is supported) |
|
||||
| `<G>` | Go to the supplied path |
|
||||
| `<H\|F1>` | Show the help |
|
||||
| `<I>` | Show information about the selected file or directory |
|
||||
| `<K>` | Create a symlink pointing to the currently selected entry |
|
||||
| `<L>` | Reload the current directory's content, or clear the current selection |
|
||||
| `<M>` | Select a file |
|
||||
| `<N>` | Create a new file with the provided name |
|
||||
| `<O\|F4>` | Edit the selected file in your text editor |
|
||||
| `<P>` | Open the log panel |
|
||||
| `<Q\|F10>` | Quit termscp |
|
||||
| `<R\|F6>` | Rename the selected file |
|
||||
| `<S\|F2>` | Save the selected file as a new name |
|
||||
| `<T>` | Synchronize changes on the selected path to the remote |
|
||||
| `<U>` | Go to the parent directory |
|
||||
| `<V\|F3>` | Open the selected file with the default program for its file type |
|
||||
| `<W>` | Open the selected file with a program you specify |
|
||||
| `<X>` | Execute a command |
|
||||
| `<Y>` | Toggle synchronized browsing |
|
||||
| `<Z>` | Change the file mode |
|
||||
| `</>` | Filter files (both regex and wildcard matching are supported) |
|
||||
| `<CTRL+A>` | Select all files |
|
||||
| `<ALT+A>` | Deselect all files |
|
||||
| `<CTRL+C>` | Abort the file transfer process |
|
||||
| `<CTRL+S>` | Get the total size of the selected path |
|
||||
| `<CTRL+T>` | Show all synchronized paths |
|
||||
@@ -0,0 +1,32 @@
|
||||
# Working with multiple files
|
||||
|
||||
termscp lets you act on several files at once. Use these controls to build a selection.
|
||||
|
||||
- `<M>`: mark the highlighted file for selection.
|
||||
- `<CTRL+A>`: select all files in the current directory.
|
||||
- `<ALT+A>`: deselect all files.
|
||||
|
||||
Once a file is marked for selection, it is displayed with a highlighted background.
|
||||
|
||||
When a selection exists, only the selected files are processed for actions; the currently highlighted item is ignored. You can also work on multiple files while in the find results panel.
|
||||
|
||||
## Actions on a selection
|
||||
|
||||
All actions are available when working with multiple files, but some behave slightly differently. With a selection, the name you enter refers to the destination directory rather than a single destination file.
|
||||
|
||||
- **Copy**: you are prompted for a destination. With multiple files selected, this name is the destination directory where all the files are copied.
|
||||
- **Rename**: same as copy, but the files are moved to the destination directory.
|
||||
- **Save as**: same as copy, but the files are written to the destination directory.
|
||||
|
||||
## The transfer queue
|
||||
|
||||
If you select a file in a directory (for example `/home`) and then change directory, the file stays selected and is shown in the **transfer queue** in the bottom panel.
|
||||
|
||||
When a file is selected, the remote directory active at that moment is associated with its entry. If the file is later transferred, it is transferred to the remote directory associated with it.
|
||||
|
||||
### Example
|
||||
|
||||
Suppose you select the local file `/home/a.txt` while the remote panel is at `/tmp`, then you move to `/var`, select `/var/b.txt` while the remote panel is at `/home`, and finally perform a transfer. The result is:
|
||||
|
||||
- `/home/a.txt` is transferred to `/tmp/a.txt`
|
||||
- `/var/b.txt` is transferred to `/home/b.txt`
|
||||
@@ -0,0 +1,24 @@
|
||||
# Opening and editing files
|
||||
|
||||
termscp can open files with an external application and edit text files in your configured editor. Both local and remote files are supported.
|
||||
|
||||
## Open and Open With
|
||||
|
||||
Press `<V>` to open a file with the system default application for its file type. termscp relies on your operating system's default opener (powered by the [open](https://docs.rs/crate/open/1.7.0) crate), so make sure at least one of the following is available on your system.
|
||||
|
||||
- **Windows**: handled automatically through the `start` command.
|
||||
- **macOS**: handled automatically through `open`, which is already installed.
|
||||
- **Linux**: one of `xdg-open`, `gio`, `gnome-open`, or `kde-open` must be installed.
|
||||
- **WSL**: `wslview` is required. Install [wslu](https://github.com/wslutilities/wslu).
|
||||
|
||||
Press `<W>` to open a file with a program you specify.
|
||||
|
||||
## Editing text files
|
||||
|
||||
Press `<O>` to open a file in your configured text editor. Only text files are supported; binary files are not.
|
||||
|
||||
If the file is located on the remote host, it is first downloaded into your temporary file directory, and then re-uploaded to the remote host **only** if you changed it. termscp detects changes by checking the file's last modification time.
|
||||
|
||||
## Editing remote files
|
||||
|
||||
You cannot edit a remote file in place directly from the remote panel. When you open a remote file, it is downloaded into a temporary directory, but termscp cannot create a watcher to detect when the external program you used to open it has closed, so it cannot tell when you are done editing. To edit a remote file, download it to a local directory first, edit it there, and then upload it again.
|
||||
@@ -0,0 +1,5 @@
|
||||
# Synchronized browsing
|
||||
|
||||
Synchronized browsing keeps navigation in sync between the two explorer panels. While it is enabled, whenever you change the working directory in one panel, the same change is reproduced in the other panel.
|
||||
|
||||
To enable synchronized browsing, press `<Y>`. Press `<Y>` again to disable it. While it is enabled, the status bar reports the synchronized browsing state as `ON`.
|
||||
@@ -1,289 +0,0 @@
|
||||
# termscp
|
||||
|
||||
<p align="center">
|
||||
<img src="/assets/images/termscp.svg" width="256" height="256" />
|
||||
</p>
|
||||
|
||||
<p align="center">~ Una transferencia de archivos de terminal rica en funciones ~</p>
|
||||
<p align="center">
|
||||
<a href="https://termscp.veeso.dev" target="_blank">Sitio Web</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#get-started" target="_blank">Instalación</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#user-manual" target="_blank">Manual de usuario</a>
|
||||
</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/gb.png"
|
||||
alt="English"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/de/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/de.png"
|
||||
alt="Deutsch"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/es/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/es.png"
|
||||
alt="Español"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/fr/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/fr.png"
|
||||
alt="Français"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/it/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/it.png"
|
||||
alt="Italiano"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/zh-CN/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/cn.png"
|
||||
alt="简体中文"
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
<p align="center">Desarrollado por <a href="https://veeso.dev/" target="_blank">@veeso</a></p>
|
||||
<p align="center">Versión actual: 0.12.3 (06/10/2023)</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://opensource.org/licenses/MIT"
|
||||
><img
|
||||
src="https://img.shields.io/badge/License-MIT-teal.svg"
|
||||
alt="License-MIT"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/stargazers"
|
||||
><img
|
||||
src="https://img.shields.io/github/stars/veeso/termscp.svg"
|
||||
alt="Repo stars"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/d/termscp.svg"
|
||||
alt="Downloads counter"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/v/termscp.svg"
|
||||
alt="Latest version"
|
||||
/></a>
|
||||
<a href="https://ko-fi.com/veeso">
|
||||
<img
|
||||
src="https://img.shields.io/badge/donate-ko--fi-red"
|
||||
alt="Ko-fi"
|
||||
/></a>
|
||||
</p>
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Linux/badge.svg"
|
||||
alt="Linux CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/MacOS/badge.svg"
|
||||
alt="MacOS CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Windows/badge.svg"
|
||||
alt="Windows CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/FreeBSD/badge.svg"
|
||||
alt="FreeBSD CI"
|
||||
/></a>
|
||||
<a href="https://coveralls.io/github/veeso/termscp"
|
||||
><img
|
||||
src="https://coveralls.io/repos/github/veeso/termscp/badge.svg"
|
||||
alt="Coveralls"
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
---
|
||||
|
||||
## Sobre termscp 🖥
|
||||
|
||||
Termscp es un explorador y transferencia de archivos de terminal rico en funciones, con apoyo para SCP/SFTP/FTP/S3. Básicamente, es una utilidad de terminal con una TUI para conectarse a un servidor remoto para recuperar y cargar archivos e interactuar con el sistema de archivos local. Es compatible con **Linux**, **MacOS**, **FreeBSD** y **Windows**.
|
||||
|
||||

|
||||
|
||||
---
|
||||
|
||||
## Características 🎁
|
||||
|
||||
- 📁 Diferentes protocolos de comunicación
|
||||
- **SFTP**
|
||||
- **SCP**
|
||||
- **FTP** y **FTPS**
|
||||
- **S3**
|
||||
- **SMB**
|
||||
- 🖥 Explore y opere en el sistema de archivos de la máquina local y remota con una interfaz de usuario práctica
|
||||
- Cree, elimine, cambie el nombre, busque, vea y edite archivos
|
||||
- ⭐ Conéctese a sus hosts favoritos y conexiones recientes
|
||||
- 📝 Ver y editar archivos con sus aplicaciones favoritas
|
||||
- 💁 Autenticación SFTP / SCP con claves SSH y nombre de usuario / contraseña
|
||||
- 🐧 compatible con Linux, MacOS, FreeBSD y Windows
|
||||
- 🎨 Haz lo tuyo!
|
||||
- Temas
|
||||
- Formato de explorador de archivos personalizado
|
||||
- Editor de texto personalizable
|
||||
- Clasificación de archivos personalizable
|
||||
- y muchos otros parámetros ...
|
||||
- 📫 Reciba una notificación cuando se haya transferido un archivo grande
|
||||
- 🔭 Mantenga los cambios de archivos sincronizados con el host remoto
|
||||
- 🔐 Guarde su contraseña en el almacén de claves de su sistema operativo
|
||||
- 🦀 Rust-powered
|
||||
- 👀 Desarrollado sin perder de vista el rendimiento
|
||||
- 🦄 Actualizaciones frecuentes
|
||||
|
||||
---
|
||||
|
||||
## Para iniciar 🚀
|
||||
|
||||
Si estás considerando instalar termscp, ¡quiero darte las gracias 💜! ¡Espero que disfrutes de termscp!
|
||||
Si desea contribuir a este proyecto, no olvide consultar nuestra [guía de contribución](../../CONTRIBUTING.md).
|
||||
|
||||
Si tu eres un usuario de Linux, FreeBSD o MacOS, este sencillo script de shell instalará termscp en tu sistema con un solo comando:
|
||||
|
||||
```sh
|
||||
curl -sSLf http://get-termscp.veeso.dev | sh
|
||||
```
|
||||
|
||||
mientras que si eres un usuario de Windows, puedes instalar termscp con [Chocolatey](https://chocolatey.org/):
|
||||
|
||||
```sh
|
||||
choco install termscp
|
||||
```
|
||||
|
||||
Para obtener más información u otras plataformas, visite [termscp.veeso.dev](https://termscp.veeso.dev/termscp/#get-started) para ver todos los métodos de instalación.
|
||||
|
||||
⚠️ Si estás buscando cómo actualizar termscp, simplemente ejecute termscp desde CLI con:: `(sudo) termscp --update` ⚠️
|
||||
|
||||
### Requisitos ❗
|
||||
|
||||
- **Linux** users:
|
||||
- libdbus-1
|
||||
- pkg-config
|
||||
- libsmbclient
|
||||
- **FreeBSD** or, **NetBSD** users:
|
||||
- dbus
|
||||
- pkgconf
|
||||
- libsmbclient
|
||||
|
||||
### Requisitos opcionales ✔️
|
||||
|
||||
These requirements are not forced required to run termscp, but to enjoy all of its features
|
||||
|
||||
- Usuarios **Linux/FreeBSD**:
|
||||
- Para **abrir** archivos con `V` (al menos uno de estos)
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- Usuarios **Linux**:
|
||||
- Un keyring manager: leer más en el [manual de usuario](man.md#linux-keyring)
|
||||
- Usuarios **WSL**
|
||||
- Para **abrir** archivos con `V` (al menos uno de estos)
|
||||
- [wslu](https://github.com/wslutilities/wslu)
|
||||
|
||||
---
|
||||
|
||||
## Apoyame ☕
|
||||
|
||||
Si te gusta termscp y te encantaría que el proyecto crezca y mejore, considera una pequeña donación para apoyarme 🥳
|
||||
|
||||
Puedes hacer una donación con una de estas plataformas:
|
||||
|
||||
[](https://ko-fi.com/veeso)
|
||||
[](https://www.paypal.me/chrisintin)
|
||||
|
||||
---
|
||||
|
||||
## Manual de usuario y documentación 📚
|
||||
|
||||
El manual del usuario se puede encontrar en el [sitio web de termscp](https://termscp.veeso.dev/termscp/#user-manual) o en [Github](man.md).
|
||||
|
||||
---
|
||||
|
||||
## Contribuir y problemas 🤝🏻
|
||||
|
||||
¡Las contribuciones, los informes de errores, las nuevas funciones y las preguntas son bienvenidas! 😉
|
||||
Si tiene alguna pregunta o inquietud, o si desea sugerir una nueva función, o simplemente desea mejorar termscp, no dude en abrir un problema o un PR.
|
||||
|
||||
Sigue [nuestras pautas de contribución](../../CONTRIBUTING.md)
|
||||
|
||||
---
|
||||
|
||||
## Changelog ⏳
|
||||
|
||||
Ver registro de cambios de termscp [AQUÍ](../../CHANGELOG.md)
|
||||
|
||||
---
|
||||
|
||||
## Powered by 💪
|
||||
|
||||
termscp funciona con estos increíbles proyectos:
|
||||
|
||||
- [bytesize](https://github.com/hyunsik/bytesize)
|
||||
- [crossterm](https://github.com/crossterm-rs/crossterm)
|
||||
- [edit](https://github.com/milkey-mouse/edit)
|
||||
- [keyring-rs](https://github.com/hwchen/keyring-rs)
|
||||
- [open-rs](https://github.com/Byron/open-rs)
|
||||
- [rpassword](https://github.com/conradkleinespel/rpassword)
|
||||
- [rust-s3](https://github.com/durch/rust-s3)
|
||||
- [self_update](https://github.com/jaemk/self_update)
|
||||
- [ssh2-rs](https://github.com/alexcrichton/ssh2-rs)
|
||||
- [suppaftp](https://github.com/veeso/suppaftp)
|
||||
- [tui-rs](https://github.com/fdehau/tui-rs)
|
||||
- [tui-realm](https://github.com/veeso/tui-realm)
|
||||
- [whoami](https://github.com/libcala/whoami)
|
||||
- [wildmatch](https://github.com/becheran/wildmatch)
|
||||
|
||||
---
|
||||
|
||||
## Galería 🎬
|
||||
|
||||
> Termscp Home
|
||||
|
||||

|
||||
|
||||
> Bookmarks
|
||||
|
||||

|
||||
|
||||
> Setup
|
||||
|
||||

|
||||
|
||||
> Text editor
|
||||
|
||||

|
||||
|
||||
---
|
||||
|
||||
## Licencia 📃
|
||||
|
||||
termscp tiene la licencia MIT.
|
||||
|
||||
Puede leer la licencia completa [AQUÍ](../../LICENSE)
|
||||
@@ -1,558 +0,0 @@
|
||||
# User manual 🎓
|
||||
|
||||
- [User manual 🎓](#user-manual-)
|
||||
- [Uso ❓](#uso-)
|
||||
- [Argumento dirección 🌎](#argumento-dirección-)
|
||||
- [Argumento dirección por AWS S3](#argumento-dirección-por-aws-s3)
|
||||
- [Argumento dirección por SMB](#argumento-dirección-por-smb)
|
||||
- [Cómo se puede proporcionar la contraseña 🔐](#cómo-se-puede-proporcionar-la-contraseña-)
|
||||
- [S3 parámetros de conexión](#s3-parámetros-de-conexión)
|
||||
- [Credenciales de S3 🦊](#credenciales-de-s3-)
|
||||
- [Explorador de archivos 📂](#explorador-de-archivos-)
|
||||
- [Keybindings ⌨](#keybindings-)
|
||||
- [Trabaja en varios archivos 🥷](#trabaja-en-varios-archivos-)
|
||||
- [Navegación sincronizada ⏲️](#navegación-sincronizada-️)
|
||||
- [Abierta y abierta con 🚪](#abierta-y-abierta-con-)
|
||||
- [Marcadores ⭐](#marcadores-)
|
||||
- [¿Son seguras mis contraseñas? 😈](#son-seguras-mis-contraseñas-)
|
||||
- [Linux Keyring](#linux-keyring)
|
||||
- [KeepassXC setup por termscp](#keepassxc-setup-por-termscp)
|
||||
- [Configuración ⚙️](#configuración--️)
|
||||
- [SSH Key Storage 🔐](#ssh-key-storage-)
|
||||
- [Formato del explorador de archivos](#formato-del-explorador-de-archivos)
|
||||
- [Temas 🎨](#temas-)
|
||||
- [Mi tema no se carga 😱](#mi-tema-no-se-carga-)
|
||||
- [Estilos 💈](#estilos-)
|
||||
- [Authentication page](#authentication-page)
|
||||
- [Transfer page](#transfer-page)
|
||||
- [Misc](#misc)
|
||||
- [Text Editor ✏](#text-editor-)
|
||||
- [Logging 🩺](#logging-)
|
||||
- [Notificaciones 📫](#notificaciones-)
|
||||
- [Observador de archivos 🔭](#observador-de-archivos-)
|
||||
|
||||
> ❗ Este documento ha sido traducido con Google Translator (y luego lo he revisado a grandes rasgos, pero no puedo hablar el idioma muy bien). Si habla l'idioma, abra un [issue](https://github.com/veeso/termscp/issues/new/choose) utilizando la label COPY o abra un PR 🙏
|
||||
|
||||
## Uso ❓
|
||||
|
||||
termscp se puede iniciar con las siguientes opciones:
|
||||
|
||||
`termscp [options]... [protocol://user@address:port:wrkdir] [local-wrkdir]`
|
||||
|
||||
OR
|
||||
|
||||
`termscp [options]... -b [bookmark-name] [local-wrkdir]`
|
||||
|
||||
- `-P, --password <password>` si se proporciona la dirección, la contraseña será este argumento
|
||||
- `-b, --address-as-bookmark` resuelve el argumento de la dirección como un nombre de marcador
|
||||
- `-c, --config` Abrir termscp comenzando desde la página de configuración
|
||||
- `-q, --quiet` Deshabilitar el registro
|
||||
- `-t, --theme <path>` Importar tema especificado
|
||||
- `-u, --update` Actualizar termscp a la última versión
|
||||
- `-v, --version` Imprimir información de la versión
|
||||
- `-h, --help` Imprimir página de ayuda
|
||||
|
||||
termscp se puede iniciar en dos modos diferentes, si no se proporcionan argumentos adicionales, termscp mostrará el formulario de autenticación, donde el usuario podrá proporcionar los parámetros necesarios para conectarse al par remoto.
|
||||
|
||||
Alternativamente, el usuario puede proporcionar una dirección como argumento para omitir el formulario de autenticación e iniciar directamente la conexión al servidor remoto.
|
||||
|
||||
Si se proporciona un argumento de dirección, también puede proporcionar el directorio de inicio de trabajo para el host local
|
||||
|
||||
### Argumento dirección 🌎
|
||||
|
||||
El argumento dirección tiene la siguiente sintaxis:
|
||||
|
||||
```txt
|
||||
[protocol://][username@]<address>[:port][:wrkdir]
|
||||
```
|
||||
|
||||
Veamos algún ejemplo de esta sintaxis en particular, ya que es muy cómoda y probablemente usarás esta en lugar de la otra ...
|
||||
|
||||
- Conéctese usando el protocolo predeterminado (*definido en la configuración*) a 192.168.1.31, el puerto, si no se proporciona, es el predeterminado para el protocolo seleccionado (en este caso, depende de su configuración); nombre de usuario es el nombre del usuario actual
|
||||
|
||||
```sh
|
||||
termscp 192.168.1.31
|
||||
```
|
||||
|
||||
- Conéctese usando el protocolo predeterminado (*definido en la configuración*) a 192.168.1.31; el nombre de usuario es `root`
|
||||
|
||||
```sh
|
||||
termscp root@192.168.1.31
|
||||
```
|
||||
|
||||
- Conéctese usando scp a 192.168.1.31, el puerto es 4022; nombre de usuario es `omar`
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022
|
||||
```
|
||||
|
||||
- Conéctese usando scp a 192.168.1.31, el puerto es 4022; El nombre de usuario es `omar`. Comenzará en el directorio `/ tmp`
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022:/tmp
|
||||
```
|
||||
|
||||
#### Argumento dirección por AWS S3
|
||||
|
||||
Aws S3 tiene una sintaxis diferente para el argumento de la dirección CLI, por razones obvias, pero logré mantenerlo lo más similar posible al argumento de la dirección genérica:
|
||||
|
||||
```txt
|
||||
s3://<bucket-name>@<region>[:profile][:/wrkdir]
|
||||
```
|
||||
|
||||
por ejemplo
|
||||
|
||||
```txt
|
||||
s3://buckethead@eu-central-1:default:/assets
|
||||
```
|
||||
|
||||
#### Argumento dirección por SMB
|
||||
|
||||
SMB tiene una sintaxis diferente para el argumento de la dirección CLI, que es diferente si está en Windows u otros sistemas:
|
||||
|
||||
**Windows** sintaxis:
|
||||
|
||||
```txt
|
||||
\\[username@]<server-name>\<share>[\path\...]
|
||||
```
|
||||
|
||||
**Other systems** sintaxis:
|
||||
|
||||
```txt
|
||||
smb://[username@]<server-name>[:port]/<share>[/path/.../]
|
||||
```
|
||||
|
||||
#### Cómo se puede proporcionar la contraseña 🔐
|
||||
|
||||
Probablemente haya notado que, al proporcionar la dirección como argumento, no hay forma de proporcionar la contraseña.
|
||||
La contraseña se puede proporcionar básicamente a través de 3 formas cuando se proporciona un argumento de dirección:
|
||||
|
||||
- `-P, --password` opción: simplemente use esta opción CLI proporcionando la contraseña. No recomiendo este método, ya que es muy inseguro (ya que puede mantener la contraseña en el historial de shell)
|
||||
- Con `sshpass`: puede proporcionar la contraseña a través de `sshpass`, p. ej. `sshpass -f ~/.ssh/topsecret.key termscp cvisintin@192.168.1.31`
|
||||
- Se te pedirá que ingreses: si no utilizas ninguno de los métodos anteriores, se te pedirá la contraseña, como ocurre con las herramientas más clásicas como `scp`, `ssh`, etc.
|
||||
|
||||
---
|
||||
|
||||
## S3 parámetros de conexión
|
||||
|
||||
Estos parámetros son necesarios para conectarse a aws s3 y otros servidores compatibles con s3:
|
||||
|
||||
- AWS S3:
|
||||
- **bucket name**
|
||||
- **region**
|
||||
- *profile* (si no se proporciona: "default")
|
||||
- *access key* (A menos que sea pública)
|
||||
- *secret access key* (A menos que sea pública)
|
||||
- *security token* (si es requerido)
|
||||
- *session token* (si es requerido)
|
||||
- new path style: **NO**
|
||||
- Otros puntos finales de S3:
|
||||
- **bucket name**
|
||||
- **endpoint**
|
||||
- *access key* (A menos que sea pública)
|
||||
- *secret access key* (A menos que sea pública)
|
||||
- new path style: **YES**
|
||||
|
||||
### Credenciales de S3 🦊
|
||||
|
||||
Para conectarse a un bucket de Aws S3, obviamente debe proporcionar algunas credenciales.
|
||||
Básicamente, hay tres formas de lograr esto.
|
||||
Entonces, estas son las formas en que puede proporcionar las credenciales para s3:
|
||||
|
||||
1. Authentication form:
|
||||
1. Puede proporcionar la `access_key` (debería ser obligatoria), la `secret_access_kedy` (debería ser obligatoria), el `security_token` y el `session_token`
|
||||
2. Si guarda la conexión s3 como marcador, estas credenciales se guardarán como una cadena AES-256 / BASE64 cifrada en su archivo de marcadores (excepto el token de seguridad y el token de sesión, que deben ser credenciales temporales).
|
||||
2. Use su archivo de credenciales: simplemente configure la cli de AWS a través de `aws configure` y sus credenciales ya deberían estar ubicadas en`~/.aws/credentials`. En caso de que esté usando un perfil diferente al "predeterminado", simplemente proporciónelo en el campo de perfil en el formulario de autenticación.
|
||||
3. **Variables de entorno**: siempre puede proporcionar sus credenciales como variables de entorno. Tenga en cuenta que estas credenciales **siempre anularán** las credenciales ubicadas en el archivo `credentials`. Vea cómo configurar el entorno a continuación:
|
||||
|
||||
Estos siempre deben ser obligatorios:
|
||||
|
||||
- `AWS_ACCESS_KEY_ID`: aws access key ID (generalmente comienza con `AKIA...`)
|
||||
- `AWS_SECRET_ACCESS_KEY`: la secret access key
|
||||
|
||||
En caso de que haya configurado una seguridad más fuerte, *puede* requerir estos también:
|
||||
|
||||
- `AWS_SECURITY_TOKEN`: security token
|
||||
- `AWS_SESSION_TOKEN`: session token
|
||||
|
||||
⚠️ Sus credenciales están seguras: ¡termscp no manipulará estos valores directamente! Sus credenciales son consumidas directamente por la caja **s3**.
|
||||
En caso de que tenga alguna inquietud con respecto a la seguridad, comuníquese con el autor de la biblioteca en [Github](https://github.com/durch/rust-s3) ⚠️
|
||||
|
||||
---
|
||||
|
||||
## Explorador de archivos 📂
|
||||
|
||||
Cuando nos referimos a exploradores de archivos en termscp, nos referimos a los paneles que puede ver después de establecer una conexión con el control remoto.
|
||||
Estos paneles son básicamente 3:
|
||||
|
||||
- Panel del explorador local: se muestra a la izquierda de la pantalla y muestra las entradas del directorio actual para localhost
|
||||
- Panel del explorador remoto: se muestra a la derecha de la pantalla y muestra las entradas del directorio actual para el host remoto.
|
||||
- Panel de resultados de búsqueda: dependiendo de dónde esté buscando archivos (local / remoto), reemplazará el panel local o del explorador. Este panel muestra las entradas que coinciden con la consulta de búsqueda que realizó.
|
||||
|
||||
Para cambiar de panel, debe escribir `<LEFT>` para mover el panel del explorador remoto y `<RIGHT>` para volver al panel del explorador local. Siempre que se encuentre en el panel de resultados de búsqueda, debe presionar `<ESC>` para salir del panel y volver al panel anterior.
|
||||
|
||||
### Keybindings ⌨
|
||||
|
||||
| Key | Command | Reminder |
|
||||
|---------------|----------------------------------------------------------------------------|-------------|
|
||||
| `<ESC>` | Desconecte; volver a la página de autenticación | |
|
||||
| `<BACKSPACE>` | Ir al directorio anterior en la pila | |
|
||||
| `<TAB>` | Cambiar pestaña del explorador | |
|
||||
| `<RIGHT>` | Mover a la pestaña del explorador remoto | |
|
||||
| `<LEFT>` | Mover a la pestaña del explorador local | |
|
||||
| `<UP>` | Subir en la lista seleccionada | |
|
||||
| `<DOWN>` | Bajar en la lista seleccionada | |
|
||||
| `<PGUP>` | Subir 8 filas en la lista seleccionada | |
|
||||
| `<PGDOWN>` | Bajar 8 filas en la lista seleccionada | |
|
||||
| `<ENTER>` | Entrar directorio | |
|
||||
| `<SPACE>` | Cargar / descargar el archivo seleccionado | |
|
||||
| `<BACKTAB>` | Cambiar entre la pestaña de registro y el explorador | |
|
||||
| `<A>` | Alternar archivos ocultos | All |
|
||||
| `<B>` | Ordenar archivos por | Bubblesort? |
|
||||
| `<C|F5>` | Copiar archivo / directorio | Copy |
|
||||
| `<D|F7>` | Hacer directorio | Directory |
|
||||
| `<E|F8|DEL>` | Eliminar archivo | Erase |
|
||||
| `<F>` | Búsqueda de archivos | Find |
|
||||
| `<G>` | Ir a la ruta proporcionada | Go to |
|
||||
| `<H|F1>` | Mostrar ayuda | Help |
|
||||
| `<I>` | Mostrar información sobre el archivo | Info |
|
||||
| `<K>` | Crear un enlace simbólico que apunte a la entrada seleccionada actualmente | symlinK |
|
||||
| `<L>` | Recargar contenido del directorio / Borrar selección | List |
|
||||
| `<M>` | Seleccione un archivo | Mark |
|
||||
| `<N>` | Crear un nuevo archivo con el nombre proporcionado | New |
|
||||
| `<O|F4>` | Editar archivo | Open |
|
||||
| `<P>` | Open log panel | Panel |
|
||||
| `<Q|F10>` | Salir de termscp | Quit |
|
||||
| `<R|F6>` | Renombrar archivo | Rename |
|
||||
| `<S|F2>` | Guardar archivo como... | Save |
|
||||
| `<T>` | Sincronizar los cambios en la ruta seleccionada con el control remoto | Track |
|
||||
| `<U>` | Ir al directorio principal | Upper |
|
||||
| `<V|F3>` | Abrir archivo con el programa predeterminado | View |
|
||||
| `<W>` | Abrir archivo con el programa proporcionado | With |
|
||||
| `<X>` | Ejecutar un comando | eXecute |
|
||||
| `<Y>` | Alternar navegación sincronizada | sYnc |
|
||||
| `<Z>` | Cambiar ppermisos de archivo | |
|
||||
| `<CTRL+A>` | Seleccionar todos los archivos | |
|
||||
| `<CTRL+C>` | Abortar el proceso de transferencia de archivos | |
|
||||
| `<CTRL+T>` | Mostrar todas las rutas sincronizadas | Track |
|
||||
|
||||
### Trabaja en varios archivos 🥷
|
||||
|
||||
Puede optar por trabajar en varios archivos, seleccionándolos presionando `<M>`, para seleccionar el archivo actual, o presionando `<CTRL + A>`, que seleccionará todos los archivos en el directorio de trabajo.
|
||||
Una vez que un archivo está marcado para su selección, se mostrará con un `*` a la izquierda.
|
||||
Al trabajar en la selección, solo se procesará el archivo seleccionado para las acciones, mientras que el elemento resaltado actual se ignorará.
|
||||
También es posible trabajar en varios archivos desde el panel de resultados de búsqueda.
|
||||
Todas las acciones están disponibles cuando se trabaja con varios archivos, pero tenga en cuenta que algunas acciones funcionan de forma ligeramente diferente. Vamos a sumergirnos en:
|
||||
|
||||
- *Copy*: cada vez que copie un archivo, se le pedirá que inserte el nombre de destino. Cuando se trabaja con varios archivos, este nombre se refiere al directorio de destino donde se copiarán todos estos archivos.
|
||||
- *Rename*: igual que copiar, pero moverá archivos allí.
|
||||
- *Save as*: igual que copiar, pero los escribirá allí.
|
||||
|
||||
### Navegación sincronizada ⏲️
|
||||
|
||||
Cuando está habilitada, la navegación sincronizada le permitirá sincronizar la navegación entre los dos paneles.
|
||||
Esto significa que siempre que cambie el directorio de trabajo en un panel, la misma acción se reproducirá en el otro panel. Si desea habilitar la navegación sincronizada, simplemente presione `<Y>`; presione dos veces para deshabilitar. Mientras está habilitado, el estado de navegación sincronizada se informará en la barra de estado en "ON".
|
||||
|
||||
### Abierta y abierta con 🚪
|
||||
|
||||
Al abrir archivos con el comando Ver (`<V>`), se utilizará la aplicación predeterminada del sistema para el tipo de archivo. Para hacerlo, se utilizará el servicio del sistema operativo predeterminado, así que asegúrese de tener al menos uno de estos instalado en su sistema:
|
||||
|
||||
- Usuarios **Windows**: no tiene que preocuparse por eso, ya que la caja usará el comando `start`.
|
||||
- Usuarios **MacOS**: tampoco tiene que preocuparse, ya que la caja usará `open`, que ya está instalado en su sistema.
|
||||
- Usuarios **Linux**: uno de estos debe estar instalado
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- Usuarios **WSL**: *wslview* es obligatorio, debe instalar [wslu](https://github.com/wslutilities/wslu).
|
||||
|
||||
> Q: ¿Puedo editar archivos remotos usando el comando de vista?
|
||||
> A: No, al menos no directamente desde el "panel remoto". Primero debe descargarlo en un directorio local, eso se debe al hecho de que cuando abre un archivo remoto, el archivo se descarga en un directorio temporal, pero no hay forma de crear un observador para que el archivo verifique cuándo el programa utilizado para abrirlo estaba cerrado, por lo que termscp no puede saber cuándo ha terminado de editar el archivo.
|
||||
|
||||
---
|
||||
|
||||
## Marcadores ⭐
|
||||
|
||||
En termscp es posible guardar hosts favoritos, que luego se pueden cargar rápidamente desde el diseño principal de termscp.
|
||||
termscp también guardará los últimos 16 hosts a los que se conectó.
|
||||
Esta función le permite cargar todos los parámetros necesarios para conectarse a un determinado control remoto, simplemente seleccionando el marcador en la pestaña debajo del formulario de autenticación.
|
||||
|
||||
Los marcadores se guardarán, si es posible, en:
|
||||
|
||||
- `$HOME/.config/termscp/` en Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` en MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` en Windows
|
||||
|
||||
Solo para marcadores (esto no se aplicará a hosts recientes) también es posible guardar la contraseña utilizada para autenticarse. La contraseña no se guarda de forma predeterminada y debe especificarse a través del indicador al guardar un nuevo marcador.
|
||||
Si le preocupa la seguridad de la contraseña guardada para sus marcadores, lea el [capítulo siguiente 👀](#are-my-passwords-safe-).
|
||||
|
||||
Para crear un nuevo marcador, simplemente siga estos pasos:
|
||||
|
||||
1. Escriba en el formulario de autenticación los parámetros para conectarse a su servidor remoto
|
||||
2. Presionar `<CTRL + S>`
|
||||
3. Escriba el nombre que desea darle al marcador
|
||||
4. Elija si recordar la contraseña o no
|
||||
5. Presionar `<ENTER>`
|
||||
|
||||
siempre que desee utilizar la conexión previamente guardada, simplemente presione `<TAB>` para navegar a la lista de marcadores y cargue los parámetros del marcador en el formulario presionando `<ENTER>`.
|
||||
|
||||

|
||||
|
||||
### ¿Son seguras mis contraseñas? 😈
|
||||
|
||||
Seguro 😉.
|
||||
Como se dijo antes, los marcadores se guardan en su directorio de configuración junto con las contraseñas. Las contraseñas obviamente no son texto sin formato, están encriptadas con **AES-128**. ¿Esto los hace seguros? ¡Absolutamente! (excepto para usuarios de BSD y WSL 😢)
|
||||
|
||||
En **Windows**, **Linux** y **MacOS**, la clave utilizada para cifrar las contraseñas se almacena, si es posible (pero debería estar), respectivamente, en *Windows Vault*, en el *anillo de claves del sistema* y en el *Llavero*. Esto es realmente muy seguro y lo administra directamente su sistema operativo.
|
||||
|
||||
❗ Por favor, tenga en cuenta que si es un usuario de Linux, es mejor que lea el [capítulo siguiente 👀](#linux-keyring), ¡porque es posible que el llavero no esté habilitado o no sea compatible con su sistema!
|
||||
|
||||
En *BSD* y *WSL*, por otro lado, la clave utilizada para cifrar sus contraseñas se almacena en su disco (en `$HOME/.config/ termscp`). Entonces, todavía es posible recuperar la clave para descifrar las contraseñas. Afortunadamente, la ubicación de la clave garantiza que su clave no pueda ser leída por usuarios diferentes al suyo, pero sí, todavía no guardaría la contraseña para un servidor expuesto en Internet 😉.
|
||||
|
||||
#### Linux Keyring
|
||||
|
||||
A todos nos encanta Linux gracias a la libertad que ofrece a los usuarios. Básicamente, puede hacer lo que quiera como usuario de Linux, pero esto también tiene algunas desventajas, como el hecho de que a menudo no hay aplicaciones estándar en las diferentes distribuciones. Y esto también implica el llavero.
|
||||
Esto significa que en Linux puede que no haya un llavero instalado en su sistema. Desafortunadamente, la biblioteca que usamos para trabajar con el almacenamiento de claves requiere un servicio que exponga `org.freedesktop.secrets` en D-BUS y el peor hecho es que solo hay dos servicios que lo exponen.
|
||||
|
||||
- ❗ Si usa GNOME como entorno de escritorio (por ejemplo, usuarios de ubuntu), ya debería estar bien, ya que `gnome-keyring` ya proporciona el llavero y todo debería estar funcionando.
|
||||
- ❗ Para otros usuarios de entornos de escritorio, hay un buen programa que pueden usar para obtener un llavero que es [KeepassXC](https://keepassxc.org/), que utilizo en mi instalación de Manjaro (con KDE) y funciona bien. El único problema es que debe configurarlo para que se use junto con termscp (pero es bastante simple). Para comenzar con KeepassXC, lea más [aquí](#keepassxc-setup-por-termscp).
|
||||
- ❗ ¿Qué pasa si no desea instalar ninguno de estos servicios? Bueno, ¡no hay problema! **termscp seguirá funcionando como de costumbre**, pero guardará la clave en un archivo, como suele hacer para BSD y WSL.
|
||||
|
||||
##### KeepassXC setup por termscp
|
||||
|
||||
Siga estos pasos para configurar keepassXC para termscp:
|
||||
|
||||
1. Instalar KeepassXC
|
||||
2. Vaya a "tools" > "settings" en la barra de herramientas
|
||||
3. Seleccione "Secret service integration" y abilita "Enable KeepassXC freedesktop.org secret service integration"
|
||||
4. Cree una base de datos, si aún no tiene una: desde la barra de herramientas "Database" > "New database"
|
||||
5. Desde la barra de herramientas: "Database" > "Database settings"
|
||||
6. Seleccione "Secret service integration" y abilita "Expose entries under this group"
|
||||
7. Seleccione el grupo de la lista donde desea que se mantenga el secreto de termscp. Recuerde que este grupo puede ser utilizado por cualquier otra aplicación para almacenar secretos a través de DBUS.
|
||||
|
||||
---
|
||||
|
||||
## Configuración ⚙️
|
||||
|
||||
termscp admite algunos parámetros definidos por el usuario, que se pueden definir en la configuración.
|
||||
Underhood termscp tiene un archivo TOML y algunos otros directorios donde se guardarán todos los parámetros, pero no se preocupe, no tocará ninguno de estos archivos manualmente, ya que hice posible configurar termscp desde su interfaz de usuario por completo.
|
||||
|
||||
termscp, al igual que para los marcadores, solo requiere tener estas rutas accesibles:
|
||||
|
||||
- `$HOME/.config/termscp/` en Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` en MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` en Windows
|
||||
|
||||
Para acceder a la configuración, solo tiene que presionar `<CTRL + C>` desde el inicio de termscp.
|
||||
|
||||
Estos parámetros se pueden cambiar:
|
||||
|
||||
- **Text Editor**: l editor de texto a utilizar. Por defecto, termscp encontrará el editor predeterminado para usted; con esta opción puede forzar el uso de un editor (por ejemplo, `vim`). **También se admiten los editores de GUI**, a menos que hagan "nohup" del proceso principal.
|
||||
- **Default Protocol**: el protocolo predeterminado es el valor predeterminado para el protocolo de transferencia de archivos que se utilizará en termscp. Esto se aplica a la página de inicio de sesión y al argumento de la CLI de la dirección.
|
||||
- **Show Hidden Files**: seleccione si los archivos ocultos se mostrarán de forma predeterminada. Podrás decidir si mostrar o no archivos ocultos en tiempo de ejecución presionando "A" de todos modos.
|
||||
- **Check for updates**: si se establece en `yes`, termscp buscará la API de Github para comprobar si hay una nueva versión de termscp disponible.
|
||||
- **Prompt when replacing existing files?**: Si se establece en "sí", termscp le pedirá confirmación cada vez que una transferencia de archivo provoque la sustitución de un archivo existente en el host de destino.
|
||||
- **Group Dirs**: seleccione si los directorios deben agruparse o no en los exploradores de archivos. Si se selecciona `Display first`, los directorios se ordenarán usando el método configurado pero se mostrarán antes de los archivos, y viceversa si se selecciona`Display last`.
|
||||
- **Remote File formatter syntax**: sintaxis para mostrar información de archivo para cada archivo en el explorador remoto. Consulte [Formato del explorador de archivos](#formato-del-explorador-de-archivos).
|
||||
- **Local File formatter syntax**: sintaxis para mostrar información de archivo para cada archivo en el explorador local. Consulte [Formato del explorador de archivos](#formato-del-explorador-de-archivos).
|
||||
- **Enable notifications?**: Si se establece en "Sí", se mostrarán las notificaciones.
|
||||
- **Notifications: minimum transfer size**: si el tamaño de la transferencia es mayor o igual que el valor especificado, se mostrarán notificaciones de transferencia. Los valores aceptados están en formato `{UNSIGNED} B/KB/MB/GB/TB/PB`
|
||||
- **SSH configuration path**: Configure el archivo de configuración SSH para usar al conectarse a un servidor SCP / SFTP. Si no se configura (está vacío), no se utilizará ningún archivo. Puede especificar una ruta que comience con `~` para indicar la ruta de inicio (por ejemplo, `~/.ssh/config`). Se especifican los parámetros soportados [AQUI](https://github.com/veeso/ssh2-config#exposed-attributes).
|
||||
|
||||
### SSH Key Storage 🔐
|
||||
|
||||
Junto con la configuración, termscp también proporciona una característica **esencial** para **clientes SFTP / SCP**: el almacenamiento de claves SSH.
|
||||
|
||||
Puede acceder al almacenamiento de claves SSH, desde la configuración pasando a la pestaña `Claves SSH`, una vez allí puede:
|
||||
|
||||
- **Agregar una nueva clave**: simplemente presione `<CTRL + N>` y se le pedirá que cree una nueva clave. Proporcione el nombre de host / dirección IP y el nombre de usuario asociado a la clave y finalmente se abrirá un editor de texto: pegue la clave ssh **PRIVATE** en el editor de texto, guarde y salga.
|
||||
- **Eliminar una clave existente**: simplemente presione `<DEL>` o `<CTRL + E>` en la clave que desea eliminar, para eliminar persistentemente la clave de termscp.
|
||||
- **Editar una clave existente**: simplemente presione `<ENTER>` en la clave que desea editar, para cambiar la clave privada.
|
||||
|
||||
> Q: Mi clave privada está protegida con contraseña, ¿puedo usarla?
|
||||
> A: Por supuesto que puede. La contraseña proporcionada para la autenticación en termscp es válida tanto para la autenticación de nombre de usuario / contraseña como para la autenticación de clave RSA.
|
||||
|
||||
### Formato del explorador de archivos
|
||||
|
||||
Es posible a través de la configuración definir un formato personalizado para el explorador de archivos. Esto es posible tanto para el host local como para el remoto, por lo que puede tener dos sintaxis diferentes en uso. Estos campos, con el nombre `File formatter syntax (local)` y `File formatter syntax (remote)` definirán cómo se mostrarán las entradas del archivo en el explorador de archivos.
|
||||
La sintaxis del formateador es la siguiente `{KEY1} ... {KEY2:LENGTH} ... {KEY3:LENGTH:EXTRA} {KEYn} ...`.
|
||||
Cada clave entre corchetes se reemplazará con el atributo relacionado, mientras que todo lo que esté fuera de los corchetes se dejará sin cambios.
|
||||
|
||||
- El nombre de la clave es obligatorio y debe ser una de las claves siguientes
|
||||
- La longitud describe la longitud reservada para mostrar el campo. Los atributos estáticos no admiten esto (GROUP, PEX, SIZE, USER)
|
||||
- Extra es compatible solo con algunos parámetros y es una opción adicional. Consulte las claves para comprobar si se admite extra.
|
||||
|
||||
Estas son las claves admitidas por el formateador:
|
||||
|
||||
- `ATIME`: Hora del último acceso (con la sintaxis predeterminada`%b %d %Y %H:%M`); Se puede proporcionar un extra como la sintaxis de tiempo (por ejemplo, "{ATIME: 8:% H:% M}")
|
||||
- `CTIME`: Hora de creación (con sintaxis`%b %d %Y %H:%M`); Se puede proporcionar un extra como sintaxis de tiempo (p. Ej., `{CTIME:8:%H:%M}`)
|
||||
- `GROUP`: Grupo propietario
|
||||
- `MTIME`: Hora del último cambio (con sintaxis`%b %d %Y %H:%M`); Se puede proporcionar extra como sintaxis de tiempo (p. Ej., `{MTIME: 8:% H:% M}`)
|
||||
- `NAME`: nombre de archivo (Las carpetas entre la raíz y los primeros antepasados se eliminan si es más largo que LENGTH)
|
||||
- `PATH`: Percorso completo de archivo (Las carpetas entre la raíz y los primeros antepasados se eliminan si es màs largo que LENGHT)
|
||||
- `PEX`: permisos de archivo (formato UNIX)
|
||||
- `SIZE`: Tamaño del archivo (se omite para directorios)
|
||||
- `SYMLINK`: Symlink (si existe` -> {FILE_PATH} `)
|
||||
- `USER`: Usuario propietario
|
||||
|
||||
Si se deja vacío, se utilizará la sintaxis del formateador predeterminada: `{NAME:24} {PEX} {USER} {SIZE} {MTIME:17:%b %d %Y %H:%M}`
|
||||
|
||||
---
|
||||
|
||||
## Temas 🎨
|
||||
|
||||
Termscp le ofrece una característica asombrosa: la posibilidad de configurar los colores para varios componentes de la aplicación.
|
||||
Si desea personalizar termscp, hay dos formas disponibles de hacerlo:
|
||||
|
||||
- Desde el **menú de configuración**
|
||||
- Importando un **archivo de tema**
|
||||
|
||||
Para crear su propia personalización desde termscp, todo lo que tiene que hacer es ingresar a la configuración desde la actividad de autenticación, presionando `<CTRL + C>` y luego `<TAB>` dos veces. Deberías haberte movido ahora al panel de `temas`.
|
||||
|
||||
Aquí puede moverse con `<UP>` y `<DOWN>` para cambiar el estilo que desea cambiar, como se muestra en el siguiente gif:
|
||||
|
||||

|
||||
|
||||
termscp admite la sintaxis tradicional hexadecimal explícita (`#rrggbb`) y rgb `rgb(r, g, b)` para proporcionar colores, pero se aceptan también **[colores css](https://www.w3schools.com/cssref/css_colors.asp)** (como `crimson`) 😉. También hay un teclado especial que es `Default`. Predeterminado significa que el color utilizado será el color de primer plano o de fondo predeterminado según la situación (primer plano para textos y líneas, fondo para bien, adivinen qué).
|
||||
|
||||
Como se dijo antes, también puede importar archivos de temas. Puede inspirarse o utilizar directamente uno de los temas proporcionados junto con termscp, ubicado en el directorio `themes/` de este repositorio e importarlos ejecutando termscp como `termscp -t <theme_file>`. Si todo estuvo bien, debería decirle que el tema se ha importado correctamente.
|
||||
|
||||
### Mi tema no se carga 😱
|
||||
|
||||
Esto probablemente se deba a una actualización reciente que ha roto el tema. Siempre que agrego una nueva clave a los temas, el tema guardado no se carga. Para solucionar este problema, existen dos soluciones realmente rápidas:
|
||||
|
||||
1. Recargar tema: cada vez que publique una actualización, también parchearé los temas "oficiales", por lo que solo tiene que descargarlo del repositorio nuevamente y volver a importar el tema a través de la opción `-t`
|
||||
|
||||
```sh
|
||||
termscp -t <theme.toml>
|
||||
```
|
||||
|
||||
2. Corrija su tema: si está utilizando un tema personalizado, puede editarlo a través de `vim` y agregar la clave que falta. El tema se encuentra en `$CONFIG_DIR/termscp/theme.toml` donde `$CONFIG_DIR` es:
|
||||
|
||||
- FreeBSD/GNU-Linux: `$HOME/.config/`
|
||||
- MacOs: `$HOME/Library/Application Support`
|
||||
- Windows: `%appdata%`
|
||||
|
||||
❗ Las claves que faltan se informan en el CAMBIO en `BREAKING CHANGES` para la versión que acaba de instalar.
|
||||
|
||||
### Estilos 💈
|
||||
|
||||
Puede encontrar en la tabla siguiente la descripción de cada campo de estilo.
|
||||
Tenga en cuenta que **los estilos no se aplicarán a la página de configuración**, para que sea siempre accesible en caso de que lo estropee todo
|
||||
|
||||
#### Authentication page
|
||||
|
||||
| Key | Description |
|
||||
|----------------|------------------------------------------|
|
||||
| auth_address | Color of the input field for IP address |
|
||||
| auth_bookmarks | Color of the bookmarks panel |
|
||||
| auth_password | Color of the input field for password |
|
||||
| auth_port | Color of the input field for port number |
|
||||
| auth_protocol | Color of the radio group for protocol |
|
||||
| auth_recents | Color of the recents panel |
|
||||
| auth_username | Color of the input field for username |
|
||||
|
||||
#### Transfer page
|
||||
|
||||
| Key | Description |
|
||||
|--------------------------------------|---------------------------------------------------------------------------|
|
||||
| transfer_local_explorer_background | Background color of localhost explorer |
|
||||
| transfer_local_explorer_foreground | Foreground coloor of localhost explorer |
|
||||
| transfer_local_explorer_highlighted | Border and highlighted color for localhost explorer |
|
||||
| transfer_remote_explorer_background | Background color of remote explorer |
|
||||
| transfer_remote_explorer_foreground | Foreground coloor of remote explorer |
|
||||
| transfer_remote_explorer_highlighted | Border and highlighted color for remote explorer |
|
||||
| transfer_log_background | Background color for log panel |
|
||||
| transfer_log_window | Window color for log panel |
|
||||
| transfer_progress_bar_partial | Partial progress bar color |
|
||||
| transfer_progress_bar_total | Total progress bar color |
|
||||
| transfer_status_hidden | Color for status bar "hidden" label |
|
||||
| transfer_status_sorting | Color for status bar "sorting" label; applies also to file sorting dialog |
|
||||
| transfer_status_sync_browsing | Color for status bar "sync browsing" label |
|
||||
|
||||
#### Misc
|
||||
|
||||
These styles applie to different part of the application.
|
||||
|
||||
| Key | Description |
|
||||
|-------------------|---------------------------------------------|
|
||||
| misc_error_dialog | Color for error messages |
|
||||
| misc_info_dialog | Color for info dialogs |
|
||||
| misc_input_dialog | Color for input dialogs (such as copy file) |
|
||||
| misc_keys | Color of text for key strokes |
|
||||
| misc_quit_dialog | Color for quit dialogs |
|
||||
| misc_save_dialog | Color for save dialogs |
|
||||
| misc_warn_dialog | Color for warn dialogs |
|
||||
|
||||
---
|
||||
|
||||
## Text Editor ✏
|
||||
|
||||
termscp tiene, como habrás notado, muchas características, una de ellas es la posibilidad de ver y editar archivos de texto. No importa si el archivo está ubicado en el host local o en el host remoto, termscp brinda la posibilidad de abrir un archivo en su editor de texto favorito.
|
||||
En caso de que el archivo esté ubicado en un host remoto, el archivo se descargará primero en su directorio de archivos temporales y luego, **solo** si se realizaron cambios en el archivo, se volverá a cargar en el host remoto. termscp comprueba si realizó cambios en el archivo verificando la última hora de modificación del archivo.
|
||||
|
||||
> ❗ Just a reminder: **you can edit only textual file**; binary files are not supported.
|
||||
|
||||
---
|
||||
|
||||
## Logging 🩺
|
||||
|
||||
termscp escribe un archivo de registro para cada sesión, que se escribe en
|
||||
|
||||
- `$HOME/.cache/termscp/termscp.log` en Linux/BSD
|
||||
- `$HOME/Library/Caches/termscp/termscp.log` en MacOs
|
||||
- `FOLDERID_LocalAppData\termscp\termscp.log` en Windows
|
||||
|
||||
el registro no se rotará, sino que se truncará después de cada lanzamiento de termscp, por lo que si desea informar un problema y desea adjuntar su archivo de registro, recuerde guardar el archivo de registro en un lugar seguro antes de usar termscp de nuevo.
|
||||
El registro por defecto informa en el nivel *INFO*, por lo que no es muy detallado.
|
||||
|
||||
Si desea enviar un problema, por favor, si puede, reproduzca el problema con el nivel establecido en "TRACE", para hacerlo, inicie termscp con
|
||||
la opción CLI `-D`.
|
||||
|
||||
Sé que es posible que tenga algunas preguntas sobre los archivos de registro, así que hice una especie de Q/A:
|
||||
|
||||
> No quiero el registro, ¿puedo apagarlo?
|
||||
|
||||
Sí tu puedes. Simplemente inicie termscp con la opción `-q o --quiet`. Puede alias termscp para que sea persistente. Recuerde que el registro se usa para diagnosticar problemas, por lo que, dado que detrás de cada proyecto de código abierto, siempre debe haber este tipo de ayuda mutua, mantener los archivos de registro puede ser su forma de respaldar el proyecto 😉.
|
||||
|
||||
> ¿Es seguro el registro?
|
||||
|
||||
Si le preocupa la seguridad, el archivo de registro no contiene ninguna contraseña simple, así que no se preocupe y expone la misma información que informa el archivo hermano `marcadores`.
|
||||
|
||||
## Notificaciones 📫
|
||||
|
||||
Termscp enviará notificaciones de escritorio para este tipo de eventos:
|
||||
|
||||
- en **Transferencia completada**: la notificación se enviará una vez que la transferencia se haya completado con éxito.
|
||||
- ❗ La notificación se mostrará solo si el tamaño total de la transferencia es al menos el `Notifications: minimum transfer size` especificado en la configuración.
|
||||
- en **Transferencia fallida**: la notificación se enviará una vez que la transferencia haya fallado debido a un error.
|
||||
- ❗ La notificación se mostrará solo si el tamaño total de la transferencia es al menos el `Notifications: minimum transfer size` especificado en la configuración.
|
||||
- en **Actualización disponible**: siempre que haya una nueva versión de termscp disponible, se mostrará una notificación.
|
||||
- en **Actualización instalada**: siempre que se haya instalado una nueva versión de termscp, se mostrará una notificación.
|
||||
- en **Actualización fallida**: siempre que falle la instalación de la actualización, se mostrará una notificación.
|
||||
|
||||
❗ Si prefiere mantener las notificaciones desactivadas, puede simplemente ingresar a la configuración y configurar `Enable notifications?` En `No` 😉.
|
||||
❗ Si desea cambiar el tamaño mínimo de transferencia para mostrar notificaciones, puede cambiar el valor en la configuración con la tecla `Notifications: minimum transfer size` y configurarlo como mejor le convenga 🙂.
|
||||
|
||||
## Observador de archivos 🔭
|
||||
|
||||
El observador de archivos le permite configurar una lista de rutas para sincronizar con los hosts remotos.
|
||||
Esto significa que siempre que se detecte un cambio en el sistema de archivos local en la ruta sincronizada, el cambio se informará automáticamente a la ruta del host remoto configurado, dentro de los 5 segundos.
|
||||
|
||||
Puede establecer tantas rutas para sincronizar como prefiera:
|
||||
|
||||
1. Coloque el cursor en el explorador local en el directorio/archivo que desea mantener sincronizado
|
||||
2. Vaya al directorio en el que desea que se informen los cambios en el host remoto
|
||||
3. Presione `<T>`
|
||||
4. Responda `<YES>` a la ventana emergente de radio
|
||||
|
||||
Para dejar de mirar, simplemente presione `<T>` en la ruta sincronizada local (o en cualquiera de sus subcarpetas)
|
||||
O simplemente puede presionar `<CTRL + T>` y presionar `<ENTER>` en la ruta sincronizada que desea dejar de ver.
|
||||
|
||||
Estos cambios se informarán al host remoto:
|
||||
|
||||
- Nuevos archivos, cambios de archivos
|
||||
- Archivo movido / renombrado
|
||||
- Archivo eliminado/desvinculado
|
||||
|
||||
> ❗ El vigilante trabaja solo en una dirección (local > remota). NO es posible sincronizar automáticamente los cambios de remoto a local.
|
||||
@@ -1,291 +0,0 @@
|
||||
# termscp
|
||||
|
||||
<p align="center">
|
||||
<img src="/assets/images/termscp.svg" width="256" height="256" />
|
||||
</p>
|
||||
|
||||
<p align="center">~ Un file transfer de terminal riche en fonctionnalités ~</p>
|
||||
<p align="center">
|
||||
<a href="https://termscp.veeso.dev" target="_blank">Site internet</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#get-started" target="_blank">Installation</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#user-manual" target="_blank">Manuel de l'Utilisateur</a>
|
||||
</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/gb.png"
|
||||
alt="English"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/de/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/de.png"
|
||||
alt="Deutsch"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/es/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/es.png"
|
||||
alt="Español"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/fr/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/fr.png"
|
||||
alt="Français"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/it/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/it.png"
|
||||
alt="Italiano"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="/docs/zh-CN/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/cn.png"
|
||||
alt="简体中文"
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
<p align="center">Développé par <a href="https://veeso.dev/" target="_blank">@veeso</a></p>
|
||||
<p align="center">Version actuelle: 0.12.3 (06/10/2023)</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://opensource.org/licenses/MIT"
|
||||
><img
|
||||
src="https://img.shields.io/badge/License-MIT-teal.svg"
|
||||
alt="License-MIT"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/stargazers"
|
||||
><img
|
||||
src="https://img.shields.io/github/stars/veeso/termscp.svg"
|
||||
alt="Repo stars"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/d/termscp.svg"
|
||||
alt="Downloads counter"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/v/termscp.svg"
|
||||
alt="Latest version"
|
||||
/></a>
|
||||
<a href="https://ko-fi.com/veeso">
|
||||
<img
|
||||
src="https://img.shields.io/badge/donate-ko--fi-red"
|
||||
alt="Ko-fi"
|
||||
/></a>
|
||||
</p>
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Linux/badge.svg"
|
||||
alt="Linux CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/MacOS/badge.svg"
|
||||
alt="MacOS CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Windows/badge.svg"
|
||||
alt="Windows CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/FreeBSD/badge.svg"
|
||||
alt="FreeBSD CI"
|
||||
/></a>
|
||||
<a href="https://coveralls.io/github/veeso/termscp"
|
||||
><img
|
||||
src="https://coveralls.io/repos/github/veeso/termscp/badge.svg"
|
||||
alt="Coveralls"
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
---
|
||||
|
||||
## À propos des termscp 🖥
|
||||
|
||||
Termscp est un file transfer et explorateur de fichiers de terminal riche en fonctionnalités, avec support pour SCP/SFTP/FTP/S3. Essentiellement c'est une utilitaire terminal avec une TUI pour se connecter à un serveur distant pour télécharger de fichiers et interagir avec le système de fichiers local. Il est compatible avec **Linux**, **MacOS**, **FreeBSD** et **Windows**.
|
||||
|
||||

|
||||
|
||||
---
|
||||
|
||||
## Fonctionnalités 🎁
|
||||
|
||||
- 📁 Différents protocoles de communication
|
||||
- **SFTP**
|
||||
- **SCP**
|
||||
- **FTP** et **FTPS**
|
||||
- **S3**
|
||||
- **SMB**
|
||||
- 🖥 Explorer et opérer sur le système de fichiers distant et local avec une interface utilisateur pratique.
|
||||
- Créer, supprimer, renommer, rechercher, afficher et modifier des fichiers
|
||||
- ⭐ Connectez-vous à vos hôtes préférés via des signets et des connexions récentes.
|
||||
- 📝 Affichez et modifiez des fichiers avec vos applications préférées
|
||||
- 💁 Authentication SFTP/SCP avec des clés SSH et nom/mot de passe
|
||||
- 🐧 Compatible avec Windows, Linux, FreeBSD et MacOS
|
||||
- 🎨 Faites en vôtre !
|
||||
- thèmes
|
||||
- format d'explorateur de fichiers personnalisé
|
||||
- éditeur de texte personnalisable
|
||||
- tri de fichiers personallisable
|
||||
- et bien d'autres paramètres...
|
||||
- 📫 Recevez une notification quande un gros fichier est télécharger.
|
||||
- 🔭 Gardez les modifications de fichiers synchronisées avec l'hôte distant
|
||||
- 🔐 Enregistre tes mots de passe dans le key vault du systeme.
|
||||
- 🦀 Rust-powered
|
||||
- 👀 Développé en gardant un œil sur les performances
|
||||
- 🦄 Mises à jour fréquentes
|
||||
|
||||
---
|
||||
|
||||
## Pour commencer 🚀
|
||||
|
||||
Si tu envisage d'installer termscp, je veux te remercier 💜 ! J'espère que tu vas apprécier termscp !
|
||||
Si tu veux contribuer à ce projet, n'oublié pas de consulter notre [guide de contribution](../../CONTRIBUTING.md).
|
||||
|
||||
Si tu es un utilisateur Linux, FreeBSD ou MacOS ce simple shell script installera termscp sur te système en un seule commande:
|
||||
|
||||
```sh
|
||||
curl -sSLf http://get-termscp.veeso.dev | sh
|
||||
```
|
||||
|
||||
tandis que si tu es un utilisateur Windows, tu peux installer termscp avec [Chocolatey](https://chocolatey.org/):
|
||||
|
||||
```sh
|
||||
choco install termscp
|
||||
```
|
||||
|
||||
Pour plus d'informations sur les autres méthodes d'installation, veuillez visiter [termscp.veeso.dev](https://termscp.veeso.dev/termscp/#get-started).
|
||||
|
||||
⚠️ Si tu cherche comme de mettre à jour termscp, tu dois exécuter cette commande dans le terminal: `(sudo) termscp --update` ⚠️
|
||||
|
||||
### Requis ❗
|
||||
|
||||
- **Linux** users:
|
||||
- libdbus-1
|
||||
- pkg-config
|
||||
- libsmbclient
|
||||
- **FreeBSD** or, **NetBSD** users:
|
||||
- dbus
|
||||
- pkgconf
|
||||
- libsmbclient
|
||||
|
||||
### Requis facultatives ✔️
|
||||
|
||||
Ces requis ne sont pas obligatoires d'exécuter termscp, mais seulement à toutes ses fonctionnalités
|
||||
|
||||
- utilisateurs **Linux/FreeBSD**:
|
||||
- Pour **ouvrir** les fichiers via `V` (au moins un de ces)
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- utilisateurs **Linux**:
|
||||
- Un keyring manager: lire plus dans le [manuel d'utilisateur](man.md#linux-keyring)
|
||||
- utilisateurs **WSL**
|
||||
- Pour **ouvrir** les fichiers via `V` (au moins un de ces)
|
||||
- [wslu](https://github.com/wslutilities/wslu)
|
||||
|
||||
---
|
||||
|
||||
## Me soutenir ☕
|
||||
|
||||
Si tu aime termscp et que tu aimerais voir le projet grandir et s'améliorer, voudrais considérer un petit don pour me soutenir
|
||||
|
||||
Tu peux faire un don avec l'une de ces plateformes:
|
||||
|
||||
[](https://ko-fi.com/veeso)
|
||||
[](https://www.paypal.me/chrisintin)
|
||||
|
||||
---
|
||||
|
||||
## Manuel d'utilisateur et Documentation 📚
|
||||
|
||||
Le manuel d'utilisateur peut être trouvé sur le [site de termscp](https://termscp.veeso.dev/termscp/#user-manual) ou sur [Github](man.md).
|
||||
|
||||
La documentation peut être trouvé sur Rust Docs <https://docs.rs/termscp>
|
||||
|
||||
---
|
||||
|
||||
## Contribution et enjeux 🤝🏻
|
||||
|
||||
Les contributions, les rapports de bugs, les nouvelles fonctionnalités et les questions sont les bienvenus ! 😉
|
||||
Si tu ai des questions ou des préoccupations, ou si tu souhaite suggérer une nouvelle fonctionnalité, ou si tu souhaite simplement améliorer les conditions de termscp, n'hésite pas à ouvrir un problème ou un PR.
|
||||
|
||||
Veuillez suivre [nos directives de contribution](../../CONTRIBUTING.md)
|
||||
|
||||
---
|
||||
|
||||
## Journal des modifications ⏳
|
||||
|
||||
Afficher le journal des modifications [ICI](../../CHANGELOG.md)
|
||||
|
||||
---
|
||||
|
||||
## Powered by 💪
|
||||
|
||||
termscp est soutenu par ces projets impressionnants:
|
||||
|
||||
- [bytesize](https://github.com/hyunsik/bytesize)
|
||||
- [crossterm](https://github.com/crossterm-rs/crossterm)
|
||||
- [edit](https://github.com/milkey-mouse/edit)
|
||||
- [keyring-rs](https://github.com/hwchen/keyring-rs)
|
||||
- [open-rs](https://github.com/Byron/open-rs)
|
||||
- [rpassword](https://github.com/conradkleinespel/rpassword)
|
||||
- [rust-s3](https://github.com/durch/rust-s3)
|
||||
- [self_update](https://github.com/jaemk/self_update)
|
||||
- [ssh2-rs](https://github.com/alexcrichton/ssh2-rs)
|
||||
- [suppaftp](https://github.com/veeso/suppaftp)
|
||||
- [tui-rs](https://github.com/fdehau/tui-rs)
|
||||
- [tui-realm](https://github.com/veeso/tui-realm)
|
||||
- [whoami](https://github.com/libcala/whoami)
|
||||
- [wildmatch](https://github.com/becheran/wildmatch)
|
||||
|
||||
---
|
||||
|
||||
## Gallerie 🎬
|
||||
|
||||
> Termscp Home
|
||||
|
||||

|
||||
|
||||
> Bookmarks
|
||||
|
||||

|
||||
|
||||
> Setup
|
||||
|
||||

|
||||
|
||||
> Text editor
|
||||
|
||||

|
||||
|
||||
---
|
||||
|
||||
## Licence 📃
|
||||
|
||||
termscp est sous licence MIT.
|
||||
|
||||
Vous pouvez lire l'intégralité de la licence [ICI](../../LICENSE)
|
||||
@@ -1,558 +0,0 @@
|
||||
# User manual 🎓
|
||||
|
||||
- [User manual 🎓](#user-manual-)
|
||||
- [Usage ❓](#usage-)
|
||||
- [Argument d'adresse 🌎](#argument-dadresse-)
|
||||
- [Argument d'adresse AWS S3](#argument-dadresse-aws-s3)
|
||||
- [Argument d'adresse SMB](#argument-dadresse-smb)
|
||||
- [Comment le mot de passe peut être fourni 🔐](#comment-le-mot-de-passe-peut-être-fourni-)
|
||||
- [S3 paramètres de connexion](#s3-paramètres-de-connexion)
|
||||
- [Identifiants S3 🦊](#identifiants-s3-)
|
||||
- [Explorateur de fichiers 📂](#explorateur-de-fichiers-)
|
||||
- [Raccourcis clavier ⌨](#raccourcis-clavier-)
|
||||
- [Travailler sur plusieurs fichiers 🥷](#travailler-sur-plusieurs-fichiers-)
|
||||
- [Navigation synchronisée ⏲️](#navigation-synchronisée-️)
|
||||
- [Ouvrir et ouvrir avec 🚪](#ouvrir-et-ouvrir-avec-)
|
||||
- [Signets ⭐](#signets-)
|
||||
- [Mes mots de passe sont-ils sûrs 😈](#mes-mots-de-passe-sont-ils-sûrs-)
|
||||
- [Linux Keyring](#linux-keyring)
|
||||
- [Configuration de KeepassXC pour termscp](#configuration-de-keepassxc-pour-termscp)
|
||||
- [Configuration ⚙️](#configuration-️)
|
||||
- [SSH Key Storage 🔐](#ssh-key-storage-)
|
||||
- [Format de l'explorateur de fichiers](#format-de-lexplorateur-de-fichiers)
|
||||
- [Thèmes 🎨](#thèmes-)
|
||||
- [Mon thème ne se charge pas 😱](#mon-thème-ne-se-charge-pas-)
|
||||
- [Modes 💈](#modes-)
|
||||
- [Authentication page](#authentication-page)
|
||||
- [Transfer page](#transfer-page)
|
||||
- [Misc](#misc)
|
||||
- [Éditeur de texte ✏](#éditeur-de-texte-)
|
||||
- [Fichier Journal 🩺](#fichier-journal-)
|
||||
- [Notifications 📫](#notifications-)
|
||||
- [Observateur de fichiers 🔭](#observateur-de-fichiers-)
|
||||
|
||||
## Usage ❓
|
||||
|
||||
termscp peut être démarré avec les options suivantes :
|
||||
|
||||
`termscp [options]... [protocol://user@address:port:wrkdir] [local-wrkdir]`
|
||||
|
||||
ou
|
||||
|
||||
`termscp [options]... -b [bookmark-name] [local-wrkdir]`
|
||||
|
||||
- `-P, --password <password>` si l'adresse est fournie, le mot de passe sera cet argument
|
||||
- `-b, --address-as-bookmark` résoudre l'argument d'adresse en tant que nom de signet
|
||||
- `-c, --config` Ouvrir termscp à partir de la page de configuration
|
||||
- `-q, --quiet` Désactiver la journalisation
|
||||
- `-t, --theme <path>` Importer le thème spécifié
|
||||
- `-u, --update` Mettre à jour termscp vers la dernière version
|
||||
- `-v, --version` Imprimer les informations sur la version
|
||||
- `-h, --help` Imprimer la page d'aide
|
||||
|
||||
termscp peut être démarré dans deux modes différents, si aucun argument supplémentaire n'est fourni, termscp affichera le formulaire d'authentification, où l'utilisateur pourra fournir les paramètres requis pour se connecter au pair distant.
|
||||
|
||||
Alternativement, l'utilisateur peut fournir une adresse comme argument pour ignorer le formulaire d'authentification et démarrer directement la connexion au serveur distant.
|
||||
|
||||
Si l'argument d'adresse est fourni, vous pouvez également fournir le répertoire de démarrage de l'hôte local
|
||||
|
||||
### Argument d'adresse 🌎
|
||||
|
||||
L'argument adresse a la syntaxe suivante :
|
||||
|
||||
```txt
|
||||
[protocole://][nom-utilisateur@]<adresse>[:port][:wrkdir]
|
||||
```
|
||||
|
||||
Voyons un exemple de cette syntaxe particulière, car elle est très confortable et vous allez probablement l'utiliser à la place de l'autre...
|
||||
|
||||
- Se connecter en utilisant le protocole par défaut (*défini dans la configuration*) à 192.168.1.31, le port s'il n'est pas fourni est par défaut pour le protocole sélectionné (dans ce cas dépend de votre configuration) ; nom d'utilisateur est le nom de l'utilisateur actuel
|
||||
|
||||
```sh
|
||||
termscp 192.168.1.31
|
||||
```
|
||||
|
||||
- Se connecter en utilisant le protocole par défaut (*défini dans la configuration*) à 192.168.1.31 ; le nom d'utilisateur est "root"
|
||||
|
||||
```sh
|
||||
termscp root@192.168.1.31
|
||||
```
|
||||
|
||||
- Se connecter en utilisant scp à 192.168.1.31, le port est 4022 ; le nom d'utilisateur est "omar"
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022
|
||||
```
|
||||
|
||||
- Se connecter en utilisant scp à 192.168.1.31, le port est 4022 ; le nom d'utilisateur est "omar". Vous commencerez dans le répertoire `/tmp`
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022:/tmp
|
||||
```
|
||||
|
||||
#### Argument d'adresse AWS S3
|
||||
|
||||
Aws S3 a une syntaxe différente pour l'argument d'adresse CLI, pour des raisons évidentes, mais j'ai réussi à le garder le plus similaire possible à l'argument d'adresse générique :
|
||||
|
||||
```txt
|
||||
s3://<bucket-name>@<region>[:profile][:/wrkdir]
|
||||
```
|
||||
|
||||
e.g.
|
||||
|
||||
```txt
|
||||
s3://buckethead@eu-central-1:default:/assets
|
||||
```
|
||||
|
||||
#### Argument d'adresse SMB
|
||||
|
||||
SMB a une syntaxe différente pour l'argument d'adresse CLI, qui est différente que vous soyez sur Windows ou sur d'autres systèmes :
|
||||
|
||||
syntaxe **Windows**:
|
||||
|
||||
```txt
|
||||
\\[username@]<server-name>\<share>[\path\...]
|
||||
```
|
||||
|
||||
syntaxe **Other systems**:
|
||||
|
||||
```txt
|
||||
smb://[username@]<server-name>[:port]/<share>[/path/.../]
|
||||
```
|
||||
|
||||
|
||||
#### Comment le mot de passe peut être fourni 🔐
|
||||
|
||||
Vous avez probablement remarqué que, lorsque vous fournissez l'adresse comme argument, il n'y a aucun moyen de fournir le mot de passe.
|
||||
Le mot de passe peut être fourni de 3 manières lorsque l'argument d'adresse est fourni :
|
||||
|
||||
- `-P, --password` option : utilisez simplement cette option CLI en fournissant le mot de passe. Je déconseille fortement cette méthode, car elle n'est pas sécurisée (puisque vous pouvez conserver le mot de passe dans l'historique du shell)
|
||||
- Avec `sshpass`: vous pouvez fournir un mot de passe via `sshpass`, par ex. `sshpass -f ~/.ssh/topsecret.key termscp cvisintin@192.168.1.31`
|
||||
- Il vous sera demandé : si vous n'utilisez aucune des méthodes précédentes, le mot de passe vous sera demandé, comme c'est le cas avec les outils plus classiques tels que `scp`, `ssh`, etc.
|
||||
|
||||
---
|
||||
|
||||
## S3 paramètres de connexion
|
||||
|
||||
Ces paramètres sont requis pour se connecter à aws s3 et à d'autres serveurs compatibles s3 :
|
||||
|
||||
- AWS S3:
|
||||
- **bucket name**
|
||||
- **region**
|
||||
- *profile* (si non fourni : "par défaut")
|
||||
- *access key* (sauf si public)
|
||||
- *secret access key* (sauf si public)
|
||||
- *security token* (si nécessaire)
|
||||
- *session token* (si nécessaire)
|
||||
- new path style: **NO**
|
||||
- Autres points de terminaison S3:
|
||||
- **bucket name**
|
||||
- **endpoint**
|
||||
- *access key* (sauf si public)
|
||||
- *secret access key* (sauf si public)
|
||||
- new path style: **YES**
|
||||
|
||||
### Identifiants S3 🦊
|
||||
|
||||
Afin de vous connecter à un compartiment Aws S3, vous devez évidemment fournir des informations d'identification.
|
||||
Il existe essentiellement trois manières d'y parvenir.
|
||||
Voici donc les moyens de fournir les informations d'identification pour s3 :
|
||||
|
||||
1. Authentication form:
|
||||
1. Vous pouvez fournir le `access_key` (devrait être obligatoire), le `secret_access_key` (devrait être obligatoire), `security_token` et le `session_token`
|
||||
2. Si vous enregistrez la connexion s3 en tant que signet, ces informations d'identification seront enregistrées en tant que chaîne AES-256/BASE64 cryptée dans votre fichier de signets (à l'exception du jeton de sécurité et du jeton de session qui sont censés être des informations d'identification temporaires).
|
||||
2. Utilisez votre fichier d'informations d'identification : configurez simplement l'AWS cli via `aws configure` et vos informations d'identification doivent déjà se trouver dans `~/.aws/credentials`. Si vous utilisez un profil différent de "default", fournissez-le simplement dans le champ profile du formulaire d'authentification.
|
||||
3. **Variables d'environnement** : vous pouvez toujours fournir vos informations d'identification en tant que variables d'environnement. Gardez à l'esprit que ces informations d'identification **remplaceront toujours** les informations d'identification situées dans le fichier « credentials ». Voir comment configurer l'environnement ci-dessous :
|
||||
|
||||
Ceux-ci devraient toujours être obligatoires:
|
||||
|
||||
- `AWS_ACCESS_KEY_ID`: aws access key ID (commence généralement par `AKIA...`)
|
||||
- `AWS_SECRET_ACCESS_KEY`: la secret access key
|
||||
|
||||
Au cas où vous auriez configuré une sécurité renforcée, vous *pourriez* également en avoir besoin :
|
||||
|
||||
- `AWS_SECURITY_TOKEN`: security token
|
||||
- `AWS_SESSION_TOKEN`: session token
|
||||
|
||||
⚠️ Vos identifiants sont en sécurité : les termscp ne manipuleront pas ces valeurs directement ! Vos identifiants sont directement consommés par la caisse **s3**.
|
||||
Si vous avez des inquiétudes concernant la sécurité, veuillez contacter l'auteur de la bibliothèque sur [Github](https://github.com/durch/rust-s3) ⚠️
|
||||
|
||||
---
|
||||
|
||||
## Explorateur de fichiers 📂
|
||||
|
||||
Lorsque nous nous référons aux explorateurs de fichiers en termscp, nous nous référons aux panneaux que vous pouvez voir après avoir établi une connexion avec la télécommande.
|
||||
Ces panneaux sont essentiellement 3 (oui, trois en fait):
|
||||
|
||||
- Panneau de l'explorateur local : il s'affiche sur la gauche de votre écran et affiche les entrées du répertoire en cours pour localhost
|
||||
- Panneau de l'explorateur distant : il s'affiche à droite de votre écran et affiche les entrées du répertoire en cours pour l'hôte distant.
|
||||
- Panneau de résultats de recherche : selon l'endroit où vous recherchez des fichiers (local/distant), il remplacera le panneau local ou l'explorateur. Ce panneau affiche les entrées correspondant à la requête de recherche que vous avez effectuée.
|
||||
|
||||
Pour changer de panneau, vous devez taper `<LEFT>` pour déplacer le panneau de l'explorateur distant et `<RIGHT>` pour revenir au panneau de l'explorateur local. Chaque fois que vous êtes dans le panneau des résultats de recherche, vous devez appuyer sur `<ESC>` pour quitter le panneau et revenir au panneau précédent.
|
||||
|
||||
### Raccourcis clavier ⌨
|
||||
|
||||
| Key | Command | Reminder |
|
||||
|---------------|---------------------------------------------------------------------------|-------------|
|
||||
| `<ESC>` | Se Déconnecter de le serveur; retour à la page d'authentification | |
|
||||
| `<BACKSPACE>` | Aller au répertoire précédent dans la pile | |
|
||||
| `<TAB>` | Changer d'onglet explorateur | |
|
||||
| `<RIGHT>` | Déplacer vers l'onglet explorateur distant | |
|
||||
| `<LEFT>` | Déplacer vers l'onglet explorateur local | |
|
||||
| `<UP>` | Remonter dans la liste sélectionnée | |
|
||||
| `<DOWN>` | Descendre dans la liste sélectionnée | |
|
||||
| `<PGUP>` | Remonter dans la liste sélectionnée de 8 lignes | |
|
||||
| `<PGDOWN>` | Descendre dans la liste sélectionnée de 8 lignes | |
|
||||
| `<ENTER>` | Entrer dans le directoire | |
|
||||
| `<SPACE>` | Télécharger le fichier sélectionné | |
|
||||
| `<BACKTAB>` | Basculer entre l'onglet journal et l'explorateur | |
|
||||
| `<A>` | Basculer les fichiers cachés | All |
|
||||
| `<B>` | Trier les fichiers par | Bubblesort? |
|
||||
| `<C|F5>` | Copier le fichier/répertoire | Copy |
|
||||
| `<D|F7>` | Créer un dossier | Directory |
|
||||
| `<E|F8|DEL>` | Supprimer le fichier (Identique à `DEL`) | Erase |
|
||||
| `<F>` | Rechercher des fichiers | Find |
|
||||
| `<G>` | Aller au chemin fourni | Go to |
|
||||
| `<H|F1>` | Afficher l'aide | Help |
|
||||
| `<I>` | Afficher les informations sur le fichier ou le dossier sélectionné | Info |
|
||||
| `<K>` | Créer un lien symbolique pointant vers l'entrée actuellement sélectionnée | symlinK |
|
||||
| `<L>` | Recharger le contenu du répertoire actuel / Effacer la sélection | List |
|
||||
| `<M>` | Sélectionner un fichier | Mark |
|
||||
| `<N>` | Créer un nouveau fichier avec le nom fourni | New |
|
||||
| `<O|F4>` | Modifier le fichier | Open |
|
||||
| `<P>` | Ouvre le panel de journals | Panel |
|
||||
| `<Q|F10>` | Quitter termscp | Quit |
|
||||
| `<R|F6>` | Renommer le fichier | Rename |
|
||||
| `<S|F2>` | Enregistrer le fichier sous... | Save |
|
||||
| `<T>` | Synchroniser les modifications apportées au chemin sélectionné | Track |
|
||||
| `<U>` | Aller dans le répertoire parent | Upper |
|
||||
| `<V|F3>` | Ouvrir le fichier avec le programme défaut pour le type de fichier | View |
|
||||
| `<W>` | Ouvrir le fichier avec le programme spécifié | With |
|
||||
| `<X>` | Exécuter une commande | eXecute |
|
||||
| `<Y>` | Basculer la navigation synchronisée | sYnc |
|
||||
| `<Z>` | Changer permissions de fichier | |
|
||||
| `<CTRL+A>` | Sélectionner tous les fichiers | |
|
||||
| `<CTRL+C>` | Abandonner le processus de transfert de fichiers | |
|
||||
| `<CTRL+T>` | Afficher tous les chemins synchronisés | Track |
|
||||
|
||||
### Travailler sur plusieurs fichiers 🥷
|
||||
|
||||
Vous pouvez choisir de travailler sur plusieurs fichiers, en les sélectionnant en appuyant sur `<M>`, afin de sélectionner le fichier actuel, ou en appuyant sur `<CTRL+A>`, ce qui sélectionnera tous les fichiers dans le répertoire de travail.
|
||||
Une fois qu'un fichier est marqué pour la sélection, il sera affiché avec un `*` sur la gauche.
|
||||
Lorsque vous travaillez sur la sélection, seul le fichier sélectionné sera traité pour les actions, tandis que l'élément en surbrillance actuel sera ignoré.
|
||||
Il est également possible de travailler sur plusieurs fichiers dans le panneau des résultats de recherche.
|
||||
Toutes les actions sont disponibles lorsque vous travaillez avec plusieurs fichiers, mais sachez que certaines actions fonctionnent de manière légèrement différente. Plongeons dans:
|
||||
|
||||
- *Copy*: chaque fois que vous copiez un fichier, vous serez invité à insérer le nom de destination. Lorsque vous travaillez avec plusieurs fichiers, ce nom fait référence au répertoire de destination où tous ces fichiers seront copiés.
|
||||
- *Rename*: identique à la copie, mais y déplacera les fichiers.
|
||||
- *Save as*: identique à la copie, mais les y écrira.
|
||||
|
||||
### Navigation synchronisée ⏲️
|
||||
|
||||
Lorsqu'elle est activée, la navigation synchronisée vous permettra de synchroniser la navigation entre les deux panneaux.
|
||||
Cela signifie que chaque fois que vous changerez de répertoire de travail sur un panneau, la même action sera reproduite sur l'autre panneau. Si vous souhaitez activer la navigation synchronisée, appuyez simplement sur `<Y>` ; appuyez deux fois pour désactiver. Lorsqu'il est activé, l'état de navigation synchronisé sera signalé dans la barre d'état sur `ON`
|
||||
|
||||
### Ouvrir et ouvrir avec 🚪
|
||||
|
||||
Lors de l'ouverture de fichiers avec la commande Afficher (`<V>`), l'application par défaut du système pour le type de fichier sera utilisée. Pour ce faire, le service du système d'exploitation par défaut sera utilisé, alors assurez-vous d'avoir au moins l'un de ceux-ci installé sur votre système :
|
||||
|
||||
- Utilisateurs **Windows** : vous n'avez pas à vous en soucier, puisque la caisse utilisera la commande `start`.
|
||||
- Utilisateurs **MacOS** : vous n'avez pas à vous inquiéter non plus, puisque le crate utilisera `open`, qui est déjà installé sur votre système.
|
||||
- Utilisateurs **Linux** : l'un d'eux doit être installé
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- Utilisateurs **WSL** : *wslview* est requis, vous devez installer [wslu](https://github.com/wslutilities/wslu).
|
||||
|
||||
> Q: Puis-je modifier des fichiers distants à l'aide de la commande view ?
|
||||
> A: Non, du moins pas directement depuis le "panneau distant". Vous devez d'abord le télécharger dans un répertoire local, cela est dû au fait que lorsque vous ouvrez un fichier distant, le fichier est téléchargé dans un répertoire temporaire, mais il n'y a aucun moyen de créer un observateur pour que le fichier vérifie quand le programme que vous utilisé pour l'ouvrir était fermé, donc termscp n'est pas en mesure de savoir quand vous avez fini de modifier le fichier.
|
||||
|
||||
---
|
||||
|
||||
## Signets ⭐
|
||||
|
||||
Dans termscp, il est possible de sauvegarder les hôtes favoris, qui peuvent ensuite être chargés rapidement à partir de la mise en page principale de termscp.
|
||||
termscp enregistrera également les 16 derniers hôtes auxquels vous vous êtes connecté.
|
||||
Cette fonctionnalité vous permet de charger tous les paramètres nécessaires pour vous connecter à une certaine télécommande, en sélectionnant simplement le signet dans l'onglet sous le formulaire d'authentification.
|
||||
|
||||
Les signets seront enregistrés, si possible à l'adresse :
|
||||
|
||||
- `$HOME/.config/termscp/` sous Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` sous MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` sous Windows
|
||||
|
||||
Pour les signets uniquement (cela ne s'appliquera pas aux hôtes récents), il est également possible de sauvegarder le mot de passe utilisé pour s'authentifier. Le mot de passe n'est pas enregistré par défaut et doit être spécifié via l'invite lors de l'enregistrement d'un nouveau signet.
|
||||
Si vous êtes préoccupé par la sécurité du mot de passe enregistré pour vos favoris, veuillez lire le [chapitre ci-dessous 👀](#mes-mots-de-passe-sont-ils-sûrs-).
|
||||
|
||||
Pour créer un nouveau signet, suivez simplement ces étapes :
|
||||
|
||||
1. Tapez dans le formulaire d'authentification les paramètres pour vous connecter à votre serveur distant
|
||||
2. Appuyez sur `<CTRL+S>`
|
||||
3. Tapez le nom que vous souhaitez donner au signet
|
||||
4. Choisissez de rappeler ou non le mot de passe
|
||||
5. Appuyez sur `<ENTER>` pour soumettre
|
||||
|
||||
chaque fois que vous souhaitez utiliser la connexion précédemment enregistrée, appuyez simplement sur `<TAB>` pour accéder à la liste des signets et chargez les paramètres des signets dans le formulaire en appuyant sur `<ENTER>`.
|
||||
|
||||

|
||||
|
||||
### Mes mots de passe sont-ils sûrs 😈
|
||||
|
||||
Bien sûr 😉.
|
||||
Comme dit précédemment, les signets sont enregistrés dans votre répertoire de configuration avec les mots de passe. Les mots de passe ne sont évidemment pas en texte brut, ils sont cryptés avec **AES-128**. Est-ce que cela les sécurise ? Absolument! (sauf pour les utilisateurs BSD et WSL 😢)
|
||||
|
||||
Sous **Windows**, **Linux** et **MacOS**, la clé utilisée pour crypter les mots de passe est stockée, si possible (mais devrait l'être), respectivement dans le *Windows Vault*, dans le *porte-clés système* et dans le *Porte-clés*. Ceci est en fait super sûr et est directement géré par votre système d'exploitation.
|
||||
|
||||
❗ Veuillez noter que si vous êtes un utilisateur Linux, vous feriez mieux de lire le [chapitre ci-dessous 👀](#linux-keyring), car le trousseau peut ne pas être activé ou pris en charge sur votre système !
|
||||
|
||||
Sur *BSD* et *WSL*, en revanche, la clé utilisée pour crypter vos mots de passe est stockée sur votre disque (dans $HOME/.config/termscp). Il est alors, toujours possible de récupérer la clé pour déchiffrer les mots de passe. Heureusement, l'emplacement de la clé garantit que votre clé ne peut pas être lue par des utilisateurs différents du vôtre, mais oui, je n'enregistrerais toujours pas le mot de passe pour un serveur exposé sur Internet 😉.
|
||||
|
||||
#### Linux Keyring
|
||||
|
||||
Nous aimons tous Linux grâce à la liberté qu'il donne aux utilisateurs. En tant qu'utilisateur Linux, vous pouvez essentiellement faire tout ce que vous voulez, mais cela présente également des inconvénients, tels que le fait qu'il n'y a souvent pas d'applications standard dans différentes distributions. Et cela implique aussi un porte-clés.
|
||||
Cela signifie que sous Linux, aucun trousseau de clés n'est peut-être installé sur votre système. Malheureusement, la bibliothèque que nous utilisons pour travailler avec le stockage des clés nécessite un service qui expose `org.freedesktop.secrets` sur D-BUS et le pire est qu'il n'y a que deux services qui l'exposent.
|
||||
|
||||
- ❗ Si vous utilisez GNOME comme environnement de bureau (par exemple, les utilisateurs d'ubuntu), ça devrait déjà aller, car le trousseau de clés est déjà fourni par `gnome-keyring` et tout devrait déjà fonctionner.
|
||||
- ❗ Pour les autres utilisateurs d'environnement de bureau, il existe un programme sympa que vous pouvez utiliser pour obtenir un trousseau de clés qui est [KeepassXC](https://keepassxc.org/), que j'utilise sur mon installation Manjaro (avec KDE) et qui fonctionne bien. Le seul problème est que vous devez le configurer pour qu'il soit utilisé avec termscp (mais c'est assez simple). Pour commencer avec KeepassXC, lisez la suite [ici](#configuration-de-keepassxc-pour-termscp).
|
||||
- ❗ Et si vous ne souhaitez installer aucun de ces services ? Eh bien, il n'y a pas de problème ! **termscp continuera à fonctionner comme d'habitude**, mais il enregistrera la clé dans un fichier, comme il le fait habituellement pour BSD et WSL.
|
||||
|
||||
##### Configuration de KeepassXC pour termscp
|
||||
|
||||
Suivez ces étapes afin de configurer keepassXC pour termscp :
|
||||
|
||||
1. Installer KeepassXC
|
||||
2. Allez dans "outils" > "paramètres" dans la barre d'outils
|
||||
3. Selectioner "Secret service integration" et basculer "Enable KeepassXC freedesktop.org secret service integration"
|
||||
4. Creer une base de données, si vous n'en avez pas encore : à partir de la barre d'outils "Database" > "New database"
|
||||
5. De la barre d'outils: "Database" > "Database settings"
|
||||
6. Selectioner "Secret service integration" et basculer "Expose entries under this group"
|
||||
7. Sélectionnez le groupe dans la liste où vous souhaitez conserver le secret du termscp. N'oubliez pas que ce groupe peut être utilisé par toute autre application pour stocker des secrets via DBUS.
|
||||
|
||||
---
|
||||
|
||||
## Configuration ⚙️
|
||||
|
||||
termscp prend en charge certains paramètres définis par l'utilisateur, qui peuvent être définis dans la configuration.
|
||||
Underhood termscp a un fichier TOML et quelques autres répertoires où tous les paramètres seront enregistrés, mais ne vous inquiétez pas, vous ne toucherez à aucun de ces fichiers manuellement, car j'ai rendu possible la configuration complète de termscp à partir de son interface utilisateur.
|
||||
|
||||
termscp, comme pour les signets, nécessite juste d'avoir ces chemins accessibles :
|
||||
|
||||
- `$HOME/.config/termscp/` sous Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` sous MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` sous Windows
|
||||
|
||||
Pour accéder à la configuration, il vous suffit d'appuyer sur `<CTRL+C>` depuis l'accueil de termscp.
|
||||
|
||||
Ces paramètres peuvent être modifiés :
|
||||
|
||||
- **Text Editor**: l'éditeur de texte à utiliser. Par défaut, termscp trouvera l'éditeur par défaut pour vous ; avec cette option, vous pouvez forcer l'utilisation d'un éditeur (par exemple `vim`). **Les éditeurs d'interface graphique sont également pris en charge**, à moins qu'ils ne soient `nohup` à partir du processus parent.
|
||||
- **Default Protocol**: le protocole par défaut est la valeur par défaut du protocole de transfert de fichiers à utiliser dans termscp. Cela s'applique à la page de connexion et à l'argument de l'adresse CLI.
|
||||
- **Show Hidden Files**: sélectionnez si les fichiers cachés doivent être affichés par défaut. Vous pourrez décider d'afficher ou non les fichiers cachés au moment de l'exécution en appuyant sur `A` de toute façon.
|
||||
- **Check for updates**: s'il est défini sur `yes`, Termscp récupère l'API Github pour vérifier si une nouvelle version de Termscp est disponible.
|
||||
- **Prompt when replacing existing files?**: S'il est défini sur `yes`, Termscp vous demandera une confirmation chaque fois qu'un transfert de fichier entraînera le remplacement d'un fichier existant sur l'hôte cible.
|
||||
- **Group Dirs**: sélectionnez si les répertoires doivent être regroupés ou non dans les explorateurs de fichiers. Si `Display first` est sélectionné, les répertoires seront triés en utilisant la méthode configurée mais affichés avant les fichiers, vice-versa si `Display last` est sélectionné.
|
||||
- **Remote File formatter syntax**: syntaxe pour afficher les informations de fichier pour chaque fichier dans l'explorateur distant. Voir [File explorer format](#format-de-lexplorateur-de-fichiers)
|
||||
- **Local File formatter syntax**: syntaxe pour afficher les informations de fichier pour chaque fichier dans l'explorateur local. Voir [File explorer format](#format-de-lexplorateur-de-fichiers)
|
||||
- **Enable notifications?**: S'il est défini sur `Yes`, les notifications seront affichées.
|
||||
- **Notifications: minimum transfer size**: si la taille du transfert est supérieure ou égale à la valeur spécifiée, les notifications de transfert seront affichées. Les valeurs acceptées sont au format `{UNSIGNED} B/KB/MB/GB/TB/PB`
|
||||
- **SSH configuration path** : définissez le fichier de configuration SSH à utiliser lors de la connexion à un serveur SCP/SFTP. S'il n'est pas défini (vide), aucun fichier ne sera utilisé. Vous pouvez spécifier un chemin commençant par `~` pour indiquer le chemin d'accueil (par exemple `~/.ssh/config`). Les paramétrages disponibles pour la configuration sont listées [ICI](https://github.com/veeso/ssh2-config#exposed-attributes).
|
||||
|
||||
### SSH Key Storage 🔐
|
||||
|
||||
n plus de la configuration, termscp fournit également une fonctionnalité **essentielle** pour les **clients SFTP/SCP** : le stockage de clés SSH.
|
||||
|
||||
Vous pouvez accéder au stockage des clés SSH, de la configuration à l'onglet « Clés SSH », une fois là-bas, vous pouvez :
|
||||
|
||||
- **Ajouter une neuf clé SSH**: appuyez simplement sur `<CTRL+N>` et vous serez invité à créer une nouvelle clé. Fournissez le nom d'hôte/l'adresse IP et le nom d'utilisateur associé à la clé et enfin un éditeur de texte s'ouvrira : collez la clé ssh **PRIVÉE** dans l'éditeur de texte, enregistrez et quittez.
|
||||
- **Supprimer une clé existante**: appuyez simplement sur `<DEL>` ou `<CTRL+E>` sur la clé que vous souhaitez supprimer, pour supprimer de manière persistante la clé de termscp.
|
||||
- **Modifier une clé existante**: appuyez simplement sur `<ENTER>` sur la clé que vous souhaitez modifier, pour changer la clé privée.
|
||||
|
||||
> Q: Ma clé privée est protégée par mot de passe, puis-je l'utiliser ?
|
||||
> A: Bien sûr vous pouvez. Le mot de passe fourni pour l'authentification dans termscp est valide à la fois pour l'authentification par nom d'utilisateur/mot de passe et pour l'authentification par clé RSA.
|
||||
|
||||
### Format de l'explorateur de fichiers
|
||||
|
||||
Il est possible via la configuration de définir un format personnalisé pour l'explorateur de fichiers. Ceci est possible à la fois pour l'hôte local et distant, vous pouvez donc utiliser deux syntaxes différentes. Ces champs, nommés `File formatter syntax (local)` et `File formatter syntax (remote)` définiront comment les entrées de fichier seront affichées dans l'explorateur de fichiers.
|
||||
La syntaxe du formateur est la suivante `{KEY1}... {KEY2:LENGTH}... {KEY3:LENGTH:EXTRA} {KEYn}...`.
|
||||
Chaque clé entre crochets sera remplacée par l'attribut associé, tandis que tout ce qui se trouve en dehors des crochets restera inchangé.
|
||||
|
||||
- Le nom de la clé est obligatoire et doit être l'une des clés ci-dessous
|
||||
- La longueur décrit la longueur réservée pour afficher le champ. Les attributs statiques ne prennent pas en charge cela (GROUP, PEX, SIZE, USER)
|
||||
- Extra n'est pris en charge que par certains paramètres et constitue une option supplémentaire. Voir les touches pour vérifier si les extras sont pris en charge.
|
||||
|
||||
Voici les clés prises en charge par le formateur :
|
||||
|
||||
- `ATIME`: Heure du dernier accès (avec la syntaxe par défaut `%b %d %Y %H:%M`) ; Un supplément peut être fourni comme syntaxe de l'heure (par exemple, `{ATIME:8:%H:%M}`)
|
||||
- `CTIME`: Heure de création (avec la syntaxe `%b %d %Y %H:%M`); Un supplément peut être fourni comme syntaxe de l'heure (par exemple, `{CTIME:8:%H:%M}`)
|
||||
- `GROUP`: Groupe de propriétaires
|
||||
- `MTIME`: Heure du dernier changement (avec la syntaxe `%b %d %Y %H:%M`); Un supplément peut être fourni comme syntaxe de l'heure (par exemple, `{MTIME:8:%H:%M}`)
|
||||
- `NAME`: Nom du fichier (élidé si plus long que LENGTH)
|
||||
- `PATH`: Chemin absolu du fichier (les dossiers entre la racine et les premiers ancêtres sont éludés s'ils sont plus longs que LENGTH)
|
||||
- `PEX`: Autorisations de fichiers (format UNIX)
|
||||
- `SIZE`: Taille du fichier (omis pour les répertoires)
|
||||
- `SYMLINK`: Lien symbolique (le cas échéant `-> {FILE_PATH}`)
|
||||
- `USER`: Utilisateur propriétaire
|
||||
|
||||
Si elle est laissée vide, la syntaxe par défaut du formateur sera utilisée : `{NAME:24} {PEX} {USER} {SIZE} {MTIME:17:%b %d %Y %H:%M}`
|
||||
|
||||
---
|
||||
|
||||
## Thèmes 🎨
|
||||
|
||||
Termscp vous offre une fonctionnalité géniale : la possibilité de définir les couleurs de plusieurs composants de l'application.
|
||||
Si vous souhaitez personnaliser termscp, il existe deux manières de le faire :
|
||||
|
||||
- Depuis le **menu de configuration**
|
||||
- Importation d'un **fichier de thème**
|
||||
|
||||
Afin de créer votre propre personnalisation à partir de termscp, il vous suffit de saisir la configuration à partir de l'activité d'authentification, en appuyant sur `<CTRL+C>` puis sur `<TAB>` deux fois. Vous devriez être maintenant passé au panneau `thèmes`.
|
||||
|
||||
Ici, vous pouvez vous déplacer avec `<UP>` et `<DOWN>` pour changer le style que vous souhaitez modifier, comme indiqué dans le gif ci-dessous :
|
||||
|
||||

|
||||
|
||||
termscp prend en charge à la fois la syntaxe hexadécimale explicite traditionnelle (`#rrggbb`) et rgb `rgb(r, g, b)` pour fournir des couleurs, mais aussi **[couleurs css](https://www.w3schools.com/cssref/css_colors.asp)** (comme `crimson`) sont acceptés 😉. Il y a aussi un keywork spécial qui est `Default`. Par défaut signifie que la couleur utilisée sera la couleur de premier plan ou d'arrière-plan par défaut en fonction de la situation (premier plan pour les textes et les lignes, arrière-plan pour bien, devinez quoi)
|
||||
|
||||
Comme dit précédemment, vous pouvez également importer des fichiers de thème. Vous pouvez vous inspirer de ou utiliser directement l'un des thèmes fournis avec termscp, situé dans le répertoire `themes/` de ce référentiel et les importer en exécutant termscp en tant que `termscp -t <theme_file>`. Si tout allait bien, cela devrait vous dire que le thème a été importé avec succès.
|
||||
|
||||
### Mon thème ne se charge pas 😱
|
||||
|
||||
Cela est probablement dû à une mise à jour récente qui a cassé le thème. Chaque fois que j'ajoute une nouvelle clé aux thèmes, le thème enregistré ne se charge pas. Pour résoudre ces problèmes, il existe deux solutions vraiment rapides :
|
||||
|
||||
1. Recharger le thème : chaque fois que je publie une mise à jour, je corrige également les thèmes "officiels", il vous suffit donc de le télécharger à nouveau depuis le référentiel et de réimporter le thème via l'option `-t`
|
||||
|
||||
```sh
|
||||
termscp -t <theme.toml>
|
||||
```
|
||||
|
||||
2. Corrigez votre thème : si vous utilisez un thème personnalisé, vous pouvez le modifier via `vim` et ajouter la clé manquante. Le thème est situé dans `$CONFIG_DIR/termscp/theme.toml` où `$CONFIG_DIR` est :
|
||||
|
||||
- FreeBSD/GNU-Linux: `$HOME/.config/`
|
||||
- MacOs: `$HOME/Library/Application Support`
|
||||
- Windows: `%appdata%`
|
||||
|
||||
❗ Les clés manquantes sont signalées dans le CHANGELOG sous `BREAKING CHANGES` pour la version que vous venez d'installer.
|
||||
|
||||
### Modes 💈
|
||||
|
||||
Vous pouvez trouver dans le tableau ci-dessous, la description de chaque champ de style.
|
||||
Veuillez noter que **les styles ne s'appliqueront pas à la page de configuration**, afin de la rendre toujours accessible au cas où vous gâcheriez tout
|
||||
|
||||
#### Authentication page
|
||||
|
||||
| Key | Description |
|
||||
|----------------|------------------------------------------|
|
||||
| auth_address | Couleur du champ pour adresse IP |
|
||||
| auth_bookmarks | Couleur du panneau des signets |
|
||||
| auth_password | Couleur du champ pour mot de passe |
|
||||
| auth_port | Couleur du champ pour nombre de port |
|
||||
| auth_protocol | Couleur du groupe radio pour protocole |
|
||||
| auth_recents | Couleur du panneau récent |
|
||||
| auth_username | Couleur du champ pour nom d'utilisateur |
|
||||
|
||||
#### Transfer page
|
||||
|
||||
| Key | Description |
|
||||
|--------------------------------------|---------------------------------------------------------------------------|
|
||||
| transfer_local_explorer_background | Couleur d'arrière-plan de l'explorateur localhost |
|
||||
| transfer_local_explorer_foreground | Couleur de premier plan de l'explorateur localhost |
|
||||
| transfer_local_explorer_highlighted | Bordure et couleur surlignée pour l'explorateur localhost |
|
||||
| transfer_remote_explorer_background | Couleur d'arrière-plan de l'explorateur distant |
|
||||
| transfer_remote_explorer_foreground | Couleur de premier plan de l'explorateur distant |
|
||||
| transfer_remote_explorer_highlighted | Bordure et couleur en surbrillance pour l'explorateur distant |
|
||||
| transfer_log_background | Couleur d'arrière-plan du panneau de journal |
|
||||
| transfer_log_window | Couleur de la fenêtre du panneau de journal |
|
||||
| transfer_progress_bar_partial | Couleur de la barre de progression partielle |
|
||||
| transfer_progress_bar_total | Couleur de la barre de progression totale |
|
||||
| transfer_status_hidden | Couleur de l'étiquette "hidden" de la barre d'état |
|
||||
| transfer_status_sorting | Couleur de l'étiquette "sorting" de la barre d'état |
|
||||
| transfer_status_sync_browsing | Couleur de l'étiquette "sync browsing" de la barre d'état |
|
||||
|
||||
#### Misc
|
||||
|
||||
These styles applie to different part of the application.
|
||||
|
||||
| Key | Description |
|
||||
|-------------------|---------------------------------------------|
|
||||
| misc_error_dialog | Couleur des messages d'erreur |
|
||||
| misc_info_dialog | Couleur des messages d'info |
|
||||
| misc_input_dialog | Couleur des messages de input |
|
||||
| misc_keys | Couleur du texte pour les frappes de touches|
|
||||
| misc_quit_dialog | Couleur des messages de quit |
|
||||
| misc_save_dialog | Couleur des messages d'enregistrement |
|
||||
| misc_warn_dialog | Couleur des messages de attention |
|
||||
|
||||
---
|
||||
|
||||
## Éditeur de texte ✏
|
||||
|
||||
termscp a, comme vous l'avez peut-être remarqué, de nombreuses fonctionnalités, l'une d'entre elles est la possibilité de visualiser et de modifier un fichier texte. Peu importe que le fichier se trouve sur l'hôte local ou sur l'hôte distant, termscp offre la possibilité d'ouvrir un fichier dans votre éditeur de texte préféré.
|
||||
Si le fichier se trouve sur l'hôte distant, le fichier sera d'abord téléchargé dans votre répertoire de fichiers temporaires, puis **uniquement** si des modifications ont été apportées au fichier, rechargé sur l'hôte distant. termscp vérifie si vous avez apporté des modifications au fichier en vérifiant l'heure de la dernière modification du fichier.
|
||||
|
||||
> ❗ Juste un rappel : **vous ne pouvez éditer que des fichiers texte** ; les fichiers binaires ne sont pas pris en charge.
|
||||
|
||||
---
|
||||
|
||||
## Fichier Journal 🩺
|
||||
|
||||
termscp écrit un fichier journal pour chaque session, qui est écrit à
|
||||
|
||||
- `$HOME/.cache/termscp/termscp.log` sous Linux/BSD
|
||||
- `$HOME/Library/Caches/termscp/termscp.log` sous MacOs
|
||||
- `FOLDERID_LocalAppData\termscp\termscp.log` sous Windows
|
||||
|
||||
le journal ne sera pas tourné, mais sera simplement tronqué après chaque lancement de termscp, donc si vous souhaitez signaler un problème et que vous souhaitez joindre votre fichier journal, n'oubliez pas de sauvegarder le fichier journal dans un endroit sûr avant de l'utiliser termescp à nouveau.
|
||||
|
||||
La journalisation par défaut se rapporte au niveau *INFO*, elle n'est donc pas très détaillée.
|
||||
|
||||
Si vous souhaitez soumettre un problème, veuillez, si vous le pouvez, reproduire le problème avec le niveau défini sur `TRACE`, pour ce faire, lancez termscp avec
|
||||
l'option CLI `-D`.
|
||||
|
||||
Je sais que vous pourriez avoir des questions concernant les fichiers journaux, alors j'ai fait une sorte de Q/R :
|
||||
|
||||
> Je ne veux pas me connecter, puis-je le désactiver ?
|
||||
|
||||
Oui, vous pouvez. Démarrez simplement termscp avec l'option `-q ou --quiet`. Vous pouvez créer un alias termcp pour le rendre persistant. N'oubliez pas que la journalisation est utilisée pour diagnostiquer les problèmes, donc puisque derrière chaque projet open source, il devrait toujours y avoir ce genre d'aide mutuelle, la conservation des fichiers journaux peut être votre moyen de soutenir le projet 😉. Je ne veux pas que tu te sentes coupable, mais juste pour dire.
|
||||
|
||||
> La journalisation est-elle sûre ?
|
||||
|
||||
Si vous êtes préoccupé par la sécurité, le fichier journal ne contient aucun mot de passe simple, alors ne vous inquiétez pas et expose les mêmes informations que le fichier frère "signets".
|
||||
|
||||
## Notifications 📫
|
||||
|
||||
Termscp enverra des notifications de bureau pour ce type d'événements :
|
||||
|
||||
- sur **Transfert terminé** : La notification sera envoyée une fois le transfert terminé avec succès.
|
||||
- ❗ La notification ne s'affichera que si la taille totale du transfert est au moins la `Notifications: minimum transfer size` spécifiée dans la configuration.
|
||||
- sur **Transfert échoué** : La notification sera envoyée une fois qu'un transfert a échoué en raison d'une erreur.
|
||||
- ❗ La notification ne s'affichera que si la taille totale du transfert est au moins la `Notifications: minimum transfer size` spécifiée dans la configuration.
|
||||
- sur **Mise à jour disponible** : chaque fois qu'une nouvelle version de Termscp est disponible, une notification s'affiche.
|
||||
- sur **Mise à jour installée** : chaque fois qu'une nouvelle version de Termscp est installée, une notification s'affiche.
|
||||
- sur **Échec de la mise à jour** : chaque fois que l'installation de la mise à jour échoue, une notification s'affiche.
|
||||
|
||||
❗ Si vous préférez désactiver les notifications, vous pouvez simplement accéder à la configuration et définir `Enable notifications?` sur `No` 😉.
|
||||
❗ Si vous souhaitez modifier la taille de transfert minimale pour afficher les notifications, vous pouvez modifier la valeur dans la configuration avec la touche `Notifications: minimum transfer size` et la définir sur ce qui vous convient le mieux 🙂.
|
||||
|
||||
## Observateur de fichiers 🔭
|
||||
|
||||
L'observateur de fichiers vous permet de configurer une liste de chemins à synchroniser avec les hôtes distants.
|
||||
Cela signifie que chaque fois qu'un changement sur le système de fichiers local sera détecté sur le chemin synchronisé, le changement sera automatiquement signalé au chemin de l'hôte distant configuré, dans les 5 secondes.
|
||||
|
||||
Vous pouvez définir autant de chemins à synchroniser que vous préférez :
|
||||
|
||||
1. Placez le curseur de l'explorateur local sur le répertoire/fichier que vous souhaitez conserver synchronisé
|
||||
2. Accédez au répertoire dans lequel vous souhaitez que les modifications soient signalées sur l'hôte distant
|
||||
3. Appuyez sur `<T>`
|
||||
4. Répondez `<YES>` à la fenêtre contextuelle de la radio
|
||||
|
||||
Pour annuler la surveillance, appuyez simplement sur `<T>` sur le chemin synchronisé local (ou sur l'un de ses sous-dossiers)
|
||||
OU vous pouvez simplement appuyer sur `<CTRL + T>` et appuyer sur `<ENTER>` jusqu'au chemin synchronisé que vous souhaitez désactiver.
|
||||
|
||||
Ces modifications seront signalées à l'hôte distant :
|
||||
|
||||
- Nouveaux fichiers, modifications de fichiers
|
||||
- Fichier déplacé / renommé
|
||||
- Fichier supprimé / dissocié
|
||||
|
||||
> ❗ Le watcher ne fonctionne que dans un sens (local > distant). Il n'est PAS possible de synchroniser automatiquement les changements de distant à local.
|
||||
@@ -1,289 +0,0 @@
|
||||
# termscp
|
||||
|
||||
<p align="center">
|
||||
<img src="/assets/images/termscp.svg" width="256" height="256" />
|
||||
</p>
|
||||
|
||||
<p align="center">~ Un file transfer ricco di funzionalità ~</p>
|
||||
<p align="center">
|
||||
<a href="https://termscp.veeso.dev" target="_blank">Sito</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#get-started" target="_blank">Installazione</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#user-manual" target="_blank">Manuale utente</a>
|
||||
</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/gb.png"
|
||||
alt="English"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/de/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/de.png"
|
||||
alt="Deutsch"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/es/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/es.png"
|
||||
alt="Español"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/fr/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/fr.png"
|
||||
alt="Français"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/it/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/it.png"
|
||||
alt="Italiano"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/zh-CN/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/cn.png"
|
||||
alt="简体中文"
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
<p align="center">Sviluppato da <a href="https://veeso.dev/" target="_blank">@veeso</a></p>
|
||||
<p align="center">Versione corrente: 0.12.3 (06/10/2023)</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://opensource.org/licenses/MIT"
|
||||
><img
|
||||
src="https://img.shields.io/badge/License-MIT-teal.svg"
|
||||
alt="License-MIT"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/stargazers"
|
||||
><img
|
||||
src="https://img.shields.io/github/stars/veeso/termscp.svg"
|
||||
alt="Repo stars"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/d/termscp.svg"
|
||||
alt="Downloads counter"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/v/termscp.svg"
|
||||
alt="Latest version"
|
||||
/></a>
|
||||
<a href="https://ko-fi.com/veeso">
|
||||
<img
|
||||
src="https://img.shields.io/badge/donate-ko--fi-red"
|
||||
alt="Ko-fi"
|
||||
/></a>
|
||||
</p>
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Linux/badge.svg"
|
||||
alt="Linux CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/MacOS/badge.svg"
|
||||
alt="MacOS CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Windows/badge.svg"
|
||||
alt="Windows CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/FreeBSD/badge.svg"
|
||||
alt="FreeBSD CI"
|
||||
/></a>
|
||||
<a href="https://coveralls.io/github/veeso/termscp"
|
||||
><img
|
||||
src="https://coveralls.io/repos/github/veeso/termscp/badge.svg"
|
||||
alt="Coveralls"
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
---
|
||||
|
||||
## Riguardo a termscp 🖥
|
||||
|
||||
Termscp è un file transfer ed explorer ricco di funzionalità, con supporto a SCP/SFTP/FTP/S3. In pratica è un utility su terminale con una terminal user-interface per connettersi a server remoti per scambiare file ed interagire con il file system sia locale che remoto. È compatibile con **Linux**, **MacOS**, **FreeBSD** e **Windows**.
|
||||
|
||||

|
||||
|
||||
---
|
||||
|
||||
## Funzionalità 🎁
|
||||
|
||||
- 📁 Diversi protocolli di comunicazione
|
||||
- **SFTP**
|
||||
- **SCP**
|
||||
- **FTP** and **FTPS**
|
||||
- **S3**
|
||||
- **SMB**
|
||||
- 🖥 Esplora e opera sia sul file system locale che su quello remoto con una UI di facile utilizzo.
|
||||
- Crea, rimuove, rinomina, cerca, visualizza e modifica file
|
||||
- ⭐ Connettiti ai tuoi host preferiti tramite la funzionalità integrata dei segnalibri e delle connessioni recenti.
|
||||
- 📝 Visualizza e modifica i file tramite le tue applicazioni preferite.
|
||||
- 💁 Autenticazione su server SFTP/SCP tramite chiavi SSH e/o username/password
|
||||
- 🐧 Compatibile con Windows, Linux, FreeBSD e MacOS
|
||||
- 🎨 Customizzalo!
|
||||
- Temi
|
||||
- Formattazione dell'explorer
|
||||
- Impostazione del text editor predefinito
|
||||
- Imposta l'ordinamento di file e cartelle
|
||||
- e tanto altro...
|
||||
- 📫 Ricevi notifiche desktop quando un file di cospicue dimensioni è stato trasferito
|
||||
- 🔭 Mantieni sincronizzate le modifiche con l'host remoto
|
||||
- 🔐 Salva le password degli host remoti nel keyring predefinito dal tuo sistema operativo
|
||||
- 🦀 Rust-powered
|
||||
- 👀 Progettato tenendo conto delle performance
|
||||
- 🦄 Aggiornamenti frequenti con nuove funzionalità
|
||||
|
||||
---
|
||||
|
||||
## Per iniziare 🚀
|
||||
|
||||
Intanto se stai considerando di installare termscp, ti voglio ringraziare 💜 e spero che termscp ti piacerà!
|
||||
Se vuoi contribuire al progetto, non dimenticarti di leggere la [contribute guide](../../CONTRIBUTING.md).
|
||||
|
||||
Se sei un utente che utilizza Linux, FreeBSD o MacOS, questo shell script installerà termscp sul tuo sistema con un comando secco:
|
||||
|
||||
```sh
|
||||
curl -sSLf http://get-termscp.veeso.dev | sh
|
||||
```
|
||||
|
||||
mentre se sei un utente Windows, puoi installare termscp con [Chocolatey](https://chocolatey.org/):
|
||||
|
||||
```sh
|
||||
choco install termscp
|
||||
```
|
||||
|
||||
Per ulteriori informazioni sui metodi di installazione su altre piattaforme, visita [termscp.veeso.dev](https://termscp.veeso.dev/termscp/#get-started).
|
||||
|
||||
⚠️ Se stavi cercando come aggiornare la tua versione di termscp, puoi semplicemente lanciare termscp con questi argomenti: `(sudo) termscp --update` ⚠️
|
||||
|
||||
### Requisiti ❗
|
||||
|
||||
- **Linux** users:
|
||||
- libdbus-1
|
||||
- pkg-config
|
||||
- libsmbclient
|
||||
- **FreeBSD** or, **NetBSD** users:
|
||||
- dbus
|
||||
- pkgconf
|
||||
- libsmbclient
|
||||
|
||||
### Requisiti opzionali ✔️
|
||||
|
||||
Questi requisiti non sono per forza necessari, ma lo sono per sfruttare tutte le sue funzionalità:
|
||||
|
||||
- Utenti **Linux/FreeBSD**:
|
||||
- Per **aprire** i file con `V` (almeno uno di questi)
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- Utenti **Linux**:
|
||||
- Un keyring manager: Approfondisci nel [Manuale](man.md#linux-keyring)
|
||||
- Utenti **WSL**
|
||||
- Per **aprire** i file con `V` (almeno uno di questi)
|
||||
- [wslu](https://github.com/wslutilities/wslu)
|
||||
|
||||
---
|
||||
|
||||
## Supporta lo sviluppatore ☕
|
||||
|
||||
Se ti piace termscp e ti piacerebbe vedere il progetto crescere e migliorare, considera una piccola donazione 🥳.
|
||||
|
||||
Puoi fare una donazione tramite una di queste piattaforme:
|
||||
|
||||
[](https://ko-fi.com/veeso)
|
||||
[](https://www.paypal.me/chrisintin)
|
||||
|
||||
---
|
||||
|
||||
## Manuale utente 📚
|
||||
|
||||
Il manuale utente lo puoi trovare sul [sito di termscp](https://termscp.veeso.dev/termscp/#user-manual) o su [Github](man.md).
|
||||
|
||||
---
|
||||
|
||||
## Contributi e issues 🤝🏻
|
||||
|
||||
Contributi, report di bug, nuove funzionalità e domande sono i benvenuti! 😉
|
||||
Se hai qualche domanda o dubbio o vuoi suggerire una nuova funzionalità, sentiti libero di aprire un issue o una PR.
|
||||
|
||||
Per favore segui le nostre [contributing guidelines](../../CONTRIBUTING.md)
|
||||
|
||||
---
|
||||
|
||||
## Changelog ⏳
|
||||
|
||||
Visualizza [Qui](../../CHANGELOG.md) il changelog
|
||||
|
||||
---
|
||||
|
||||
## Un grazie a questi progetti 💪
|
||||
|
||||
se termscp esiste, è anche grazie a questi fantastici progetti:
|
||||
|
||||
- [bytesize](https://github.com/hyunsik/bytesize)
|
||||
- [crossterm](https://github.com/crossterm-rs/crossterm)
|
||||
- [edit](https://github.com/milkey-mouse/edit)
|
||||
- [keyring-rs](https://github.com/hwchen/keyring-rs)
|
||||
- [open-rs](https://github.com/Byron/open-rs)
|
||||
- [rpassword](https://github.com/conradkleinespel/rpassword)
|
||||
- [rust-s3](https://github.com/durch/rust-s3)
|
||||
- [self_update](https://github.com/jaemk/self_update)
|
||||
- [ssh2-rs](https://github.com/alexcrichton/ssh2-rs)
|
||||
- [suppaftp](https://github.com/veeso/suppaftp)
|
||||
- [tui-rs](https://github.com/fdehau/tui-rs)
|
||||
- [tui-realm](https://github.com/veeso/tui-realm)
|
||||
- [whoami](https://github.com/libcala/whoami)
|
||||
- [wildmatch](https://github.com/becheran/wildmatch)
|
||||
|
||||
---
|
||||
|
||||
## Galleria 🎬
|
||||
|
||||
> Termscp Home
|
||||
|
||||

|
||||
|
||||
> Bookmarks
|
||||
|
||||

|
||||
|
||||
> Configurazione
|
||||
|
||||

|
||||
|
||||
> Text editor
|
||||
|
||||

|
||||
|
||||
---
|
||||
|
||||
## Licenza 📃
|
||||
|
||||
termscp è fornito sotto licenza MIT.
|
||||
|
||||
Puoi leggere l'intero documento di licenza [Qui](../../LICENSE)
|
||||
@@ -1,556 +0,0 @@
|
||||
# Manuale utente 🎓
|
||||
|
||||
- [Manuale utente 🎓](#manuale-utente-)
|
||||
- [Argomenti da linea di comando ❓](#argomenti-da-linea-di-comando-)
|
||||
- [Argomento indirizzo 🌎](#argomento-indirizzo-)
|
||||
- [Argomento indirizzo per AWS S3](#argomento-indirizzo-per-aws-s3)
|
||||
- [Indirizzo SMB](#indirizzo-smb)
|
||||
- [Come fornire la password 🔐](#come-fornire-la-password-)
|
||||
- [Parametri di connessione S3](#parametri-di-connessione-s3)
|
||||
- [Credenziali S3 🦊](#credenziali-s3-)
|
||||
- [File explorer 📂](#file-explorer-)
|
||||
- [Abbinamento tasti ⌨](#abbinamento-tasti-)
|
||||
- [Lavora su più file 🥷](#lavora-su-più-file-)
|
||||
- [Synchronized browsing ⏲️](#synchronized-browsing-️)
|
||||
- [Apri e apri con 🚪](#apri-e-apri-con-)
|
||||
- [Segnalibri ⭐](#segnalibri-)
|
||||
- [Le mie password sono al sicuro 😈](#le-mie-password-sono-al-sicuro-)
|
||||
- [Linux Keyring](#linux-keyring)
|
||||
- [KeepassXC setup per termscp](#keepassxc-setup-per-termscp)
|
||||
- [Configurazione ⚙️](#configurazione-️)
|
||||
- [SSH Key Storage 🔐](#ssh-key-storage-)
|
||||
- [File Explorer Format](#file-explorer-format)
|
||||
- [Temi 🎨](#temi-)
|
||||
- [Il tema non carica 😱](#il-tema-non-carica-)
|
||||
- [Stili 💈](#stili-)
|
||||
- [Pagina autenticazione](#pagina-autenticazione)
|
||||
- [Pagina explorer e trasferimento](#pagina-explorer-e-trasferimento)
|
||||
- [Misc](#misc)
|
||||
- [Editor di testo ✏](#editor-di-testo-)
|
||||
- [Logging 🩺](#logging-)
|
||||
- [Notifiche 📫](#notifiche-)
|
||||
- [File watcher 🔭](#file-watcher-)
|
||||
|
||||
## Argomenti da linea di comando ❓
|
||||
|
||||
termscp può essere lanciato con questi argomenti:
|
||||
|
||||
`termscp [options]... [protocol://user@address:port:wrkdir] [local-wrkdir]`
|
||||
|
||||
O
|
||||
|
||||
`termscp [options]... -b [bookmark-name] [local-wrkdir]`
|
||||
|
||||
- `-P, --password <password>` Se viene fornito l'argomento indirizzo, questa sarà la password utilizzata per autenticarsi
|
||||
- `-b, --address-as-bookmark` risolve l'argomento indirizzo come nome di un segnalibro
|
||||
- `-c, --config` Apri la configurazione di termscp
|
||||
- `-q, --quiet` Disabilita i log
|
||||
- `-t, --theme <path>` Importa il tema al percorso fornito
|
||||
- `-u, --update` Aggiorna termscp all'ultima versione
|
||||
- `-v, --version` Mostra a video le informazioni sulla versione attualmente installata
|
||||
- `-h, --help` Mostra la pagina di aiuto.
|
||||
|
||||
termscp può venire lanciato in due modalità diverse. Se nessun argomento posizionale viene fornito, termscp mostrerà il form di autenticazione, dove l'utente potrà fornire i parametri di connessione necessari.
|
||||
Alternativamente, l'utente può fornire l'argomento posizionale "indirizzo" per connettersi direttamente all'host fornito.
|
||||
Se viene fornito anche il secondo argomento posizionale, ovvero la directory locale, termscp avvierà l'explorer locale sul percorso fornito.
|
||||
|
||||
### Argomento indirizzo 🌎
|
||||
|
||||
L'argomento indirizzo ha la sintassi seguente:
|
||||
|
||||
```txt
|
||||
[protocollo://][username@]<indirizzo>[:porta][:wrkdir]
|
||||
```
|
||||
|
||||
Vediamo qualche esempio per questa sintassi, dal momento che risulta molto comodo connettersi tramite questa modalità:
|
||||
|
||||
- Connessione utilizzando il protocollo di default (definito in configurazione) a 192.168.1.31, la porta sarà quella di default per il protocollo di default. Il nome utente è quello attualmente attivo sulla propria macchina:
|
||||
|
||||
```sh
|
||||
termscp 192.168.1.31
|
||||
```
|
||||
|
||||
- Connessione con protocollo di default a 192.168.1.31, utente è `root`:
|
||||
|
||||
```sh
|
||||
termscp root@192.168.1.31
|
||||
```
|
||||
|
||||
- Connessione usando `scp`, la porta è 4022, l'utente è `omar`:
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022
|
||||
```
|
||||
|
||||
- Connessione via `scp`, porta 4022, utente `omar`, l'explorer si avvierà in `/tmp`:
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022:/tmp
|
||||
```
|
||||
|
||||
#### Argomento indirizzo per AWS S3
|
||||
|
||||
Aws S3 ha una sintassi differente dal classico argomento indirizzo, per ovvie ragioni, in quanto S3 non ha la porta o l'host o l'utente. Ho deciso però di mantenere una sintassi il più simile possibile a quella "tradizionale":
|
||||
|
||||
```txt
|
||||
s3://<bucket-name>@<region>[:profile][:/wrkdir]
|
||||
```
|
||||
|
||||
e.g.
|
||||
|
||||
```txt
|
||||
s3://buckethead@eu-central-1:default:/assets
|
||||
```
|
||||
|
||||
#### Indirizzo SMB
|
||||
|
||||
SMB ha una sintassi differente rispetto agli altri protocolli e cambia in base al sistema operativo:
|
||||
|
||||
**Windows**:
|
||||
|
||||
```txt
|
||||
\\[username@]<server-name>\<share>[\path\...]
|
||||
```
|
||||
|
||||
**Altri sistemi**:
|
||||
|
||||
```txt
|
||||
smb://[username@]<server-name>[:port]/<share>[/path/.../]
|
||||
```
|
||||
|
||||
|
||||
#### Come fornire la password 🔐
|
||||
|
||||
Quando si usa l'argomento indirizzo non è possibile fornire la password direttamente nell'argomento, esistono però altri metodi per farlo:
|
||||
|
||||
- Argomento `-P, --password <password>`: Passa direttamente la password nell'argomento. Non lo consiglio particolarmente questo metodo, in quanto la password rimarrebbe nella history della shell in chiaro.
|
||||
- Tramite `sshpass`: puoi fornire la password tramite l'applicazione GNU/Linux sshpass `sshpass -f ~/.ssh/topsecret.key termscp cvisintin@192.168.1.31`
|
||||
- Forniscila quando richiesta: se non la fornisci tramite nessun metodo precedente, alla connessione ti verrà richiesto di fornirla in un prompt che la oscurerà (come avviene con sudo tipo).
|
||||
|
||||
---
|
||||
|
||||
## Parametri di connessione S3
|
||||
|
||||
Questi parametri sono necessari per connettersi ad un bucket Aws s3 o ad uno storage compatibile:
|
||||
|
||||
- AWS S3:
|
||||
- **bucket name**
|
||||
- **region**
|
||||
- *profile* (se non fornito: "default")
|
||||
- *access key* (a meno che non sia pubblico)
|
||||
- *secret access key* (a meno che non sia pubblico)
|
||||
- *security token* (se necessario)
|
||||
- *session token* (se necessario)
|
||||
- new path style: **NO**
|
||||
- Other S3 endpoints:
|
||||
- **bucket name**
|
||||
- **endpoint**
|
||||
- *access key* (a meno che non sia pubblico)
|
||||
- *secret access key* (a meno che non sia pubblico)
|
||||
- new path style: **YES**
|
||||
|
||||
### Credenziali S3 🦊
|
||||
|
||||
Per connettersi ad un bucket S3 devi come già saprai fornire le credenziali fornite da AWS.
|
||||
Ci sono tre modi per passare queste credenziali a termscp.
|
||||
Questi sono quindi i tre modi per passare le chiavi:
|
||||
|
||||
1. Form di autenticazione:
|
||||
1. Puoi fornire la `access_key` (dovrebbe essere obbligatoria), la `secret_access_key` (dovrebbe essere obbligatoria), il `security_token` ed il `session_token`
|
||||
2. Se salvi la connessione s3 come segnalibro e decidi di salvare la password, questi parametri verranno salvati nel file dei segnalibri criptati con AES-256/BASE64; ad eccezion fatta per i due token, che dovrebbero essere credenziali temporanee, quindi inutili da salvare.
|
||||
2. Utilizza il file delle credenziali s3: configurando aws via `aws configure` le tue credenziali dovrebbero già venir salvate in `~/.aws/credentials`. Nel caso tu debba usare un profile diverso da `default`, puoi fornire un profilo diverso nell'authentication form.
|
||||
3. **Variabili d'ambiente**: nel caso il primo metodo non sia utilizzabile, puoi comunque fornirle come variabili d'ambiente. Considera però che queste variabili sovrascriveranno sempre le credenziali situate nel file credentials. Vediamo come impostarle:
|
||||
|
||||
Queste sono sempre obbligatorie:
|
||||
|
||||
- `AWS_ACCESS_KEY_ID`: aws access key ID (di solito inizia per `AKIA...`)
|
||||
- `AWS_SECRET_ACCESS_KEY`: la secret access key
|
||||
|
||||
nel caso tu abbia impostato un maggiore livello di sicurezza, potrebbero servirti anche queste:
|
||||
|
||||
- `AWS_SECURITY_TOKEN`: security token
|
||||
- `AWS_SESSION_TOKEN`: session token
|
||||
|
||||
⚠️ le tue credenziali sono al sicuro: termscp non manipola direttamente questi dati! Le credenziali sono direttamente lette dal crate di **s3**. Nel caso tu abbia dei dubbi sulla sicurezza, puoi contattare l'autore della libreria su [Github](https://github.com/durch/rust-s3) ⚠️
|
||||
|
||||
---
|
||||
|
||||
## File explorer 📂
|
||||
|
||||
Quando ci riferiamo al file explorer in termscp, intendiamo i pannelli che puoi vedere quando stabilisci una connessione con il server remoto.
|
||||
Questi pannelli sono 3 (e non 2 come sembra):
|
||||
|
||||
- Pannello locale: viene visualizzato sulla sinistra del tuo schermo e mostra la cartella sul file system locale.
|
||||
- Pannello remoto: viene visualizzato sulla destra del tuo schermo e mostra la cartella sul file system remoto.
|
||||
- Pannello di ricerca: viene visualizzato a destra o a sinistra in base a dove stai cercando dei file. Questo pannello mostra i file che matchano al pattern cercato sull'host.
|
||||
|
||||
Per cambiare pannello ti puoi muovere con le frecce, `<LEFT>` per andare sul pannello locale e `<RIGHT>` per andare su quello remoto. Attenzione che quando è attivo il pannello ricerca non puoi spostarti sugli altri pannelli e devi prima chiuderlo con `<ESC>`.
|
||||
|
||||
### Abbinamento tasti ⌨
|
||||
|
||||
| Key | Command | Reminder |
|
||||
|---------------|-------------------------------------------------------|-------------|
|
||||
| `<ESC>` | Disconnettiti; chiudi popup | |
|
||||
| `<BACKSPACE>` | Vai alla directory precedente | |
|
||||
| `<TAB>` | Cambia pannello remoto | |
|
||||
| `<RIGHT>` | Vai al pannello remoto | |
|
||||
| `<LEFT>` | Vai al pannello locale | |
|
||||
| `<UP>` | Muovi il cursore verso l'alto | |
|
||||
| `<DOWN>` | Muovi il cursore verso il basso | |
|
||||
| `<PGUP>` | Muovi il cursore verso l'alto di 8 | |
|
||||
| `<PGDOWN>` | Muovi il cursore verso il basso di 8 | |
|
||||
| `<ENTER>` | Entra nella directory | |
|
||||
| `<SPACE>` | Upload / download file selezionato/i | |
|
||||
| `<BACKTAB>` | Cambia tra explorer e pannello di log | |
|
||||
| `<A>` | Mostra/nascondi file nascosti | All |
|
||||
| `<B>` | Ordina file per | Bubblesort? |
|
||||
| `<C|F5>` | Copia file/directory | Copy |
|
||||
| `<D|F7>` | Crea directory | Directory |
|
||||
| `<E|F8|DEL>` | Elimina file | Erase |
|
||||
| `<F>` | Cerca file (wild match supportato) | Find |
|
||||
| `<G>` | Vai al percorso indicato | Go to |
|
||||
| `<H|F1>` | Mostra help | Help |
|
||||
| `<I>` | Mostra informazioni per il file selezionato | Info |
|
||||
| `<K>` | Crea un link simbolico che punta al file selezionato | symlinK |
|
||||
| `<L>` | Ricarica posizione corrente / pulisci selezione file | List |
|
||||
| `<M>` | Seleziona file | Mark |
|
||||
| `<N>` | Crea nuovo file con il nome fornito | New |
|
||||
| `<O|F4>` | Modifica file; Vedi text editor | Open |
|
||||
| `<P>` | Apri pannello log | Panel |
|
||||
| `<Q|F10>` | Termina termscp | Quit |
|
||||
| `<R|F6>` | Rinomina file | Rename |
|
||||
| `<S|F2>` | Salva file con nome | Save |
|
||||
| `<T>` | Sincronizza il percorso locale con l'host remoto | Track |
|
||||
| `<U>` | Vai alla directory padre | Upper |
|
||||
| `<V|F3>` | Apri il file con il programma definito dal sistema | View |
|
||||
| `<W>` | Apri il file con il programma specificato | With |
|
||||
| `<X>` | Esegui comando shell | eXecute |
|
||||
| `<Y>` | Abilita/disabilita Sync-Browsing | sYnc |
|
||||
| `<Z>` | Modifica permessi file | |
|
||||
| `<CTRL+A>` | Seleziona tutti i file | |
|
||||
| `<CTRL+C>` | Annulla trasferimento file | |
|
||||
| `<CTRL+T>` | Visualizza tutti i percorsi sincronizzati | Track |
|
||||
|
||||
### Lavora su più file 🥷
|
||||
|
||||
Puoi lavorare su una selezione di file, marcandoli come selezionati tramite `<M>`, per selezionare il file corrente o con `<CTRL+A` per selezionarli tutti.
|
||||
Una volta che un file è marcato, sarà visualizzato con un `*` prima del nome.
|
||||
Quando lavori con una selezioni, solo i file selezionati saranno presi in considerazione (l'eventuale file evidenziato sarà ignorato).
|
||||
È possibile operare su più file anche nel pannello di ricerca.
|
||||
Tutte le azioni sono disponibili quando si lavora sulle selezioni, ma occhio, che alcune azioni si comporteranno in maniera leggermente differente. Vediamo quali e come:
|
||||
|
||||
- *Copia*: Se copi un file, ti verrà richiesto di inserire il nome delle destinazione, ma quando lavori con la selezione, il nome si riferisce alla directory di destinazione, mentre il nome del file rimarrà inviariato.
|
||||
- *Rinomina*: Come il copia, ma li sposterà.
|
||||
- *Salva con nome*: Come il copia, ma li trasferirà.
|
||||
|
||||
### Synchronized browsing ⏲️
|
||||
|
||||
Quando abilitato, ti permetterà di sincronizzare la navigazione tra i due pannelli.
|
||||
Ciò comporta che quando cambierai directory in uno dei due pannelli, lo stesso verrà fatto nell'altro. Per abilitare la modalità è sufficiente premere `<Y>`; fai lo stesso per disabilitarlo. Mentre abilitato, sull'interfaccia dovrebbe essere visualizzato `Sync Browsing: ON` nella barra di stato.
|
||||
|
||||
### Apri e apri con 🚪
|
||||
|
||||
I comandi "apri" e "apri con" sono forniti da [open-rs](https://docs.rs/crate/open/2.1.0).
|
||||
Quando apri un file (`<V>`), l'applicazione predefinita di sistema sarà utilizzata per aprire il file. Per fare ciò, sul tuo sistema dovrà essere usato il servizio di default del sistema.
|
||||
|
||||
- **Windows**: non devi installare niente, è già presente sul sistema.
|
||||
- **MacOS**: non devi installare niente, è già presente sul sistema.
|
||||
- **Linux**: uno di questi dev'essere presente (potrebbe già esserlo):
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- **WSL**: *wslview* è richiesto, lo puoi installare tramite questa suite [wslu](https://github.com/wslutilities/wslu).
|
||||
|
||||
> Q: Posso modificare i file su remoto tramite la funzionalità "apri" / "apri con"?
|
||||
> A: No, almeno non direttamente dal pannello remoto. Devi prima scaricarlo in locale, modificarlo e poi ricaricarlo. Questo perché il file remoto viene scaricato come file temporaneo in locale, ma non esiste poi un modo per sapere quando è stato modificato e quando l'utente ha effettivamente finito di lavorarci.
|
||||
|
||||
---
|
||||
|
||||
## Segnalibri ⭐
|
||||
|
||||
In termscp è possibile salvare i tuoi host preferiti tramite i segnalibri al fine di connettersi velocemente ad essi.
|
||||
Termscp salverà anche gli ultimi 16 host ai quali ti sei connesso.
|
||||
Questa funzionalità ti permette di caricare tutti i parametri necessari per connettersi ad un certo host, semplicemente selezioandolo dal tab dei preferiti nel form di autenticazione.
|
||||
|
||||
I preferiti saranno salvati se possibile presso:
|
||||
|
||||
- `$HOME/.config/termscp/` su Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` su MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` su Windows
|
||||
|
||||
Per i segnalibri (ma non per le connessioni recenti), è anche possibile salvare la password. La password non viene salvata di default e deve essere specificato tramite apposita opzione, al momento della creazione del segnalibro stesso.
|
||||
Se sei preoccupato riguardo alla sicurezza della password per i segnalibri, dai un'occhiata al capitolo qui sotto 👀.
|
||||
|
||||
Per creare un segnalibro, segui questa procedura:
|
||||
|
||||
1. Inserisci i parametri per connetterti all'host che vuoi inserire come segnalibro nell'authentication form.
|
||||
2. Premi `<CTRL+S>`
|
||||
3. Inserisci il nome che vuoi dare al bookmark
|
||||
4. Seleziona nel radio button se salvare la password
|
||||
5. Premi `<ENTER>` per salvare
|
||||
|
||||
Quando vuoi caricare un segnalibro, premi `<TAB>` e naviga nella lista dei segnalibri fino al segnalibro che vuoi caricare, quindi premi `<ENTER>`.
|
||||
|
||||

|
||||
|
||||
### Le mie password sono al sicuro 😈
|
||||
|
||||
Certo 😉.
|
||||
Come detto in precedenza, i segnalibri sono salvati nella cartella delle configurazioni insieme alle password. Le password però non sono in chiaro, ma bensì sono criptate con **AES-128**. Questo le rende sicure? Sì! Does this make them safe? (salvo che per gli utenti di FreeBSD e WSL 😢)
|
||||
|
||||
In **Windows**, **Linux** and **MacOS** la chiave per criptare le password è salvata, se possibile, rispettivamente nel *Windows Vault*, nel *system keyring* e nel *Keychain*. Questo sistema è super-sicuro, in quanto garantito direttamente dal tuo sistema operativo.
|
||||
|
||||
❗ Attenzione che se sei un utente Linux, dovresti leggere il capitolo qui sotto riguardante il linux keyring 👀, questo perché il keyring potrebbe non essere ancora presente sul tuo sistema.
|
||||
|
||||
Su *FreeBSD* e *WSL*, d'altro canto, la chiave utilizzata per criptare le password è salvata su file presso (at $HOME/.config/termscp). È quindi possibile per un malintenzionato ottenere la chiave. Per fortuna essendo sotto la tua home, non dovrebbe essere possibile accedere al file, se non con il tuo utente, ma comunque per sicurezza ti consiglio di non salvare dati sensibili 😉.
|
||||
|
||||
#### Linux Keyring
|
||||
|
||||
Tutti gli amanti di Linux lo preferiscono per la libertà che questo dà agli utenti nella personalizzazione. Allo stesso tempo però questo spesso comporta degli effetti collaterali, tra cui la mancanza spesso di un'imposizione da parte dei creatori delle distro di standard e applicazioni e questo fatto coinvolge anche la questione del keyring.
|
||||
Su alcuni sistemi di default, non c'è nessun provider di keyring, perché la distro dà all'utente la possibilità di sceglierne uno.
|
||||
termscp richiede un servizio D-BUS che fornisce `org.freedesktop.secrets` e purtroppo ci sono ad oggi solo due servizi mantenuti che lo supportano.
|
||||
|
||||
- ❗ Se usi GNOME come Desktop environment (come gli utenti Ubuntu), dovresti già averne uno installato sul sistema, chiamato `gnome-keyring` e quindi dovrebbe già funzionare tutto.
|
||||
- ❗ Se invece usi un altro DE, dovresti installare [KeepassXC](https://keepassxc.org/), che io per esempio utilizzo sul mio Manjaro Linux (con KDE) e funziona piuttosto bene. L'unico problema è che dovrai fare il setup per farlo funzionare. Per farlo puoi leggere il tutorial [qui](#keepassxc-setup-per-termscp)
|
||||
- ❗ Se non volessi installare uno di questi servizi, termscp funzionerà come sempre, l'unica differenza sarà che salverà la chiave di crittazione su un file, come fa per FreeBSD e WSL.
|
||||
|
||||
##### KeepassXC setup per termscp
|
||||
|
||||
Questo tutorial spiega come impostare KeepassXC per termscp.
|
||||
|
||||
1. Installa KeepassXC dal sito ufficiale <https://keepassxc.org/>
|
||||
2. Una volta avviato, vai su "strumenti" > "impostazioni" nella toolbar
|
||||
3. Seleziona "Secret service integration" e abilita "Enable KeepassXC freedesktop.org secret service integration"
|
||||
4. Crea un database se non ne hai già uno: dalla toolbar "Database" > "Nuovo database"
|
||||
5. Dalla toolbar: "Database" > "Impostazioni database"
|
||||
6. Seleziona "Secret service integration" e abilita "Expose entries under this group"
|
||||
7. Seleziona il gruppo in cui vuoi salvare le chiavi di termscp. Attenzione che questo gruppo sarà utilizzato da tutte le altre eventuali applicazioni che salvano le password via D-BUS.
|
||||
|
||||
---
|
||||
|
||||
## Configurazione ⚙️
|
||||
|
||||
termscp supporta diversi parametri definiti dall'utente, che possono essere impostati nella configurazione.
|
||||
termscp usa un file TOML e altre directory per salvare tutti i parametri, ma non preoccuparti, tutto può essere comodamente configurato da interfaccia grafica.
|
||||
|
||||
Per la configurazione, termscp richiede che i seguenti percorsi siano accessibili (termscp proverà a crearli per te):
|
||||
|
||||
- `$HOME/.config/termscp/` su Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` su MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` su Windows
|
||||
|
||||
Per accedere alla configurazione è sufficiente premere `<CTRL+C>` dall'authentication form.
|
||||
|
||||
Questi parametri possono essere impostati:
|
||||
|
||||
- **Text Editor**: l'editor di testo da utilizzare per aprire i file. Di default termscp userà quello definito nella variabile `EDITOR` od il primo che troverà installato tra quelli più popolari. Puoi tuttavia definire quello che vuoi (ad esempio `vim`). **Anche gli editor GUI sono supportati**, a meno che loro non partano in `nohup` dal processo padre.
|
||||
- **Default Protocol**: il protocollo di default da visualizzare come prima opzione nell'authentication form. Questa opzione sarà anche utilizzata quando si usa l'argomento indirizzo da CLI e non si specifica un protocollo.
|
||||
- **Show Hidden Files**: seleziona se mostrare di default i file nascosti. A runtime potrai comunque scegliere se visualizzarli o meno premendo `<A>`.
|
||||
- **Check for updates**: se impostato a `YES` all'avvio termscp controllerà l'eventuale presenza di aggiornamenti. Per farlo utilizzerà una chiamata GET all'API di Github.
|
||||
- **Prompt when replacing existing files?**: se impostato a `yes`, termscp ti chiederà una conferma prima di sovrascrivere un file a seguito di un download/upload.
|
||||
- **Group Dirs**: seleziona se e come raggruppare le cartelle negli explorer. Se `Display first` è impostato, le directory verranno ordinate secondo quanto stabilito nel `sort by`, ma verranno messe prima dei file, viceversa se `Display last` è utilizzato. Se invece metti `no`, le cartelle verrano messe in ordine assieme ad i file.
|
||||
- **Remote File formatter syntax**: La formattazione da usare per formattare i file sull'explorer remoto. Vedi [File explorer format](#file-explorer-format)
|
||||
- **Local File formatter syntax**: La formattazione da usare per formattare i file sull'explorer locale. Vedi [File explorer format](#file-explorer-format)
|
||||
- **Enable notifications?**: Se impostato a `yes`, le notifiche desktop saranno abilitate.
|
||||
- **Notifications: minimum transfer size**: se la dimensione di un trasferimento supera o è uguale al valore impostato, al termine del trasferimento riceverai una notifica desktop (se queste sono abilitate). Il formato del valore dev'essere `{UNSIGNED} B/KB/MB/GB/TB/PB`
|
||||
- **SSH configuration path**: Imposta il percorso del file di configurazione per SSH, per quando ci si connette ad un server SFTP/SCP. Se lasciato vuoto, nessun file verrà usato. Il percorso può anche iniziare con `~` per indicare il percorso della home dell'utente attuale (e.s. `~/.ssh/config`). I parametri supportati dalla configurazioni sono descritti [QUI](https://github.com/veeso/ssh2-config#exposed-attributes).
|
||||
|
||||
### SSH Key Storage 🔐
|
||||
|
||||
Assieme alla configurazione termscp supporta anche una feature essenziale per i client **SFTP/SCP**: lo storage di chiavi SSH.
|
||||
|
||||
Puoi accedere allo storage muovendoti nel tab delle chiavi SSH tramite `<TAB>` dalla configurazione.
|
||||
|
||||
- **Aggiungere chiavi**: premi `<CTRL+N>` e ti verrà chiesto di creare una nuova chiave. Inserisci l'hostname/indirizzo ed il nome utente, infine una volta che premerai invio, ti si aprirà l'editor di testo: incolla la chiave SSH **PRIVATA**, salva ed esci.
|
||||
- **Rimuovi una chiave esistente**: premi `<DEL>` o `<CTRL+E>` selezionando la chiave da rimuovere.
|
||||
- **Aggiorna una chiave esistente**: premi `<ENTER>` sulla chiave che vuoi modificare.
|
||||
|
||||
> Q: Se la mia chiave è protetta da password, posso comunque usarla?
|
||||
> A: Sì, certo. In questo caso dovrai fornire la password come faresti per autenticarti con utente/password, ma in questo caso la password sarà usata per decrittare la chiave.
|
||||
|
||||
### File Explorer Format
|
||||
|
||||
È possibile dalla configurazione impostare la formattazione dei file sull'explorer. È possibile sia farlo per il pannello locale, che per quello remoto; quindi puoi avere due sintassi diverse. Questi campi, con nome `File formatter syntax (local)` and `File formatter syntax (remote)` definiranno come i file devono essere formattati sull'explorer.
|
||||
La sintassi è la seguente `{KEY1}... {KEY2:LENGTH}... {KEY3:LENGTH:EXTRA} {KEYn}...`.
|
||||
Ogni chiave sarà rimpiazzata dal formatter con il relativo attributo, mentre tutto ciò che è fuori dalle parentesi graffe rimarrà inviariato (quindi puoi metterci del testo arbitratio).
|
||||
|
||||
- Il nome della chiave è obbligatorio e dev'essere uno di quelli sotto.
|
||||
- La lunghezza descrive quanto spazio in caratteri riservare al campo. Attributi con dimensione statico (GROUP, PEX, SIZE, USER) non supportano la lunghezza.
|
||||
- L'extra serve a definire degli attributi in più. Solo alcuni lo supportano.
|
||||
|
||||
These are the keys supported by the formatter:
|
||||
|
||||
- `ATIME`: Last access time (con sintassi di default `%b %d %Y %H:%M`); Extra definisce il formato data (e.g. `{ATIME:8:%H:%M}`)
|
||||
- `CTIME`: Creation time (con sintassi di default `%b %d %Y %H:%M`); Extra definisce il formato data (e.g. `{CTIME:8:%H:%M}`)
|
||||
- `GROUP`: Owner group
|
||||
- `MTIME`: Last change time (con sintassi di default `%b %d %Y %H:%M`); Extra definisce il formato data (e.g. `{MTIME:8:%H:%M}`)
|
||||
- `NAME`: Nome file (Le cartelle comprese tra la root ed il genitore del file sono omessi se la lunghezza è maggiore di LENGTH)
|
||||
- `PATH`: Percorso assoluto del file (Le cartelle comprese tra la root ed il genitore del file sono omessi se la lunghezza è maggiore di LENGHT)
|
||||
- `PEX`: Permessi utente (formato UNIX)
|
||||
- `SIZE`: Dimensione file (omesso per le directory)
|
||||
- `SYMLINK`: Link simbolico (se presente `-> {FILE_PATH}`)
|
||||
- `USER`: Owner user
|
||||
|
||||
Se lasciata vuota, la sintassi di default sarà utilizzata: `{NAME:24} {PEX} {USER} {SIZE} {MTIME:17:%b %d %Y %H:%M}`
|
||||
|
||||
---
|
||||
|
||||
## Temi 🎨
|
||||
|
||||
termscp fornisce anche una funzionalità strafiga: la possibilità di impostare i colori per tutta l'interfaccia.
|
||||
Se vuoi impostare i colori, ci sono due modi per farlo:
|
||||
|
||||
- dal **menù di configurazione**
|
||||
- importando un **tema** da file
|
||||
|
||||
Per personalizzare i colori dovrai andare nella configurazione temi, partendo dal menù di autenticazione, premendo `<CTRL+C>` e premendo due volte `<TAB>`. Dovresti essere quindi in configurazione nel tab `themes`.
|
||||
|
||||
Da qui puoi spostarti con le frecce per cambiare lo stile che vuoi, come mostrato nella GIF qua sotto:
|
||||
|
||||

|
||||
|
||||
termscp supporta diverse sintassi per i colori, sia il formato hex (`#rrggbb`) che rgb `rgb(r, g, b)`, ma anche i **[colori CSS](https://www.w3schools.com/cssref/css_colors.asp)** (tipo `crimson`) 😉. C'è anche una chiave speciale `Default`. Default significa che per il colore verrà usato il default in base al tipo di elemento (foreground per i testi e linee, background per gli sfondi e i riempimenti).
|
||||
|
||||
Come detto già in precedenza, puoi anche importare i temi da file. Volendo puoi anche creare un tema prendendo ispirazione da quelli situati nella cartella `themes/` del repository ed importarli su termscp con `termscp -t <theme_file>`. Se l'operazione va a buon fine dovrebbe dirti che l'ha importato con successo.
|
||||
|
||||
### Il tema non carica 😱
|
||||
|
||||
Probabilmente è dovuto ad un aggiornamento che ha rotto il tema. Se viene aggiunta una nuova chiave nel tema (ma questo accade molto raramente), il tema non verrà più caricato. Ci sono diverse soluzioni veloci per questo problema.
|
||||
|
||||
1. Ricarica il tema: se stai usando un tema "ufficiale" fornito nel repository, basterà ricaricarlo, perché li aggiorno sempre quando modifico i temi:
|
||||
|
||||
```sh
|
||||
termscp -t <theme.toml>
|
||||
```
|
||||
|
||||
2. Sistema il tuo tema a mano: puoi modificare il tuo tema con un editor di testo tipo `vim` e aggiungere la chiave mancante. Il il tema si trova in `$CONFIG_DIR/termscp/theme.toml` dove `$CONFIG_DIR` è:
|
||||
|
||||
- FreeBSD/GNU-Linux: `$HOME/.config/`
|
||||
- MacOs: `$HOME/Library/Application Support`
|
||||
- Windows: `%appdata%`
|
||||
|
||||
❗ Le chiavi mancanti vengono riportate nel CHANGELOG sotto `BREAKING CHANGES` per la versione installata.
|
||||
|
||||
### Stili 💈
|
||||
|
||||
Puoi trovare qui sotto la definizione per ogni chiave.
|
||||
Attenzione che gli stili **non coinvolgono la pagina di configurazione**, per renderla sempre accessibile nel caso gli stili siano inutilizzabili.
|
||||
|
||||
#### Pagina autenticazione
|
||||
|
||||
| Key | Description |
|
||||
|----------------|------------------------------------|
|
||||
| auth_address | Colore del campo indirizzo IP |
|
||||
| auth_bookmarks | Colore del pannello segnalibri |
|
||||
| auth_password | Colore del campo password |
|
||||
| auth_port | Colore del campo numero porta |
|
||||
| auth_protocol | Colore del selettore di protocollo |
|
||||
| auth_recents | Colore del pannello recenti |
|
||||
| auth_username | Colore del campo nome utente |
|
||||
|
||||
#### Pagina explorer e trasferimento
|
||||
|
||||
| Key | Description |
|
||||
|--------------------------------------|---------------------------------------------------------------------------|
|
||||
| transfer_local_explorer_background | Sfondo explorer locale |
|
||||
| transfer_local_explorer_foreground | Foreground explorer locale |
|
||||
| transfer_local_explorer_highlighted | Colore bordo e file selezionato explorer locale |
|
||||
| transfer_remote_explorer_background | Sfondo explorer remoto |
|
||||
| transfer_remote_explorer_foreground | Foreground explorer remoto |
|
||||
| transfer_remote_explorer_highlighted | Colore bordo e file selezionato explorer remoto |
|
||||
| transfer_log_background | Sfondo pannello di log |
|
||||
| transfer_log_window | Colore bordi e testo log |
|
||||
| transfer_progress_bar_partial | Colore barra progresso parziale |
|
||||
| transfer_progress_bar_total | Colore barra progresso totale |
|
||||
| transfer_status_hidden | Colore status bar file nascosti |
|
||||
| transfer_status_sorting | Colore status bar ordinamento file; si applica anche al popup ordinamento |
|
||||
| transfer_status_sync_browsing | Colore status bar per sync browsing |
|
||||
|
||||
#### Misc
|
||||
|
||||
Questi stili si applicano a varie componenti dell'applicazione.
|
||||
|
||||
| Key | Description |
|
||||
|-------------------|---------------------------------------------|
|
||||
| misc_error_dialog | Colore dialoghi errore |
|
||||
| misc_info_dialog | Colore per dialoghi informazioni |
|
||||
| misc_input_dialog | Colore per dialoghi input (tipo copia file) |
|
||||
| misc_keys | Colore per abbinamento tasti |
|
||||
| misc_quit_dialog | Colore per dialogo quit |
|
||||
| misc_save_dialog | Colore per dialogo salva |
|
||||
| misc_warn_dialog | Colore per dialoghi avvertimento |
|
||||
|
||||
---
|
||||
|
||||
## Editor di testo ✏
|
||||
|
||||
Con termscp puoi anche modificare i file di testo direttamente da terminale, utilizzando il tuo editor preferito.
|
||||
Non importa se il file si trova in locale od in remoto, termscp ti consente di modificare e sincronizzare le modifiche per entrambi.
|
||||
Nel caso il file si trovi su host remoto, il file verrà prima scaricato temporaneamente in locale, modificato e poi nel caso ci siano state modifiche, reinviato in remoto.
|
||||
|
||||
> ❗ Ricorda: **puoi modificare solo i file testuali**; non puoi modificare i file binari.
|
||||
|
||||
---
|
||||
|
||||
## Logging 🩺
|
||||
|
||||
termscp scrive un file di log per ogni sessione, nel percorso seguente:
|
||||
|
||||
- `$HOME/.cache/termscp/termscp.log` su Linux/BSD
|
||||
- `$HOME/Library/Caches/termscp/termscp.log` su MacOs
|
||||
- `FOLDERID_LocalAppData\termscp\termscp.log` su Windows
|
||||
|
||||
Il log non viene ruotato, ma viene troncato ad ogni lancio di termscp, quindi se devi riportare un issue, non avviare termscp fino a che non avrai salvato il file di log.
|
||||
I log sono di default riportati a livello *INFO*, quindi non sono particolarmente parlanti.
|
||||
|
||||
Se vuoi riportare un problema, se riesci, riproduci l'errore lanciando termscp in modalità di debug, in modo da fornire un log più dettagliato.
|
||||
Per farlo, lancia termscp con l'opzione `-D`.
|
||||
|
||||
Ho scritto questo FAQ sui log, visto che potresti avere qualche dubbio:
|
||||
|
||||
> Non voglio il log, posso disabilitarlo?
|
||||
|
||||
Sì, puoi. Basta lanciare termscp con `-q or --quiet` come opzione. Puoi mantenerlo persistente salvandolo come alias nella tua shell. Ricorda che i log vengono usati per diagnosticare problemi e considerando che questo è un progetto open-source è anche un modo per contribuire al progetto 😉. Non voglio far sentire in colpa nessuno, ma tanto per dire.
|
||||
|
||||
> Il log è sicuro?
|
||||
|
||||
Se ti chiedi se il log espone dati sensibili, il log non espone nessuna password o dato sensibile.
|
||||
|
||||
## Notifiche 📫
|
||||
|
||||
termscp invierà notifiche destkop per i seguenti eventi:
|
||||
|
||||
- a **Transferimento completato**: La notifica verrà inviata a seguito di un trasferimento completato.
|
||||
- ❗ La notifica verrà mostrata solo se la dimensione totale del trasferimento è uguale o maggiore al parametro `Notifications: minimum transfer size` definito in configurazione.
|
||||
- a **Transferimento fallito**: La notifica verrà inviata a seguito di un trasferimento fallito.
|
||||
- ❗ La notifica verrà mostrata solo se la dimensione totale del trasferimento è uguale o maggiore al parametro `Notifications: minimum transfer size` definito in configurazione.
|
||||
- ad **Aggiornamento disponibile**: Ogni volta che una nuova versione di termscp è disponibile, verrà mostrata una notifica.
|
||||
- ad **Aggiornamento installato**: Al termine dell'installazione di un aggiornamento, verrà mostrata una notifica.
|
||||
- ad **Aggiornamento fallito**: Al fallimento dell'installazione di un aggiornamento, verrà mostrata una notifica.
|
||||
|
||||
❗ Se vuoi disabilitare le notifiche, è sufficiente andare in configurazione ed impostare `Enable notifications?` a `No` 😉.
|
||||
❗ Se vuoi modificare la soglia minima per le notifiche dei trasferimenti, puoi impostare il valore di `Notifications: minimum transfer size` in configurazione 🙂.
|
||||
|
||||
## File watcher 🔭
|
||||
|
||||
Il file watcher ti permette di impostare una lista di percorsi da sincronizzare con l'host remoto.
|
||||
Ciò implica che ogni volta che una modifica verrà rilevata al percorso sincronizzato, la modifica verrà automaticamente sincronizzata con l'host remoto, entro 5 secondi.
|
||||
|
||||
Puoi impostare quanti percorsi preferisci da sincronizzare:
|
||||
|
||||
1. Porta il cursore dell'explorer sulla cartella/file che vuoi sincronizzare
|
||||
2. Vai alla directory sull'explorer remoto dove vuoi riportare le modifiche
|
||||
3. Premi `<T>`
|
||||
4. Rispondi `<YES>` alla domanda se vuoi sincronizzare il percorso
|
||||
|
||||
Per terminare la sincronizzazione, premi `<T>`, al percorso locale sincronizzato (od in qualsiasi sua sottocartella)
|
||||
OPPURE, puoi semplicemente premere `<CTRL+T>` e premi `<ENTER>` sul percorso che vuoi desincronizzare.
|
||||
|
||||
Queste modifiche verranno applicate sull'host remoto:
|
||||
|
||||
- Nuovi file, modifiche
|
||||
- File spostati o rinominati
|
||||
- File rimossi
|
||||
|
||||
> ❗ Il watcher funziona solo in maniera unidirezionale locale > remoto. NON è possibile tracciare le modifiche da remoto a locale.
|
||||
@@ -1,559 +0,0 @@
|
||||
# User manual 🎓
|
||||
|
||||
- [User manual 🎓](#user-manual-)
|
||||
- [Usage ❓](#usage-)
|
||||
- [Address argument 🌎](#address-argument-)
|
||||
- [AWS S3 address argument](#aws-s3-address-argument)
|
||||
- [SMB address argument](#smb-address-argument)
|
||||
- [How Password can be provided 🔐](#how-password-can-be-provided-)
|
||||
- [S3 connection parameters](#s3-connection-parameters)
|
||||
- [S3 credentials 🦊](#s3-credentials-)
|
||||
- [File explorer 📂](#file-explorer-)
|
||||
- [Keybindings ⌨](#keybindings-)
|
||||
- [Work on multiple files 🥷](#work-on-multiple-files-)
|
||||
- [Synchronized browsing ⏲️](#synchronized-browsing-️)
|
||||
- [Open and Open With 🚪](#open-and-open-with-)
|
||||
- [Bookmarks ⭐](#bookmarks-)
|
||||
- [Are my passwords Safe 😈](#are-my-passwords-safe-)
|
||||
- [Linux Keyring](#linux-keyring)
|
||||
- [KeepassXC setup for termscp](#keepassxc-setup-for-termscp)
|
||||
- [Configuration ⚙️](#configuration-️)
|
||||
- [SSH Key Storage 🔐](#ssh-key-storage-)
|
||||
- [File Explorer Format](#file-explorer-format)
|
||||
- [Themes 🎨](#themes-)
|
||||
- [My theme won't load 😱](#my-theme-wont-load-)
|
||||
- [Styles 💈](#styles-)
|
||||
- [Authentication page](#authentication-page)
|
||||
- [Transfer page](#transfer-page)
|
||||
- [Misc](#misc)
|
||||
- [Text Editor ✏](#text-editor-)
|
||||
- [Logging 🩺](#logging-)
|
||||
- [Notifications 📫](#notifications-)
|
||||
- [File watcher 🔭](#file-watcher-)
|
||||
|
||||
## Usage ❓
|
||||
|
||||
termscp can be started with the following options:
|
||||
|
||||
`termscp [options]... [protocol://user@address:port:wrkdir] [local-wrkdir]`
|
||||
|
||||
OR
|
||||
|
||||
`termscp [options]... -b [bookmark-name] [local-wrkdir]`
|
||||
|
||||
- `-P, --password <password>` if address is provided, password will be this argument
|
||||
- `-b, --address-as-bookmark` resolve address argument as a bookmark name
|
||||
- `-c, --config` Open termscp starting from the configuration page
|
||||
- `-q, --quiet` Disable logging
|
||||
- `-t, --theme <path>` Import specified theme
|
||||
- `-u, --update` Update termscp to latest version
|
||||
- `-v, --version` Print version info
|
||||
- `-h, --help` Print help page
|
||||
|
||||
termscp can be started in three different modes, if no extra arguments is provided, termscp will show the authentication form, where the user will be able to provide the parameters required to connect to the remote peer.
|
||||
|
||||
Alternatively, the user can provide an address as argument to skip the authentication form and starting directly the connection to the remote server.
|
||||
|
||||
If address argument or bookmark name is provided you can also provide the start working directory for local host
|
||||
|
||||
### Address argument 🌎
|
||||
|
||||
The address argument has the following syntax:
|
||||
|
||||
```txt
|
||||
[protocol://][username@]<address>[:port][:wrkdir]
|
||||
```
|
||||
|
||||
Let's see some example of this particular syntax, since it's very comfortable and you'll probably going to use this instead of the other one...
|
||||
|
||||
- Connect using default protocol (*defined in configuration*) to 192.168.1.31, port if not provided is default for the selected protocol (in this case depends on your configuration); username is current user's name
|
||||
|
||||
```sh
|
||||
termscp 192.168.1.31
|
||||
```
|
||||
|
||||
- Connect using default protocol (*defined in configuration*) to 192.168.1.31; username is `root`
|
||||
|
||||
```sh
|
||||
termscp root@192.168.1.31
|
||||
```
|
||||
|
||||
- Connect using scp to 192.168.1.31, port is 4022; username is `omar`
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022
|
||||
```
|
||||
|
||||
- Connect using scp to 192.168.1.31, port is 4022; username is `omar`. You will start in directory `/tmp`
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022:/tmp
|
||||
```
|
||||
|
||||
#### AWS S3 address argument
|
||||
|
||||
Aws S3 has a different syntax for CLI address argument, for obvious reasons, but I managed to keep it the more similar as possible to the generic address argument:
|
||||
|
||||
```txt
|
||||
s3://<bucket-name>@<region>[:profile][:/wrkdir]
|
||||
```
|
||||
|
||||
e.g.
|
||||
|
||||
```txt
|
||||
s3://buckethead@eu-central-1:default:/assets
|
||||
```
|
||||
|
||||
#### SMB address argument
|
||||
|
||||
SMB has a different syntax for CLI address argument, which is different whether you're on Windows or other systems:
|
||||
|
||||
**Windows** syntax:
|
||||
|
||||
```txt
|
||||
\\[username@]<server-name>\<share>[\path\...]
|
||||
```
|
||||
|
||||
**Other systems** syntax:
|
||||
|
||||
```txt
|
||||
smb://[username@]<server-name>[:port]/<share>[/path/.../]
|
||||
```
|
||||
|
||||
#### How Password can be provided 🔐
|
||||
|
||||
You have probably noticed, that, when providing the address as argument, there's no way to provide the password.
|
||||
Password can be basically provided through 3 ways when address argument is provided:
|
||||
|
||||
- `-P, --password` option: just use this CLI option providing the password. I strongly unrecommend this method, since it's very insecure (since you might keep the password in the shell history)
|
||||
- Via `sshpass`: you can provide password via `sshpass`, e.g. `sshpass -f ~/.ssh/topsecret.key termscp cvisintin@192.168.1.31`
|
||||
- You will be prompted for it: if you don't use any of the previous methods, you will be prompted for the password, as happens with the more classics tools such as `scp`, `ssh`, etc.
|
||||
|
||||
---
|
||||
|
||||
## S3 connection parameters
|
||||
|
||||
These parameters are required to connect to aws s3 and other s3 compatible servers:
|
||||
|
||||
- AWS S3:
|
||||
- **bucket name**
|
||||
- **region**
|
||||
- *profile* (if not provided: "default")
|
||||
- *access key* (unless if public)
|
||||
- *secret access key* (unless if public)
|
||||
- *security token* (if required)
|
||||
- *session token* (if required)
|
||||
- new path style: **NO**
|
||||
- Other S3 endpoints:
|
||||
- **bucket name**
|
||||
- **endpoint**
|
||||
- *access key* (unless if public)
|
||||
- *secret access key* (unless if public)
|
||||
- new path style: **YES**
|
||||
|
||||
### S3 credentials 🦊
|
||||
|
||||
In order to connect to an Aws S3 bucket you must obviously provide some credentials.
|
||||
There are basically three ways to achieve this:
|
||||
So these are the ways you can provide the credentials for s3:
|
||||
|
||||
1. Authentication form:
|
||||
1. You can provide the `access_key` (should be mandatory), the `secret_access_key` (should be mandatory), `security_token` and the `session_token`
|
||||
2. If you save the s3 connection as a bookmark, these credentials will be saved as an encrypted AES-256/BASE64 string in your bookmarks file (except for the security token and session token which are meant to be temporary credentials).
|
||||
2. Use your credentials file: just configure the AWS cli via `aws configure` and your credentials should already be located at `~/.aws/credentials`. In case you're using a profile different from `default`, just provide it in the profile field in the authentication form.
|
||||
3. **Environment variables**: you can always provide your credentials as environment variables. Keep in mind that these credentials **will always override** the credentials located in the `credentials` file. See how to configure the environment below:
|
||||
|
||||
These should always be mandatory:
|
||||
|
||||
- `AWS_ACCESS_KEY_ID`: aws access key ID (usually starts with `AKIA...`)
|
||||
- `AWS_SECRET_ACCESS_KEY`: the secret access key
|
||||
|
||||
In case you've configured a stronger security, you *may* require these too:
|
||||
|
||||
- `AWS_SECURITY_TOKEN`: security token
|
||||
- `AWS_SESSION_TOKEN`: session token
|
||||
|
||||
⚠️ Your credentials are safe: termscp won't manipulate these values directly! Your credentials are directly consumed by the **s3** crate.
|
||||
In case you've got some concern regarding security, please contact the library author on [Github](https://github.com/durch/rust-s3) ⚠️
|
||||
|
||||
---
|
||||
|
||||
## File explorer 📂
|
||||
|
||||
When we refer to file explorers in termscp, we refer to the panels you can see after establishing a connection with the remote.
|
||||
These panels are basically 3 (yes, three actually):
|
||||
|
||||
- Local explorer panel: it is displayed on the left of your screen and shows the current directory entries for localhost
|
||||
- Remote explorer panel: it is displayed on the right of your screen and shows the current directory entries for the remote host.
|
||||
- Find results panel: depending on where you're searching for files (local/remote) it will replace the local or the explorer panel. This panel shows the entries matching the search query you performed.
|
||||
|
||||
In order to change panel you need to type `<LEFT>` to move the remote explorer panel and `<RIGHT>` to move back to the local explorer panel. Whenever you are in the find results panel, you need to press `<ESC>` to exit panel and go back to the previous panel.
|
||||
|
||||
### Keybindings ⌨
|
||||
|
||||
| Key | Command | Reminder |
|
||||
|---------------|---------------------------------------------------------|-------------|
|
||||
| `<ESC>` | Disconnect from remote; return to authentication page | |
|
||||
| `<BACKSPACE>` | Go to previous directory in stack | |
|
||||
| `<TAB>` | Switch explorer tab | |
|
||||
| `<RIGHT>` | Move to remote explorer tab | |
|
||||
| `<LEFT>` | Move to local explorer tab | |
|
||||
| `<UP>` | Move up in selected list | |
|
||||
| `<DOWN>` | Move down in selected list | |
|
||||
| `<PGUP>` | Move up in selected list by 8 rows | |
|
||||
| `<PGDOWN>` | Move down in selected list by 8 rows | |
|
||||
| `<ENTER>` | Enter directory | |
|
||||
| `<SPACE>` | Upload / download selected file | |
|
||||
| `<BACKTAB>` | Switch between log tab and explorer | |
|
||||
| `<A>` | Toggle hidden files | All |
|
||||
| `<B>` | Sort files by | Bubblesort? |
|
||||
| `<C|F5>` | Copy file/directory | Copy |
|
||||
| `<D|F7>` | Make directory | Directory |
|
||||
| `<E|F8|DEL>` | Delete file | Erase |
|
||||
| `<F>` | Search for files (wild match is supported) | Find |
|
||||
| `<G>` | Go to supplied path | Go to |
|
||||
| `<H|F1>` | Show help | Help |
|
||||
| `<I>` | Show info about selected file or directory | Info |
|
||||
| `<K>` | Create symlink pointing to the currently selected entry | symlinK |
|
||||
| `<L>` | Reload current directory's content / Clear selection | List |
|
||||
| `<M>` | Select a file | Mark |
|
||||
| `<N>` | Create new file with provided name | New |
|
||||
| `<O|F4>` | Edit file; see Text editor | Open |
|
||||
| `<P>` | Open log panel | Panel |
|
||||
| `<Q|F10>` | Quit termscp | Quit |
|
||||
| `<R|F6>` | Rename file | Rename |
|
||||
| `<S|F2>` | Save file as... | Save |
|
||||
| `<T>` | Synchronize changes to selected path to remote | Track |
|
||||
| `<U>` | Go to parent directory | Up |
|
||||
| `<V|F3>` | Open file with default program for filetype | View |
|
||||
| `<W>` | Open file with provided program | With |
|
||||
| `<X>` | Execute a command | eXecute |
|
||||
| `<Y>` | Toggle synchronized browsing | sYnc |
|
||||
| `<Z>` | Change file mode | |
|
||||
| `<CTRL+A>` | Select all files | |
|
||||
| `<CTRL+C>` | Abort file transfer process | |
|
||||
| `<CTRL+T>` | Show all synchronized paths | Track |
|
||||
|
||||
### Work on multiple files 🥷
|
||||
|
||||
You can opt to work on multiple files, selecting them pressing `<M>`, in order to select the current file, or pressing `<CTRL+A>`, which will select all the files in the working directory.
|
||||
Once a file is marked for selection, it will be displayed with a `*` on the left.
|
||||
When working on selection, only selected file will be processed for actions, while the current highlighted item will be ignored.
|
||||
It is possible to work on multiple files also when in the find result panel.
|
||||
All the actions are available when working with multiple files, but be aware that some actions work in a slightly different way. Let's dive in:
|
||||
|
||||
- *Copy*: whenever you copy a file, you'll be prompted to insert the destination name. When working with multiple file, this name refers to the destination directory where all these files will be copied.
|
||||
- *Rename*: same as copy, but will move files there.
|
||||
- *Save as*: same as copy, but will write them there.
|
||||
|
||||
### Synchronized browsing ⏲️
|
||||
|
||||
When enabled, synchronized browsing, will allow you to synchronize the navigation between the two panels.
|
||||
This means that whenever you'll change the working directory on one panel, the same action will be reproduced on the other panel. If you want to enable synchronized browsing just press `<Y>`; press twice to disable. While enabled, the synchronized browsing state will be reported on the status bar on `ON`.
|
||||
|
||||
### Open and Open With 🚪
|
||||
|
||||
Open and open with commands are powered by [open-rs](https://docs.rs/crate/open/1.7.0).
|
||||
When opening files with View command (`<V>`), the system default application for the file type will be used. To do so, the default operting system service will be used, so be sure to have at least one of these installed on your system:
|
||||
|
||||
- **Windows** users: you don't have to worry about it, since the crate will use the `start` command.
|
||||
- **MacOS** users: you don't have to worry either, since the crate will use `open`, which is already installed on your system.
|
||||
- **Linux** users: one of these should be installed
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- **WSL** users: *wslview* is required, you must install [wslu](https://github.com/wslutilities/wslu).
|
||||
|
||||
> Q: Can I edit remote files using the view command?
|
||||
> A: No, at least not directly from the "remote panel". You have to download it to a local directory first, that's due to the fact that when you open a remote file, the file is downloaded into a temporary directory, but there's no way to create a watcher for the file to check when the program you used to open it was closed, so termscp is not able to know when you're done editing the file.
|
||||
|
||||
---
|
||||
|
||||
## Bookmarks ⭐
|
||||
|
||||
In termscp it is possible to save favourites hosts, which can be then loaded quickly from the main layout of termscp.
|
||||
termscp will also save the last 16 hosts you connected to.
|
||||
This feature allows you to load all the parameters required to connect to a certain remote, simply selecting the bookmark in the tab under the authentication form.
|
||||
|
||||
Bookmarks will be saved, if possible at:
|
||||
|
||||
- `$HOME/.config/termscp/` on Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` on MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` on Windows
|
||||
|
||||
For bookmarks only (this won't apply to recent hosts) it is also possible to save the password used to authenticate. The password is not saved by default and must be specified through the prompt when saving a new Bookmark.
|
||||
If you're concerned about the security of the password saved for your bookmarks, please read the [chapter below 👀](#are-my-passwords-safe-).
|
||||
|
||||
In order to create a new bookmark, just follow these steps:
|
||||
|
||||
1. Type in the authentication form the parameters to connect to your remote server
|
||||
2. Press `<CTRL+S>`
|
||||
3. Type in the name you want to give to the bookmark
|
||||
4. Choose whether to remind the password or not
|
||||
5. Press `<ENTER>` to submit
|
||||
|
||||
whenever you want to use the previously saved connection, just press `<TAB>` to navigate to the bookmarks list and load the bookmark parameters into the form pressing `<ENTER>`.
|
||||
|
||||

|
||||
|
||||
### Are my passwords Safe 😈
|
||||
|
||||
Sure 😉.
|
||||
As said before, bookmarks are saved in your configuration directory along with passwords. Passwords are obviously not plain text, they are encrypted with **AES-128**. Does this make them safe? Absolutely! (except for BSD and WSL users 😢)
|
||||
|
||||
On **Windows**, **Linux** and **MacOS** the key used to encrypt passwords is stored, if possible (but should be), respectively in the *Windows Vault*, in the *system keyring* and into the *Keychain*. This is actually super-safe and is directly managed by your operating system.
|
||||
|
||||
❗ Please, notice that if you're a Linux user, you'd better to read the [chapter below 👀](#linux-keyring), because the keyring might not be enabled or supported on your system!
|
||||
|
||||
On *BSD* and *WSL*, on the other hand, the key used to encrypt your passwords is stored on your drive (at $HOME/.config/termscp). It is then, still possible to retrieve the key to decrypt passwords. Luckily, the location of the key guarantees your key can't be read by users different from yours, but yeah, I still wouldn't save the password for a server exposed on the internet 😉.
|
||||
|
||||
#### Linux Keyring
|
||||
|
||||
We all love Linux thanks to the freedom it gives to the users. You can basically do anything you want as a Linux user, but this has also some cons, such as the fact that often there is no standard applications across different distributions. And this involves keyring too.
|
||||
This means that on Linux there might be no keyring installed on your system. Unfortunately the library we use to work with the key storage requires a service which exposes `org.freedesktop.secrets` on D-BUS and the worst fact is that there only two services exposing it.
|
||||
|
||||
- ❗ If you use GNOME as desktop environment (e.g. ubuntu users), you should already be fine, since keyring is already provided by `gnome-keyring` and everything should already be working.
|
||||
- ❗ For other desktop environment users there is a nice program you can use to get a keyring which is [KeepassXC](https://keepassxc.org/), which I use on my Manjaro installation (with KDE) and works fine. The only problem is that you have to setup it to be used along with termscp (but it's quite simple). To get started with KeepassXC read more [here](#keepassxc-setup-for-termscp).
|
||||
- ❗ What about you don't want to install any of these services? Well, there's no problem! **termscp will keep working as usual**, but it will save the key in a file, as it usually does for BSD and WSL.
|
||||
|
||||
##### KeepassXC setup for termscp
|
||||
|
||||
Follow these steps in order to setup keepassXC for termscp:
|
||||
|
||||
1. Install KeepassXC
|
||||
2. Go to "tools" > "settings" in toolbar
|
||||
3. Select "Secret service integration" and toggle "Enable KeepassXC freedesktop.org secret service integration"
|
||||
4. Create a database, if you don't have one yet: from toolbar "Database" > "New database"
|
||||
5. From toolbar: "Database" > "Database settings"
|
||||
6. Select "Secret service integration" and toggle "Expose entries under this group"
|
||||
7. Select the group in the list where you want the termscp secret to be kept. Remember that this group might be used by any other application to store secrets via DBUS.
|
||||
|
||||
---
|
||||
|
||||
## Configuration ⚙️
|
||||
|
||||
termscp supports some user defined parameters, which can be defined in the configuration.
|
||||
Underhood termscp has a TOML file and some other directories where all the parameters will be saved, but don't worry, you won't touch any of these files manually, since I made possible to configure termscp from its user interface entirely.
|
||||
|
||||
termscp, like for bookmarks, just requires to have these paths accessible:
|
||||
|
||||
- `$HOME/.config/termscp/` on Linux/BSD
|
||||
- `$HOME/Library/Application Support/termscp` on MacOs
|
||||
- `FOLDERID_RoamingAppData\termscp\` on Windows
|
||||
|
||||
To access configuration, you just have to press `<CTRL+C>` from the home of termscp.
|
||||
|
||||
These parameters can be changed:
|
||||
|
||||
- **Text Editor**: the text editor to use. By default termscp will find the default editor for you; with this option you can force an editor to be used (e.g. `vim`). **Also GUI editors are supported**, unless they `nohup` from the parent process.
|
||||
- **Default Protocol**: the default protocol is the default value for the file transfer protocol to be used in termscp. This applies for the login page and for the address CLI argument.
|
||||
- **Show Hidden Files**: select whether hidden files shall be displayed by default. You will be able to decide whether to show or not hidden files at runtime pressing `A` anyway.
|
||||
- **Check for updates**: if set to `yes`, termscp will fetch the Github API to check if there is a new version of termscp available.
|
||||
- **Prompt when replacing existing files?**: If set to `yes`, termscp will prompt for confirmation you whenever a file transfer would cause an existing file on target host to be replaced.
|
||||
- **Group Dirs**: select whether directories should be groupped or not in file explorers. If `Display first` is selected, directories will be sorted using the configured method but displayed before files, viceversa if `Display last` is selected.
|
||||
- **Remote File formatter syntax**: syntax to display file info for each file in the remote explorer. See [File explorer format](#file-explorer-format)
|
||||
- **Local File formatter syntax**: syntax to display file info for each file in the local explorer. See [File explorer format](#file-explorer-format)
|
||||
- **Enable notifications?**: If set to `Yes`, notifications will be displayed.
|
||||
- **Notifications: minimum transfer size**: if transfer size is greater or equal than the specified value, notifications for transfer will be displayed. The accepted values are in format `{UNSIGNED} B/KB/MB/GB/TB/PB`
|
||||
- **SSH configuration path**: Set SSH configuration file to use when connecting to a SCP/SFTP server. If unset (empty) no file will be used. You can specify a path starting with `~` to indicate the home path (e.g. `~/.ssh/config`). The parameters supported by termscp are specified [HERE](https://github.com/veeso/ssh2-config#exposed-attributes).
|
||||
|
||||
### SSH Key Storage 🔐
|
||||
|
||||
Along with configuration, termscp provides also an **essential** feature for **SFTP/SCP clients**: the SSH key storage.
|
||||
|
||||
You can access the SSH key storage, from configuration moving to the `SSH Keys` tab, once there you can:
|
||||
|
||||
- **Add a new key**: just press `<CTRL+N>` and you will be prompted to create a new key. Provide the hostname/ip address and the username associated to the key and finally a text editor will open up: paste the **PRIVATE** ssh key into the text editor, save and quit.
|
||||
- **Remove an existing key**: just press `<DEL>` or `<CTRL+E>` on the key you want to remove, to delete persistently the key from termscp.
|
||||
- **Edit an existing key**: just press `<ENTER>` on the key you want to edit, to change the private key.
|
||||
|
||||
> Q: Wait, my private key is protected with password, can I use it?
|
||||
> A: Of course you can. The password provided for authentication in termscp, is valid both for username/password authentication and for RSA key authentication.
|
||||
|
||||
### File Explorer Format
|
||||
|
||||
It is possible through configuration to define a custom format for the file explorer. This is possible both for local and remote host, so you can have two different syntax in use. These fields, with name `File formatter syntax (local)` and `File formatter syntax (remote)` will define how the file entries will be displayed in the file explorer.
|
||||
The syntax for the formatter is the following `{KEY1}... {KEY2:LENGTH}... {KEY3:LENGTH:EXTRA} {KEYn}...`.
|
||||
Each key in bracket will be replaced with the related attribute, while everything outside brackets will be left unchanged.
|
||||
|
||||
- The key name is mandatory and must be one of the keys below
|
||||
- The length describes the length reserved to display the field. Static attributes doesn't support this (GROUP, PEX, SIZE, USER)
|
||||
- Extra is supported only by some parameters and is an additional options. See keys to check if extra is supported.
|
||||
|
||||
These are the keys supported by the formatter:
|
||||
|
||||
- `ATIME`: Last access time (with default syntax `%b %d %Y %H:%M`); Extra might be provided as the time syntax (e.g. `{ATIME:8:%H:%M}`)
|
||||
- `CTIME`: Creation time (with syntax `%b %d %Y %H:%M`); Extra might be provided as the time syntax (e.g. `{CTIME:8:%H:%M}`)
|
||||
- `GROUP`: Owner group
|
||||
- `MTIME`: Last change time (with syntax `%b %d %Y %H:%M`); Extra might be provided as the time syntax (e.g. `{MTIME:8:%H:%M}`)
|
||||
- `NAME`: File name (Folders between root and first ancestors are elided if longer than LENGTH)
|
||||
- `PATH`: File absolute path (Folders between root and first ancestors are elided if longer than LENGHT)
|
||||
- `PEX`: File permissions (UNIX format)
|
||||
- `SIZE`: File size (omitted for directories)
|
||||
- `SYMLINK`: Symlink (if any `-> {FILE_PATH}`)
|
||||
- `USER`: Owner user
|
||||
|
||||
If left empty, the default formatter syntax will be used: `{NAME:24} {PEX} {USER} {SIZE} {MTIME:17:%b %d %Y %H:%M}`
|
||||
|
||||
---
|
||||
|
||||
## Themes 🎨
|
||||
|
||||
Termscp provides you with an awesome feature: the possibility to set the colors for several components in the application.
|
||||
If you want to customize termscp there are two available ways to do so:
|
||||
|
||||
- From the **configuration menu**
|
||||
- Importing a **theme file**
|
||||
|
||||
In order to create your own customization from termscp, all you have to do so is to enter the configuration from the auth activity, pressing `<CTRL+C>` and then `<TAB>` twice. You should have now moved to the `themes` panel.
|
||||
|
||||
Here you can move with `<UP>` and `<DOWN>` to change the style you want to change, as shown in the gif below:
|
||||
|
||||

|
||||
|
||||
termscp supports both the traditional explicit hex (`#rrggbb`) and rgb `rgb(r, g, b)` syntax to provide colors, but also **[css colors](https://www.w3schools.com/cssref/css_colors.asp)** (such as `crimson`) are accepted 😉. There is also a special keywork which is `Default`. Default means that the color used will be the default foreground or background color based on the situation (foreground for texts and lines, background for well, guess what).
|
||||
|
||||
As said before, you can also import theme files. You can take inspiration from or directly use one of the themes provided along with termscp, located in the `themes/` directory of this repository and import them running termscp as `termscp -t <theme_file>`. If everything was fine, it should tell you the theme has successfully been imported.
|
||||
|
||||
### My theme won't load 😱
|
||||
|
||||
This is probably due to a recent update which has broken the theme. Whenever I add a new key to themes, the saved theme won't load. To fix this issues there are two really quick-fix solutions:
|
||||
|
||||
1. Reload theme: whenever I release an update I will also patch the "official" themes, so you just have to download it from the repository again and re-import the theme via `-t` option
|
||||
|
||||
```sh
|
||||
termscp -t <theme.toml>
|
||||
```
|
||||
|
||||
2. Fix your theme: If you're using a custom theme, then you can edit via `vim` and add the missing key. The theme is located at `$CONFIG_DIR/termscp/theme.toml` where `$CONFIG_DIR` is:
|
||||
|
||||
- FreeBSD/GNU-Linux: `$HOME/.config/`
|
||||
- MacOs: `$HOME/Library/Application Support`
|
||||
- Windows: `%appdata%`
|
||||
|
||||
❗ Missing keys are reported in the CHANGELOG under `BREAKING CHANGES` for the version you've just installed.
|
||||
|
||||
### Styles 💈
|
||||
|
||||
You can find in the table below, the description for each style field.
|
||||
Please, notice that **styles won't apply to configuration page**, in order to make it always accessible in case you mess everything up
|
||||
|
||||
#### Authentication page
|
||||
|
||||
| Key | Description |
|
||||
|----------------|------------------------------------------|
|
||||
| auth_address | Color of the input field for IP address |
|
||||
| auth_bookmarks | Color of the bookmarks panel |
|
||||
| auth_password | Color of the input field for password |
|
||||
| auth_port | Color of the input field for port number |
|
||||
| auth_protocol | Color of the radio group for protocol |
|
||||
| auth_recents | Color of the recents panel |
|
||||
| auth_username | Color of the input field for username |
|
||||
|
||||
#### Transfer page
|
||||
|
||||
| Key | Description |
|
||||
|--------------------------------------|---------------------------------------------------------------------------|
|
||||
| transfer_local_explorer_background | Background color of localhost explorer |
|
||||
| transfer_local_explorer_foreground | Foreground color of localhost explorer |
|
||||
| transfer_local_explorer_highlighted | Border and highlighted color for localhost explorer |
|
||||
| transfer_remote_explorer_background | Background color of remote explorer |
|
||||
| transfer_remote_explorer_foreground | Foreground color of remote explorer |
|
||||
| transfer_remote_explorer_highlighted | Border and highlighted color for remote explorer |
|
||||
| transfer_log_background | Background color for log panel |
|
||||
| transfer_log_window | Window color for log panel |
|
||||
| transfer_progress_bar_partial | Partial progress bar color |
|
||||
| transfer_progress_bar_total | Total progress bar color |
|
||||
| transfer_status_hidden | Color for status bar "hidden" label |
|
||||
| transfer_status_sorting | Color for status bar "sorting" label; applies also to file sorting dialog |
|
||||
| transfer_status_sync_browsing | Color for status bar "sync browsing" label |
|
||||
|
||||
#### Misc
|
||||
|
||||
These styles applie to different part of the application.
|
||||
|
||||
| Key | Description |
|
||||
|-------------------|---------------------------------------------|
|
||||
| misc_error_dialog | Color for error messages |
|
||||
| misc_info_dialog | Color for info dialogs |
|
||||
| misc_input_dialog | Color for input dialogs (such as copy file) |
|
||||
| misc_keys | Color of text for key strokes |
|
||||
| misc_quit_dialog | Color for quit dialogs |
|
||||
| misc_save_dialog | Color for save dialogs |
|
||||
| misc_warn_dialog | Color for warn dialogs |
|
||||
|
||||
---
|
||||
|
||||
## Text Editor ✏
|
||||
|
||||
termscp has, as you might have noticed, many features, one of these is the possibility to view and edit text file. It doesn't matter if the file is located on the local host or on the remote host, termscp provides the possibility to open a file in your favourite text editor.
|
||||
In case the file is located on remote host, the file will be first downloaded into your temporary file directory and then, **only** if changes were made to the file, re-uploaded to the remote host. termscp checks if you made changes to the file verifying the last modification time of the file.
|
||||
|
||||
> ❗ Just a reminder: **you can edit only textual file**; binary files are not supported.
|
||||
|
||||
---
|
||||
|
||||
## Logging 🩺
|
||||
|
||||
termscp writes a log file for each session, which is written at
|
||||
|
||||
- `$HOME/.cache/termscp/termscp.log` on Linux/BSD
|
||||
- `$HOME/Library/Caches/termscp/termscp.log` on MacOs
|
||||
- `FOLDERID_LocalAppData\termscp\termscp.log` on Windows
|
||||
|
||||
the log won't be rotated, but will just be truncated after each launch of termscp, so if you want to report an issue and you want to attach your log file, keep in mind to save the log file in a safe place before using termscp again.
|
||||
The logging by default reports in *INFO* level, so it is not very verbose.
|
||||
|
||||
If you want to submit an issue, please, if you can, reproduce the issue with the level set to `TRACE`, to do so, launch termscp with
|
||||
the `-D` CLI option.
|
||||
|
||||
I know you might have some questions regarding log files, so I made a kind of a Q/A:
|
||||
|
||||
> I don't want logging, can I turn it off?
|
||||
|
||||
Yes, you can. Just start termscp with `-q or --quiet` option. You can alias termscp to make it persistent. Remember that logging is used to diagnose issues, so since behind every open source project, there should always be this kind of mutual help, keeping log files might be your way to support the project 😉. I don't want you to feel guilty, but just to say.
|
||||
|
||||
> Is logging safe?
|
||||
|
||||
If you're concerned about security, the log file doesn't contain any plain password, so don't worry and exposes the same information the sibling file `bookmarks` reports.
|
||||
|
||||
## Notifications 📫
|
||||
|
||||
Termscp will send Desktop notifications for these kind of events:
|
||||
|
||||
- on **Transfer completed**: The notification will be sent once a transfer has been successfully completed.
|
||||
- ❗ The notification will be displayed only if the transfer total size is at least the specified `Notifications: minimum transfer size` in the configuration.
|
||||
- on **Transfer failed**: The notification will be sent once a transfer has failed due to an error.
|
||||
- ❗ The notification will be displayed only if the transfer total size is at least the specified `Notifications: minimum transfer size` in the configuration.
|
||||
- on **Update available**: Whenever a new version of termscp is available, a notification will be displayed.
|
||||
- on **Update installed**: Whenever a new version of termscp has been installed, a notification will be displayed.
|
||||
- on **Update failed**: Whenever the installation of the update fails, a notification will be displayed.
|
||||
|
||||
❗ If you prefer to keep notifications turned off, you can just enter setup and set `Enable notifications?` to `No` 😉.
|
||||
❗ If you want to change the minimum transfer size to display notifications, you can change the value in the configuration with key `Notifications: minimum transfer size` and set it to whatever suits better for you 🙂.
|
||||
|
||||
---
|
||||
|
||||
## File watcher 🔭
|
||||
|
||||
The file watcher allows you to setup a list of paths to synchronize with the remote hosts.
|
||||
This means that whenever a change on the local file system will be detected on the synchronized path, the change will be automatically reported to the configured remote host path, within 5 seconds.
|
||||
|
||||
You can set as many paths to synchronize as you prefer:
|
||||
|
||||
1. Put the cursor on the local explorer on the directory/file you want to keep synchronized
|
||||
2. Go to the directory you want the changes to be reported to on the remote host
|
||||
3. Press `<T>`
|
||||
4. Answer `<YES>` to the radio popup
|
||||
|
||||
To unwatch, just press `<T>` on the local synchronized path (or to any of its subfolders)
|
||||
OR you can just press `<CTRL+T>` and press `<ENTER>` to the synchronized path you want to unwatch.
|
||||
|
||||
These changes will be reported to the remote host:
|
||||
|
||||
- New files, file changes
|
||||
- File moved/renamed
|
||||
- File removed/unlinked
|
||||
|
||||
> ❗ The watcher works only in one direction (local > remote). It is NOT possible to synchronize automatically the changes from remote to local.
|
||||
@@ -1,4 +1,4 @@
|
||||
Termscp is a feature rich terminal file transfer and explorer, with support for SCP/SFTP/FTP/S3.
|
||||
Termscp is a feature rich terminal file transfer and explorer, with support for SCP/SFTP/FTP/Kube/S3/WebDAV.
|
||||
Basically is a terminal utility with an TUI to connect to a remote server to retrieve and upload files and
|
||||
to interact with the local file system.
|
||||
|
||||
|
||||

|
Before Width: | Height: | Size: 879 B After Width: | Height: | Size: 879 B |

|
Before Width: | Height: | Size: 1.6 KiB After Width: | Height: | Size: 1.6 KiB |

|
Before Width: | Height: | Size: 2.8 KiB After Width: | Height: | Size: 2.8 KiB |
|
After Width: | Height: | Size: 361 KiB |
@@ -0,0 +1,47 @@
|
||||
// Injects a language toggle (EN / 中文) into the mdBook menu bar.
|
||||
// Swaps the leading /en-US/ <-> /zh-CN/ path segment, preserving the
|
||||
// rest of the path; falls back to the language root on 404 navigation.
|
||||
(function () {
|
||||
const LANGS = [
|
||||
{ code: "en-US", label: "EN" },
|
||||
{ code: "zh-CN", label: "中文" },
|
||||
];
|
||||
|
||||
function currentLang() {
|
||||
const m = window.location.pathname.match(/\/(en-US|zh-CN)\//);
|
||||
return m ? m[1] : "en-US";
|
||||
}
|
||||
|
||||
function swapTo(code) {
|
||||
const path = window.location.pathname;
|
||||
const cur = currentLang();
|
||||
if (path.includes(`/${cur}/`)) {
|
||||
return path.replace(`/${cur}/`, `/${code}/`);
|
||||
}
|
||||
return `/${code}/`;
|
||||
}
|
||||
|
||||
function build() {
|
||||
const right = document.querySelector(".right-buttons");
|
||||
if (!right) return;
|
||||
const cur = currentLang();
|
||||
const wrap = document.createElement("div");
|
||||
wrap.className = "lang-switcher";
|
||||
wrap.style.display = "inline-flex";
|
||||
wrap.style.gap = "0.5rem";
|
||||
wrap.style.marginInlineStart = "0.5rem";
|
||||
LANGS.forEach((l) => {
|
||||
const a = document.createElement("a");
|
||||
a.textContent = l.label;
|
||||
a.href = swapTo(l.code);
|
||||
a.title = l.code;
|
||||
a.setAttribute("aria-current", l.code === cur ? "true" : "false");
|
||||
if (l.code === cur) a.style.fontWeight = "bold";
|
||||
wrap.appendChild(a);
|
||||
});
|
||||
right.appendChild(wrap);
|
||||
}
|
||||
|
||||
if (document.readyState !== "loading") build();
|
||||
else document.addEventListener("DOMContentLoaded", build);
|
||||
})();
|
||||

|
After Width: | Height: | Size: 79 KiB |

@@ -0,0 +1 @@
|
||||
<svg xmlns="http://www.w3.org/2000/svg" viewBox="0 0 500 500"><circle style="fill:#31363b" cx="250" cy="250" r="250"/><circle style="fill:#ea4444" cx="225" cy="40" r="7.344"/><circle style="fill:#eac944" cx="58.177" cy="22.745" r="7.344" transform="matrix(1, 0, 0, 1.031863, 191.822998, 16.530386)"/><circle style="fill:#34b938" cx="57.564" cy="22.269" r="7.344" transform="matrix(1, 0, 0, 1.031863, 217.43605, 17.021263)"/><polygon style="stroke:#000;fill:#f0f0f0" points="83.462 135.575 200 252.112 87.687 364.425 48.108 324.846 122.07 250.881 45.738 174.55"/><g transform="matrix(0.408921, 0, 0, 0.408921, 241.338654, 169.687912)"><polygon style="fill:#f0f0f0" points="196.4 0 292 49.2 388 98 292 147.2 196.4 196.4 100.8 147.2 4.8 98 100.8 49.2"/><polygon style="fill:#31363b" points="316 179.6 316 135.2 268 159.6 268 204 294.4 171.6"/><polygon style="fill:#f0f0f0" points="196.4 196.4 196.4 392.8 388 294.8 388 98 316 135.2 314.4 136 314.4 179.2 294.4 171.6 268 204 268 159.6"/><polygon style="fill:#f0f0f0" points="196.4 392.8 196.4 196.4 100.8 147.2 4.8 98 4.8 294.8"/><polygon style="fill:#31363b" points="76.8 61.2 268 159.6 314.4 136 316 135.2 124.8 36.8 100.8 49.2"/></g><rect style="fill:#f0f0f0" width="200" height="35.702" x="222.229" y="364.298" rx="10" ry="10"/></svg>
|
||||
|
After Width: | Height: | Size: 1.3 KiB |
@@ -1,134 +1,43 @@
|
||||
# termscp
|
||||
|
||||
<p align="center">
|
||||
<img src="/assets/images/termscp.svg" width="256" height="256" />
|
||||
<img src="/assets/images/termscp.svg" alt="termscp logo" width="256" height="256" />
|
||||
</p>
|
||||
|
||||
<p align="center">~ 功能丰富的终端文件传输工具 ~</p>
|
||||
<p align="center">
|
||||
<a href="https://termscp.veeso.dev" target="_blank">网站</a>
|
||||
<a href="https://termscp.rs" target="_blank">网站</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#get-started" target="_blank">安装</a>
|
||||
<a href="https://termscp.rs/install" target="_blank">安装</a>
|
||||
·
|
||||
<a href="https://termscp.veeso.dev/#user-manual" target="_blank">用户手册</a>
|
||||
<a href="https://docs.termscp.rs" target="_blank">用户手册</a>
|
||||
</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp"
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/gb.png"
|
||||
alt="English"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/de/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/de.png"
|
||||
alt="Deutsch"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/es/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/es.png"
|
||||
alt="Español"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/fr/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/fr.png"
|
||||
alt="Français"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/it/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/it.png"
|
||||
alt="Italiano"
|
||||
/></a>
|
||||
|
||||
<a
|
||||
href="https://github.com/veeso/termscp/blob/main/docs/zh-CN/README.md"
|
||||
><img
|
||||
height="20"
|
||||
src="/assets/images/flags/cn.png"
|
||||
alt="简体中文"
|
||||
/></a>
|
||||
</p>
|
||||
|
||||
<p align="center">由 <a href="https://veeso.dev/" target="_blank">@veeso</a> 开发</p>
|
||||
<p align="center">当前版本: 0.12.3 (06/10/2023)</p>
|
||||
<p align="center">由 <a href="https://veeso.me/" target="_blank">@veeso</a> 开发</p>
|
||||
|
||||
<p align="center">
|
||||
<a href="https://opensource.org/licenses/MIT"
|
||||
><img
|
||||
src="https://img.shields.io/badge/License-MIT-teal.svg"
|
||||
alt="License-MIT"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/stargazers"
|
||||
><img
|
||||
src="https://img.shields.io/github/stars/veeso/termscp.svg"
|
||||
alt="Repo stars"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/d/termscp.svg"
|
||||
alt="Downloads counter"
|
||||
/></a>
|
||||
<a href="https://crates.io/crates/termscp"
|
||||
><img
|
||||
src="https://img.shields.io/crates/v/termscp.svg"
|
||||
alt="Latest version"
|
||||
/></a>
|
||||
<a href="https://ko-fi.com/veeso">
|
||||
<img
|
||||
src="https://img.shields.io/badge/donate-ko--fi-red"
|
||||
alt="Ko-fi"
|
||||
/></a>
|
||||
</p>
|
||||
<p align="center">
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Linux/badge.svg"
|
||||
alt="Linux CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/MacOS/badge.svg"
|
||||
alt="MacOS CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/Windows/badge.svg"
|
||||
alt="Windows CI"
|
||||
/></a>
|
||||
<a href="https://github.com/veeso/termscp/actions"
|
||||
><img
|
||||
src="https://github.com/veeso/termscp/workflows/FreeBSD/badge.svg"
|
||||
alt="FreeBSD CI"
|
||||
/></a>
|
||||
<a href="https://coveralls.io/github/veeso/termscp"
|
||||
><img
|
||||
src="https://coveralls.io/repos/github/veeso/termscp/badge.svg"
|
||||
alt="Coveralls"
|
||||
/></a>
|
||||
</p>
|
||||
[](https://opensource.org/licenses/MIT)
|
||||
[](https://github.com/veeso/termscp/stargazers)
|
||||
[](https://crates.io/crates/termscp)
|
||||
[](https://crates.io/crates/termscp)
|
||||
[](https://github.com/veeso/termscp/actions/workflows/ci.yml)
|
||||
|
||||
---
|
||||
|
||||
## 关于 termscp 🖥
|
||||
|
||||
termscp 是一个功能丰富的终端文件浏览和传输工具,支持 SCP/SFTP/FTP/S3。 作为一个带有 TUI 的命令行工具,它可以连接到远程服务器进行文件检索和上传,并能够与本地文件系统进行交互。
|
||||
termscp 是一个功能丰富的终端文件浏览和传输工具,支持 SCP/SFTP/FTP/Kube/S3/WebDAV。 简而言之,它是一个带有 TUI 的终端工具,可以连接到远程服务器进行文件的检索和上传,并能够与本地文件系统进行交互。 它兼容 **Linux**、**MacOS**、**FreeBSD**、**NetBSD** 和 **Windows** 操作系统。
|
||||
|
||||
兼容 **Linux**、**MacOS**、**FreeBSD** 和 **Windows** 操作系统。
|
||||
|
||||

|
||||

|
||||
|
||||
---
|
||||
|
||||
@@ -137,114 +46,140 @@ termscp 是一个功能丰富的终端文件浏览和传输工具,支持 SCP/S
|
||||
- 📁 支持多种通信协议
|
||||
- **SFTP**
|
||||
- **SCP**
|
||||
- **FTP** and **FTPS**
|
||||
- **FTP** 和 **FTPS**
|
||||
- **Kube**
|
||||
- **S3**
|
||||
- **SMB**
|
||||
- **WebDAV**
|
||||
- 🖥 使用便捷的 UI 在远程和本地文件系统上浏览和操作
|
||||
- 创建、删除、重命名、搜索、查看和编辑文件
|
||||
- ⭐ 通过“内置书签”和“最近连接”快速连接到您的主机
|
||||
- ⭐ 通过“内置书签”和“最近连接”快速连接到您喜爱的主机
|
||||
- 📝 使用您喜欢的应用程序查看和编辑文件
|
||||
- 💁 使用 SSH 密钥和用户名/密码进行 SFTP/SCP 身份验证
|
||||
- 🐧 兼容 Windows、Linux、FreeBSD 和 MacOS 操作系统
|
||||
- 🐧 兼容 Windows、Linux、FreeBSD、NetBSD 和 MacOS 操作系统
|
||||
- 🐚 内置终端,可在系统上执行命令。
|
||||
- 🎨 丰富的个性化设置!
|
||||
- 主题
|
||||
- 自定义文件浏览器格式
|
||||
- 可选择的文本编辑器
|
||||
- 可选择的文件排序
|
||||
- 探索更多功能...
|
||||
- 可自定义的文本编辑器
|
||||
- 可自定义的文件排序
|
||||
- 以及许多其他参数...
|
||||
- 📫 传输大文件时通过桌面通知获得提醒
|
||||
- 🔭 与远程主机文件更改保持同步
|
||||
- 🔐 将密码保存在操作系统密钥保管库中
|
||||
- 🦀 由 Rust 提供强力支持
|
||||
- 👀 开发时更注重性能
|
||||
- 🦄 快速且精彩迭代
|
||||
- 🦄 频繁的精彩更新
|
||||
|
||||
---
|
||||
|
||||
## 开始 🚀
|
||||
|
||||
非常荣幸您能考虑安装termscp💜! 希望你会喜欢termscp!
|
||||
如果您正在考虑安装 termscp,我想对您表示感谢 💜 ! 希望您会喜欢 termscp!
|
||||
如果您想为此项目做出贡献,请不要忘记查看我们的[贡献指南](CONTRIBUTING.md)。
|
||||
|
||||
如果您想为此项目做出贡献,请不要忘记查看我们的贡献指南。 [阅读更多](../../CONTRIBUTING.md)
|
||||
|
||||
如果您是 Linux、FreeBSD 或 MacOS 用户,使用以下简单的 shell 脚本通过单行指令在您的系统上安装 termscp:
|
||||
如果您是 Linux、FreeBSD 或 MacOS 用户,使用以下简单的 shell 脚本即可通过单行指令在您的系统上安装 termscp:
|
||||
|
||||
```sh
|
||||
curl -sSLf http://get-termscp.veeso.dev | sh
|
||||
curl --proto '=https' --tlsv1.2 -sSLf https://termscp.rs/install.sh | sh
|
||||
```
|
||||
|
||||
如果您是 Windows 用户,则可以使用 [Chocolatey](https://chocolatey.org/) 安装 termscp:
|
||||
> ❗ MacOS 安装需要 [Homebrew](https://brew.sh/),否则将会安装 Rust 编译器
|
||||
|
||||
```sh
|
||||
如果您是 Windows 用户,则可以在 PowerShell 中通过单行指令安装 termscp:
|
||||
|
||||
```ps
|
||||
irm https://termscp.rs/install.ps1 | iex
|
||||
```
|
||||
|
||||
或者,使用 [Chocolatey](https://chocolatey.org/):
|
||||
|
||||
```ps
|
||||
choco install termscp
|
||||
```
|
||||
|
||||
如需更多信息或其他的平台支持,请访问 [termscp.veeso.dev](https://termscp.veeso.dev/termscp/#get-started) 查看所有安装方法。
|
||||
NetBSD 用户可以从官方仓库安装 termscp。
|
||||
|
||||
⚠️ 如果您正在寻找如何更新 termscp 只需从 CLI 运行 termscp : `(sudo) termscp --update` ⚠️
|
||||
```sh
|
||||
pkgin install termscp
|
||||
```
|
||||
|
||||
Arch Linux 用户可以从官方仓库安装 termscp。
|
||||
|
||||
```sh
|
||||
pacman -S termscp
|
||||
```
|
||||
|
||||
如需更多信息或其他平台支持,请访问 [termscp.rs](https://termscp.rs/install) 查看所有安装方法。
|
||||
|
||||
⚠️ 如果您想了解如何更新 termscp,只需从 CLI 运行 termscp: `(sudo) termscp update` ⚠️
|
||||
|
||||
### 依赖 ❗
|
||||
|
||||
- **Linux** 用户:
|
||||
- libssh
|
||||
- **Linux** 用户:
|
||||
- libdbus-1
|
||||
- pkg-config
|
||||
- libsmbclient
|
||||
- **FreeBSD** 用户:
|
||||
- libssh
|
||||
- **FreeBSD** 或 **NetBSD** 用户:
|
||||
- dbus
|
||||
- pkgconf
|
||||
- libsmbclient
|
||||
|
||||
### 可选项 ✔️
|
||||
### 可选依赖 ✔️
|
||||
|
||||
通过执行以下操作以享受软件的完整功能,但不做强制要求
|
||||
这些依赖并非运行 termscp 的强制要求,但有助于享受其全部功能
|
||||
|
||||
- **Linux/FreeBSD** 用户:
|
||||
- 用 `V` **打开** 文件(至少其中之一)
|
||||
- **Linux/FreeBSD** 用户:
|
||||
- 用 `V` **打开**文件(至少其中之一)
|
||||
- *xdg-open*
|
||||
- *gio*
|
||||
- *gnome-open*
|
||||
- *kde-open*
|
||||
- **Linux** 用户:
|
||||
- keyring manager: [在用户手册中阅读更多内容](man.md#linux-keyring)
|
||||
- **Linux** 用户:
|
||||
- 密钥环管理器:在[用户手册](https://docs.termscp.rs/zh-CN/configuration/password-security.html#linux-密钥环)中阅读更多内容
|
||||
- **WSL** 用户
|
||||
- 用 `V` **打开** 文件(至少其中之一)
|
||||
- 用 `V` **打开**文件(至少其中之一)
|
||||
- [wslu](https://github.com/wslutilities/wslu)
|
||||
|
||||
---
|
||||
|
||||
## 支持我 ☕
|
||||
## 支持开发者 ☕
|
||||
|
||||
如果您喜欢 termscp 并且希望看到该项目不断发展和改进,请考虑在 **Buy me a coffee** 上赞赏以支持我🥳
|
||||
如果您喜欢 termscp 并且感激我所做的工作,请考虑给予一点捐赠 🥳
|
||||
|
||||
您可以通过以下平台之一进行捐赠:
|
||||
|
||||
[](https://ko-fi.com/veeso)
|
||||
|
||||
或者,如果您愿意,您也可以在 PayPal 上赞赏我:
|
||||
|
||||
[](https://www.paypal.me/chrisintin)
|
||||
|
||||
---
|
||||
|
||||
## 用户手册和文档 📚
|
||||
## 用户手册 📚
|
||||
|
||||
用户手册可以在[termscp的网站](https://termscp.veeso.dev/termscp/#user-manual)或者在[Github](man.md)上找到。
|
||||
用户手册可以在 [termscp 文档网站](https://docs.termscp.rs)上找到。
|
||||
|
||||
---
|
||||
|
||||
## 即将推出的功能 🧪
|
||||
|
||||
请查看 [Milestones](https://github.com/veeso/termscp/milestones)
|
||||
|
||||
---
|
||||
|
||||
## 贡献和问题 🤝🏻
|
||||
|
||||
欢迎贡献、bug报告、新功能和问题! 😉
|
||||
欢迎贡献、bug 报告、新功能和问题! 😉
|
||||
如果您有任何问题或困惑,或者想建议新功能,或者只是想改进 termscp,请随时打开 issue 或 PR。
|
||||
|
||||
如果您有任何问题或困惑,或者您想建议新功能,或者您只是想改进termscp,请随时打开 issue 或 PR。
|
||||
一个**值得赞赏**的贡献是将用户手册和 README 翻译成**其他语言**
|
||||
|
||||
请遵循 [我们的贡献指南](../../CONTRIBUTING.md)
|
||||
请遵循[我们的贡献指南](CONTRIBUTING.md)
|
||||
|
||||
---
|
||||
|
||||
## 更新日志 ⏳
|
||||
|
||||
查看termscp的 [更新日志](../../CHANGELOG.md)
|
||||
查看 termscp 的更新日志[点此](CHANGELOG.md)
|
||||
|
||||
---
|
||||
|
||||
@@ -256,13 +191,13 @@ termscp 由这些很棒的项目提供支持:
|
||||
- [crossterm](https://github.com/crossterm-rs/crossterm)
|
||||
- [edit](https://github.com/milkey-mouse/edit)
|
||||
- [keyring-rs](https://github.com/hwchen/keyring-rs)
|
||||
- [kube](https://github.com/kube-rs/kube)
|
||||
- [open-rs](https://github.com/Byron/open-rs)
|
||||
- [pavao](https://github.com/veeso/pavao)
|
||||
- [remotefs](https://github.com/veeso/remotefs-rs)
|
||||
- [rpassword](https://github.com/conradkleinespel/rpassword)
|
||||
- [rust-s3](https://github.com/durch/rust-s3)
|
||||
- [self_update](https://github.com/jaemk/self_update)
|
||||
- [ssh2-rs](https://github.com/alexcrichton/ssh2-rs)
|
||||
- [suppaftp](https://github.com/veeso/suppaftp)
|
||||
- [tui-rs](https://github.com/fdehau/tui-rs)
|
||||
- [ratatui](https://github.com/ratatui-org/ratatui)
|
||||
- [tui-realm](https://github.com/veeso/tui-realm)
|
||||
- [whoami](https://github.com/libcala/whoami)
|
||||
- [wildmatch](https://github.com/becheran/wildmatch)
|
||||
@@ -271,26 +206,26 @@ termscp 由这些很棒的项目提供支持:
|
||||
|
||||
## 演示 🎬
|
||||
|
||||
> 首页
|
||||
> termscp 首页
|
||||
|
||||

|
||||

|
||||
|
||||
> 书签
|
||||
|
||||

|
||||

|
||||
|
||||
> 设置
|
||||
|
||||

|
||||

|
||||
|
||||
> 文本编辑器
|
||||
|
||||

|
||||

|
||||
|
||||
---
|
||||
|
||||
## 许可协议 📃
|
||||
|
||||
“termscp”使用 MIT 许可。
|
||||
termscp 使用 MIT 许可证授权。
|
||||
|
||||
您可以阅读整个 [许可证](../../LICENSE)
|
||||
您可以阅读完整的[许可证](LICENSE)
|
||||
|
||||
@@ -0,0 +1,37 @@
|
||||
# 目录
|
||||
|
||||
[简介](index.md)
|
||||
|
||||
# 入门
|
||||
|
||||
- [安装](getting-started/installation.md)
|
||||
- [连接到服务器](getting-started/connecting.md)
|
||||
- [连接参数](getting-started/connection-parameters.md)
|
||||
|
||||
# 使用 termscp
|
||||
|
||||
- [文件浏览器](usage/file-explorer.md)
|
||||
- [键盘快捷键](usage/keyboard-shortcuts.md)
|
||||
- [批量操作文件](usage/multiple-files.md)
|
||||
- [同步浏览](usage/synced-browsing.md)
|
||||
- [打开与编辑文件](usage/open-edit-files.md)
|
||||
- [书签与最近主机](usage/bookmarks.md)
|
||||
- [保持文件同步](usage/file-watcher.md)
|
||||
|
||||
# 配置
|
||||
|
||||
- [配置](configuration/configuration.md)
|
||||
- [文件浏览器格式](configuration/explorer-format.md)
|
||||
- [SSH 密钥存储](configuration/ssh-keys.md)
|
||||
- [主题](configuration/themes.md)
|
||||
- [通知](configuration/notifications.md)
|
||||
- [日志](configuration/logging.md)
|
||||
- [密码安全](configuration/password-security.md)
|
||||
|
||||
# 命令行参考
|
||||
|
||||
- [命令行用法](cli/cli.md)
|
||||
|
||||
# 开发者
|
||||
|
||||
- [开发者手册](developer/developer.md)
|
||||
@@ -0,0 +1,22 @@
|
||||
[book]
|
||||
title = "termscp"
|
||||
description = "A feature rich terminal UI file transfer and explorer with support for SCP/SFTP/FTP/Kube/S3/SMB/WebDAV"
|
||||
authors = ["Christian Visintin"]
|
||||
language = "zh"
|
||||
src = "."
|
||||
|
||||
[output.html]
|
||||
default-theme = "light"
|
||||
preferred-dark-theme = "navy"
|
||||
git-repository-url = "https://github.com/veeso/termscp"
|
||||
edit-url-template = "https://github.com/veeso/termscp/edit/main/docs/zh-CN/{path}"
|
||||
additional-js = ["lang-switcher.js", "mermaid.min.js", "mermaid-init.js"]
|
||||
|
||||
[output.html.fold]
|
||||
enable = true
|
||||
level = 1
|
||||
|
||||
[preprocessor]
|
||||
|
||||
[preprocessor.mermaid]
|
||||
command = "mdbook-mermaid"
|
||||
@@ -0,0 +1,68 @@
|
||||
# 命令行用法
|
||||
|
||||
termscp 可以通过以下调用形式启动:
|
||||
|
||||
```sh
|
||||
termscp [options]... [protocol://user@address:port:wrkdir] [protocol://user@address:port:wrkdir] [local-wrkdir]
|
||||
```
|
||||
|
||||
或
|
||||
|
||||
```sh
|
||||
termscp [options]... -b [bookmark-name] -b [bookmark-name] [local-wrkdir]
|
||||
```
|
||||
|
||||
以及两者的任意组合。
|
||||
|
||||
如果未提供额外参数,termscp 会显示身份验证表单。如果提供了地址参数或书签名称,termscp 会跳过该表单并直接连接到远程服务器。当提供地址或书签时,你还可以将本地主机的起始工作目录作为最后一个位置参数提供。
|
||||
|
||||
## 选项
|
||||
|
||||
| Key | 说明 |
|
||||
| -------------------- | --------------------------------------------------------------------------------------------------------------------------------- |
|
||||
| `-b <bookmark-name>` | 将位置地址参数解析为书签名称。重复使用该标志可以打开多个书签。 |
|
||||
| `-D` | 启用 `TRACE` 日志级别(调试/详细日志)。 |
|
||||
| `-P <password>` | 从命令行提供密码。重复使用该标志可为多个远程主机提供密码;其顺序必须与地址参数一致。不推荐使用。 |
|
||||
| `-q` | 禁用日志记录。 |
|
||||
| `-T <ticks>` | 设置 UI 的 tick 间隔(以毫秒为单位)。默认值为 `10`。 |
|
||||
| `--wno-keyring` | 禁用系统 keyring 支持。 |
|
||||
| `-v` | 打印版本信息。 |
|
||||
| `--help` | 打印帮助页面。 |
|
||||
|
||||
不推荐使用 `-P` 选项,因为密码可能会保留在 shell 历史记录中。请参阅书签和密码安全章节,了解更安全的凭据提供方式。
|
||||
|
||||
## 子命令
|
||||
|
||||
termscp 提供以下子命令。
|
||||
|
||||
### 导入主题
|
||||
|
||||
```sh
|
||||
termscp theme <theme-file>
|
||||
```
|
||||
|
||||
导入在 `<theme-file>` 中定义的主题。
|
||||
|
||||
### 安装最新版本
|
||||
|
||||
```sh
|
||||
termscp update
|
||||
```
|
||||
|
||||
下载并安装 termscp 的最新可用版本。
|
||||
|
||||
### 导入 ssh 主机
|
||||
|
||||
```sh
|
||||
termscp import-ssh-hosts [ssh-config-file]
|
||||
```
|
||||
|
||||
将指定 ssh 配置文件中的所有主机作为书签导入到 termscp 中。如果未提供 `[ssh-config-file]`,则使用默认位置 `~/.ssh/config`。身份文件也会作为 ssh 密钥导入到 termscp 中。
|
||||
|
||||
### 打开配置
|
||||
|
||||
```sh
|
||||
termscp config
|
||||
```
|
||||
|
||||
直接在配置(setup)界面中启动 termscp。
|
||||
@@ -0,0 +1,27 @@
|
||||
# 配置
|
||||
|
||||
termscp 支持大量用户自定义参数。termscp 将这些参数存储在一个 TOML 文件和若干目录中,但你无需手动编辑这些文件:所有配置都完全在用户界面中完成。
|
||||
|
||||
要进入配置界面,请在 termscp 主页按下 `<CTRL+C>`。
|
||||
|
||||
termscp 要求以下路径可访问:
|
||||
|
||||
- Linux/BSD 上的 `$HOME/.config/termscp/`
|
||||
- macOS 上的 `$HOME/.config/termscp/`
|
||||
- Windows 上的 `%USERPROFILE%\.termscp\`
|
||||
|
||||
## 参数
|
||||
|
||||
可以配置以下参数:
|
||||
|
||||
- **文本编辑器**:要使用的文本编辑器。默认情况下,termscp 会为你查找默认编辑器;通过此选项你可以强制使用某个编辑器(例如 `vim`)。也支持 GUI 编辑器,除非它们会从父进程中分离(`nohup`)。
|
||||
- **默认协议**:termscp 中使用的文件传输协议的默认值。它适用于登录页面以及地址命令行参数。
|
||||
- **显示隐藏文件**:是否默认显示隐藏文件。你也可以在运行时按 `A` 切换隐藏文件的显示。
|
||||
- **检查更新**:如果设置为 `yes`,termscp 会查询 GitHub API 以检查是否有新版本的 termscp 可用。
|
||||
- **替换已有文件时提示**:如果设置为 `yes`,每当文件传输会替换目标主机上已有的文件时,termscp 都会请求确认。
|
||||
- **目录分组**:文件浏览器中是否将目录分组。如果选择 `Display first`,目录会按配置的方法排序,但显示在文件之前;如果选择 `Display last`,则显示在文件之后。
|
||||
- **远程文件格式化语法**:用于在远程浏览器中显示每个文件信息的语法。参见 [文件浏览器格式](explorer-format.md)。
|
||||
- **本地文件格式化语法**:用于在本地浏览器中显示每个文件信息的语法。参见 [文件浏览器格式](explorer-format.md)。
|
||||
- **启用通知**:如果设置为 `Yes`,则会显示桌面通知。参见 [通知](notifications.md)。
|
||||
- **通知:最小传输大小**:如果传输大小大于或等于指定值,则显示传输通知。可接受的格式为 `{UNSIGNED} B/KB/MB/GB/TB/PB`。
|
||||
- **SSH 配置路径**:连接到 SCP/SFTP 服务器时使用的 SSH 配置文件。如果留空,则不使用任何文件。你可以指定以 `~` 开头的路径来表示主目录(例如 `~/.ssh/config`)。termscp 支持的属性列于 [ssh2-config 公开的属性](https://github.com/veeso/ssh2-config#exposed-attributes)。另请参见 [SSH 密钥存储](ssh-keys.md)。
|
||||
@@ -0,0 +1,42 @@
|
||||
# 文件浏览器格式
|
||||
|
||||
你可以通过配置为文件浏览器定义自定义格式。本地主机和远程主机都支持此功能,因此你可以使用两种不同的语法。这两个字段分别名为 **文件格式化语法(本地)** 和 **文件格式化语法(远程)**,它们定义了文件条目在文件浏览器中的显示方式。
|
||||
|
||||
## 语法
|
||||
|
||||
格式化器的语法如下:
|
||||
|
||||
```text
|
||||
{KEY1}... {KEY2:LENGTH}... {KEY3:LENGTH:EXTRA} {KEYn}...
|
||||
```
|
||||
|
||||
花括号中的每个键都会被替换为相关的属性,而花括号之外的所有内容则保持不变。
|
||||
|
||||
- 键名是必填的,且必须是下列键之一。
|
||||
- `LENGTH` 描述了用于显示该字段所保留的宽度。静态属性不支持它(`GROUP`、`PEX`、`SIZE`、`USER`)。
|
||||
- `EXTRA` 仅由部分键支持,并提供一个附加选项。请查看下面的键以确认是否支持 `EXTRA`。
|
||||
|
||||
## 键
|
||||
|
||||
以下是格式化器支持的键:
|
||||
|
||||
| 键 | 说明 |
|
||||
| --------- | ------------------------------------------------------------------------------------------------ |
|
||||
| `ATIME` | 最后访问时间(默认 `%b %d %Y %H:%M`);`EXTRA` 为时间格式(例如 `{ATIME:8:%H:%M}`) |
|
||||
| `CTIME` | 创建时间(默认 `%b %d %Y %H:%M`);`EXTRA` 为时间格式(例如 `{CTIME:8:%H:%M}`) |
|
||||
| `GROUP` | 所属组 |
|
||||
| `MTIME` | 最后修改时间(默认 `%b %d %Y %H:%M`);`EXTRA` 为时间格式(例如 `{MTIME:8:%H:%M}`) |
|
||||
| `NAME` | 文件名(如果根目录与首个祖先目录之间的文件夹长度超过 `LENGTH`,则会被省略) |
|
||||
| `PATH` | 文件绝对路径(如果根目录与首个祖先目录之间的文件夹长度超过 `LENGTH`,则会被省略) |
|
||||
| `PEX` | 文件权限(UNIX 格式) |
|
||||
| `SIZE` | 文件大小(目录省略) |
|
||||
| `SYMLINK` | 符号链接目标(如果有,`-> {FILE_PATH}`) |
|
||||
| `USER` | 所属用户 |
|
||||
|
||||
## 默认格式
|
||||
|
||||
如果留空,则使用默认的格式化语法:
|
||||
|
||||
```text
|
||||
{NAME:24} {PEX} {USER} {SIZE} {MTIME:17:%b %d %Y %H:%M}
|
||||
```
|
||||
@@ -0,0 +1,23 @@
|
||||
# 日志
|
||||
|
||||
termscp 会为每个会话写入一个日志文件,位于:
|
||||
|
||||
- Linux/BSD 上的 `$HOME/.cache/termscp/termscp.log`
|
||||
- macOS 上的 `$HOME/Library/Caches/termscp/termscp.log`
|
||||
- Windows 上的 `FOLDERID_LocalAppData\termscp\termscp.log`
|
||||
|
||||
日志不会轮转:每次启动 termscp 时都会被截断。如果你想报告问题并附上日志文件,请在再次启动 termscp 之前将日志保存到安全的位置。
|
||||
|
||||
默认情况下,日志以 `INFO` 级别记录,因此不是很详细。
|
||||
|
||||
## 以 TRACE 级别复现问题
|
||||
|
||||
要提交问题,请通过使用 `-D` 命令行选项启动 termscp,将日志级别设置为 `TRACE` 来复现问题。
|
||||
|
||||
## 禁用日志
|
||||
|
||||
要关闭日志,请使用 `-q` 或 `--quiet` 选项启动 termscp。你可以为 termscp 设置别名,使其永久生效。
|
||||
|
||||
## 安全性
|
||||
|
||||
日志文件不包含任何明文密码。它暴露的信息与同级的 `bookmarks` 文件相同。
|
||||
@@ -0,0 +1,17 @@
|
||||
# 通知
|
||||
|
||||
termscp 会针对以下事件发送桌面通知:
|
||||
|
||||
- **传输完成**:在传输成功完成后发送。仅当总传输大小至少达到所配置的 `Notifications: minimum transfer size` 时才会显示。
|
||||
- **传输失败**:在传输因错误而失败后发送。仅当总传输大小至少达到所配置的 `Notifications: minimum transfer size` 时才会显示。
|
||||
- **有可用更新**:每当有新版本的 termscp 可用时发送。
|
||||
- **更新已安装**:每当新版本的 termscp 安装完成时发送。
|
||||
- **更新失败**:每当更新安装失败时发送。
|
||||
|
||||
## 禁用通知
|
||||
|
||||
要关闭通知,请进入设置并将 `Enable notifications?` 设置为 `No`。
|
||||
|
||||
## 更改最小传输大小
|
||||
|
||||
要更改用于控制传输通知的阈值,请进入设置并将 `Notifications: minimum transfer size` 设置为适合你的值。
|
||||
@@ -0,0 +1,33 @@
|
||||
# 密码安全
|
||||
|
||||
书签连同其密码一起保存在你的配置目录中。密码不会以明文存储:它们使用 AES 加密。
|
||||
|
||||
用于加密密码的密钥会尽可能存储在操作系统的密钥存储中:
|
||||
|
||||
- Windows 上的 Windows Vault
|
||||
- Linux 上的系统密钥环
|
||||
- macOS 上的 Keychain
|
||||
|
||||
这由你的操作系统直接管理。
|
||||
|
||||
在 BSD 和 WSL 上没有这样的密钥存储,因此加密密钥会保存在磁盘上的 `$HOME/.config/termscp`。该位置通过文件权限保护密钥,使其无法被其他用户读取,但你仍应避免在这些系统上为暴露于互联网上的服务器保存密码。
|
||||
|
||||
## Linux 密钥环
|
||||
|
||||
在 Linux 上,你的系统中可能没有安装密钥环。密钥存储需要一个在 D-Bus 上暴露 `org.freedesktop.secrets` 的服务,而只有少数服务提供它:
|
||||
|
||||
- 如果你使用 GNOME 作为桌面环境(例如 Ubuntu 用户),密钥环已经由 `gnome-keyring` 提供,一切应该开箱即用。
|
||||
- 对于其他桌面环境,你可以使用 [KeepassXC](https://keepassxc.org/) 来获取一个密钥环。它必须经过设置才能与 termscp 配合使用;参见下面的 [KeepassXC 设置](#keepassxc-设置)。
|
||||
- 如果你不想安装这些服务中的任何一个,termscp 会照常工作,并回退到将密钥保存在文件中,正如它在 BSD 和 WSL 上所做的那样。
|
||||
|
||||
### KeepassXC 设置
|
||||
|
||||
按照以下步骤为 termscp 设置 KeepassXC:
|
||||
|
||||
1. 安装 KeepassXC。
|
||||
2. 在工具栏中进入 "Tools" > "Settings"。
|
||||
3. 选择 "Secret service integration" 并启用 "Enable KeepassXC freedesktop.org secret service integration"。
|
||||
4. 如果你还没有数据库,请创建一个:在工具栏中,"Database" > "New database"。
|
||||
5. 在工具栏中,进入 "Database" > "Database settings"。
|
||||
6. 选择 "Secret service integration" 并启用 "Expose entries under this group"。
|
||||
7. 选择将保存 termscp 密钥的组。请注意,任何其他应用程序都可以读取通过 D-Bus 为该组暴露的密钥。
|
||||
@@ -0,0 +1,17 @@
|
||||
# SSH 密钥存储
|
||||
|
||||
除了配置之外,termscp 还为 SFTP/SCP 客户端提供了一项重要功能:SSH 密钥存储。
|
||||
|
||||
要访问 SSH 密钥存储,请进入配置界面并切换到 `SSH Keys` 选项卡。
|
||||
|
||||
## 管理密钥
|
||||
|
||||
在 `SSH Keys` 选项卡中你可以:
|
||||
|
||||
- **添加新密钥**:按 `<CTRL+N>`。系统会提示你提供与该密钥关联的主机名/IP 地址和用户名,然后会打开一个文本编辑器:将 **私有** SSH 密钥粘贴到编辑器中,保存并退出。
|
||||
- **删除现有密钥**:在要删除的密钥上按 `<DEL>` 或 `<CTRL+E>`,即可将其从 termscp 中永久删除。
|
||||
- **编辑现有密钥**:在要编辑的密钥上按 `<ENTER>`,即可更改私有密钥。
|
||||
|
||||
## 受密码保护的密钥
|
||||
|
||||
支持受密码保护的私有密钥。你在 termscp 中提供的用于身份验证的密码,对用户名/密码认证和密钥认证都有效。
|
||||
@@ -0,0 +1,97 @@
|
||||
# 主题
|
||||
|
||||
termscp 允许你为应用程序中的多个组件设置颜色。有两种方式可以自定义 termscp:
|
||||
|
||||
- 通过 **配置菜单**
|
||||
- 导入 **主题文件**
|
||||
|
||||
## 通过配置菜单自定义
|
||||
|
||||
要通过配置菜单自定义 termscp,请在认证界面按 `<CTRL+C>` 进入配置,然后按两次 `<TAB>` 到达 `themes` 面板。使用 `<UP>` 和 `<DOWN>` 移动以选择你想更改的样式,如下面的 gif 所示:
|
||||
|
||||

|
||||
|
||||
## 导入主题文件
|
||||
|
||||
你也可以导入主题文件。你可以从仓库 `themes/` 目录中随 termscp 附带的某个主题获取灵感,或直接使用它。通过运行以下命令导入主题:
|
||||
|
||||
```sh
|
||||
termscp theme <theme_file>
|
||||
```
|
||||
|
||||
如果一切正常,termscp 会确认主题已导入。
|
||||
|
||||
## 颜色语法
|
||||
|
||||
termscp 接受以下颜色格式:
|
||||
|
||||
- 显式十六进制:`#rrggbb`
|
||||
- RGB:`rgb(r, g, b)`
|
||||
- [CSS 颜色名称](https://www.w3schools.com/cssref/css_colors.asp)(例如 `crimson`)
|
||||
- 特殊关键字 `Default`,它使用与情境相关的默认前景色或背景色(文本和线条使用前景色,其余使用背景色)
|
||||
|
||||
## 从无法加载的主题中恢复
|
||||
|
||||
更新后,已保存的主题可能无法加载。这发生在向主题添加新键时:之前保存的主题不再包含该键。有两种快速修复方法:
|
||||
|
||||
1. 重新导入官方主题。每次发布后,官方主题都会被修补,因此从仓库下载更新后的主题并重新导入:
|
||||
|
||||
```sh
|
||||
termscp theme <theme.toml>
|
||||
```
|
||||
|
||||
2. 手动编辑你的主题。如果你使用自定义主题,请编辑该文件并添加缺失的键。主题位于 `$CONFIG_DIR/theme.toml`,其中 `$CONFIG_DIR` 为:
|
||||
|
||||
- FreeBSD/Linux:`$HOME/.config/termscp`
|
||||
- macOS:`$HOME/.config/termscp`
|
||||
- Windows:`%USERPROFILE%\.termscp`
|
||||
|
||||
缺失的键会在你刚安装的版本的 CHANGELOG 中 `BREAKING CHANGES` 部分列出。
|
||||
|
||||
## 样式
|
||||
|
||||
下面的表格描述了每个样式字段。请注意,样式 **不** 适用于配置页面,因此即使你不小心更改了某些内容,配置页面也始终保持可用。
|
||||
|
||||
### 认证页面
|
||||
|
||||
| 键 | 说明 |
|
||||
| ---------------- | -------------------------- |
|
||||
| `auth_address` | IP 地址输入框的颜色 |
|
||||
| `auth_bookmarks` | 书签面板的颜色 |
|
||||
| `auth_password` | 密码输入框的颜色 |
|
||||
| `auth_port` | 端口号输入框的颜色 |
|
||||
| `auth_protocol` | 协议单选框组的颜色 |
|
||||
| `auth_recents` | 最近记录面板的颜色 |
|
||||
| `auth_username` | 用户名输入框的颜色 |
|
||||
|
||||
### 传输页面
|
||||
|
||||
| 键 | 说明 |
|
||||
| -------------------------------------- | -------------------------------------------------- |
|
||||
| `transfer_local_explorer_background` | 本地主机浏览器的背景色 |
|
||||
| `transfer_local_explorer_foreground` | 本地主机浏览器的前景色 |
|
||||
| `transfer_local_explorer_highlighted` | 本地主机浏览器的边框及高亮颜色 |
|
||||
| `transfer_remote_explorer_background` | 远程浏览器的背景色 |
|
||||
| `transfer_remote_explorer_foreground` | 远程浏览器的前景色 |
|
||||
| `transfer_remote_explorer_highlighted` | 远程浏览器的边框及高亮颜色 |
|
||||
| `transfer_log_background` | 日志面板的背景色 |
|
||||
| `transfer_log_window` | 日志面板的窗口颜色 |
|
||||
| `transfer_progress_bar_partial` | 部分进度条的颜色 |
|
||||
| `transfer_progress_bar_total` | 总进度条的颜色 |
|
||||
| `transfer_status_hidden` | 状态栏 "hidden" 标签的颜色 |
|
||||
| `transfer_status_sorting` | 状态栏 "sorting" 标签的颜色;也适用于文件排序对话框 |
|
||||
| `transfer_status_sync_browsing` | 状态栏 "sync browsing" 标签的颜色 |
|
||||
|
||||
### 杂项
|
||||
|
||||
这些样式适用于应用程序的不同部分。
|
||||
|
||||
| 键 | 说明 |
|
||||
| ------------------- | -------------------------------- |
|
||||
| `misc_error_dialog` | 错误消息的颜色 |
|
||||
| `misc_info_dialog` | 信息对话框的颜色 |
|
||||
| `misc_input_dialog` | 输入对话框的颜色(例如复制文件) |
|
||||
| `misc_keys` | 按键文本的颜色 |
|
||||
| `misc_quit_dialog` | 退出对话框的颜色 |
|
||||
| `misc_save_dialog` | 保存对话框的颜色 |
|
||||
| `misc_warn_dialog` | 警告对话框的颜色 |
|
||||
@@ -0,0 +1,59 @@
|
||||
# 开发者手册
|
||||
|
||||
欢迎阅读 termscp 的开发者手册。本章不包含 termscp 各模块的文档,相关文档可以在 Rust Docs 上找到:<https://docs.rs/termscp>。本章描述 termscp 的工作原理,以及实现诸如文件传输和用户界面扩展等功能的指南。
|
||||
|
||||
termscp 使用 Rust 编写(edition 2024,MSRV 1.89.0)。用户界面使用 [tuirealm](https://github.com/veeso/tui-realm) v3 构建,它运行在 [crossterm](https://github.com/crossterm-rs/crossterm) 之上。
|
||||
|
||||
## termscp 的工作原理
|
||||
|
||||
termscp 基本上由 3 个核心模块组成:
|
||||
|
||||
- **host**:host 模块提供与文件系统交互的函数。它暴露 `HostBridge` trait,该 trait 抽象了对本地主机(`Localhost`)和远程主机(`RemoteBridged`)的文件操作。
|
||||
- **ui**:该模块包含用户界面的实现。如下一章所示,这是通过 **activities** 实现的。
|
||||
- **activity_manager**:activity manager 负责管理 activities。它运行用户界面的 activities,并根据它们的状态决定何时终止当前 activity 以及接下来运行哪个 activity。
|
||||
|
||||
除了这 3 个核心模块之外,随着时间推移又添加了其他模块:
|
||||
|
||||
- **config**:提供配置 schema 及其序列化方法。
|
||||
- **explorer**:暴露 explorer 结构,用于处理 ui 中的文件资源管理器。它们存储当前目录模型和视图状态(例如排序、是否显示隐藏文件、传输队列)。
|
||||
- **filetransfer**:定义 `FileTransferProtocol` 枚举和 `RemoteFsBuilder`,后者根据连接参数构造合适的 `RemoteFs` 客户端。
|
||||
- **system**:提供与配置、ssh 密钥存储和书签交互的方式。
|
||||
- **utils**:包含几乎整个项目都会使用的工具。
|
||||
|
||||
termscp 支持以下协议:SFTP、SCP、FTP/FTPS、Kube、S3、SMB 和 WebDAV。
|
||||
|
||||
## Activities
|
||||
|
||||
本段对 activities 做一个简短的概述。请阅读代码和文档,以清晰地了解 ui 的工作方式。
|
||||
|
||||
实现用户界面有很多方法。本项目借鉴了不同框架中各自最佳的部分:
|
||||
|
||||
- **顶层的 Activities**:每个“视图”都是一个 Activity,并由 `Activity Manager` 来处理它们。这种方法受 Android 启发。它适用于具有不同视图的 ui,每个视图都有自己的组件和逻辑。Activities 与 `Context` 协作,`Context` 是用于在 activities 之间共享数据的数据持有者。
|
||||
- **Activities 显示 Applications**:每个 activity 可以显示不同的 **Applications**。一个 application 包含一个 **View**,它基本上是一个 **components** 列表,每个组件都有其属性。view 是组件的门面,同时也处理焦点,即当前处于活动状态的组件。你不能拥有多个活动组件,因此必须对此进行处理;与此同时,如果当前组件被销毁,焦点必须交还给之前处于活动状态的组件。**Application** 负责处理所有这些工作。要了解更多信息,请阅读 <https://github.com/veeso/tui-realm>。
|
||||
- **Components**:components 是围绕 tui 构建的,以便复用控件。这是通过 `Component` trait 实现的,该 trait 受 [React](https://reactjs.org/) 启发。每个组件都有其 *Properties*,并且可以拥有其 *States*。每个组件必须处理输入事件、接受新的属性,并提供一个用于**渲染**自身的方法。这一逻辑现在位于 [tui-realm](https://github.com/veeso/tui-realm) 中。
|
||||
- **Messages:基于 Elm 的方法**:输入事件采用受 [Elm](https://elm-lang.org/) 启发的方法来处理。在 Elm 中,你使用三个基本函数来实现 ui:**update**、**view** 和 **init**。termscp 将 Elm update 函数的等价实现编写为一个递归函数内部的大型 match 分支,你可以在每个 activity 的 `update.rs` 文件中找到它。这个 match 分支处理组件为响应传入的输入事件而产生的消息,并促使 activity 改变其状态。
|
||||
|
||||
termscp 实现了一个名为 `Activity` 的 trait,它是 Android activity 的一个大幅精简版本。该 trait 提供以下方法:
|
||||
|
||||
- `on_create`:初始化 activity。context 被传递给 activity,activity 成为 Context 的唯一所有者,直到该 activity 终止。
|
||||
- `on_draw`:每当用户界面应当更新时被调用。它基本上就是 activity 的运行方法,同时也处理输入事件。界面不应在每次调用时都被绘制(该方法每秒可能被调用数百次),而只应在确实发生变化时(例如在某次输入事件之后)才绘制。
|
||||
- `will_umount`:返回 activity 是否应当被销毁。如果是,它会返回一个 `ExitReason`,用于指示该 activity 应当终止的原因。activity manager 会根据该原因决定是停止 termscp 的执行,还是启动一个新的 activity 以及启动哪一个。
|
||||
- `on_destroy`:终结 activity 并将其释放。该方法将 Context 返回给调用方(activity manager)。
|
||||
|
||||
### Context
|
||||
|
||||
context 是一个保存 activities 之间共享数据的结构。每次某个 Activity 启动时,Context 都会被该 activity 取走,直到它被销毁时,context 才最终返回给 activity manager。context 保存以下数据:
|
||||
|
||||
- **Localhost**:本地主机结构。
|
||||
- **File Transfer Params**:当前用于连接到远程主机的参数。
|
||||
- **Config Client**:一个提供访问用户配置的函数的结构。
|
||||
- **Store**:一个可以保存任意类型数据的键值存储。它可用于在 activities 之间共享状态,或为繁重或缓慢的任务(例如检查更新)保持持久化。
|
||||
- **Terminal**:用于在终端上渲染 tui。
|
||||
|
||||
## 实现抽象的文件传输客户端
|
||||
|
||||
当 termscp 的实现于 2020 年 12 月开始时,文件传输处于设计的核心,因为它是 termscp 的核心所在。最初的实现由一个 `filetransfer` 模块组成,该模块暴露了一个名为 `FileTransfer` 的 trait,它提供了与远程文件系统进行通用交互的方法。
|
||||
|
||||
随着时间推移,由于不同用户都希望有一个专门的库,这种情况发生了变化。在 2021 年最后一个季度,[remotefs](https://github.com/veeso/remotefs-rs) 诞生了:一个用于操作远程设备文件系统的抽象库。remotefs 提供了一个 `RemoteFs` trait,它暴露了所有核心文件系统功能,并且自 0.8.0 版本起,它已经取代了 `FileTransfer` trait。
|
||||
|
||||
文件传输模块仍然存在,但它唯一的任务是通过 `RemoteFsBuilder` 根据文件传输参数构建一个 `RemoteFs` 客户端实现。
|
||||
@@ -0,0 +1,61 @@
|
||||
# 连接到服务器
|
||||
|
||||
termscp 可以根据你传入的参数以三种不同的方式启动。
|
||||
|
||||
- 不带参数:termscp 打开认证表单,你在其中提供连接到远程主机所需的参数。
|
||||
- 带地址参数:termscp 跳过认证表单,直接连接到远程主机。
|
||||
- 通过 `-b <bookmark-name>` 传入书签名称:termscp 将参数解析为已保存的书签并进行连接。重复使用 `-b` 可打开多个书签。
|
||||
|
||||
当你提供地址参数或书签名称时,还可以为本地主机提供一个起始工作目录。
|
||||
|
||||
## 认证表单
|
||||
|
||||
当 termscp 在不带地址的情况下启动时,会显示认证表单。填写协议、地址、端口、用户名和密码,然后进行连接。连接成功后,termscp 将打开双面板浏览器。
|
||||
|
||||
## 地址参数语法
|
||||
|
||||
通用地址参数采用以下语法:
|
||||
|
||||
```txt
|
||||
[protocol://][username@]<address>[:port][:wrkdir]
|
||||
```
|
||||
|
||||
这种语法很方便,你很可能会用它来代替交互式表单。下面是一些示例。
|
||||
|
||||
使用默认协议(在你的配置中定义)连接到 `192.168.1.31`。如果未提供端口,则使用所选协议的默认端口。用户名为当前用户的名称。
|
||||
|
||||
```sh
|
||||
termscp 192.168.1.31
|
||||
```
|
||||
|
||||
使用默认协议连接到 `192.168.1.31`,用户名为 `root`:
|
||||
|
||||
```sh
|
||||
termscp root@192.168.1.31
|
||||
```
|
||||
|
||||
使用 SCP 连接到 `192.168.1.31`,端口为 `4022`,用户名为 `omar`:
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022
|
||||
```
|
||||
|
||||
使用 SCP 连接到 `192.168.1.31`,端口为 `4022`,用户名为 `omar`,并以目录 `/tmp` 作为起始目录:
|
||||
|
||||
```sh
|
||||
termscp scp://omar@192.168.1.31:4022:/tmp
|
||||
```
|
||||
|
||||
有关各协议专属的地址语法(S3、Kube、WebDAV 和 SMB),请参阅[连接参数](connection-parameters.md)。
|
||||
|
||||
## 密码的提供方式
|
||||
|
||||
当你以参数形式提供地址时,地址本身没有用于填写密码的字段。你可以通过三种方式提供密码:
|
||||
|
||||
- 系统会提示你输入密码。这是默认方式:如果你不使用下面的任何方法,termscp 会像 `scp`、`ssh` 等经典工具一样提示你输入密码。
|
||||
- `-P, --password` 选项:直接在命令行上传入密码。不推荐这种方法,因为它不安全:密码可能会保留在你的 shell 历史记录中。
|
||||
- 通过 `sshpass`:借助 `sshpass` 提供密码,例如:
|
||||
|
||||
```sh
|
||||
sshpass -f ~/.ssh/topsecret.key termscp cvisintin@192.168.1.31
|
||||
```
|
||||